MobileApp-Pentest-Cheatsheet

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

Android APK unpacker that dumps DEX files from running or installed apps on Android 5.0–12 without root, Xposed, or Frida, supporting deep unpacking…

[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…

Full featured multi arch/os debugger built on top of PyQt5 and frida

A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices

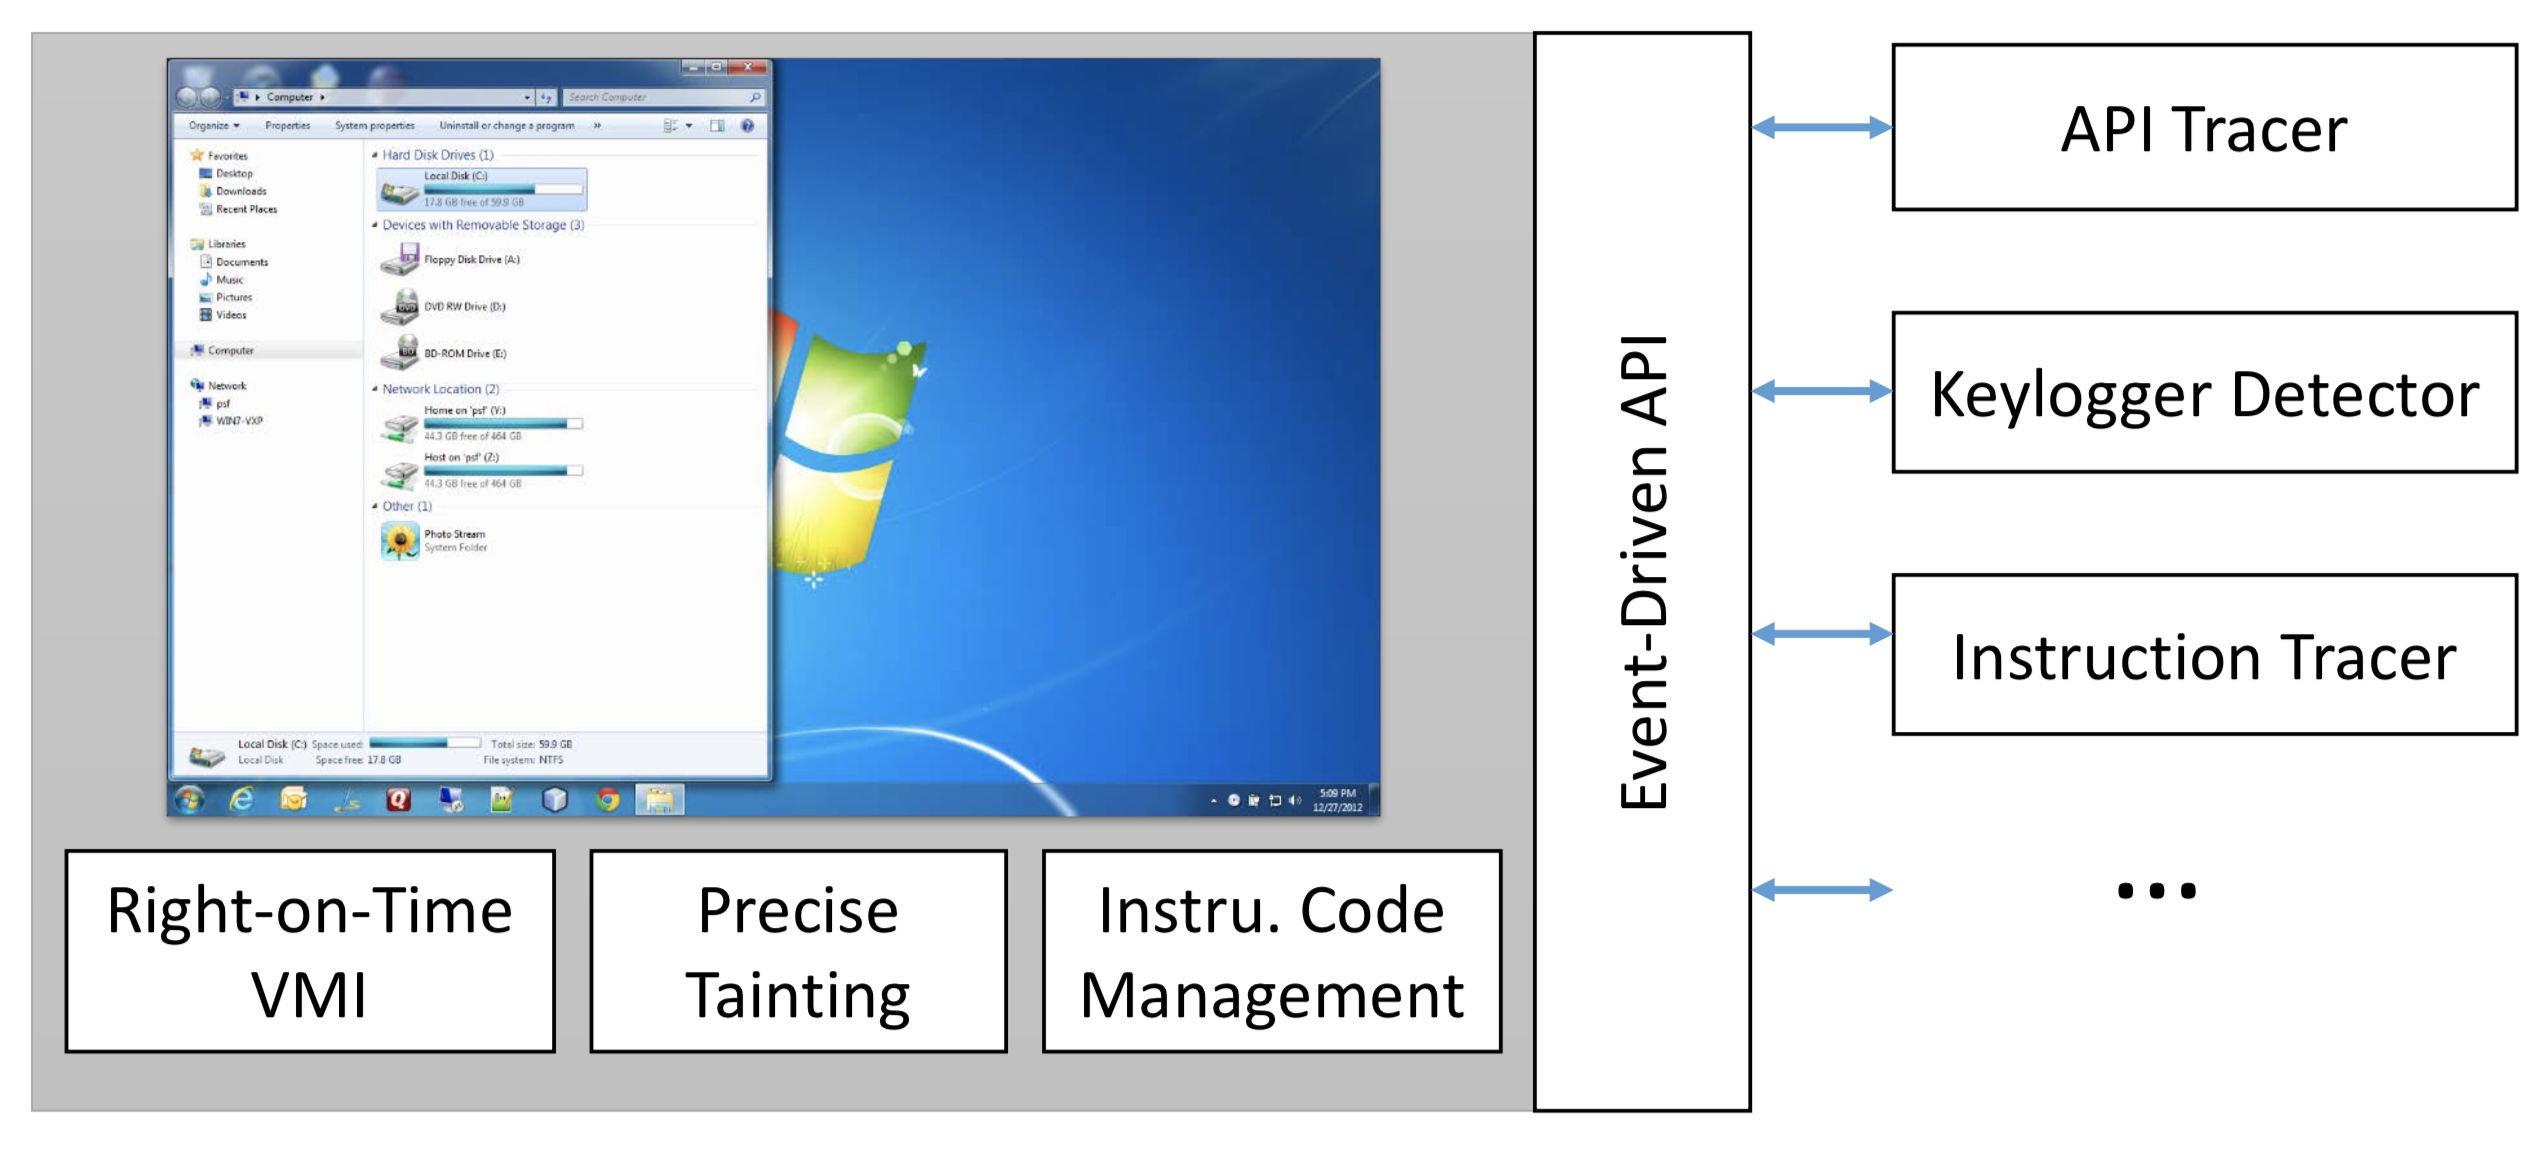
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…

Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…

Ninja Reverse Engineering on Android APK packages

Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…

FairPlay decryptor (dump iPA) for iOS Application that running on macOS with SIP-enabled, using CVE-2025-24204. Support macOS 15.0-15.2

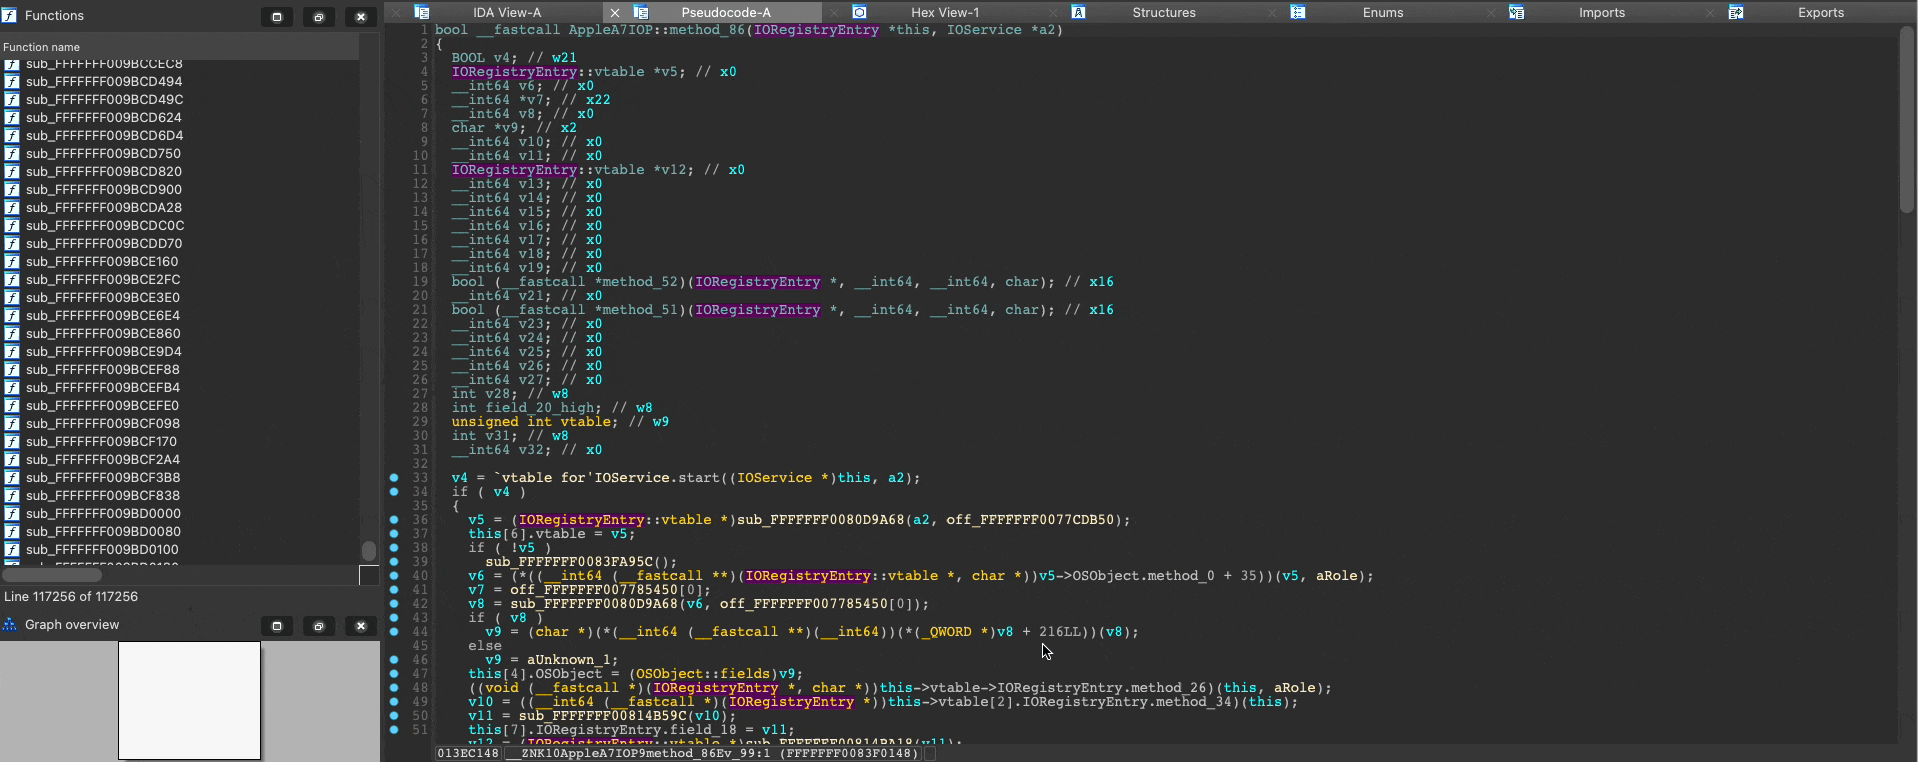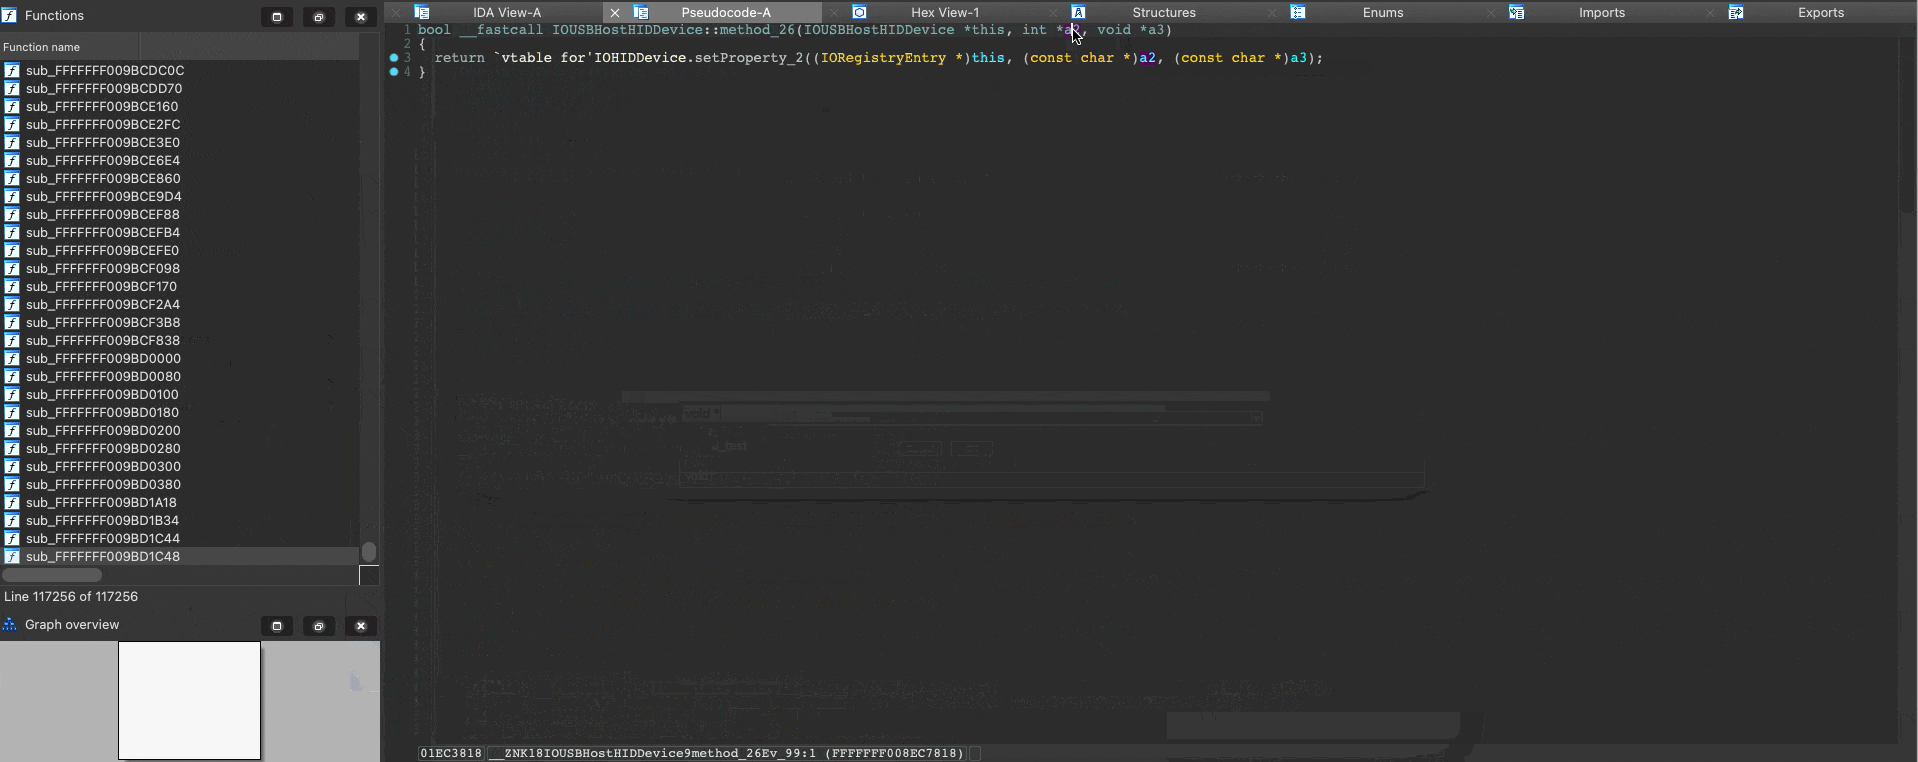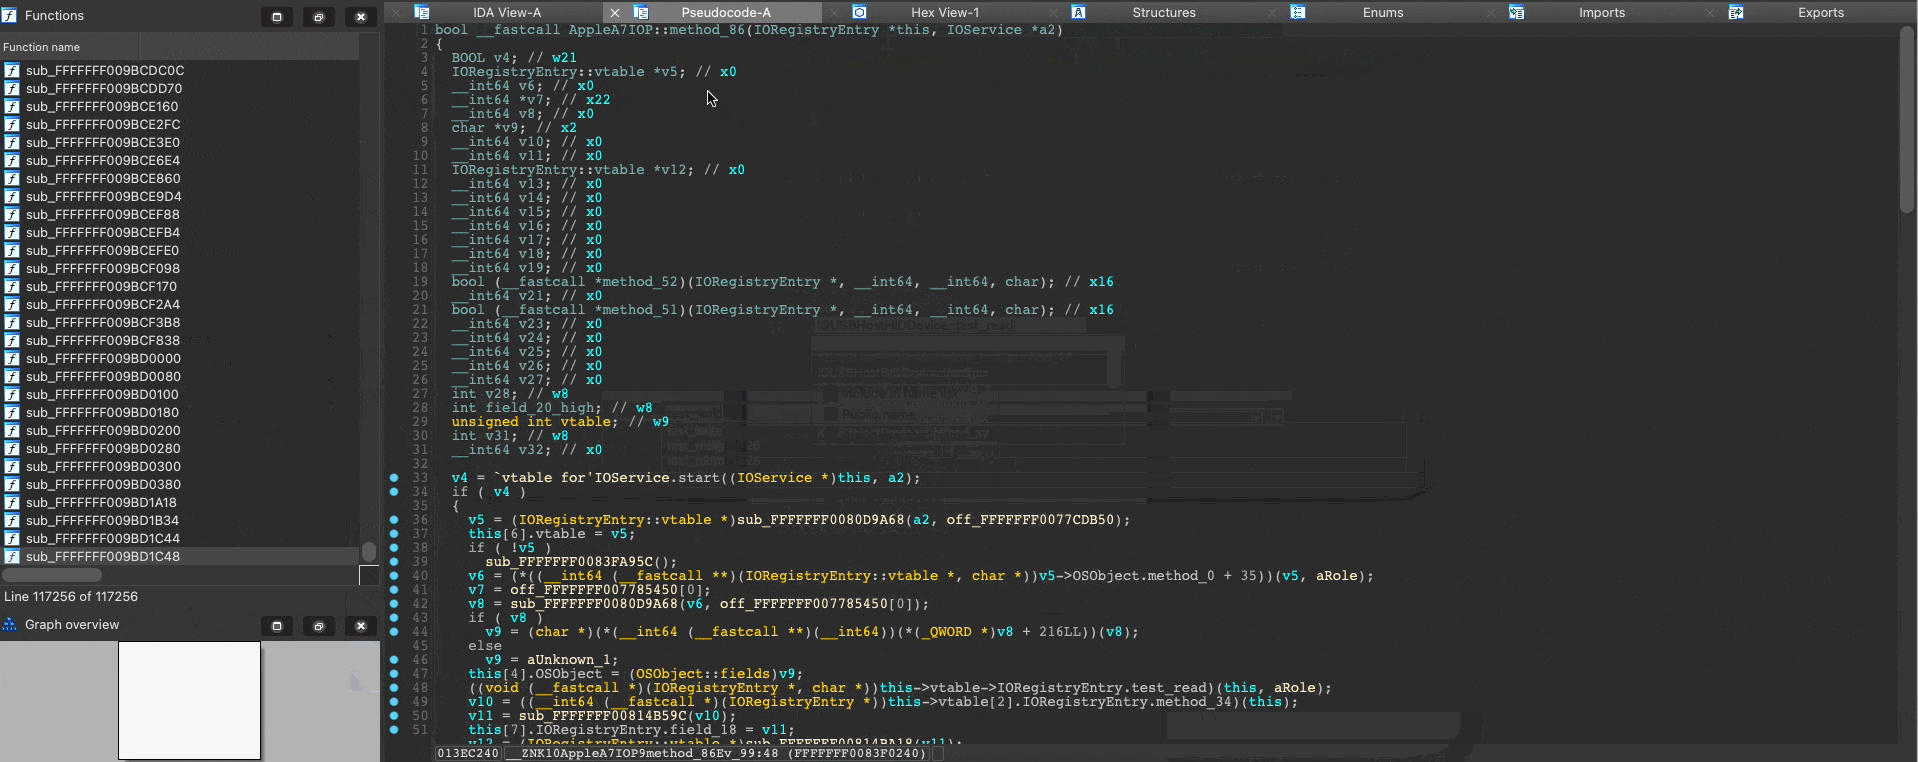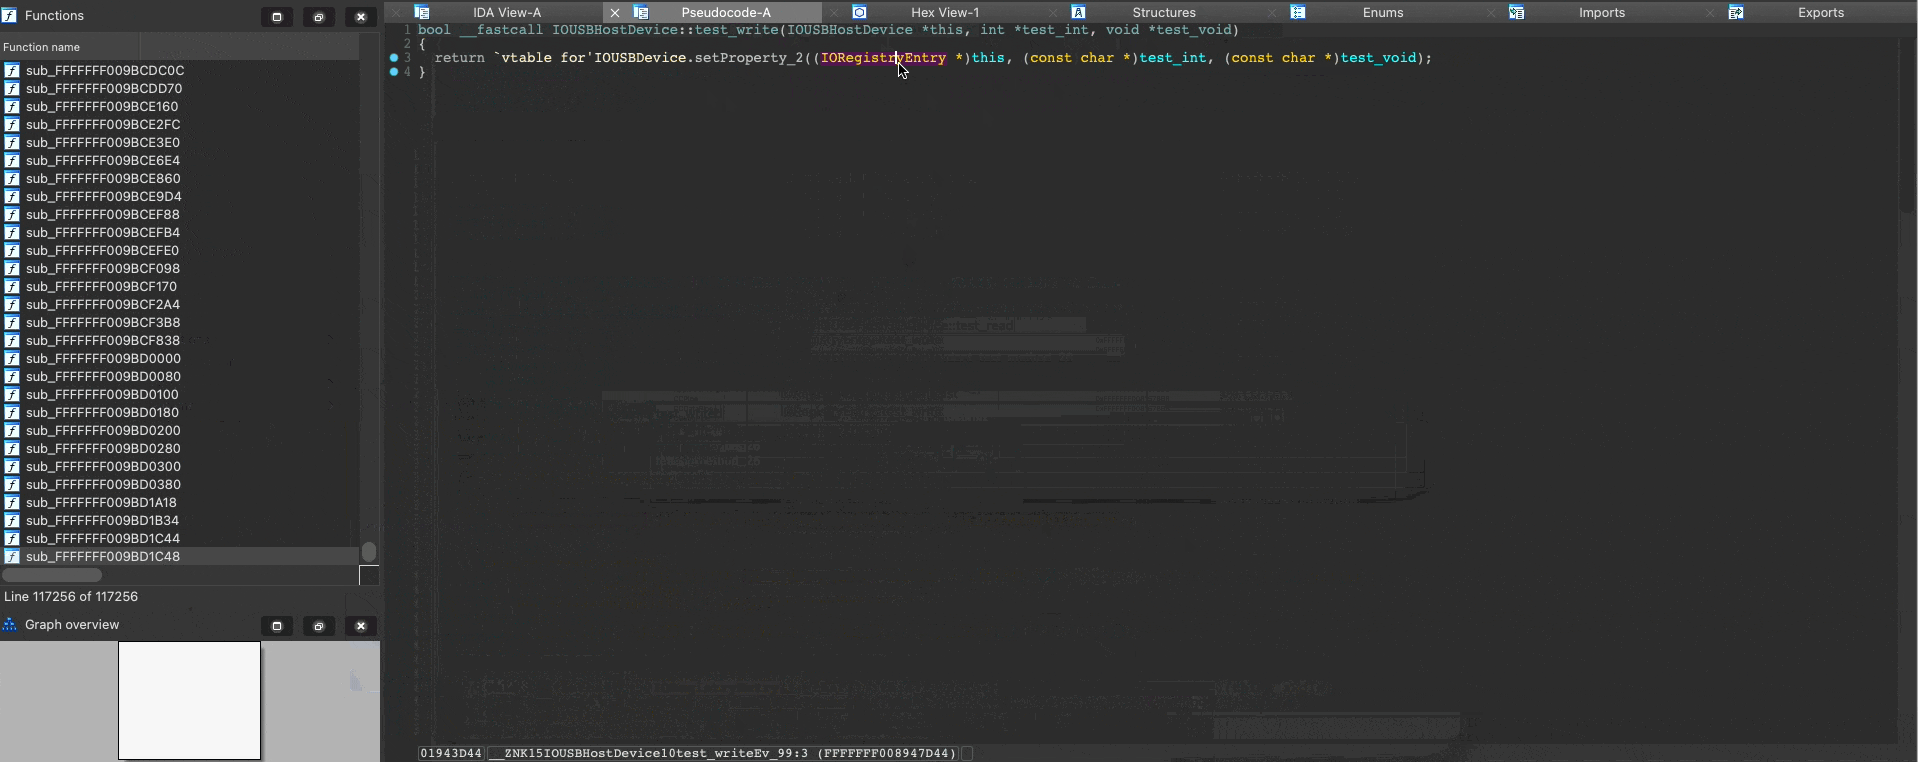
An IDAPython module for enhancing c++ support on top of ida_kernelcache

Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…

Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…

Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…

Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.

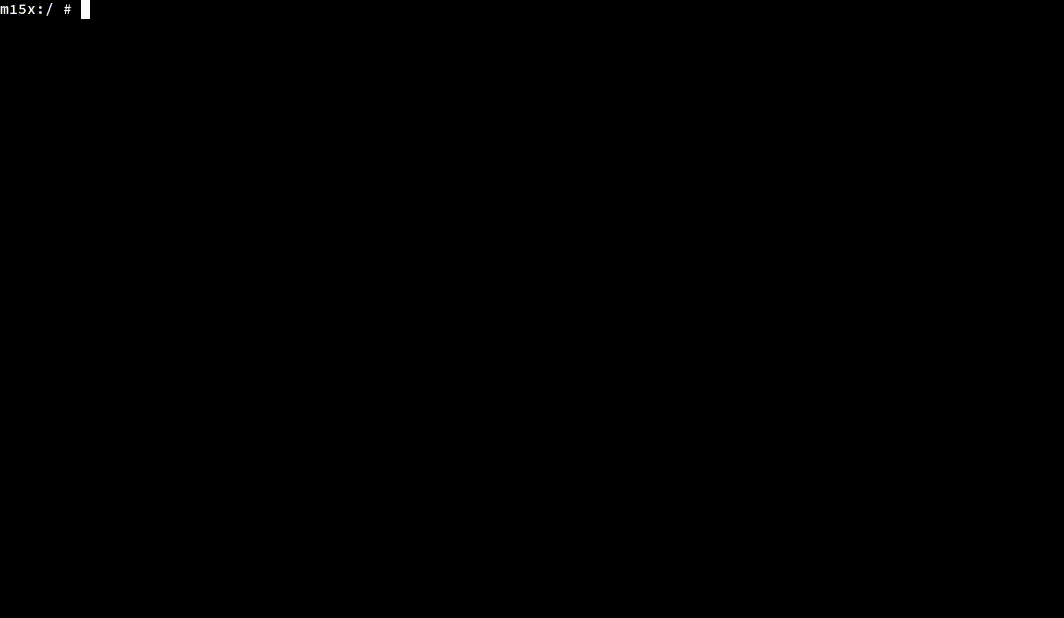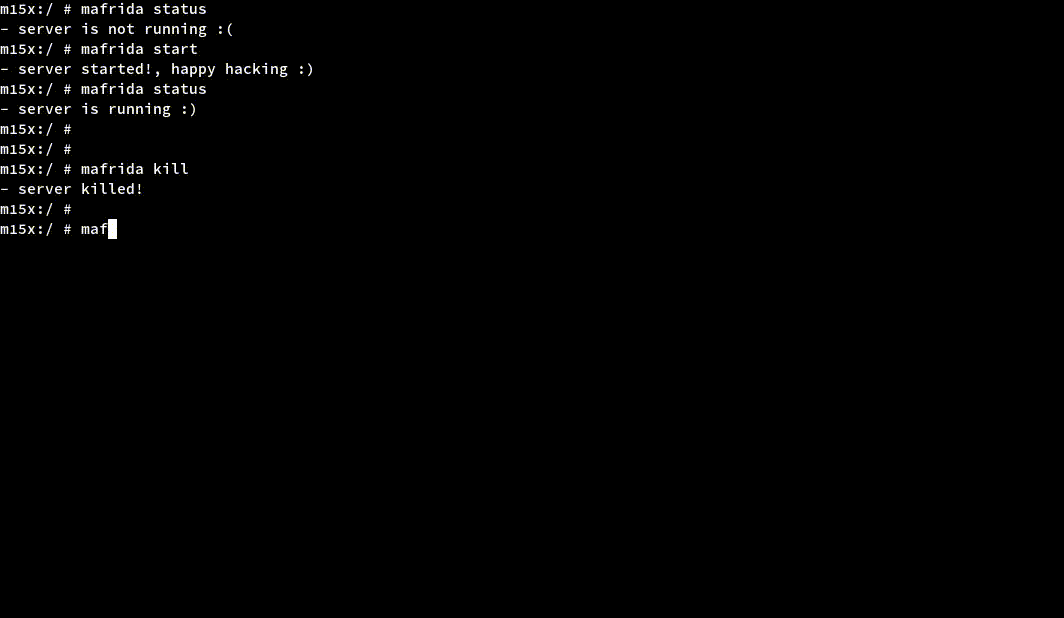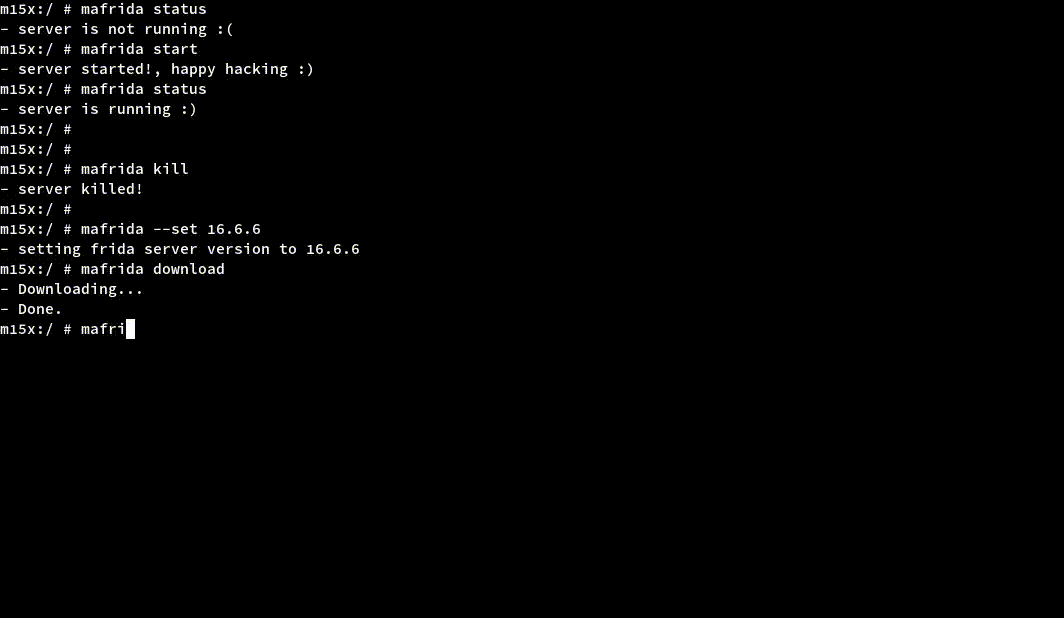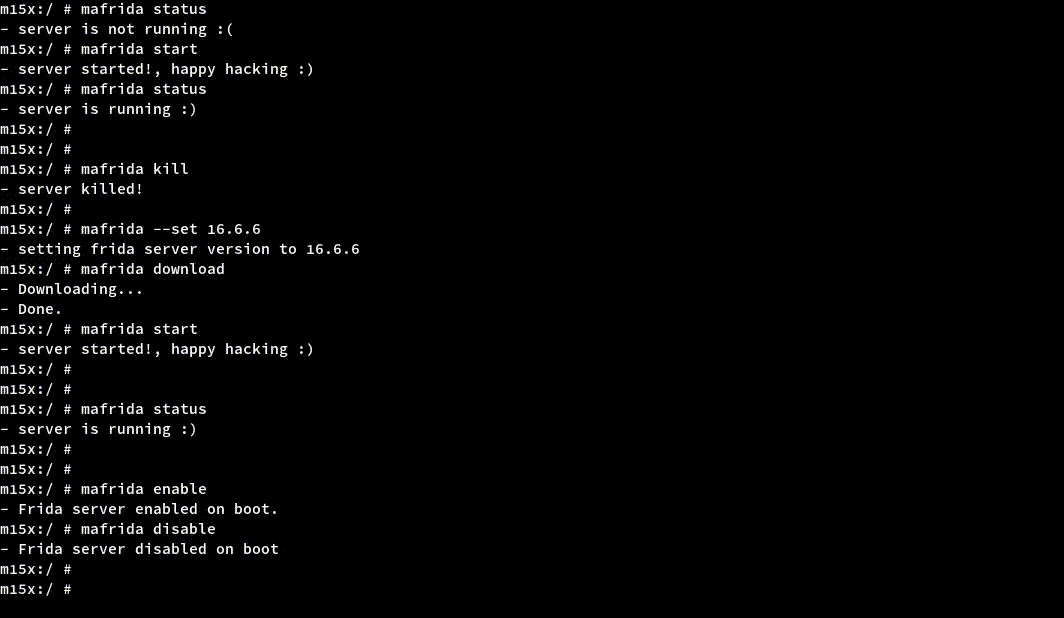
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…

Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.

Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…