
GhidrAssist
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
ai-assisted-reversingbinary-analysisdebuggers+5
symgraph/ghidrassistAn LLM extension for Ghidra to enable AI assistance in RE.
 al3xtjames/ghidra-firmware-utils
Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…
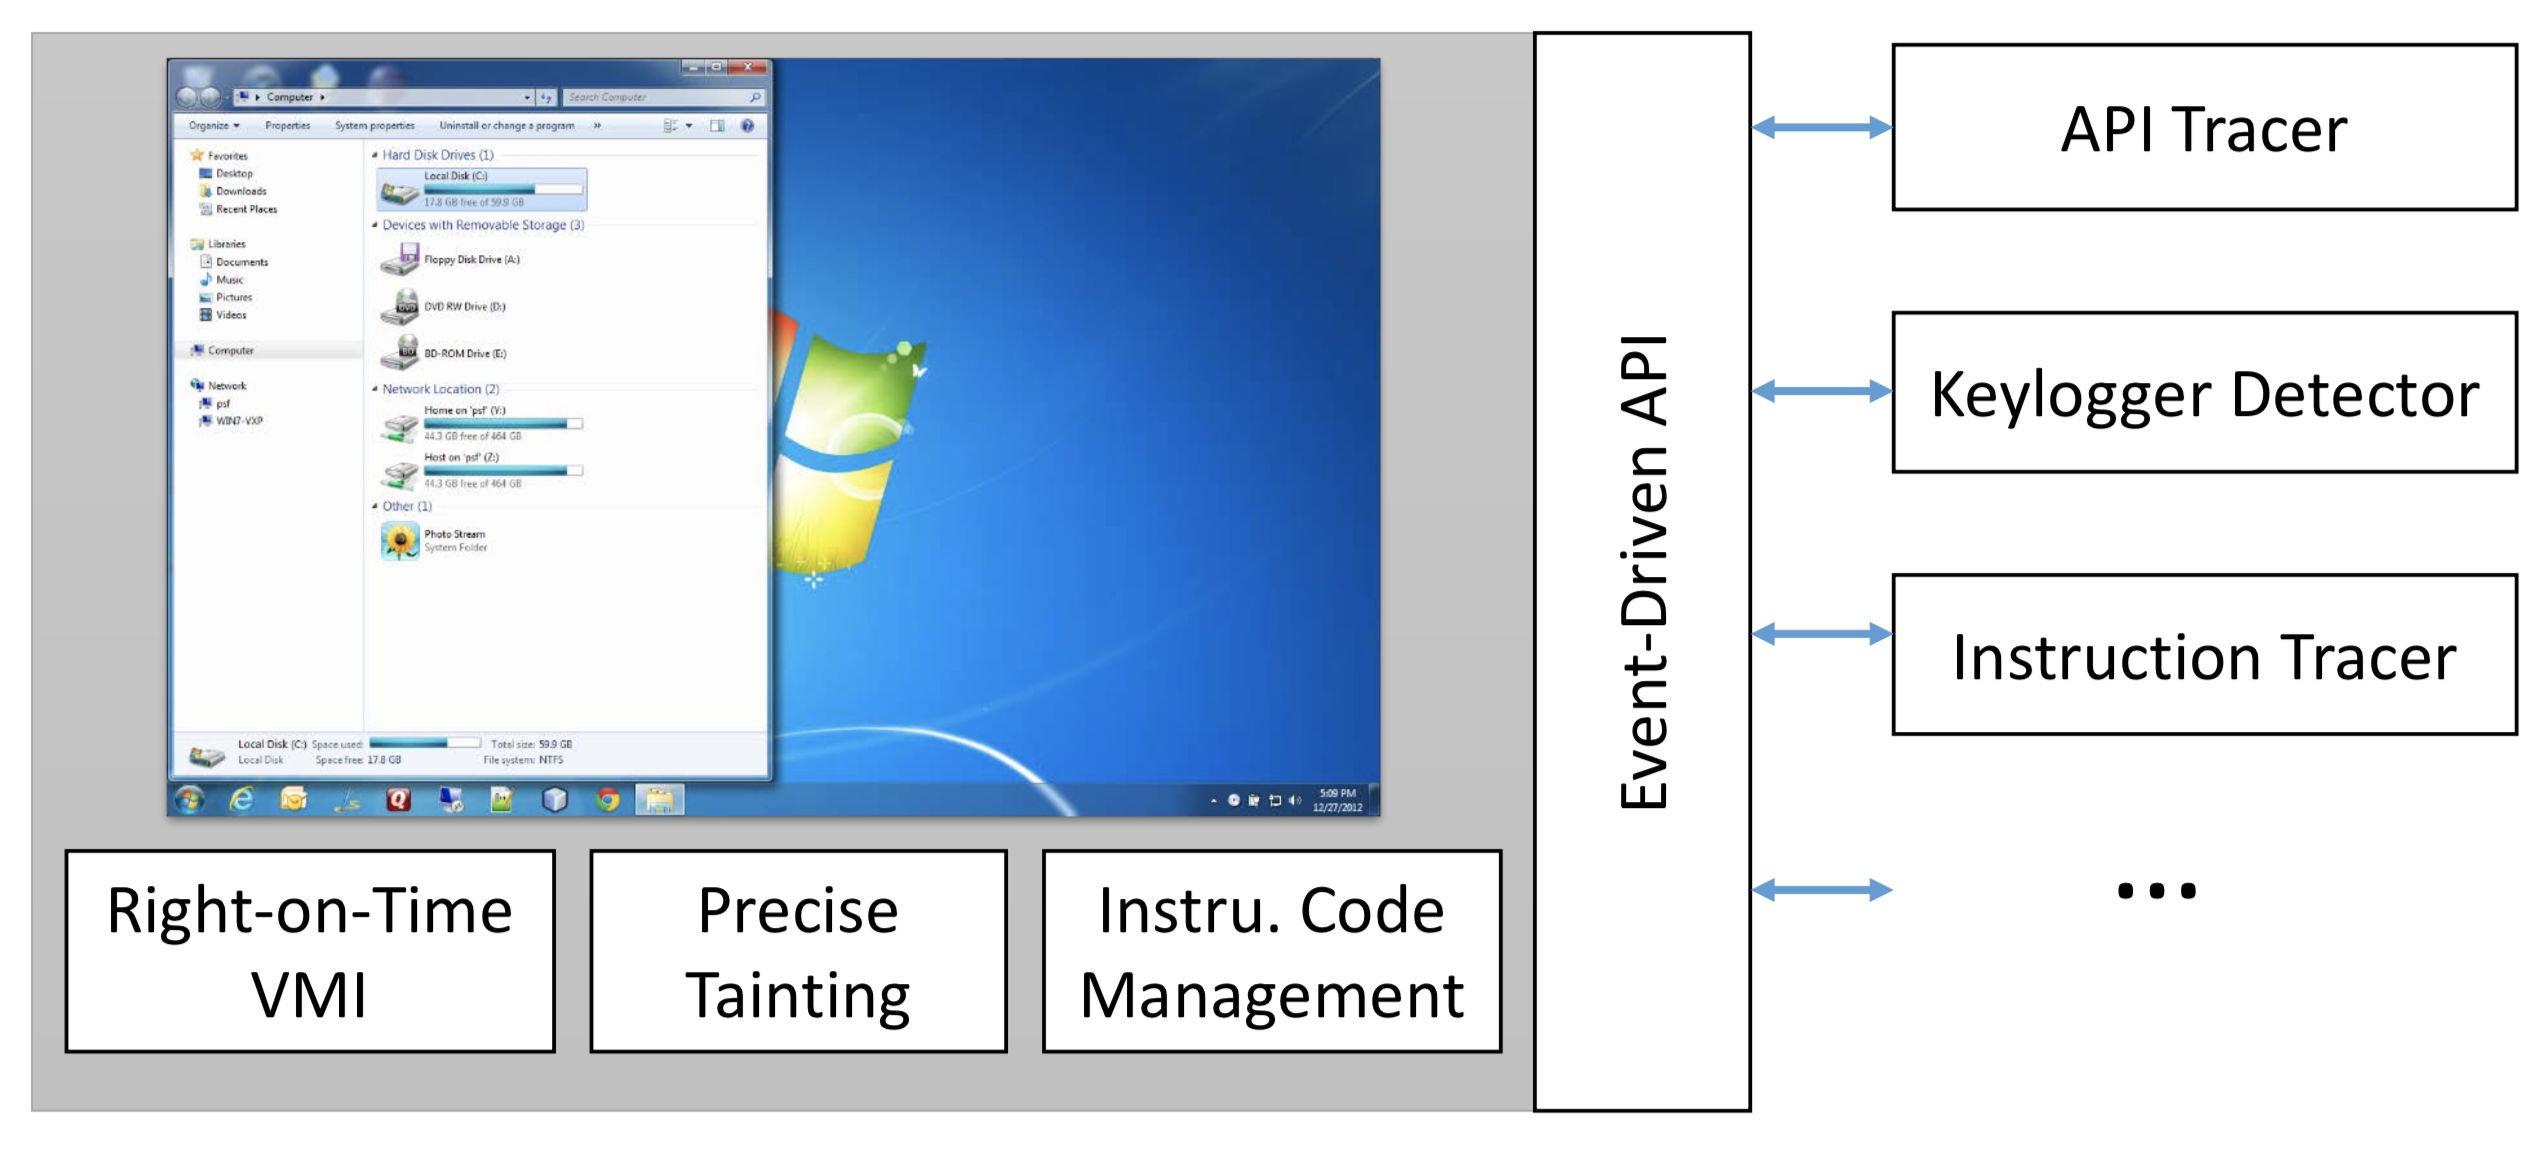 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
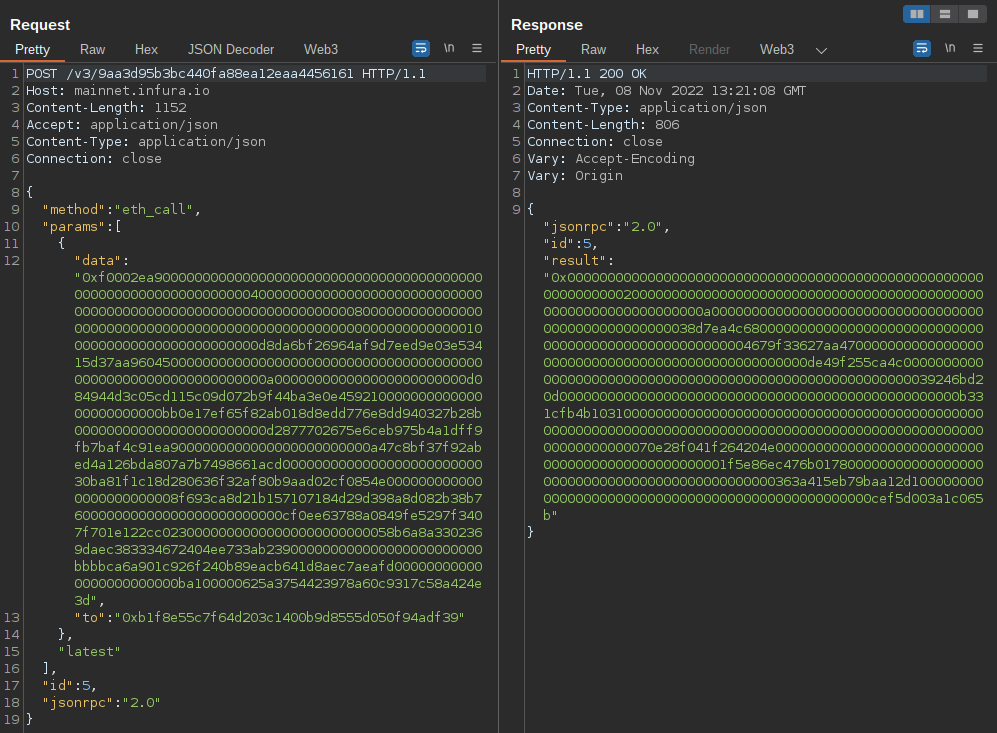 uwctcjnwlk/web3-decoder
Burp Suite extension for decoding Ethereum JSON-RPC calls and smart contract interactions, supporting multiple chains and automatic ABI retrieval.
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
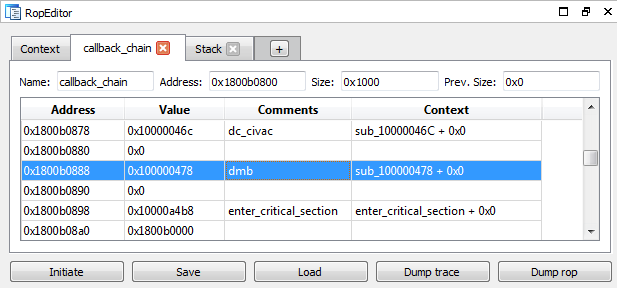 dsecurity/crauemu
crauEmu is an uEmu extension for developing and analyzing payloads for code-reuse attacks
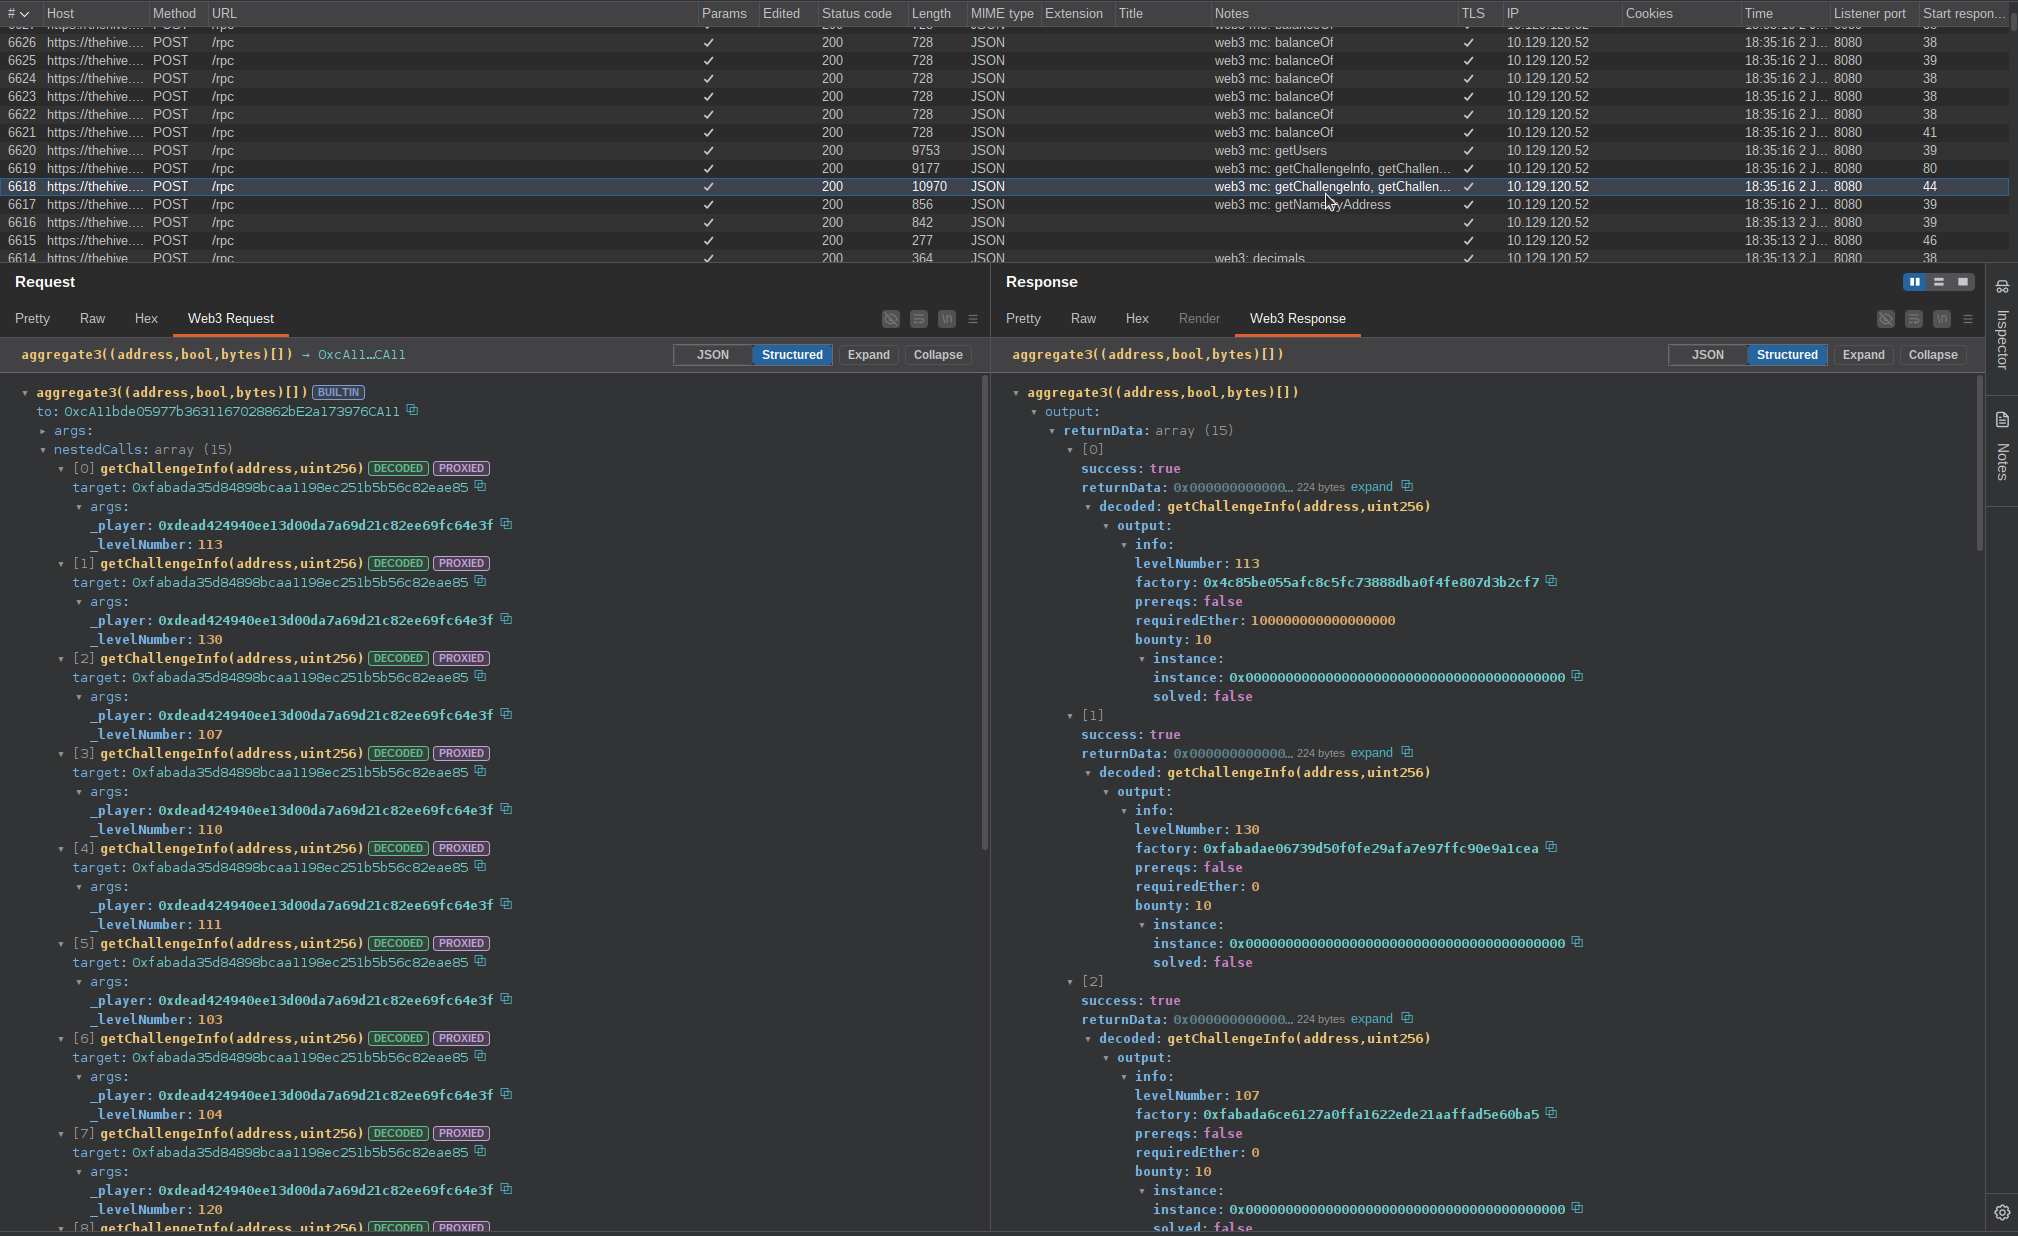 nccgroup/web3-decoder
Burp Suite extension for decoding Web3 JSON-RPC traffic, including smart contract function calls, responses, and ABI resolution with proxy-aware and…
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
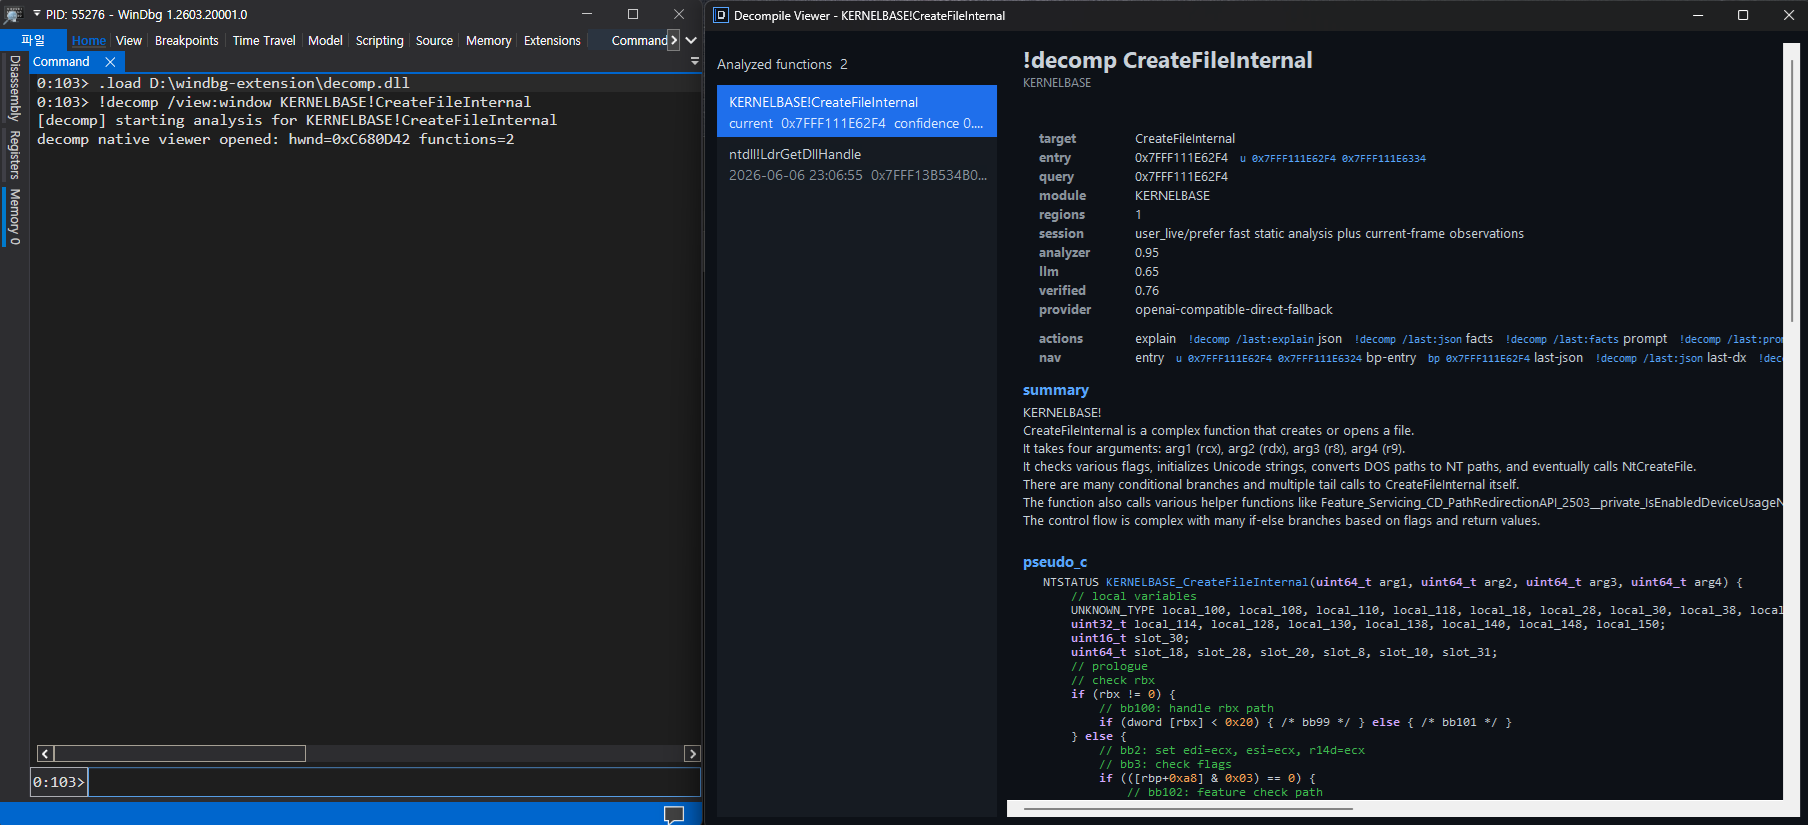 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
 bytev0rtex/cve-2026-64788
Proof-of-concept for CVE-2026-64788, a use-after-free in IOGPUFamily kernel extension on iOS 26.6, demonstrating exploitation via Metal texture…
 eddinos2/cve-2026-64747
Root-cause analysis and reachability PoC for CVE-2026-64747, a buffer overflow in the AppleAVE2 kernel extension. Includes reversed IOKit wire…
 romanrybachek/cve-2023-36900
Denial-of-Service PoC | Writeup | Header with CLFS structures | Imhex pattern for .blf extension
 hyunjungg/cve-2025-62821
Microsoft HEIF Extension (msheif_store.dll) OOB-read
 tomer8007/widevine-l3-decryptor
A Chrome extension that demonstrates bypassing Widevine L3 DRM
 mandiant/ghidrathon
The FLARE team's open-source extension to add Python 3 scripting to Ghidra.