
0day-security-software-vulnerability-analysis-technology
 jas502n/0day-security-software-vulnerability-analysis-technology
0day安全_软件漏洞分析技术
binary-analysiscurated-resourceseducation+3
jas502n/0day-security-software-vulnerability-analysis-technology0day安全_软件漏洞分析技术
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 jonathansalwan/triton
Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification…
 ashemery/exploitation-course
Offensive Software Exploitation Course
 devploit/awesome-ctf-resources
A list of Capture The Flag (CTF) frameworks, libraries, resources and software for started/experienced CTF players 🚩
 jonathansalwan/vmprotect-devirtualization
Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.
 medusalix/freemdu
Open hardware and software tools for communicating with Miele appliances via their optical diagnostic interface
 mfthomps/resim
Reverse engineering software using a full system simulator
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
 quarkslab/binbloom
Raw binary firmware analysis software
 adriancable/eternal
Minimal machine architecture with LLVM compiler backend, Linux port, and virtual machine for creating self-contained software capsules that remain…
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.
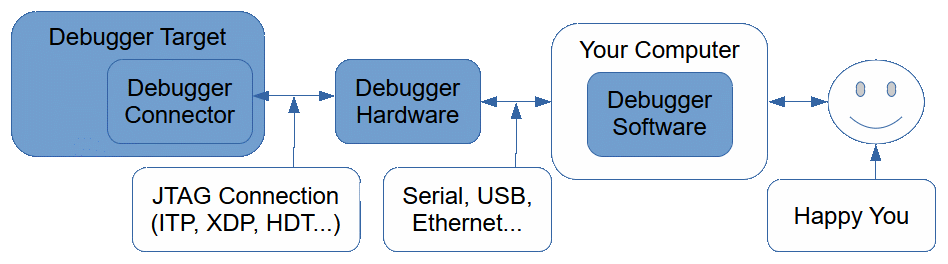 x86-jtag-open-research/x86-jtag-information
Documents Intel and AMD x86 JTAG debugger hardware, connectors, probe software, and target platforms for low-level system debugging and firmware…
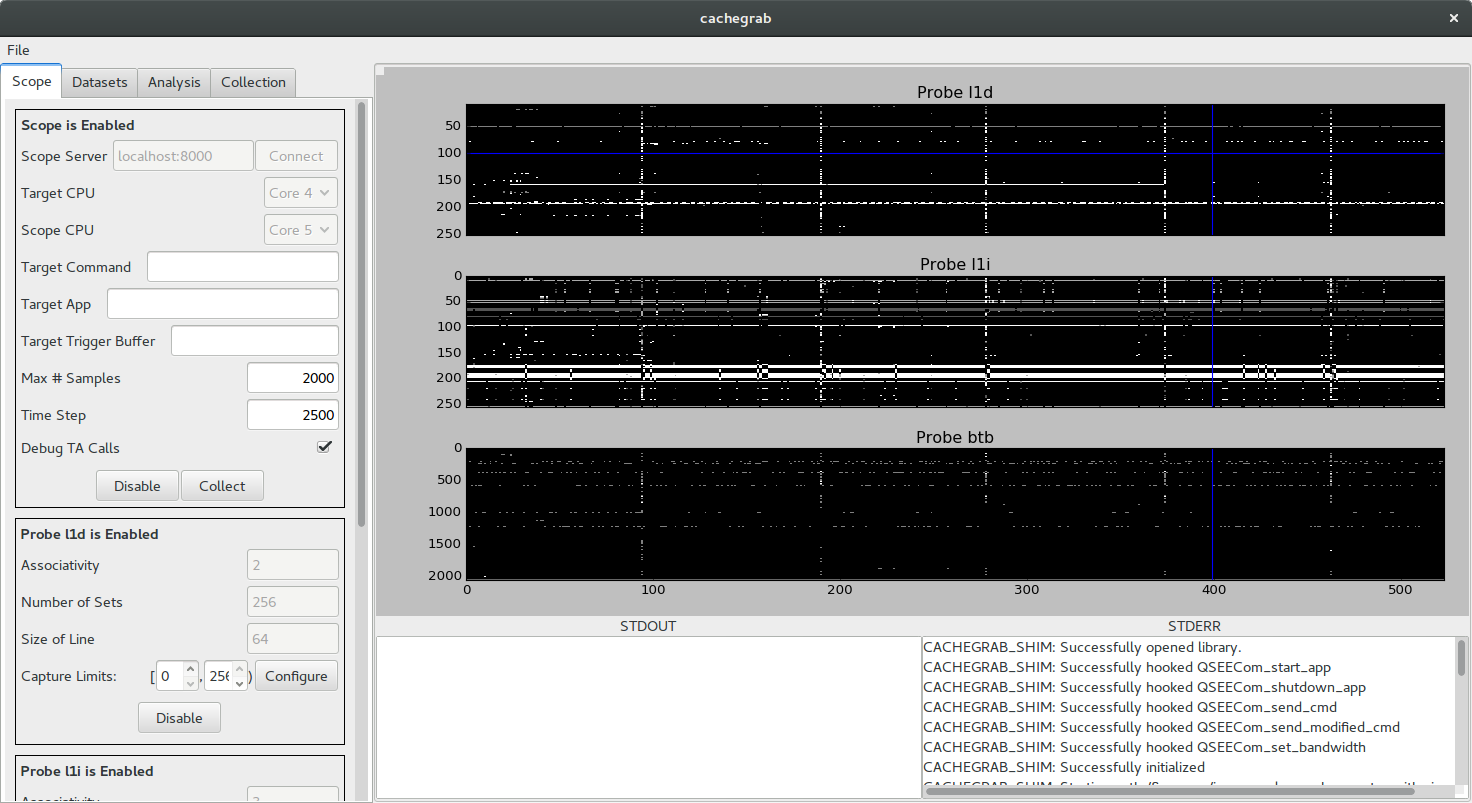 nccgroup/cachegrab
a tool designed to help perform and visualize trace-driven cache attacks against software in the secure world of TrustZone-enabled ARMv8 cores
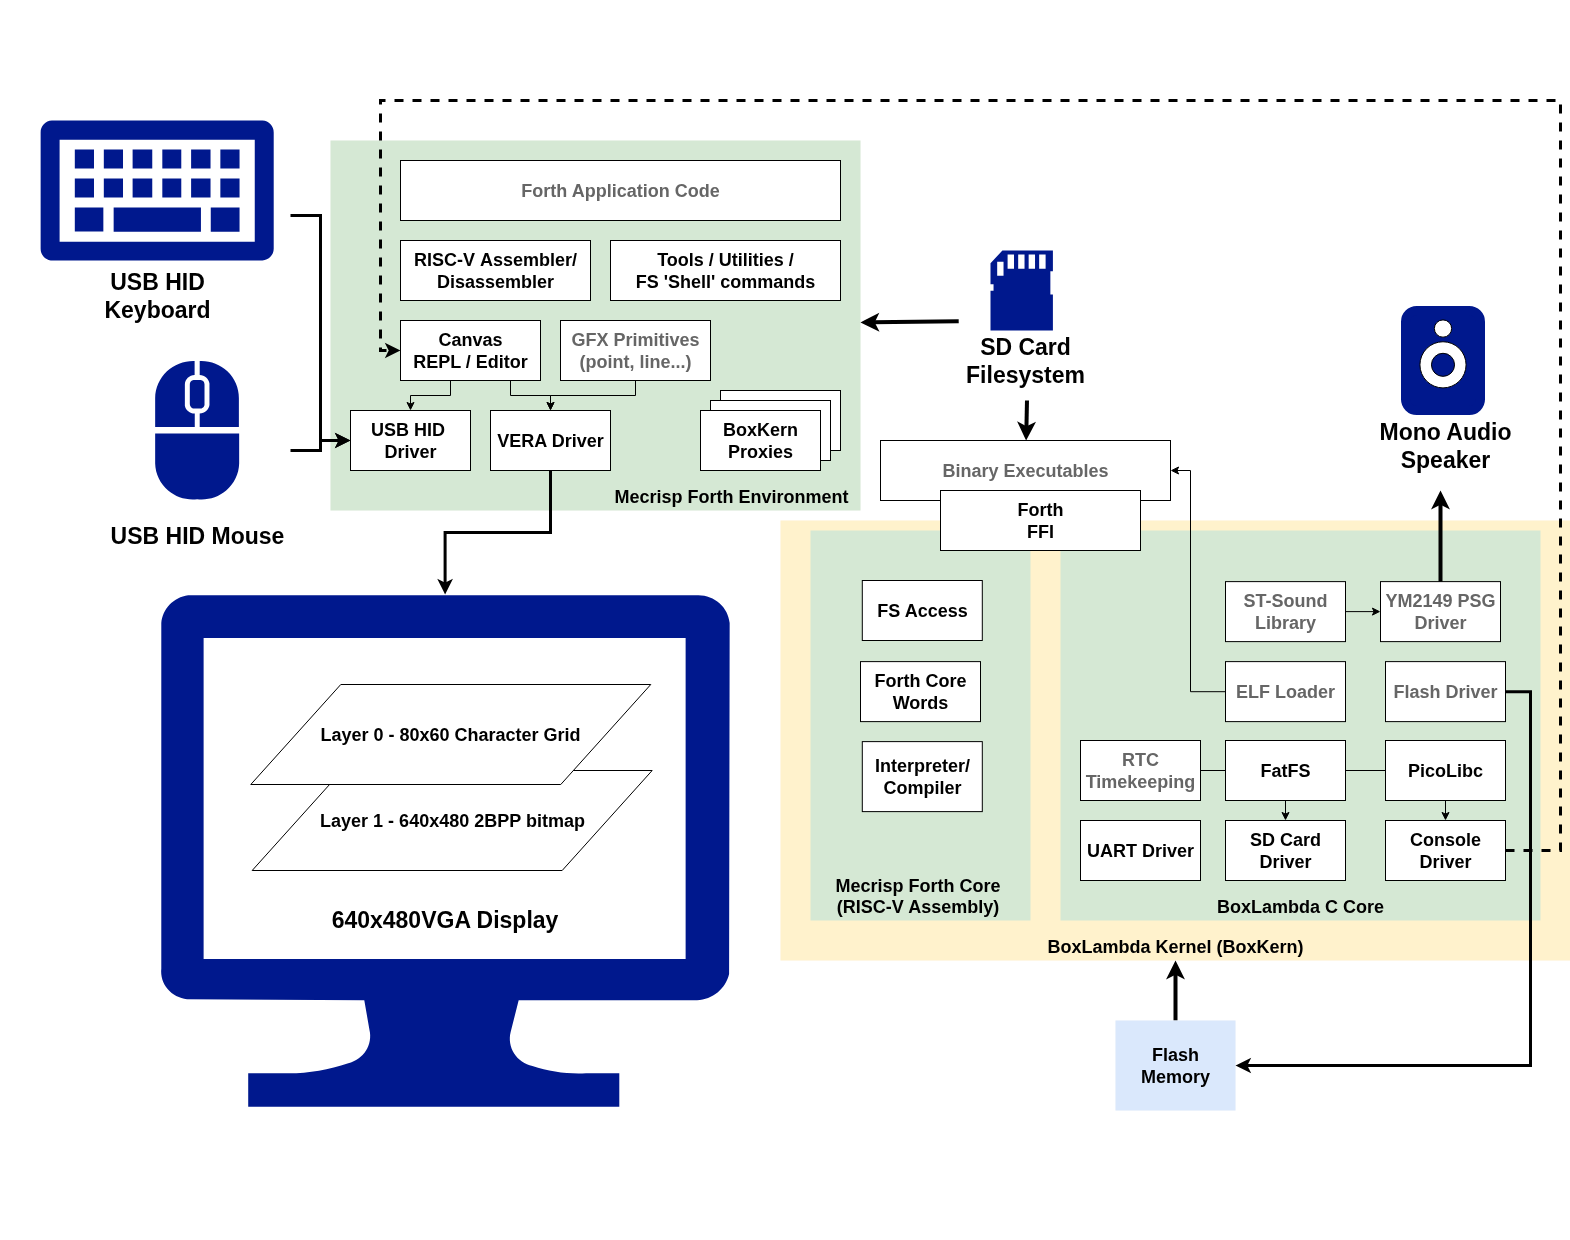 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation