
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
256 results
intel-me-research preview

intel-me-research

GitHubjatinkapilaq1/intel-me-research

Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…

binary-analysisembedded-systems-securityfirmware-analysis+4
15
1 month ago
PhaseDump preview

PhaseDump

GitHubmalwaretech/phasedump

Python tool for decrypting W32/Phase modules

binary-analysisencryption-decryption-toolsforensics+2
711 years ago
Total-Commander-FTP-Password-Recovery-Tool-Python preview

Total-Commander-FTP-Password-Recovery-Tool-Python

GitHubpelock/total-commander-ftp-password-recovery-tool-python

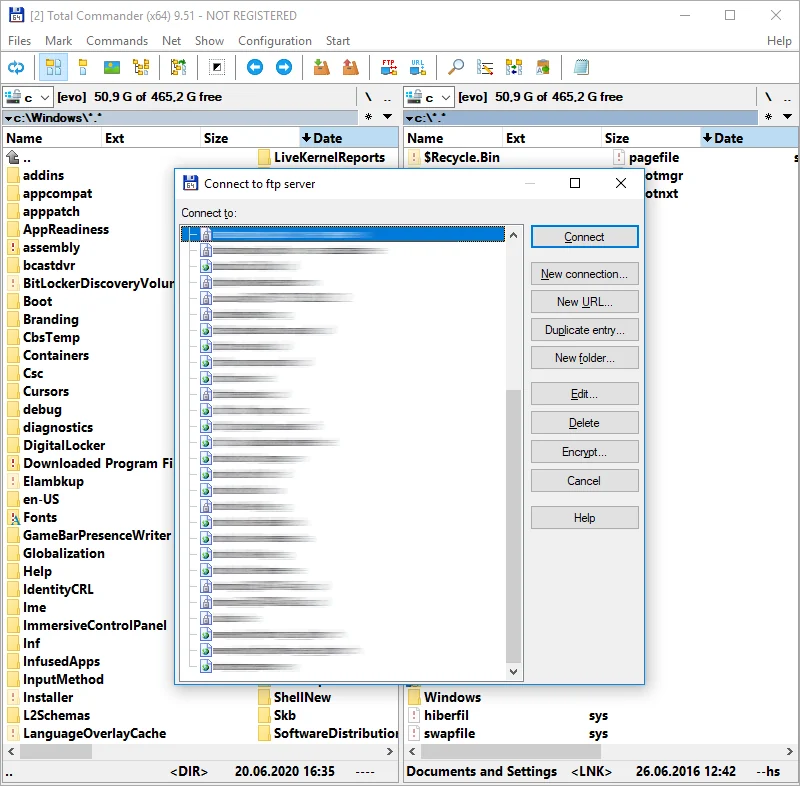
Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…

data-recoveryencryption-decryption-toolsforensics+2
14 months ago
pythia preview

pythia

GitHubnccgroup/pythia

A tool to extract RTTI information from Delphi executables, written in pure Python

binary-analysismalware-analysisreverse-engineering
257 years ago
themida-unmutate preview

themida-unmutate

GitHubergrelet/themida-unmutate

Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.

binary-analysisbinary-exploitationmalware-analysis+3
3902 years ago
flare-qdb preview
Archived

flare-qdb

GitHubmandiant/flare-qdb

Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.

binary-analysisdebuggersdynamic-analysis-sandboxing+3
1643 years ago
call_map preview

call_map

GitHubnccgroup/call_map

Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.

code-analysisreverse-engineeringstatic-code-analysis+1
298 years ago
Intensio-Obfuscator preview

Intensio-Obfuscator

GitHubhnfull/intensio-obfuscator

Obfuscate a python code 2.x and 3.x

code-analysiseducationreverse-engineering+1
6486 years ago
ghidrecomp preview

ghidrecomp

GitHubclearbluejar/ghidrecomp

Python Command-Line Ghidra Decompiler

binary-analysisreverse-engineeringstatic-code-analysis+1
1578 months ago
ipaforge preview

ipaforge

GitHubvighnesh91/ipaforge

Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…

binary-analysiscode-analysisios-security+6
9 days ago
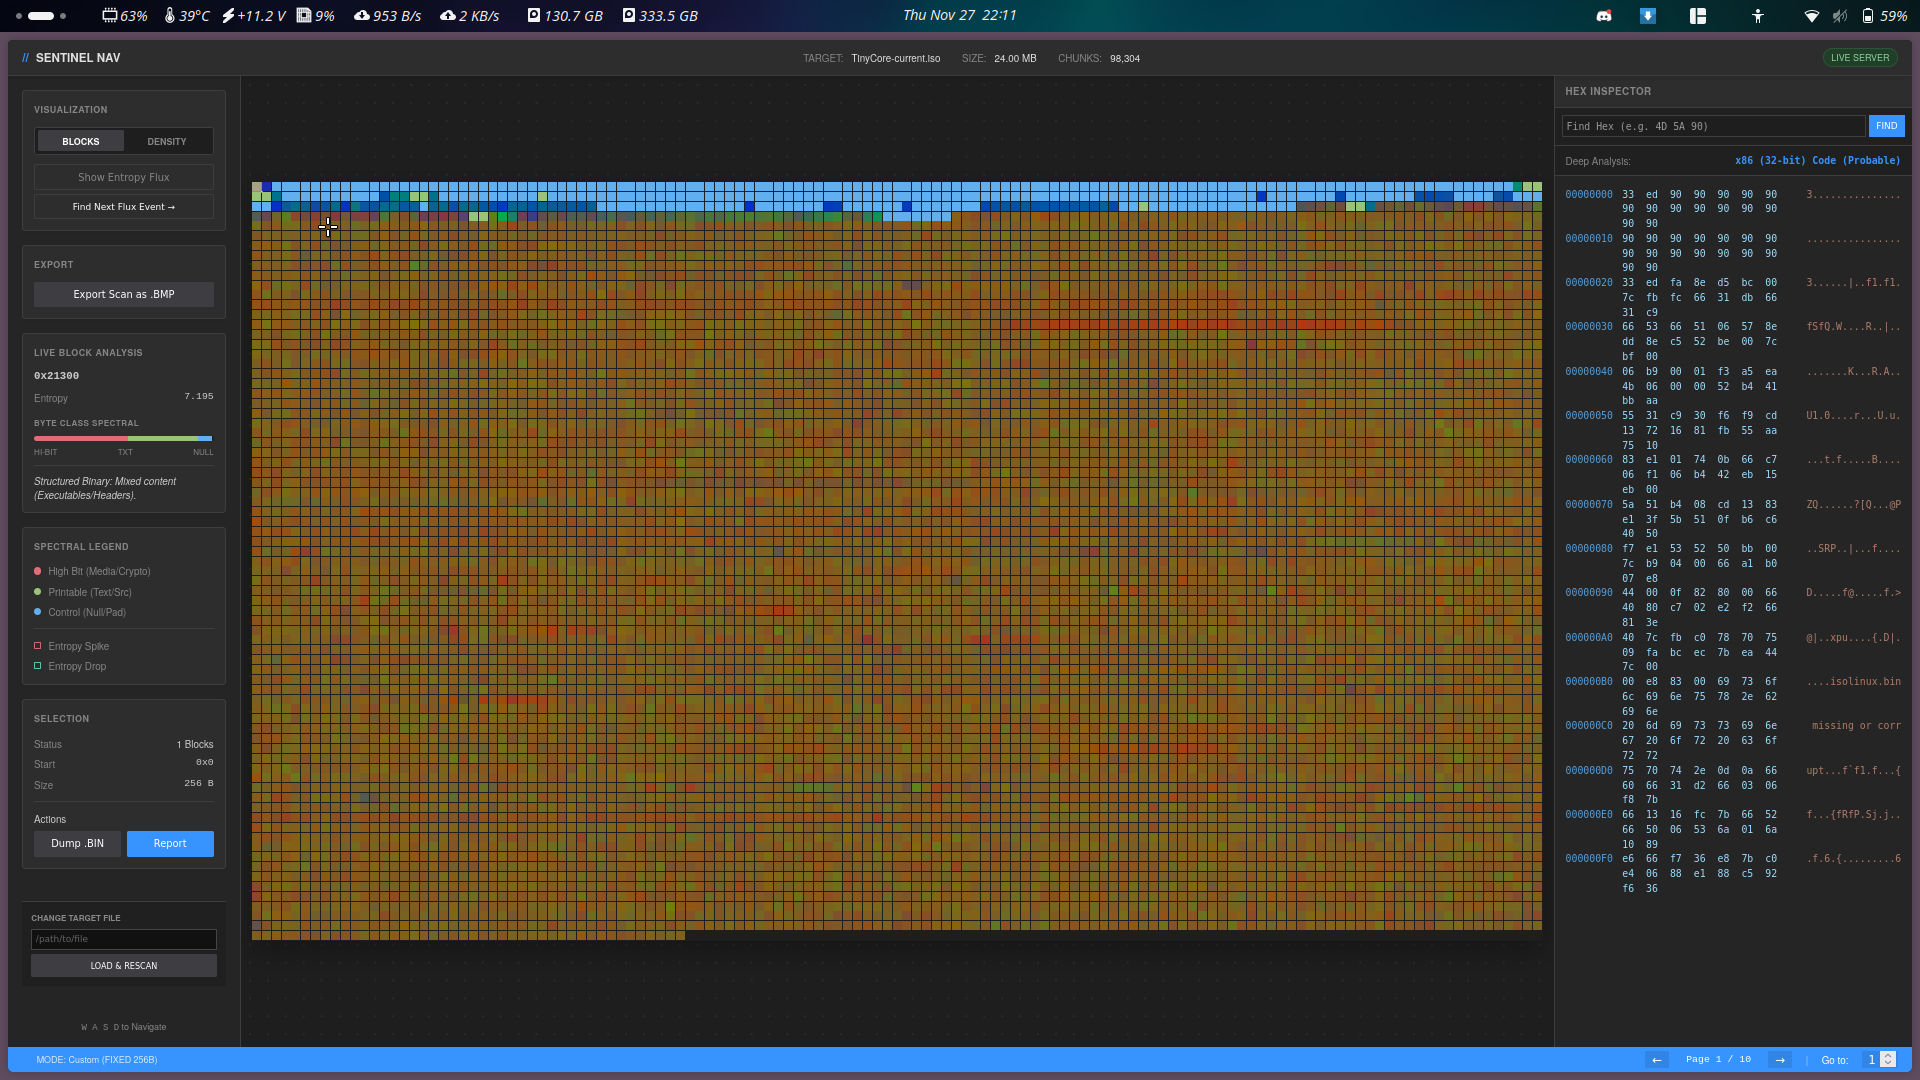
SentinelNav preview

SentinelNav

GitHubsmolfiddle/sentinelnav

SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.

binary-analysisdata-recoverydigital-forensics+4
1489 months ago
pecli preview

pecli

GitHubte-k/pecli

CLI tool to analyze PE files

binary-analysismalware-analysisreverse-engineering+1
902 years ago
TS_LLMLib preview

TS_LLMLib

GitHubtrustedsec/ts_llmlib

Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…

ai-securitybinary-analysiscode-analysis+7
13 months ago
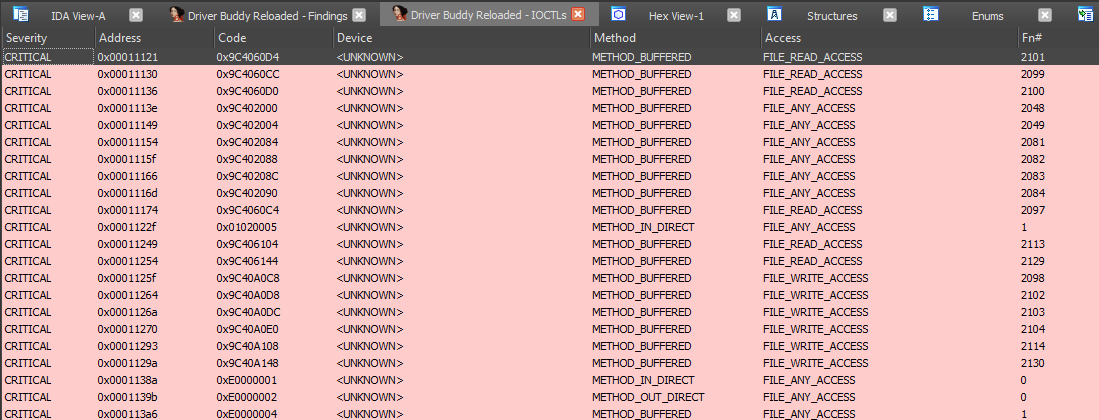
DriverBuddyReloaded preview

DriverBuddyReloaded

GitHubvoidsec/driverbuddyreloaded

Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks

binary-analysisdebuggersreverse-engineering+2
4642 months ago
filterforge preview

filterforge

GitHubcloudflare/filterforge

Tool for solving BPF filters and crafting packets based on these.

binary-analysisforensicsfuzzing+5
646 months ago
rePy2exe preview

rePy2exe

GitHub4w4k3/repy2exe

A Reverse Engineering Tool for py2exe applications.

binary-analysismalware-analysisreverse-engineering+1
2089 years ago
hackEmbedded preview

hackEmbedded

GitHubdoudoudedi/hackembedded

This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices

command-and-controlembedded-systems-securityencryption-decryption-tools+8
2062 months ago
NoMoreXOR preview

NoMoreXOR

GitHubhiddenillusion/nomorexor

Tool to help guess a files 256 byte XOR key by using frequency analysis

binary-analysiscryptographyforensics+3
908 years ago
Previous12…15Next