
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
26 results
bincrypter preview

bincrypter

GitHubhackerschoice/bincrypter

Pack/Encrypt/Obfuscate ELF + SHELL scripts
binary-analysisencryption-decryption-toolsmalware-analysis+2
4575 months ago
AntiCheat-Testing-Framework preview

AntiCheat-Testing-Framework

GitHubniemand-sec/anticheat-testing-framework

Framework to test any Anti-Cheat

educationexploit-frameworksreverse-engineering
8226 years ago
ROPInjector preview

ROPInjector

GitHubgpoulios/ropinjector

Patching ROP-encoded shellcodes into PEs

binary-analysisbinary-exploitationexploitation+7
1868 years ago
IPA preview

IPA

GitHubseekbytes/ipa

GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…

binary-analysisdefensive-toolsdigital-forensics+6
8822 years ago
CVE-2026-9490 preview

CVE-2026-9490

GitHubugvxb/cve-2026-9490

The ACCSvc service creates a Named Pipe with a weak Security Descriptor that allows any authenticated user to connect and send messages. When a…
binary-analysisexploitationpenetration-testing+3
4 months ago
CVE-2026-9789 preview

CVE-2026-9789

GitHubugvxb/cve-2026-9789

A critical local privilege escalation vulnerability has been discovered in Acer NitroSense software (PSAdminAgent.exe). The vulnerability allows any…

binary-analysiseducationexploitation+3
4 months ago
icebox preview

icebox

GitHubthalium/icebox

Virtual Machine Introspection, Tracing & Debugging
debuggersdynamic-analysis-sandboxingforensics+3
6014 years ago
unblob preview

unblob

GitHubonekey-sec/unblob

Extract files from any kind of container formats
binary-analysisdata-recoveryembedded-systems-security+3
2.6k16h 15m ago
apxutil preview

apxutil

GitHubfinngineering/apxutil

A tool to manipulate Schneider Electric PLC archive files
binary-analysisembedded-systems-securityexploitation+5
118 months ago
Transformers-Forged-To-Fight-Offline-Version preview

Transformers-Forged-To-Fight-Offline-Version

GitHubgeamztheangrybirds727/transformers-forged-to-fight-offline-version

TRANSFORMERS: Forged to Fight is a 3D combat game where you take over some of the most charismatic troopers straight out of the Transformers…
binary-analysisbinary-exploitationcurated-resources+5
33 months ago
universal-flutter-ssl-pinning preview

universal-flutter-ssl-pinning

GitHubvichhka-git/universal-flutter-ssl-pinning

Automated SSL pinning bypass for any Flutter & Shorebird version — PyGhidra static analysis auto-discovers BoringSSL and generates ready-to-run Frida…
binary-analysisdynamic-analysis-sandboxingmobile-security+4
681 month ago
Android-Disassembler preview

Android-Disassembler

GitHubyhs0602/android-disassembler

Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
android-securitybinary-analysisdebuggers+4
7166 months ago
IDA2Obj preview

IDA2Obj

GitHubjhftss/ida2obj

Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
binary-analysisdebuggersfuzzing+2
1225 years ago
react preview

react

GitHubjanhalendk/react

A OSINT project that explores how to dump data from React
educationinformation-gatheringosint+2
821 year ago
WDExtract preview

WDExtract

GitHubhfiref0x/wdextract

Extract Windows Defender database from vdm files and unpack it
binary-analysisencryption-decryption-toolsforensics+2
4945 months ago
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

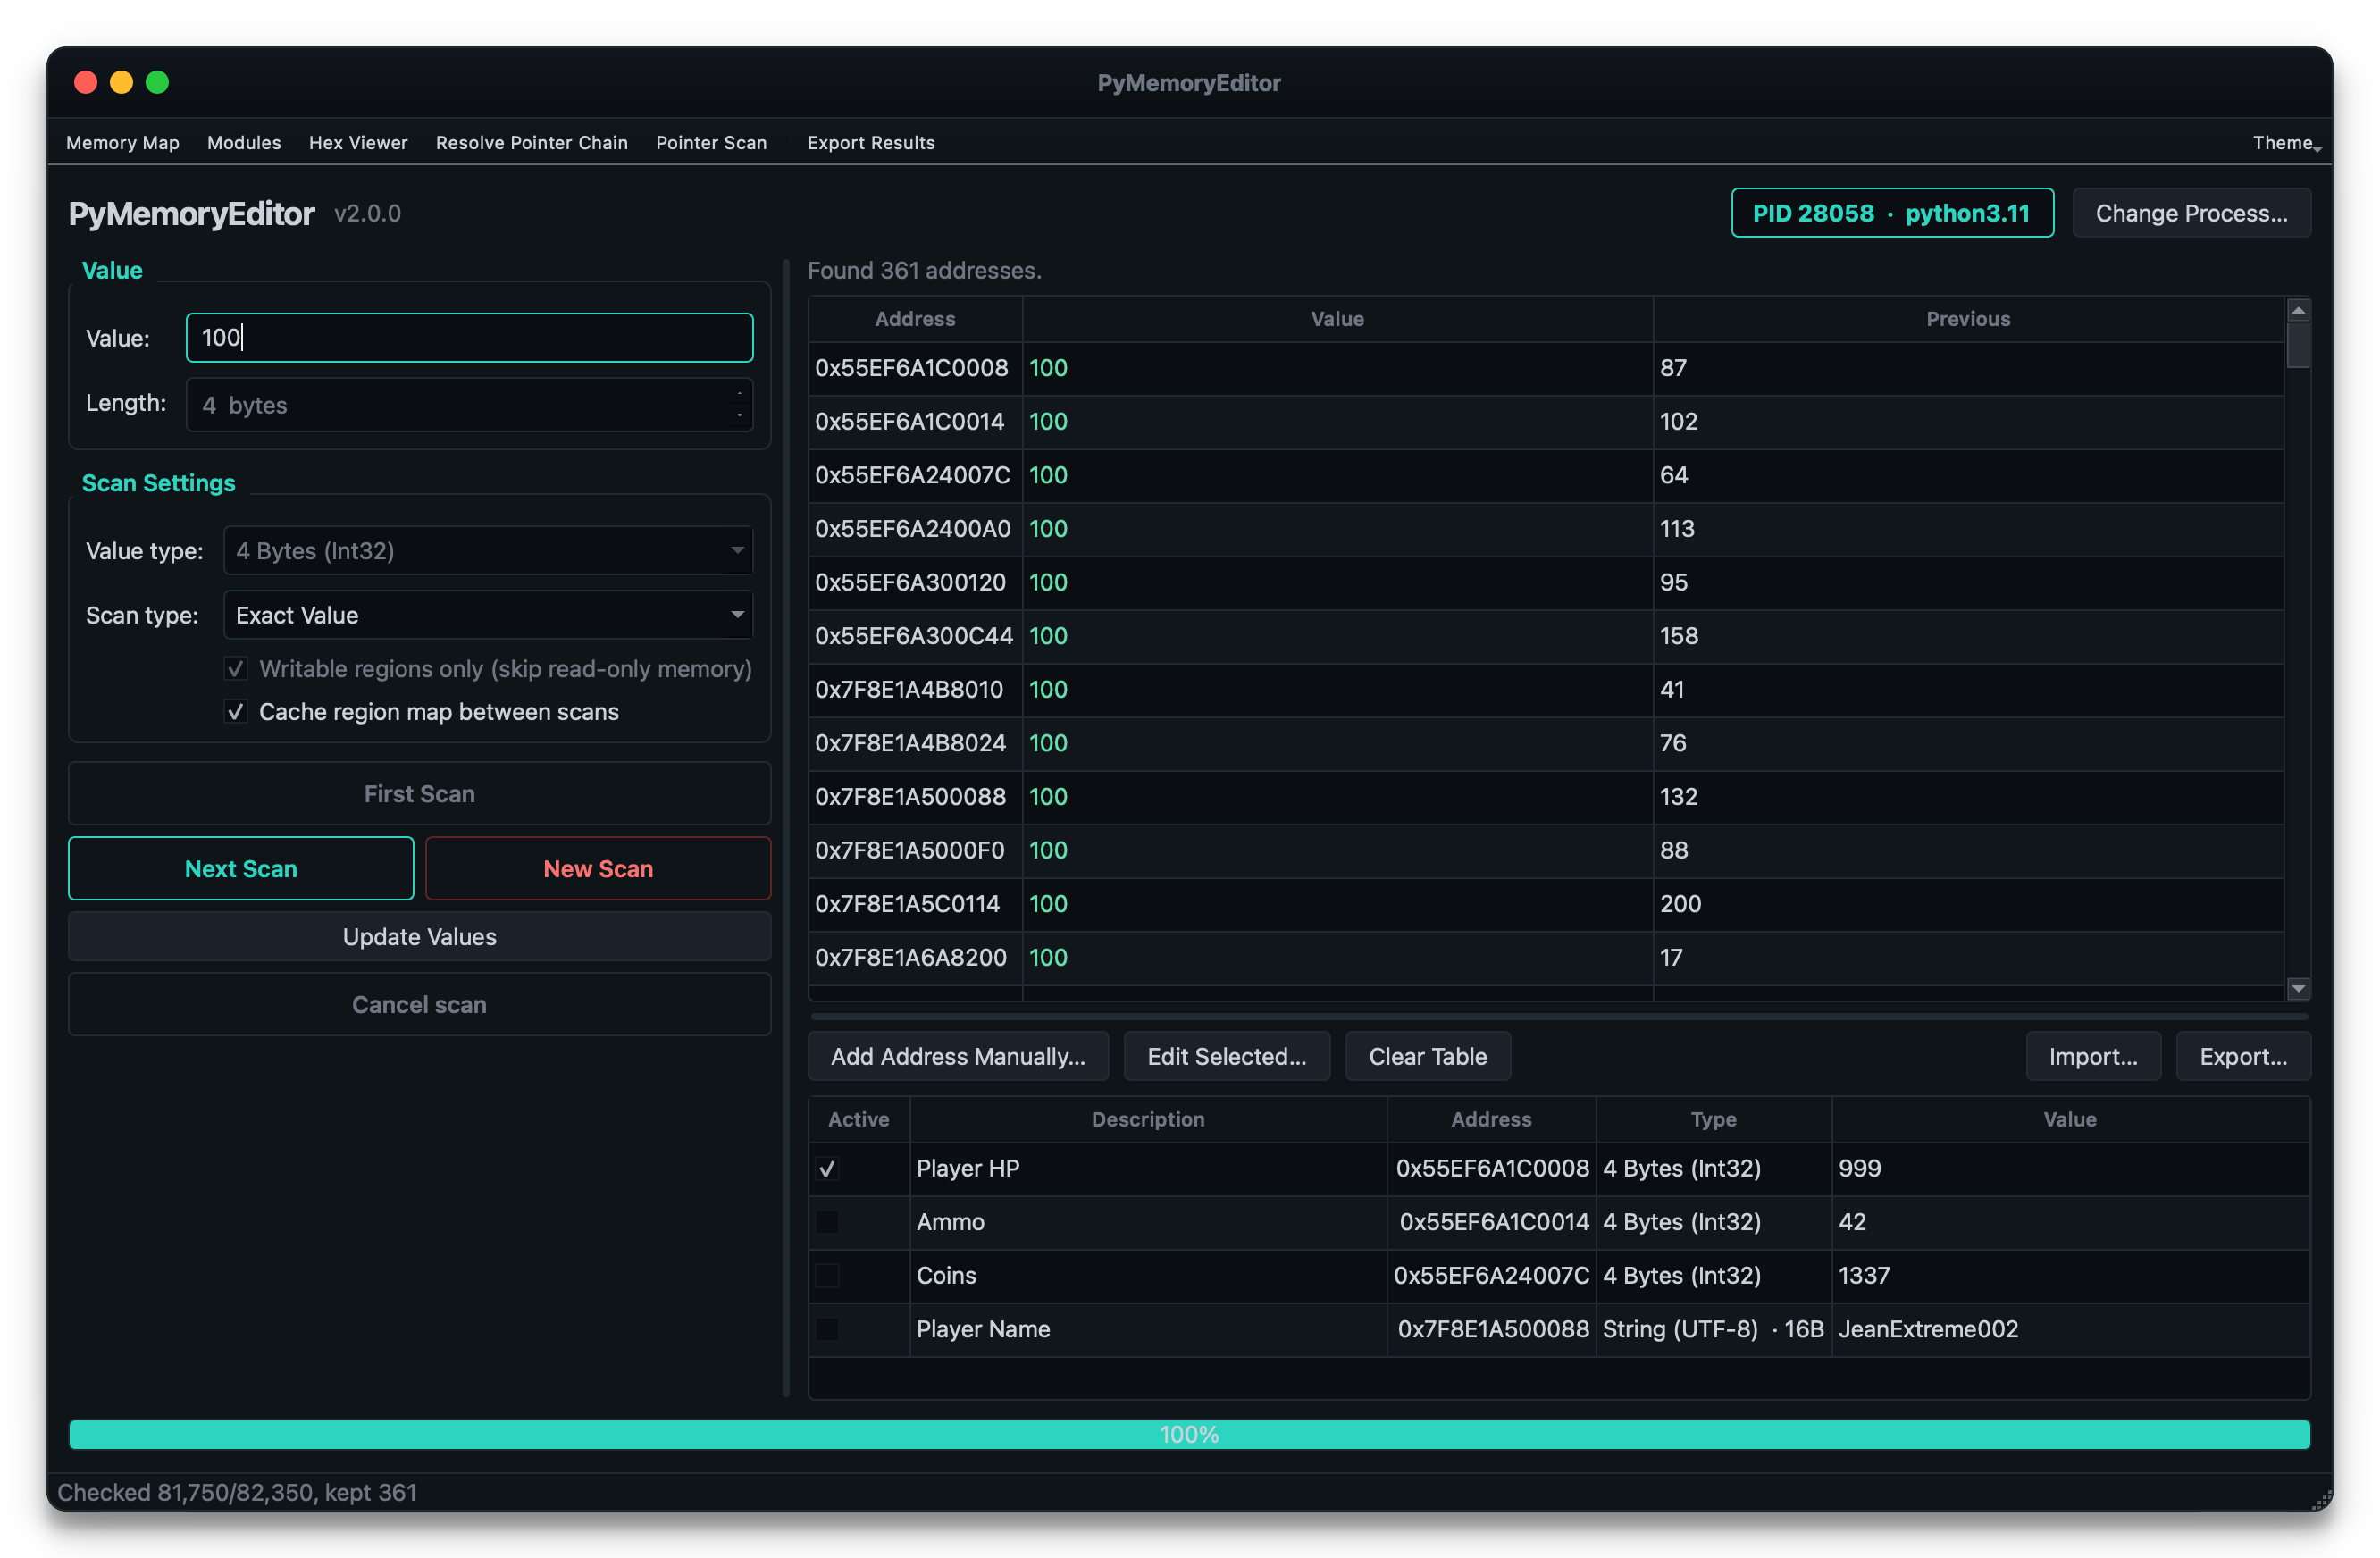
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
binary-analysisdebuggerseducation+3
2223 days ago
incarcero preview

incarcero

GitHub0x48piraj/incarcero

Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis…
cloud-securitycurated-resourcesdynamic-analysis-sandboxing+4
922 years ago
pe-signgen preview

pe-signgen

GitHubforentfraps/pe-signgen

Universal signature generation for any system function from all Windows Builds using Winbindex

binary-analysisforensicsmalware-analysis+3
199 months ago
Previous12Next