
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
261 results
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
binary-analysisforensicsmalware-analysis+2
3.9k
3 months ago
Manalyze preview

Manalyze

GitHubjusticerage/manalyze

Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…

binary-analysismalware-analysisreverse-engineering+2
1.1k1 month ago
Inspeckage preview

Inspeckage

GitHubac-pm/inspeckage

Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)

android-securityapi-security-testingdynamic-analysis-sandboxing+2
3.0k8 years ago
mtkclient preview

mtkclient

GitHubbkerler/mtkclient

Mediatek Flash and Repair Utility

android-securitydata-recoveryembedded-systems-security+5
1.3k20 days ago
LFISuite preview

LFISuite

GitHubd35m0nd142/lfisuite

Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner

exploitationpayload-generationpenetration-testing+3
2.0k8 years ago
tiny_tracer preview

tiny_tracer

GitHubhasherezade/tiny_tracer

Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
api-securitybinary-analysisdynamic-analysis-sandboxing+2
1.7k4 months ago
binsync preview

binsync

GitHubbinsync/binsync

A reversing plugin for cross-decompiler collaboration, built on git.
binary-analysisreverse-engineeringstatic-analysis+1
7451 month ago
pwninit preview

pwninit

GitHubio12/pwninit

Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
binary-exploitationctfexploitation+2
1.1k2 months ago
sickle-pdk preview

sickle-pdk

GitHubwetw0rk/sickle-pdk

Sickle - Payload Development Kit
binary-analysisexploitationexploit-frameworks+3
8702 months ago
Mergen preview

Mergen

GitHubnac-l/mergen

Deobfuscation via optimization with usage of LLVM IR and parsing assembly.
binary-analysisbinary-exploitationdynamic-analysis-sandboxing+2
9064 months ago
CallObfuscator preview

CallObfuscator

GitHubd35ha/callobfuscator

Obfuscate specific windows apis with different apis

binary-analysisdefensive-toolsdynamic-analysis-sandboxing+4
1.0k5 years ago
Intensio-Obfuscator preview

Intensio-Obfuscator

GitHubhnfull/intensio-obfuscator

Obfuscate a python code 2.x and 3.x
code-analysiseducationreverse-engineering+1
6486 years ago
shellen preview

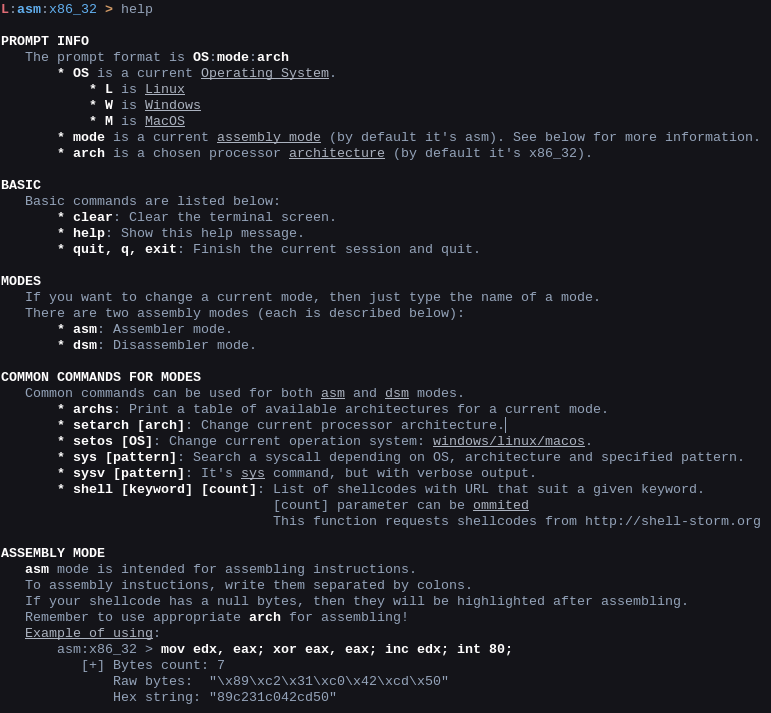
shellen

GitHubkonatabrk/shellen

:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
binary-analysisctfeducation+5
9085 years ago
pe-bear-old preview

pe-bear-old

GitHubhasherezade/pe-bear-old

PE-bear (builds only)
binary-analysismalware-analysisreverse-engineering
7763 years ago
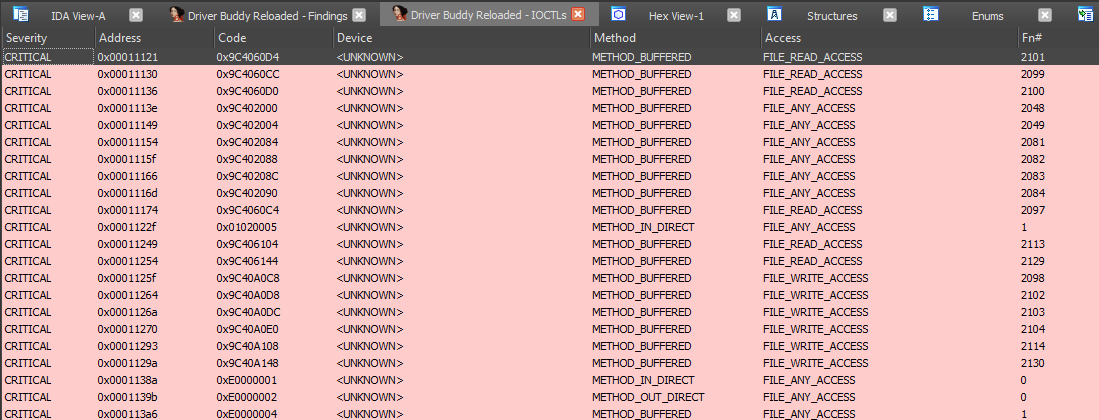
DriverBuddyReloaded preview

DriverBuddyReloaded

GitHubvoidsec/driverbuddyreloaded

Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
binary-analysisdebuggersreverse-engineering+2
4672 months ago
applepie preview

applepie

GitHubgamozolabs/applepie

A hypervisor for fuzzing built with WHVP and Bochs
binary-analysisdynamic-analysis-sandboxingfuzzing+2
3857 years ago
View8 preview

View8

GitHubsuleram/view8

Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
binary-analysismalware-analysisreverse-engineering+2
3792 months ago
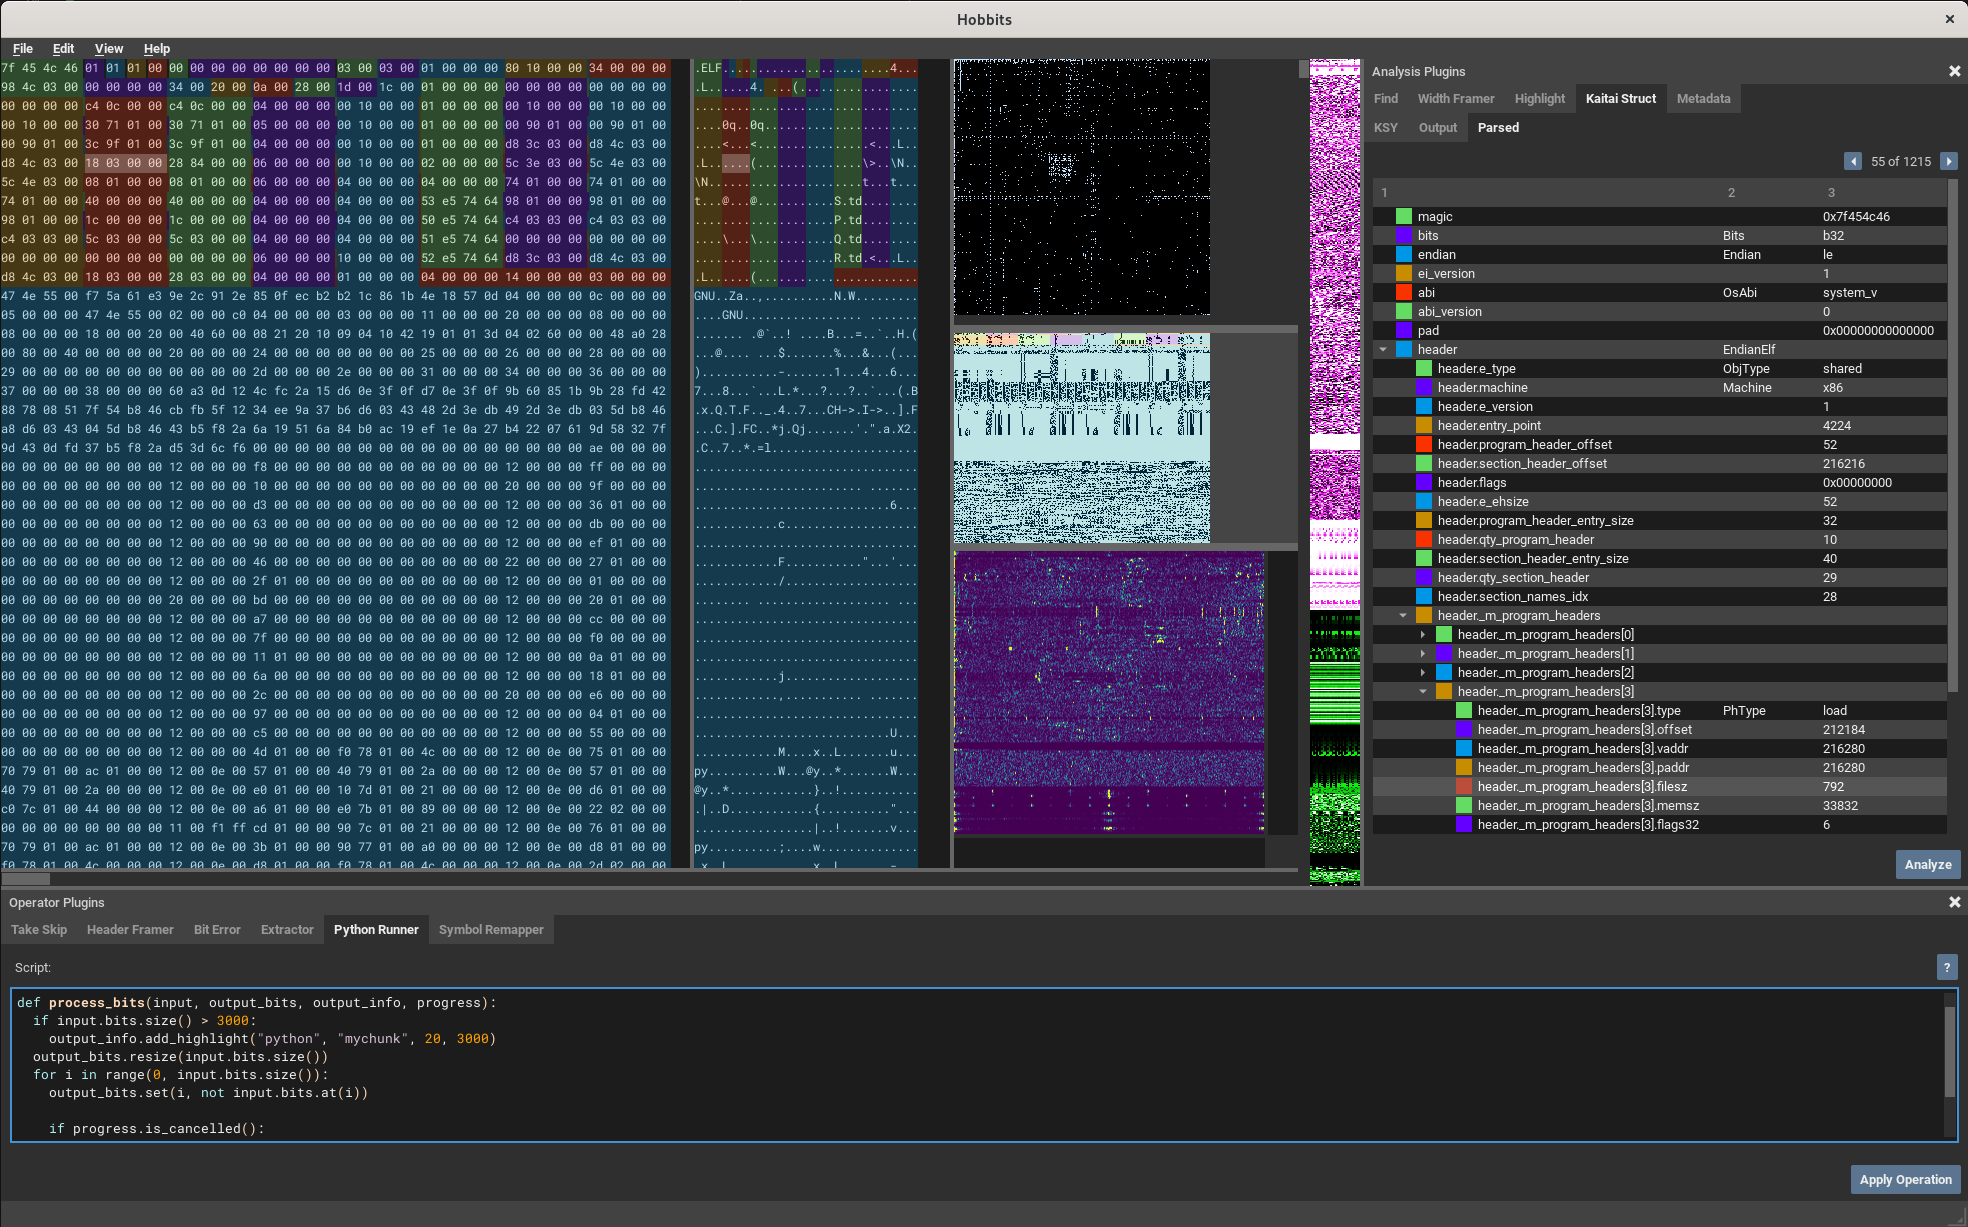
hobbits preview

hobbits

GitHubmahlet-inc/hobbits

A multi-platform GUI for bit-based analysis, processing, and visualization

binary-analysisdata-recoveryforensics+1
7541 year ago
Previous1…8910…15Next