

ReflectivePluginLoader
 racoten/reflectivepluginloader
A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
binary-exploitationdefensive-toolseducation+7
47
racoten/reflectivepluginloaderA minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
 zx0cf1/shredder-rs
A high-fidelity x86_64 polymorphic mutation engine focused on instruction-level fragmentation and context preservation.
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.
 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 mainframed/dc30_workshop
DEFCON 30 Mainframe buffer overlow workshop container
 m0n1x90/elfxtract
Automated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…
 ffri/shadebios
PoC code of Shade BIOS (stripped) presented at Black Hat USA 2025
 bedrock-safeguard/gentlemen-decryptor
First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
 do4choo/cve-2026-3227-tp-link-authenticated-rce
Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…
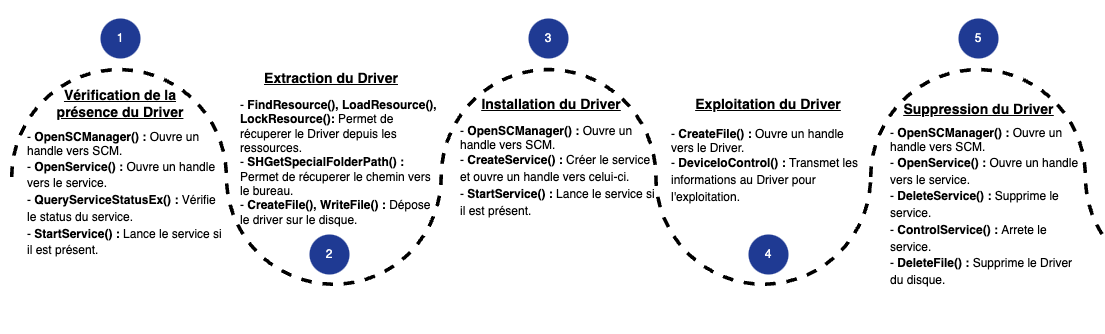 alex3o/byovd-driverkiller
Driver Reverse & Exploitation
 witherornot/warbird-docs
Documentation of Microsoft's Warbird obfuscation
 uoftctf/uoftctf-2025-chals-public
Challenge handouts, source code, and solutions for UofTCTF 2025
 nicholasaleks/infected-drones
A collection of vulnerabilities & exploits against modern GCS
 janhalendk/react
A OSINT project that explores how to dump data from React
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.
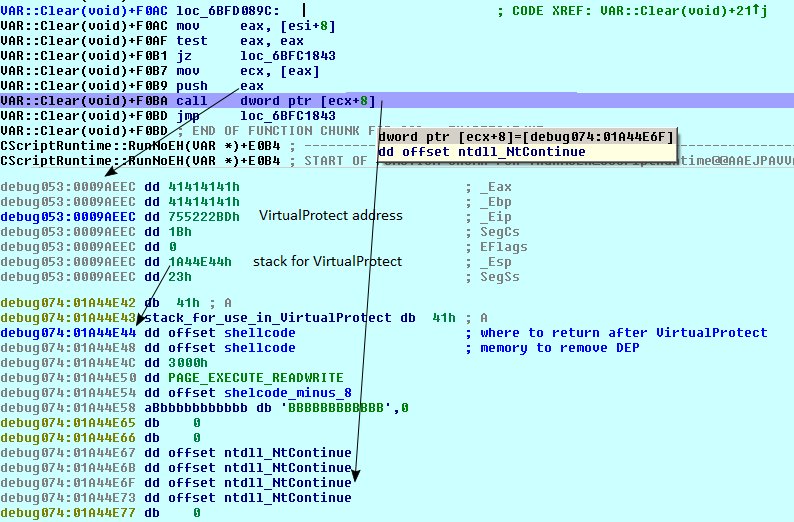 piotrflorczyk/cve-2018-8174_analysis
Analysis of VBS exploit CVE-2018-8174
 matheuzsecurity/nullsection
ELF anti-reversing tool that overwrites section headers with nullbytes to prevent static analysis by disassemblers and debuggers, rendering functions…