

MalConfig
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
android-securitycommand-and-controlinformation-gathering+3
7
jacobsoo/malconfigThis is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 darioi/droidcarve
Android Reverse Engineering Framework
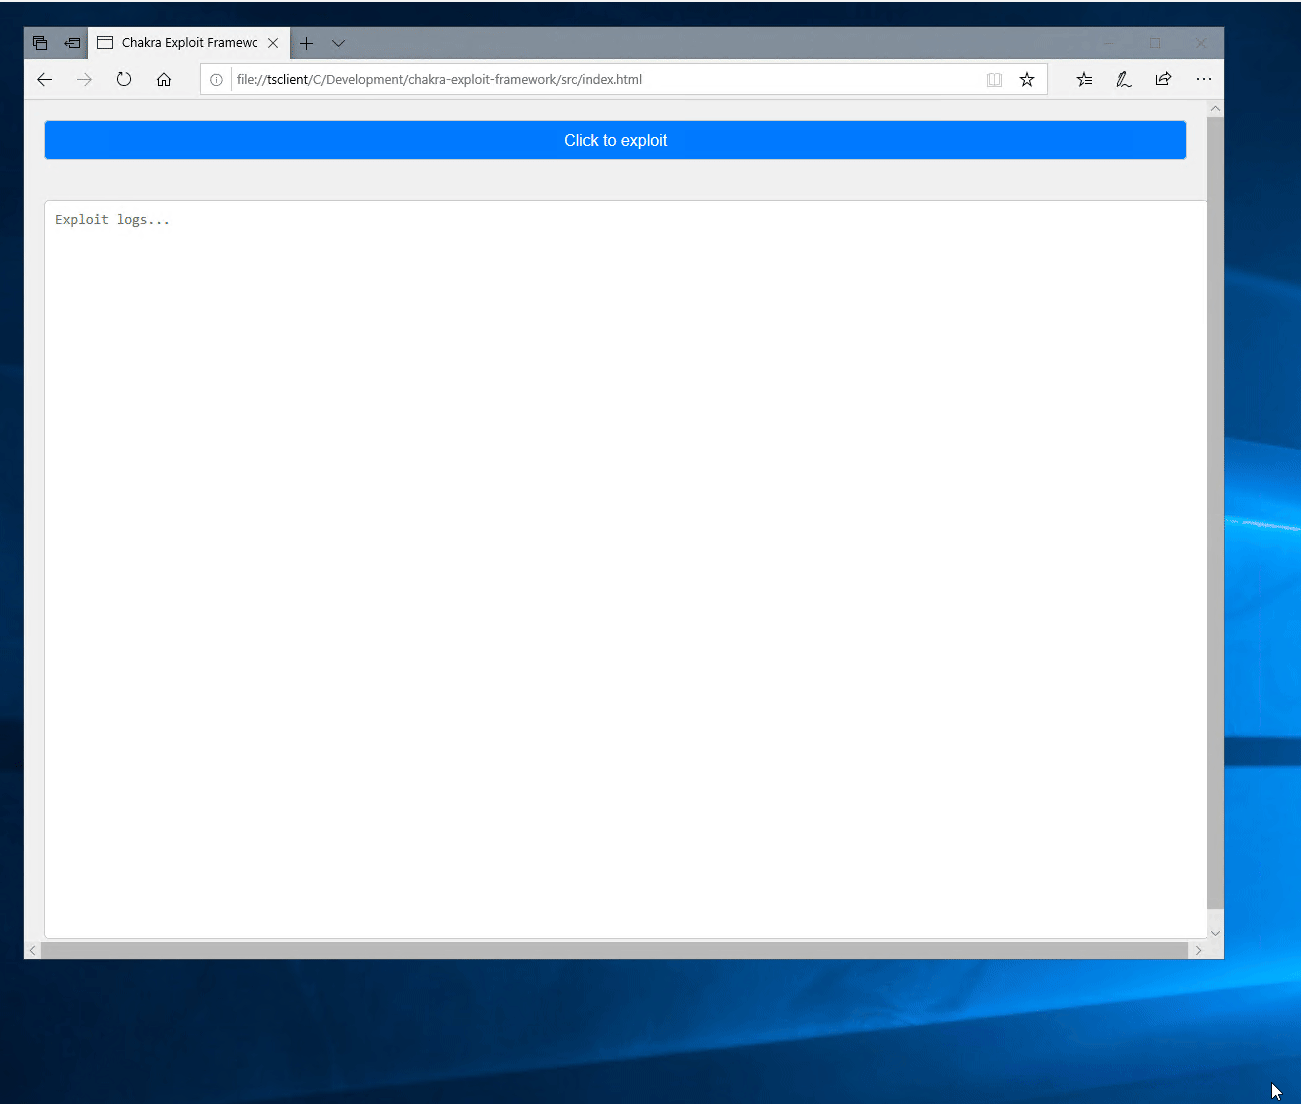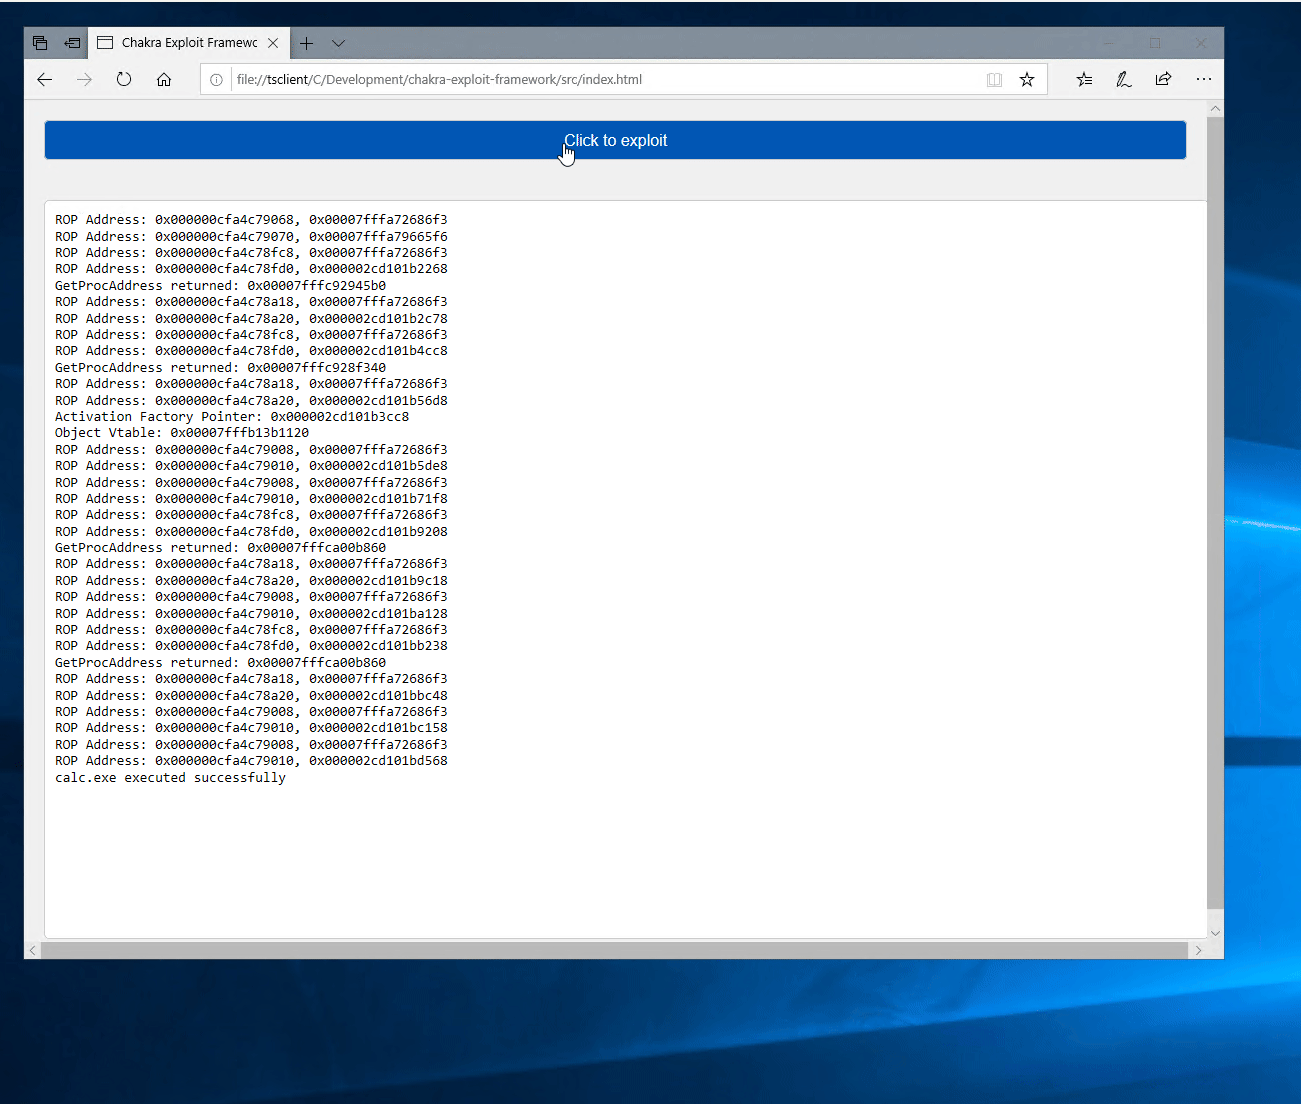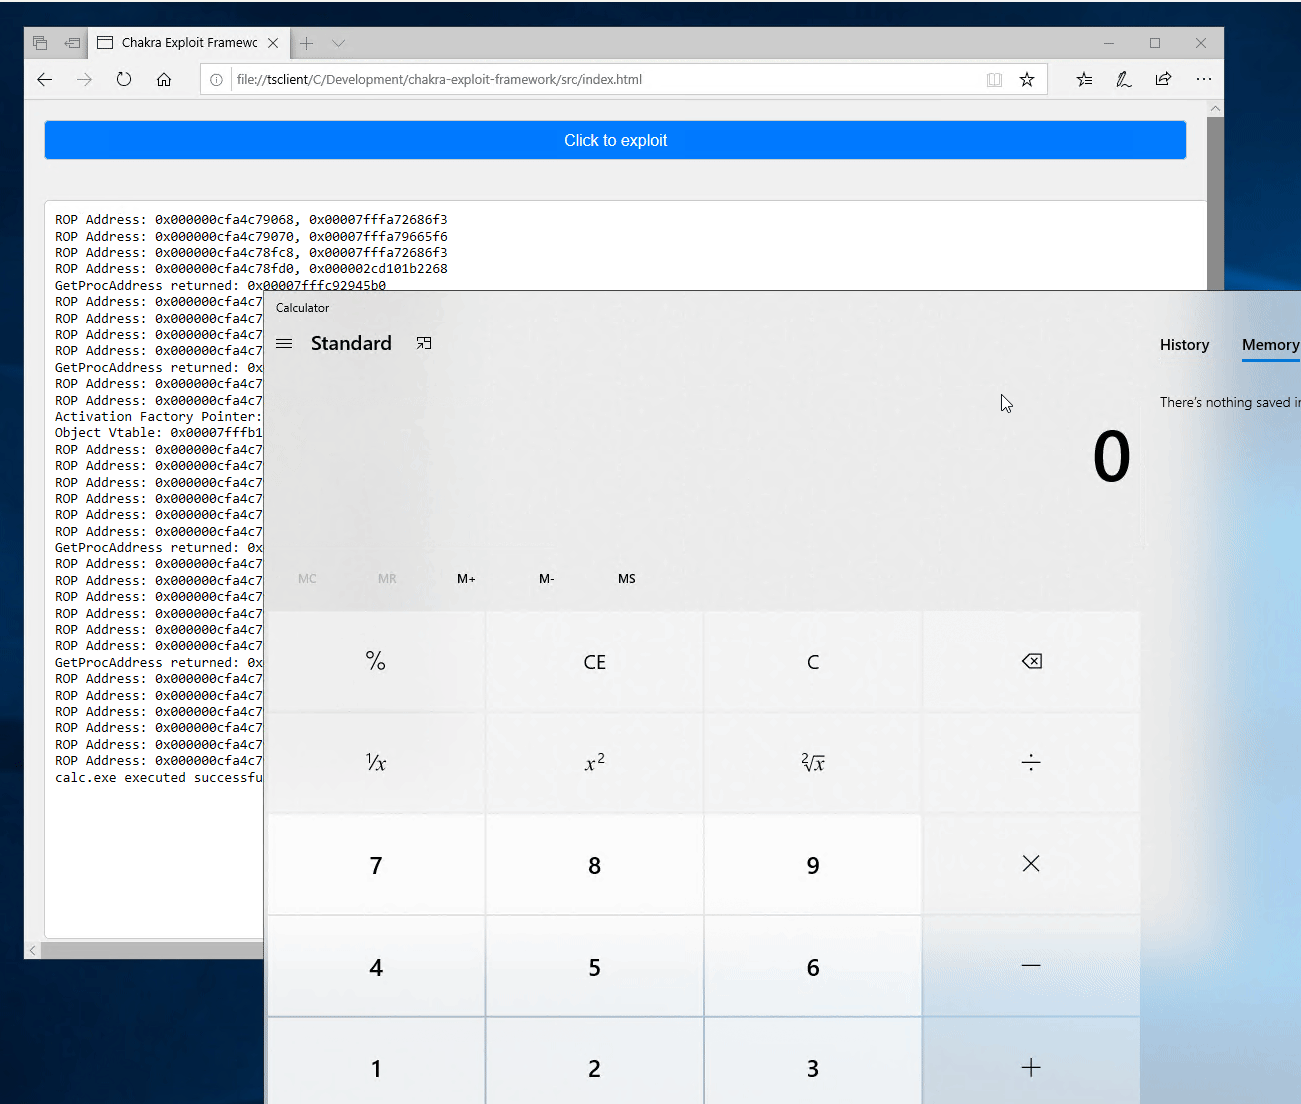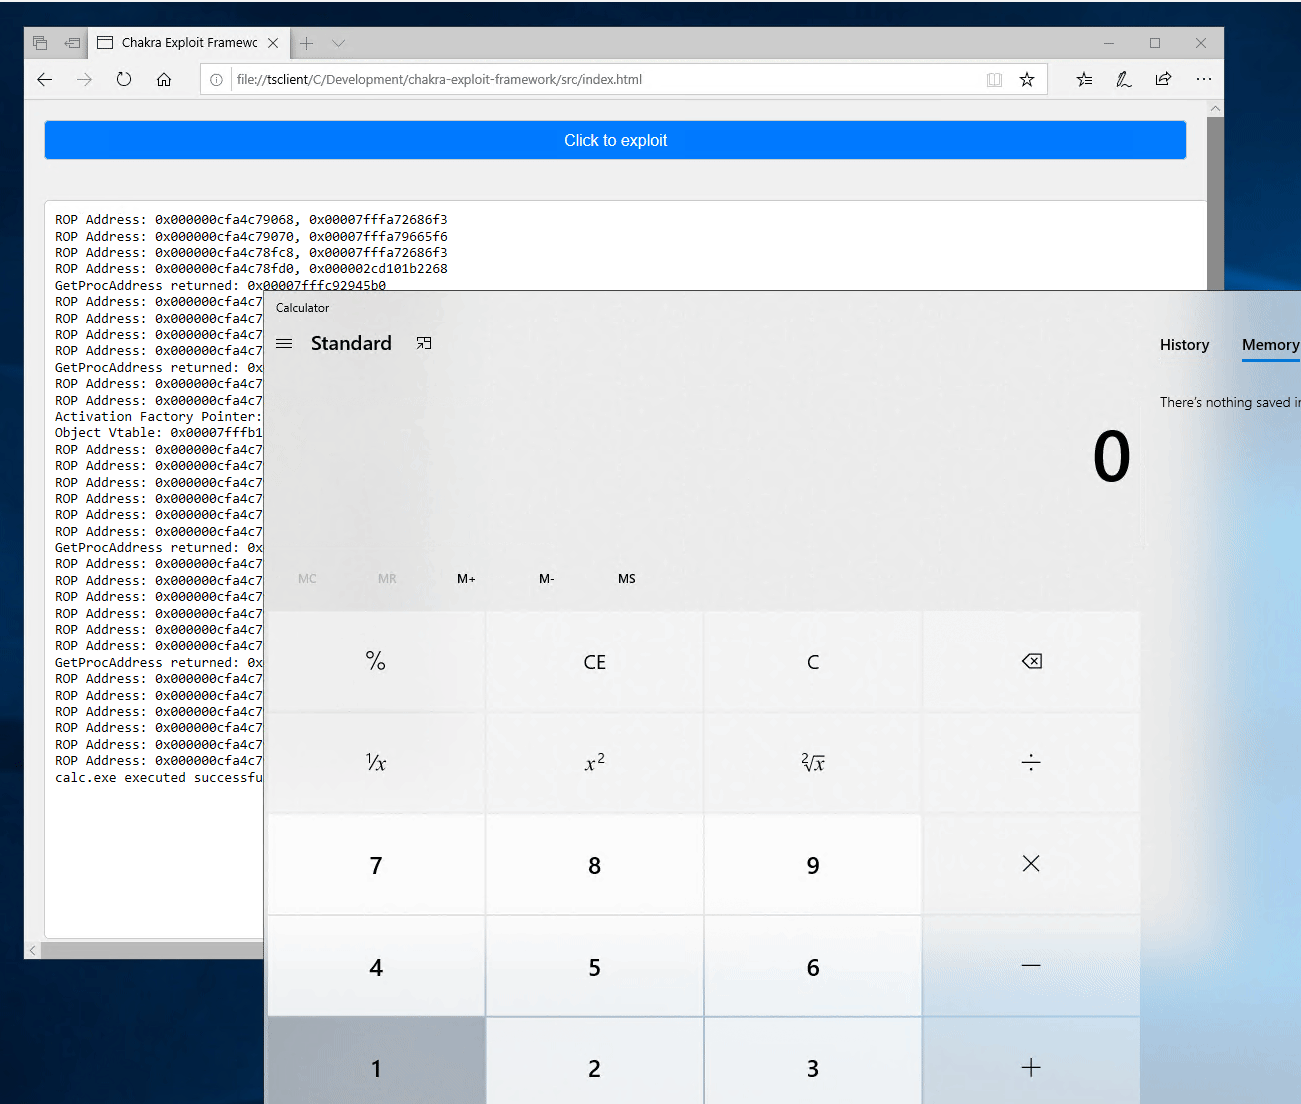 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 ptswarm/reflutter
Flutter Reverse Engineering Framework
 volatilityfoundation/volatility
An advanced memory forensics framework
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
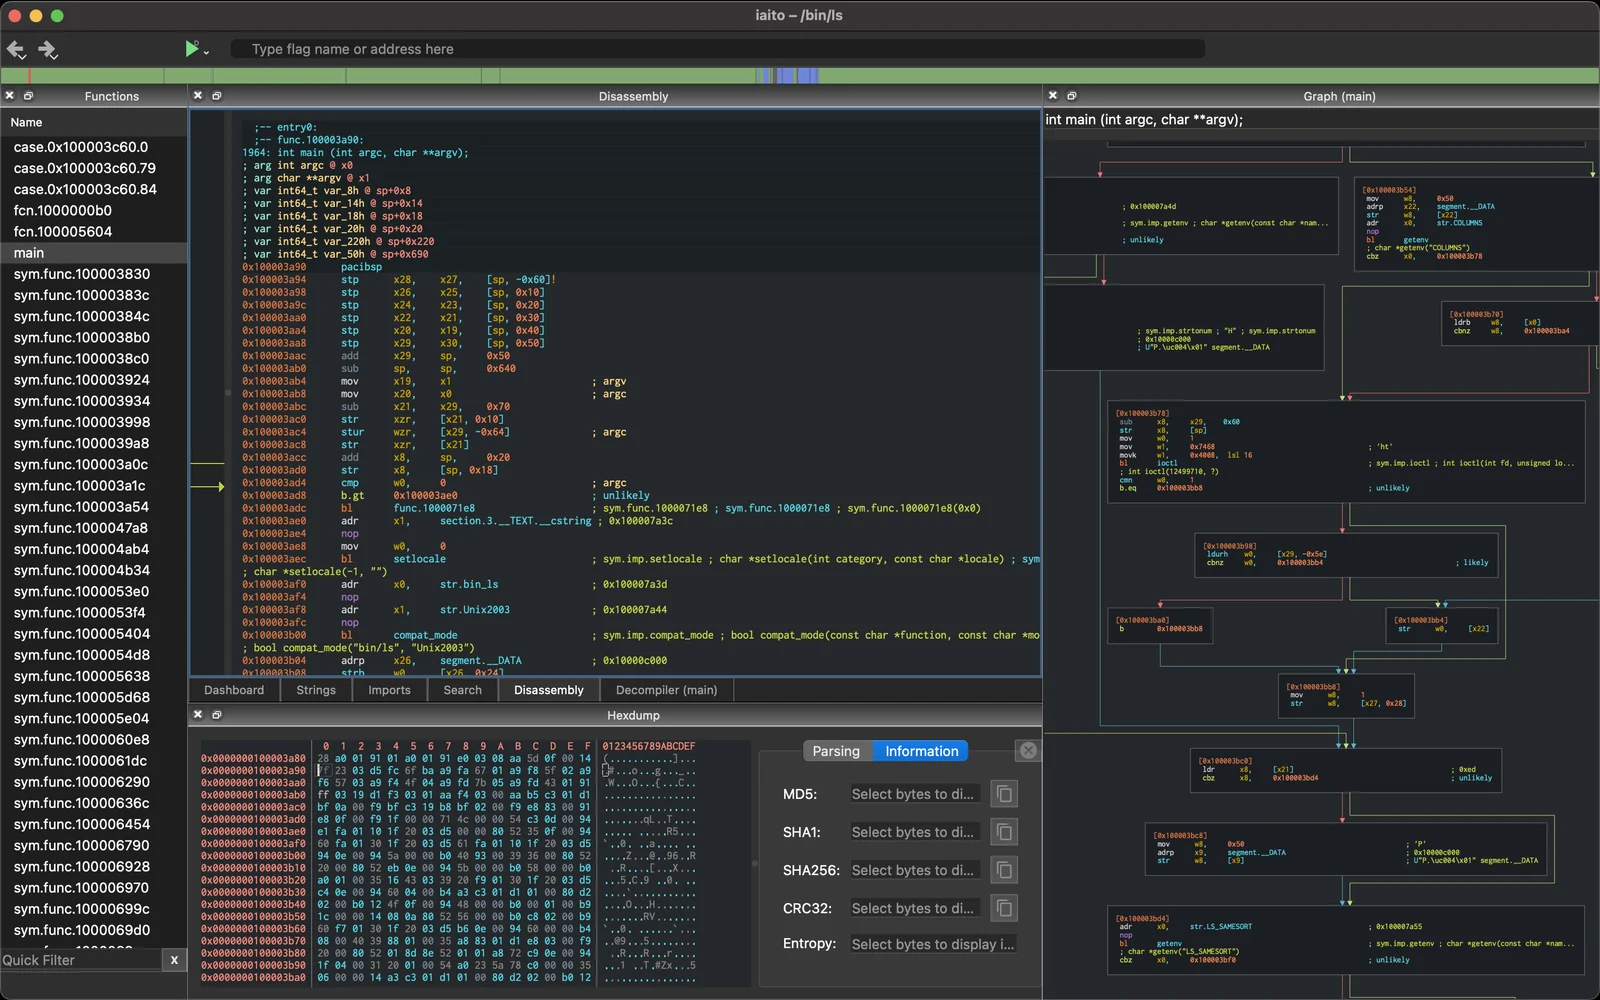 radareorg/iaito
Qt-based graphical interface for the radare2 reverse engineering framework, providing disassembly, binary analysis, debugging, patching and forensics…
 34zy/cve-2026-86950
Exploitation framework for CVE-2026-86950, a CoreGraphics integer overflow: crafts malicious TrueType fonts and PDFs, extracts ASLR leaks, and builds…
 carpedm20/awesome-hacking
A curated list of awesome Hacking tutorials, tools and resources
 angr/angr
A powerful and user-friendly binary analysis platform!
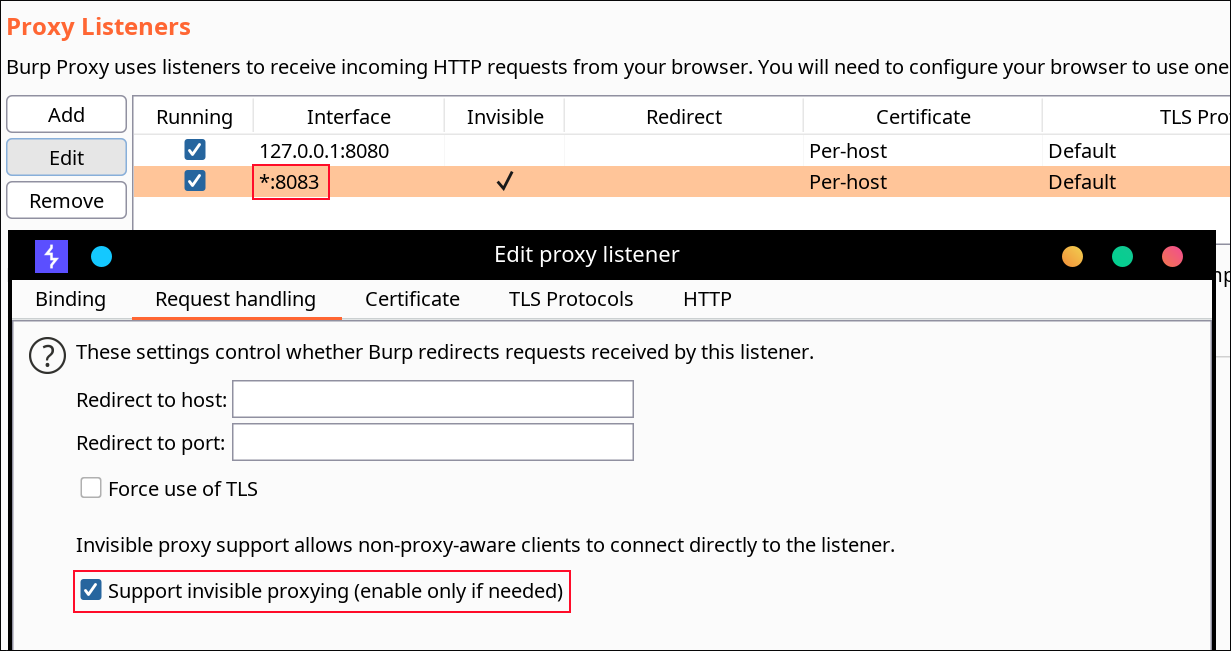 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
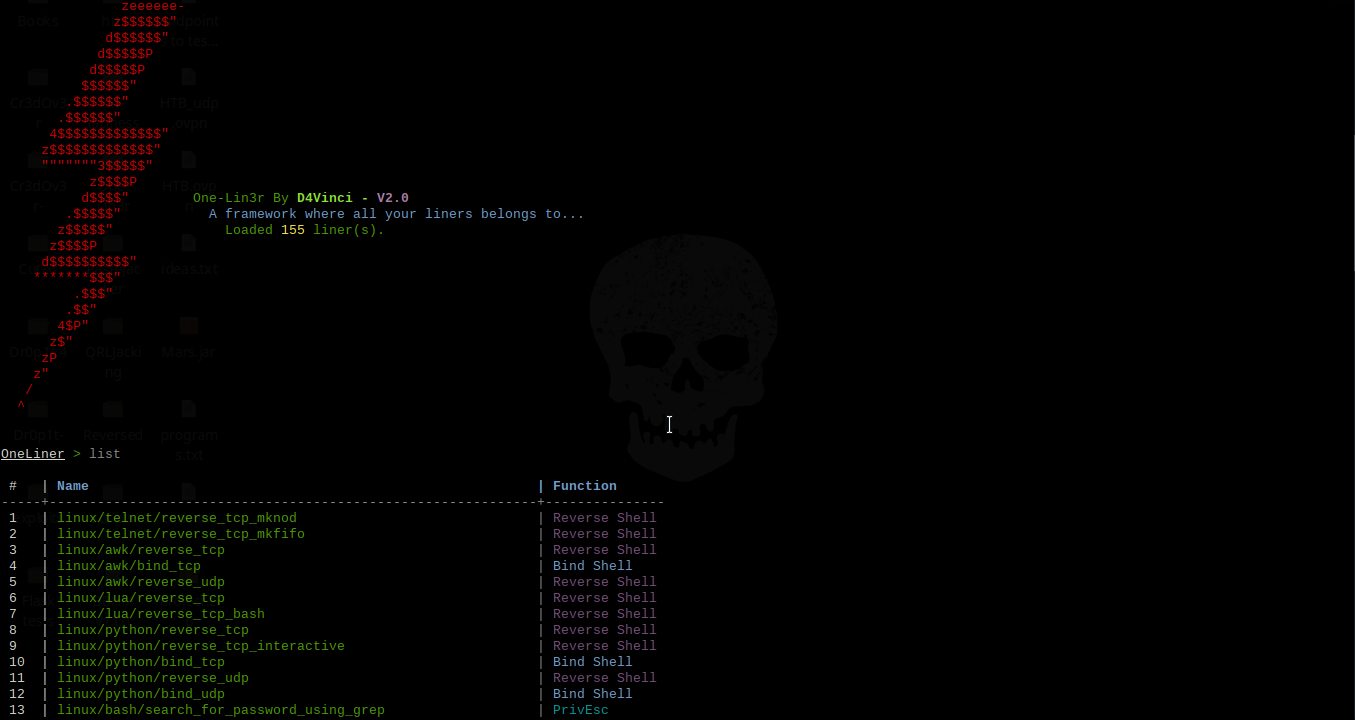 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
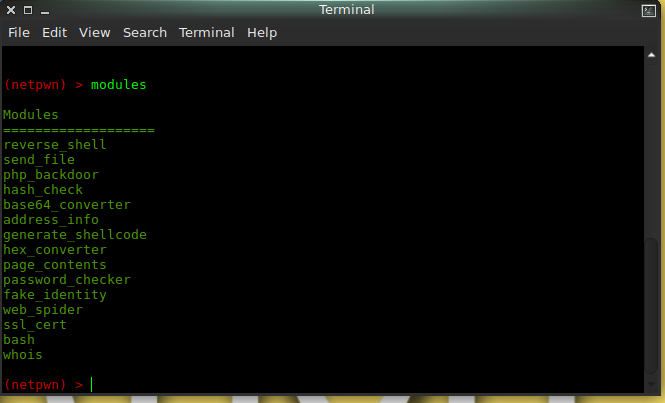 andromeda1957/netpwn
Tool made to automate tasks of pentesting.
 ch0pin/rdx
A native APK and DEX decompiler written in Rust