FlowName
 123wwwa/flowname
Next-generation JavaScript identifier recovery with LLMs.
ai-assisted-reversingai-securitycode-analysis+3
123wwwa/flownameNext-generation JavaScript identifier recovery with LLMs.
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
 eset/malware-research
Code written as part of our various malware investigations
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
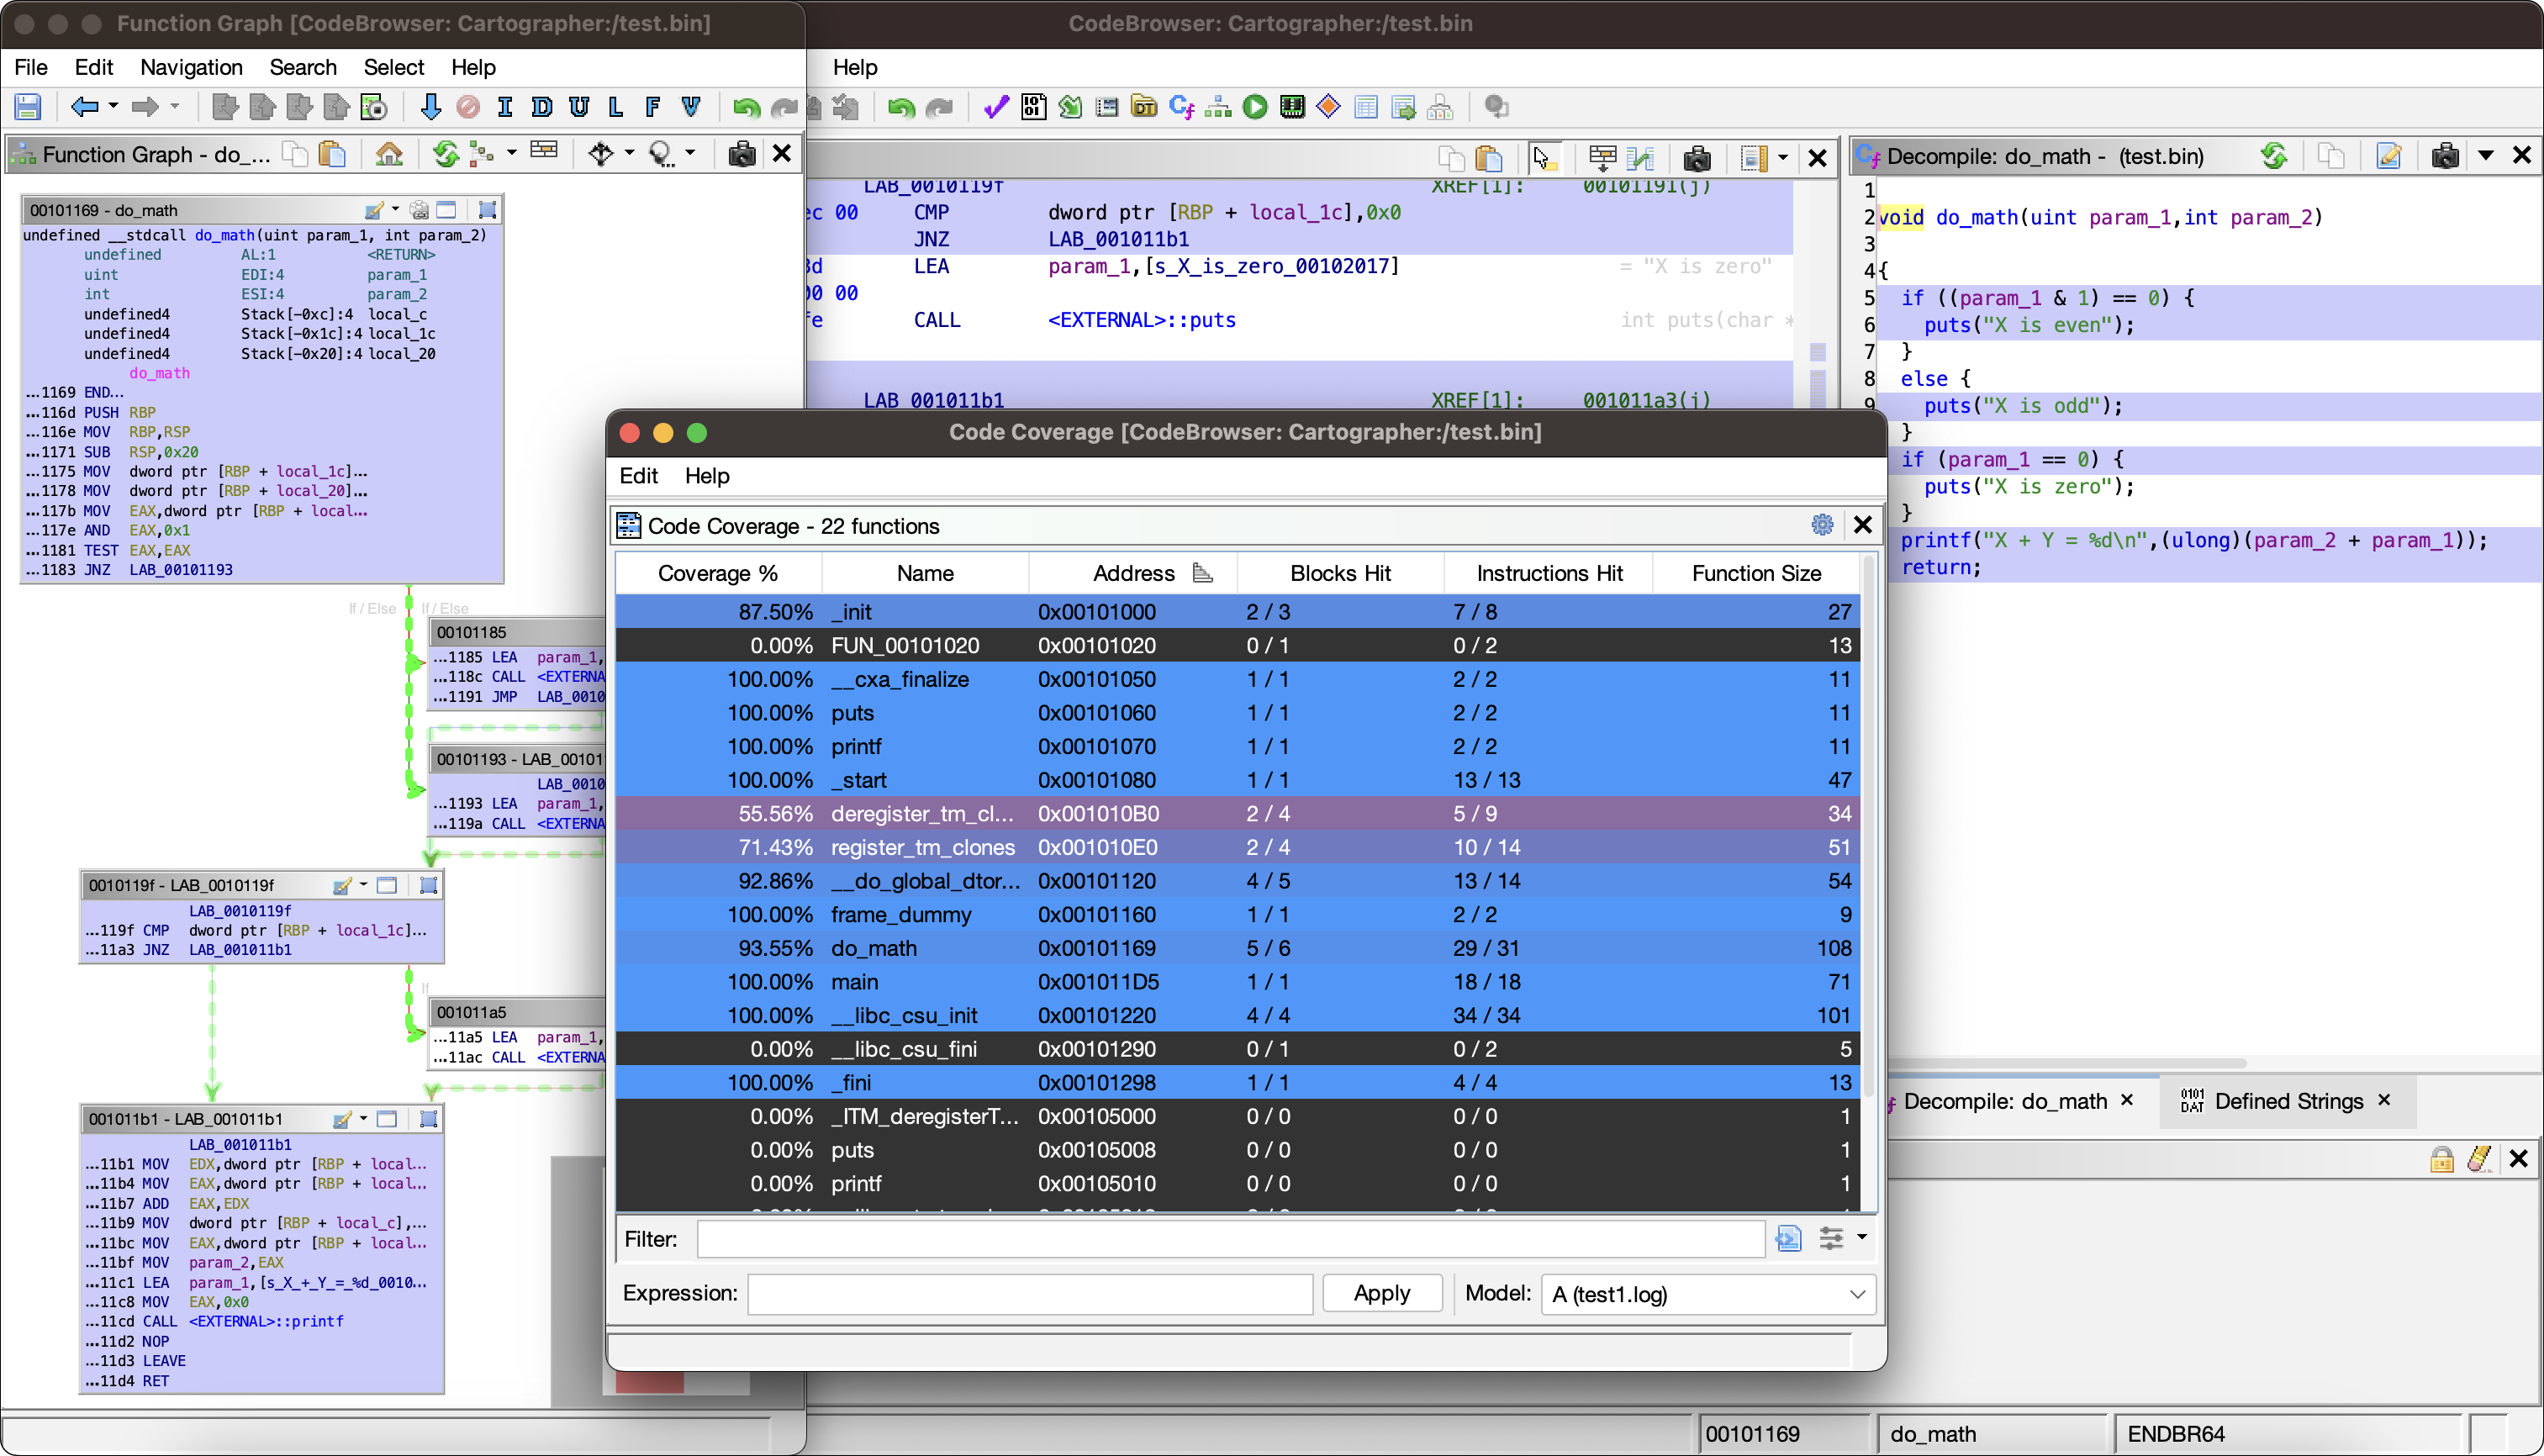 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 binsec/xyntia
Xyntia, the black-box deobfuscator
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
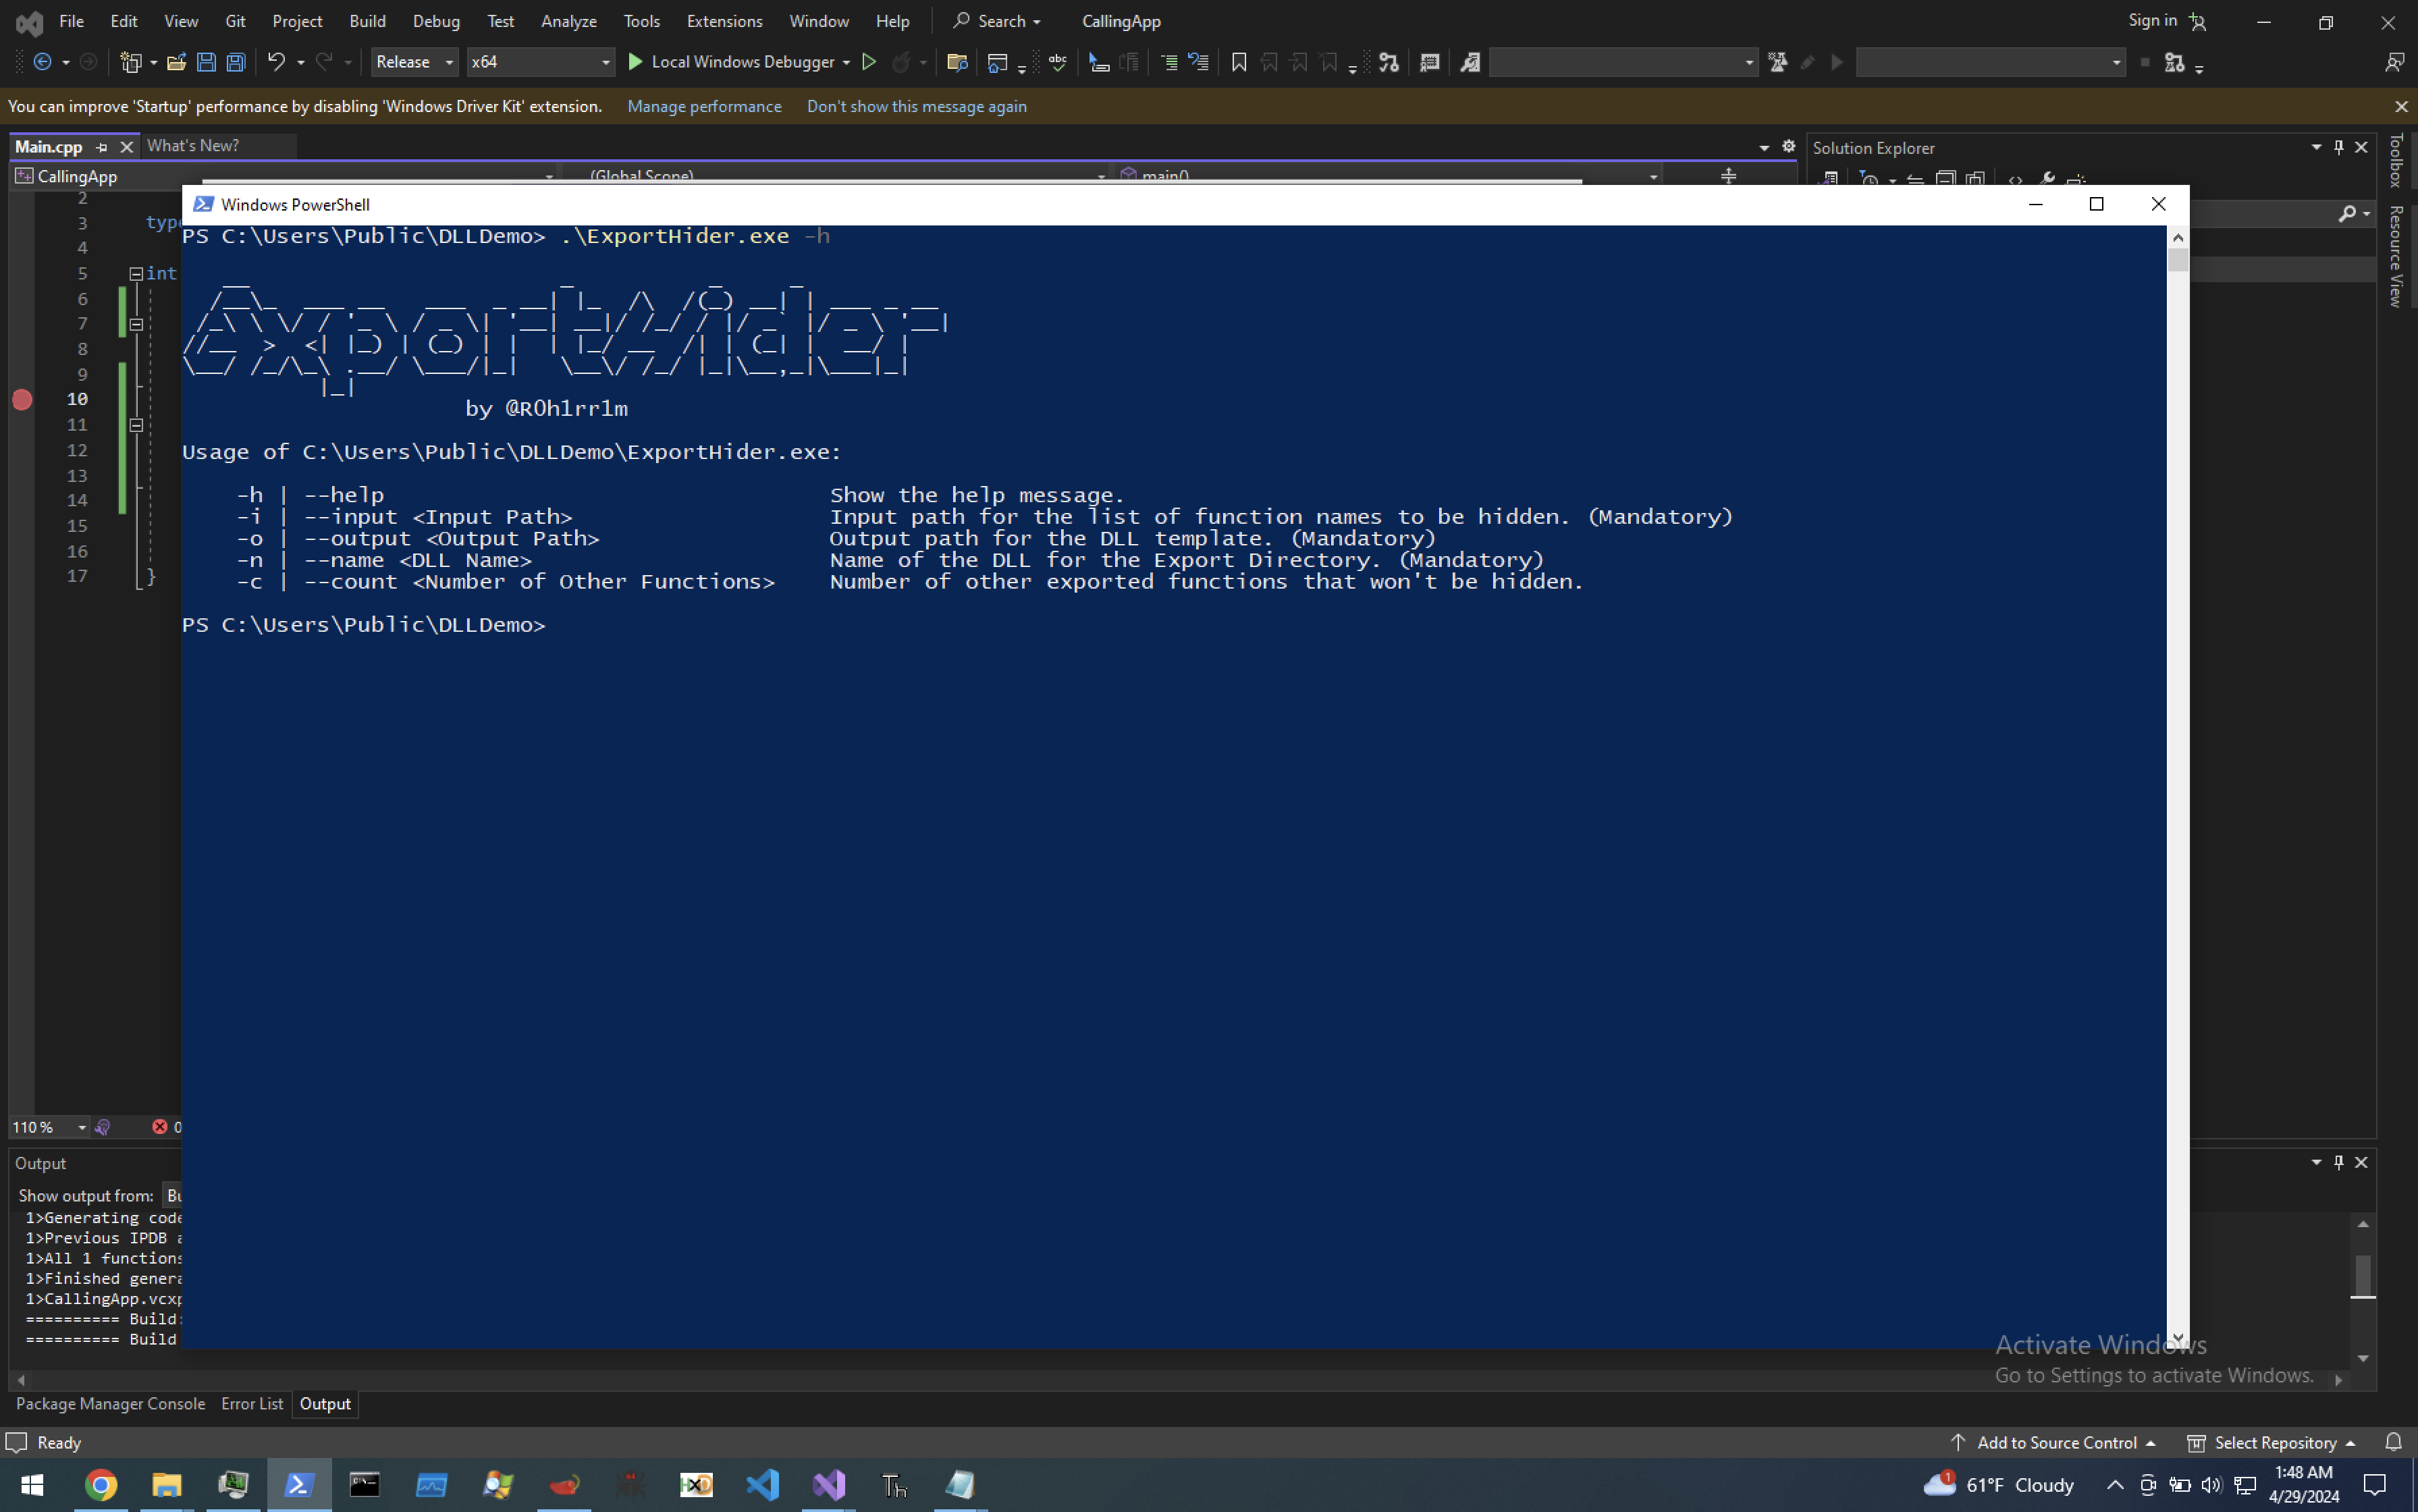 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)