
SASM
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
binary-analysiscode-analysisdebuggers+3
dman95/sasmSASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
 plasma-disassembler/plasma
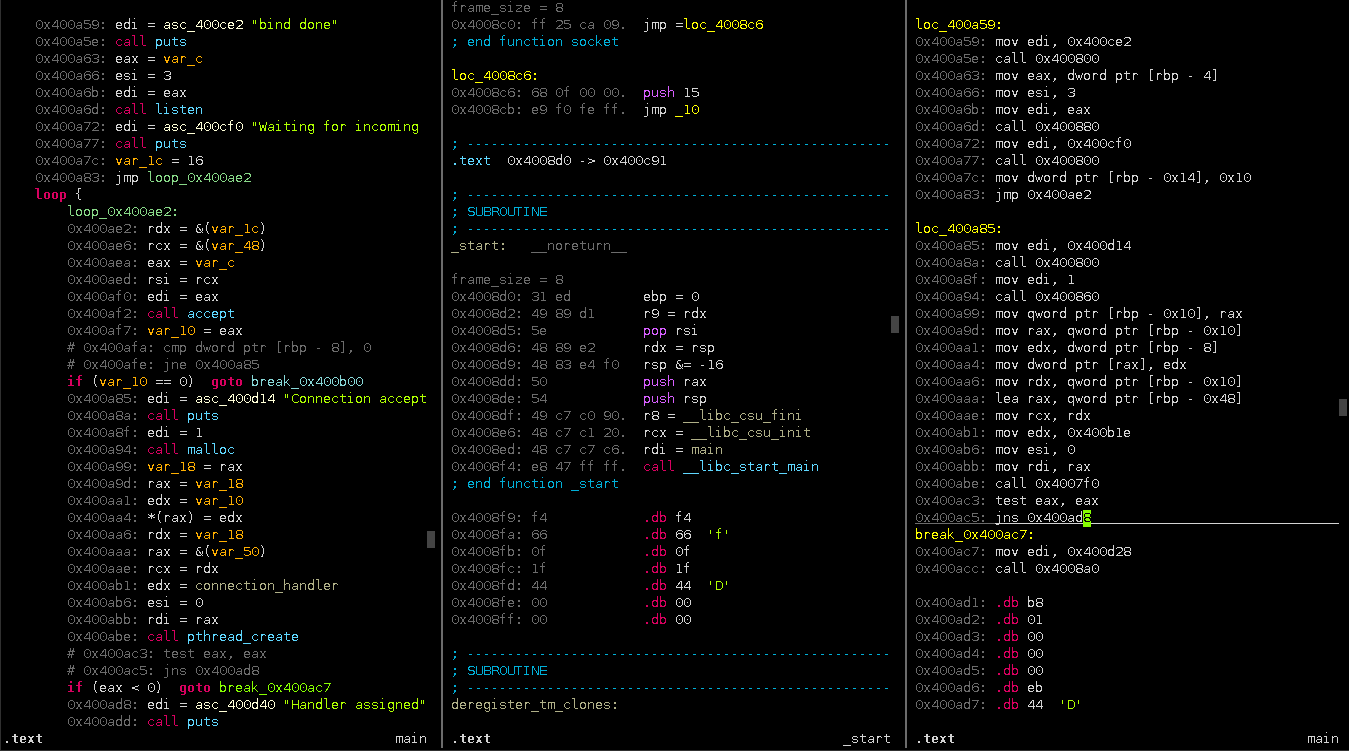
Plasma is an interactive disassembler for x86/ARM/MIPS. It can generates indented pseudo-code with colored syntax.
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
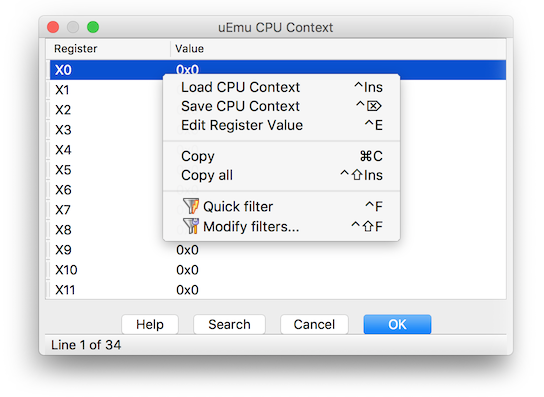 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 justicerage/manalyze
Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
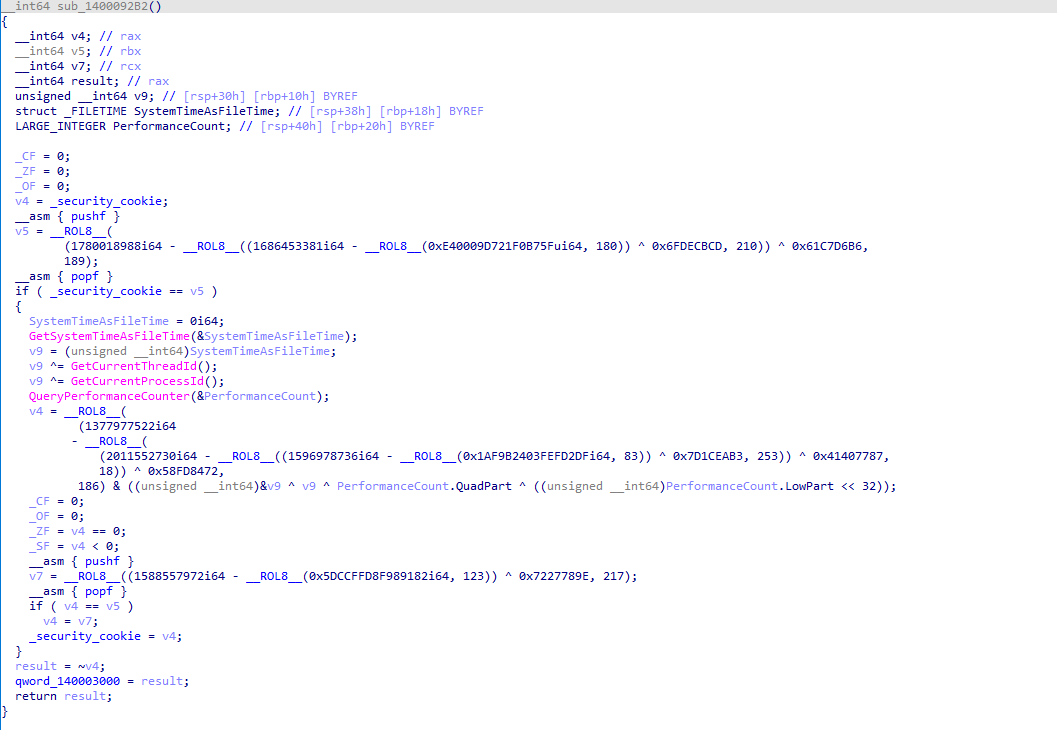 weak1337/alcatraz
x64 binary obfuscator for PE files with control flow flattening, anti-disassembly, import obfuscation, and instruction mutation to hinder reverse…
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
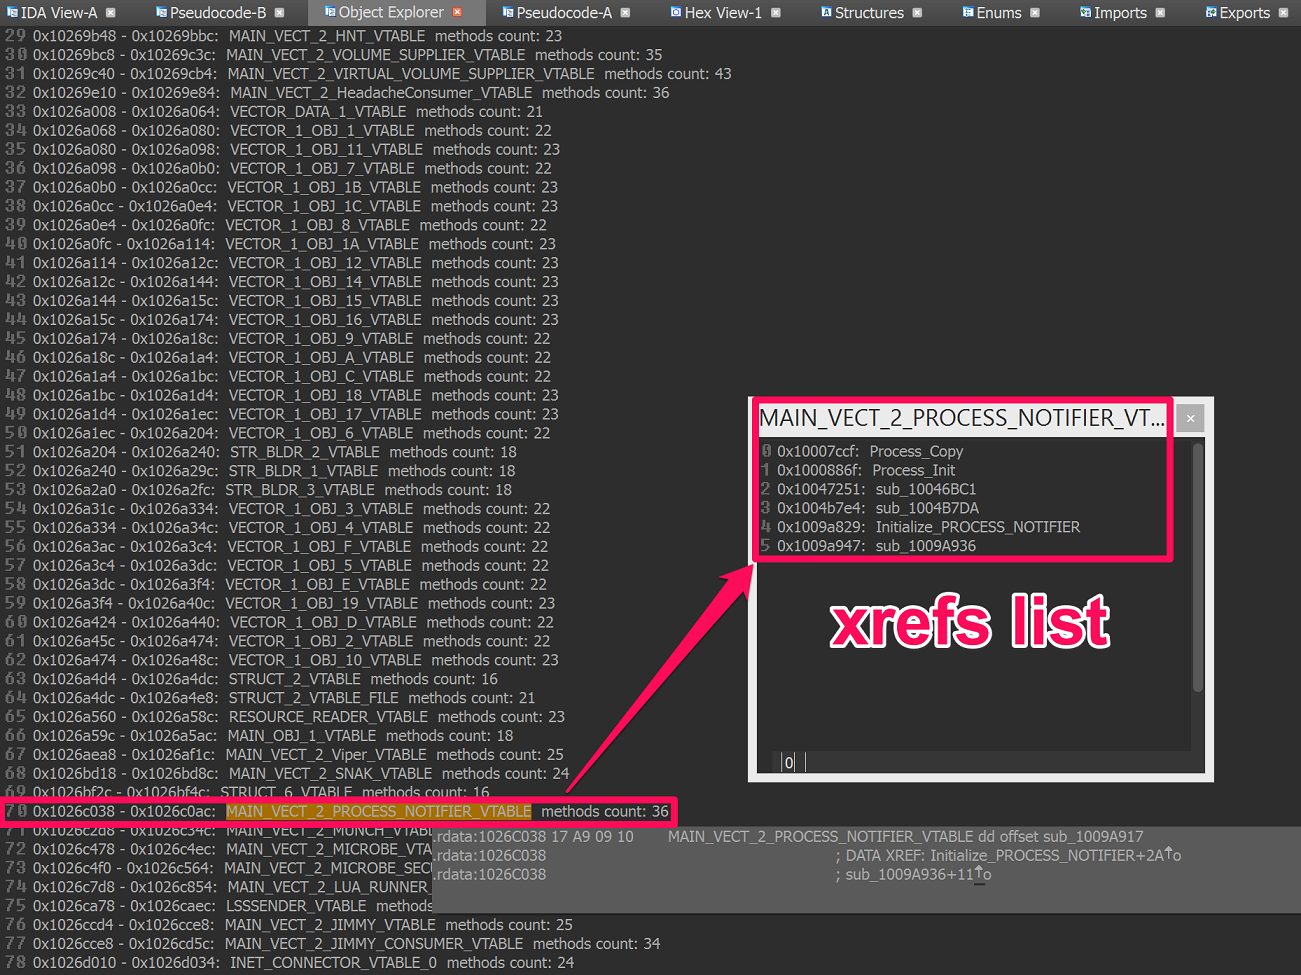 rehints/hexrayscodexplorer
Hex-Rays Decompiler plugin for better code navigation
 lifting-bits/remill
Library for lifting machine code to LLVM bitcode
 devploit/awesome-ctf-resources
A list of Capture The Flag (CTF) frameworks, libraries, resources and software for started/experienced CTF players 🚩
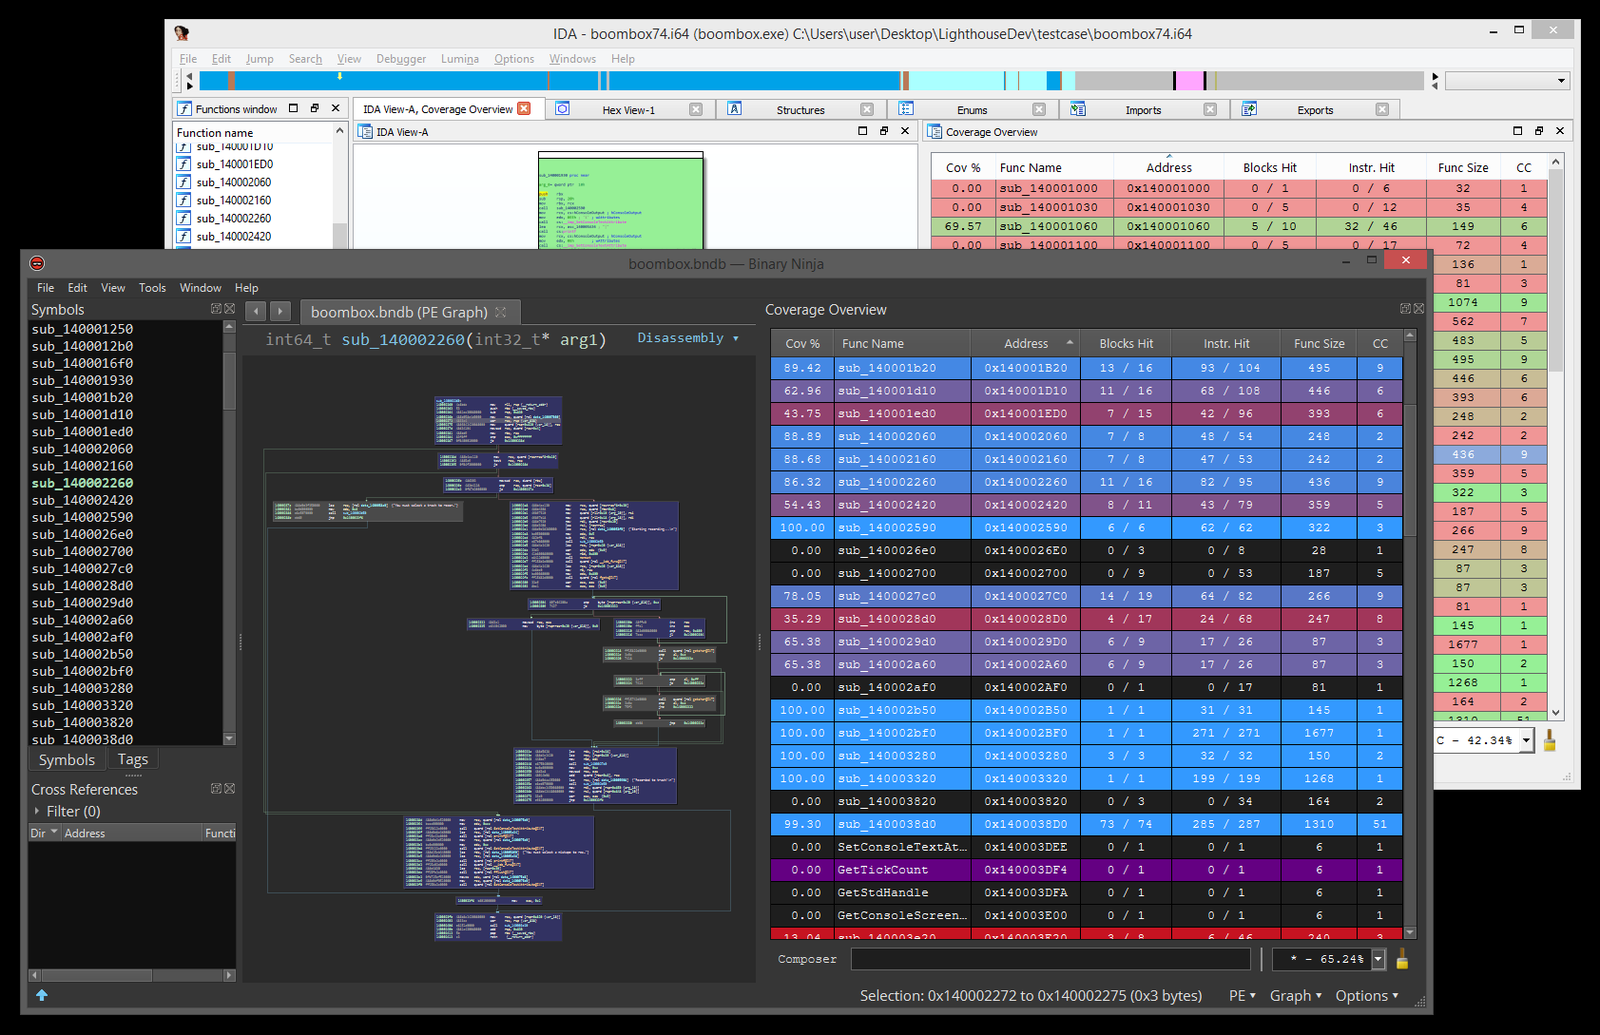 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 viruscamp/luadec
Lua Decompiler for lua 5.1 , 5.2 and 5.3
 washi1337/asmresolver
A library for creating, reading and editing PE files and .NET modules.
 kevthehermit/ratdecoders
Python Decoders for Common Remote Access Trojans