


 androguard/androguard
Reverse engineering and pentesting for Android applications
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
 momo5502/sogen
🪅 Userspace emulator for Windows, Linux & macOS
 darthton/blackbone
Windows memory hacking library
 seemoo-lab/openhaystack
Build your own 'AirTags' 🏷 today! Framework for tracking personal Bluetooth devices via Apple's massive Find My network.
 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
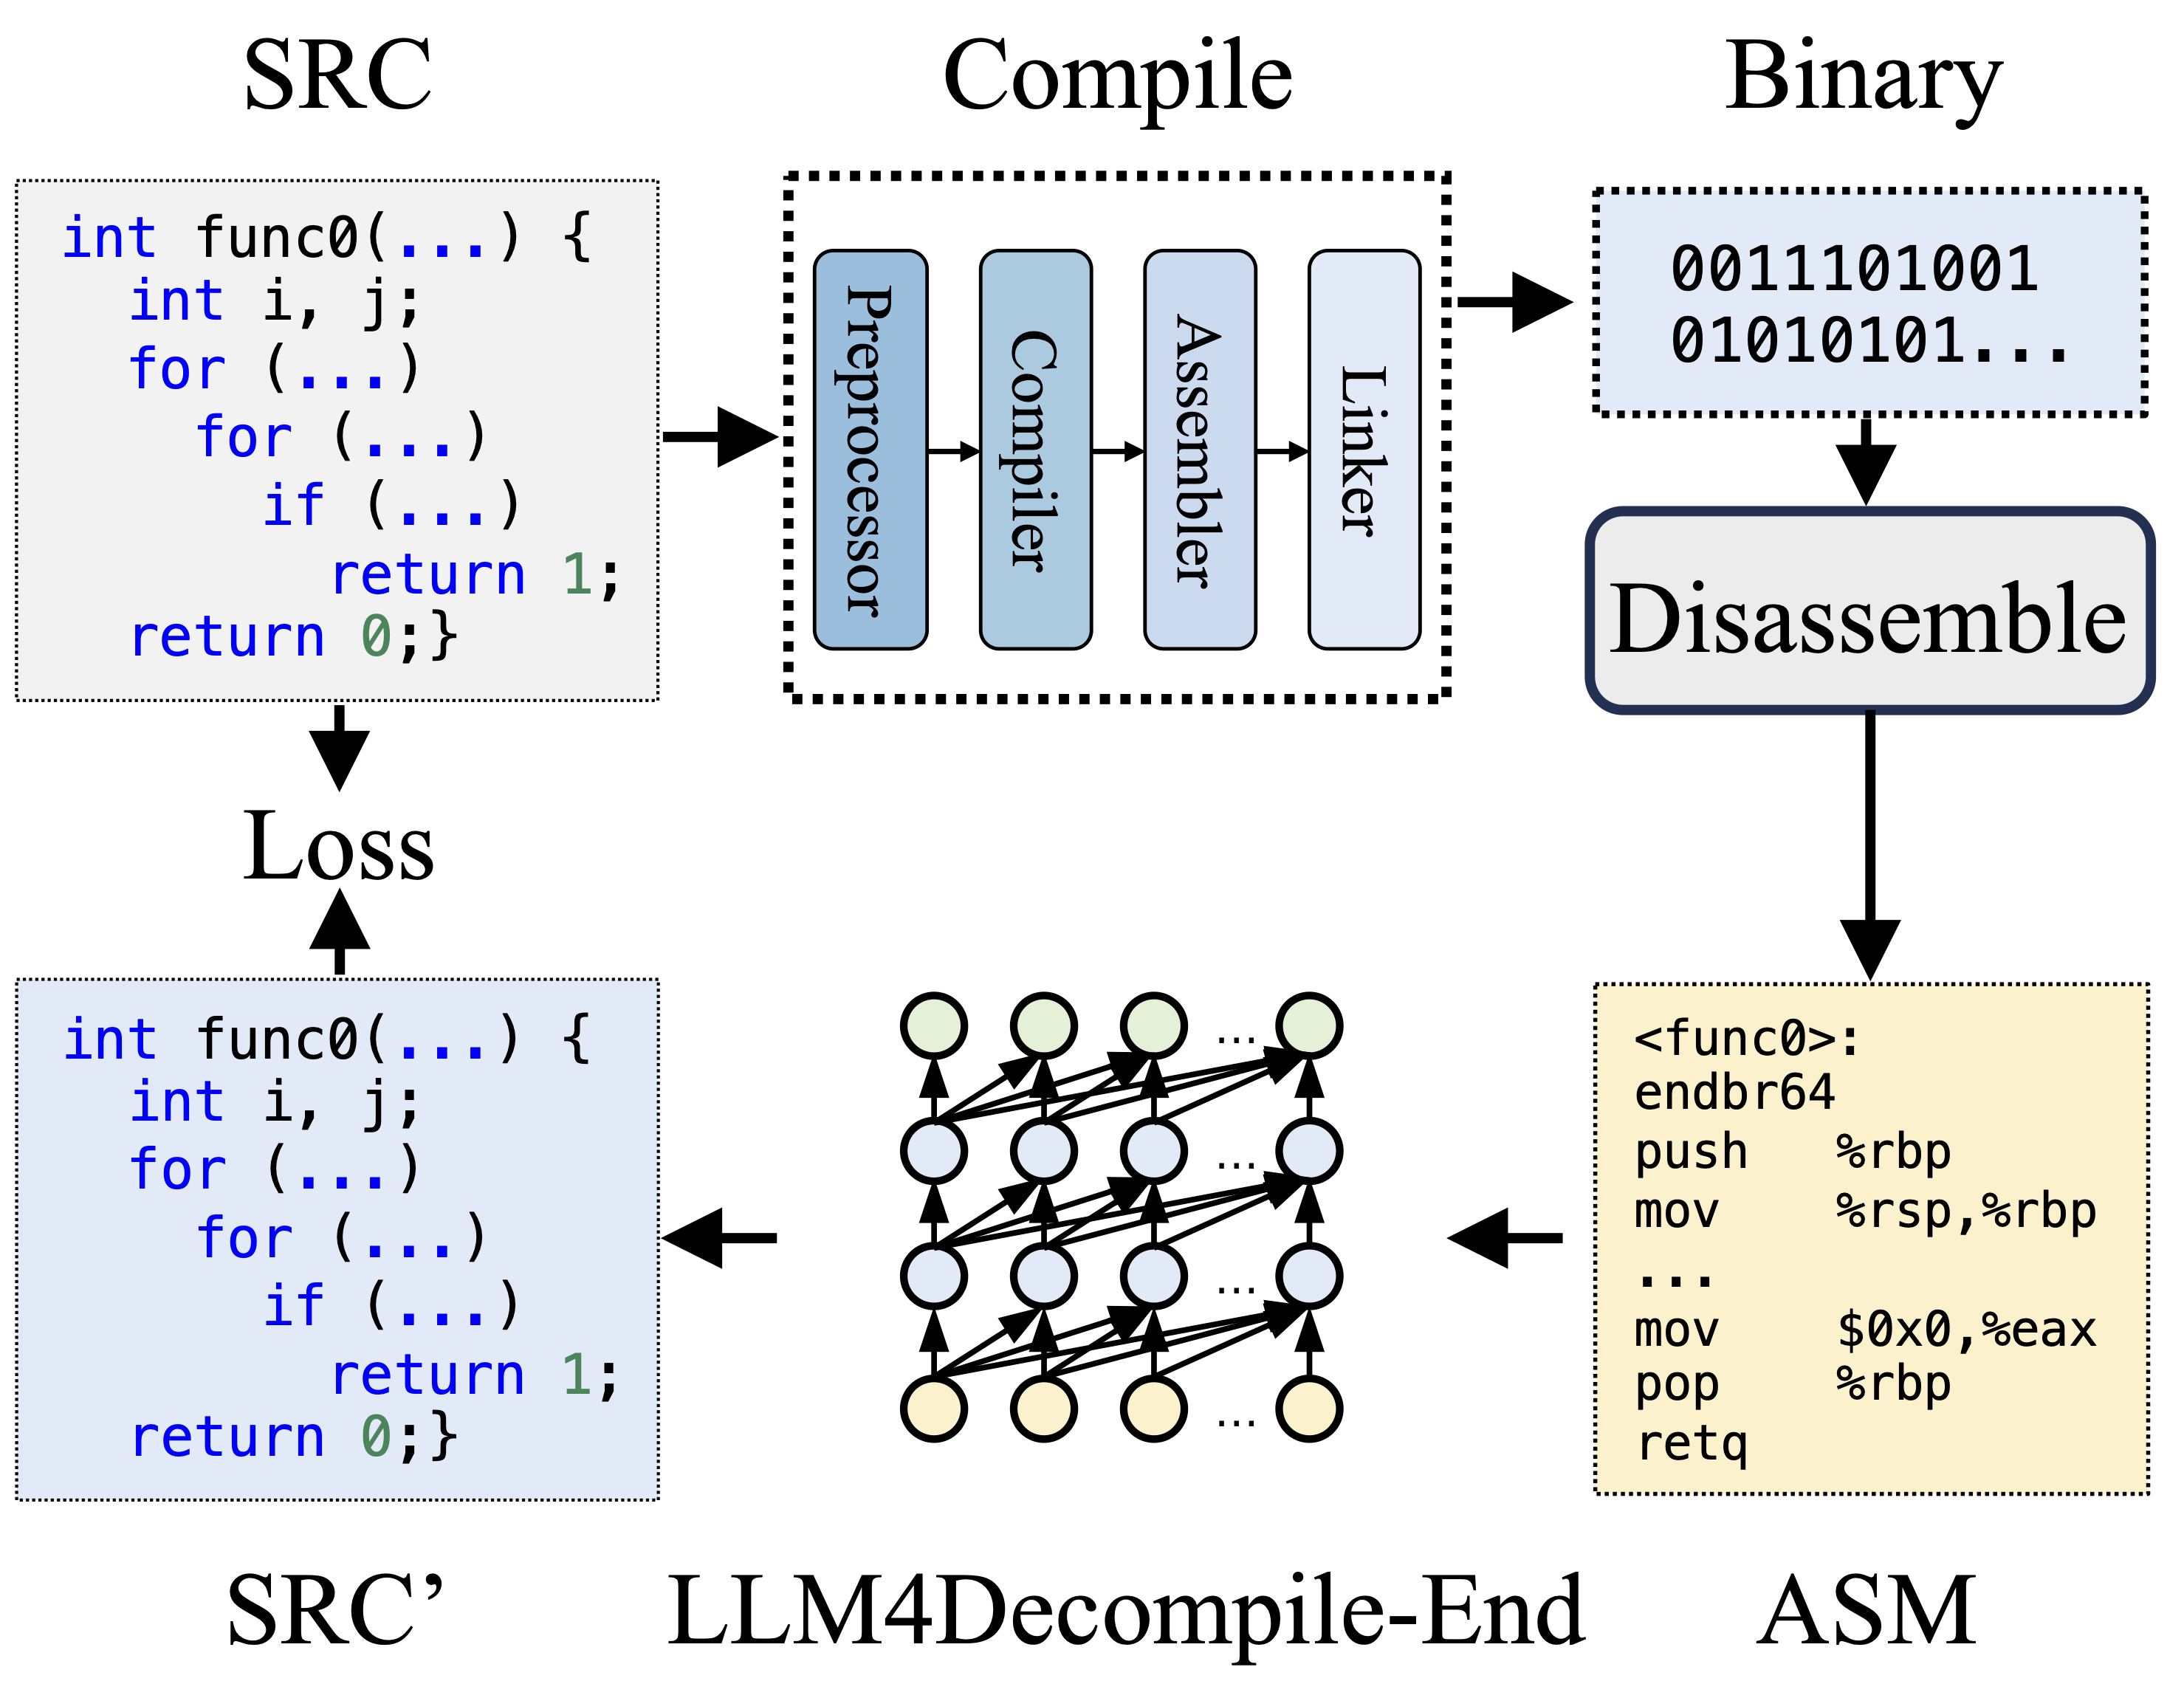 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
 bmax121/apatch
The patching of Android kernel and Android system
 olivierlaflamme/cheatsheet-god
Penetration Testing Reference Bank - OSCP / PTP & PTX Cheatsheet
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.