
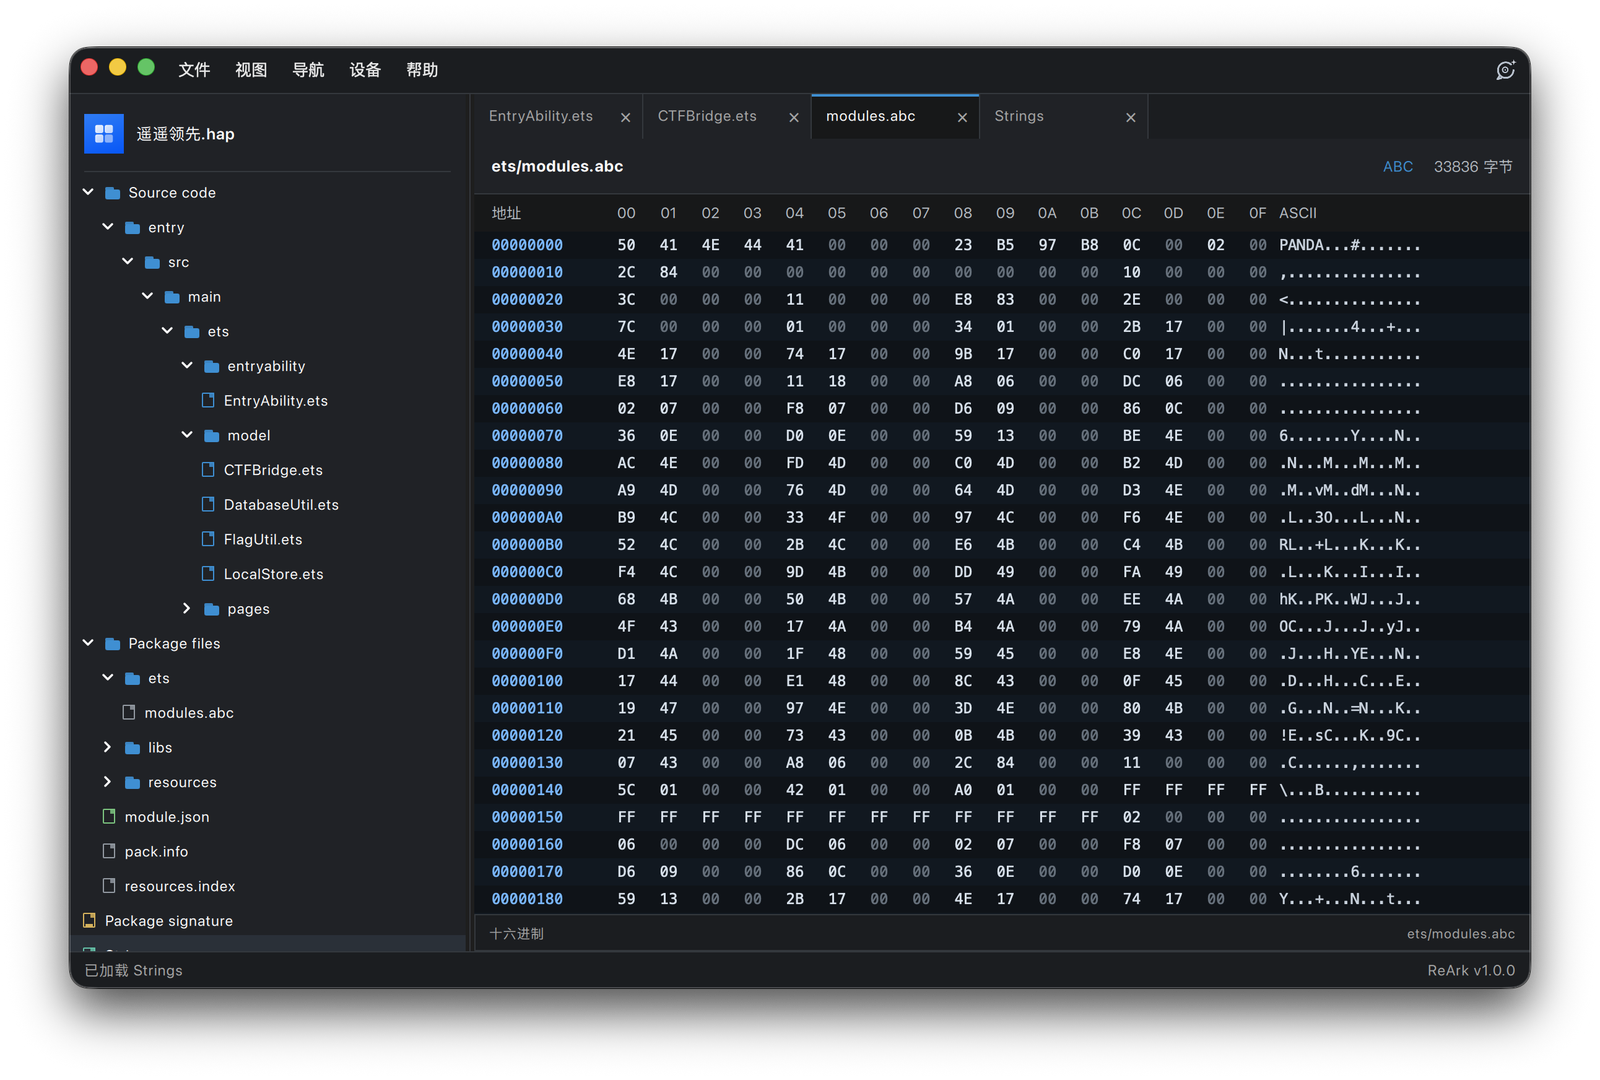
ReArk
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
ai-assisted-reversingandroid-securitybinary-analysis+6
444
lkimuk/rearkAn intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
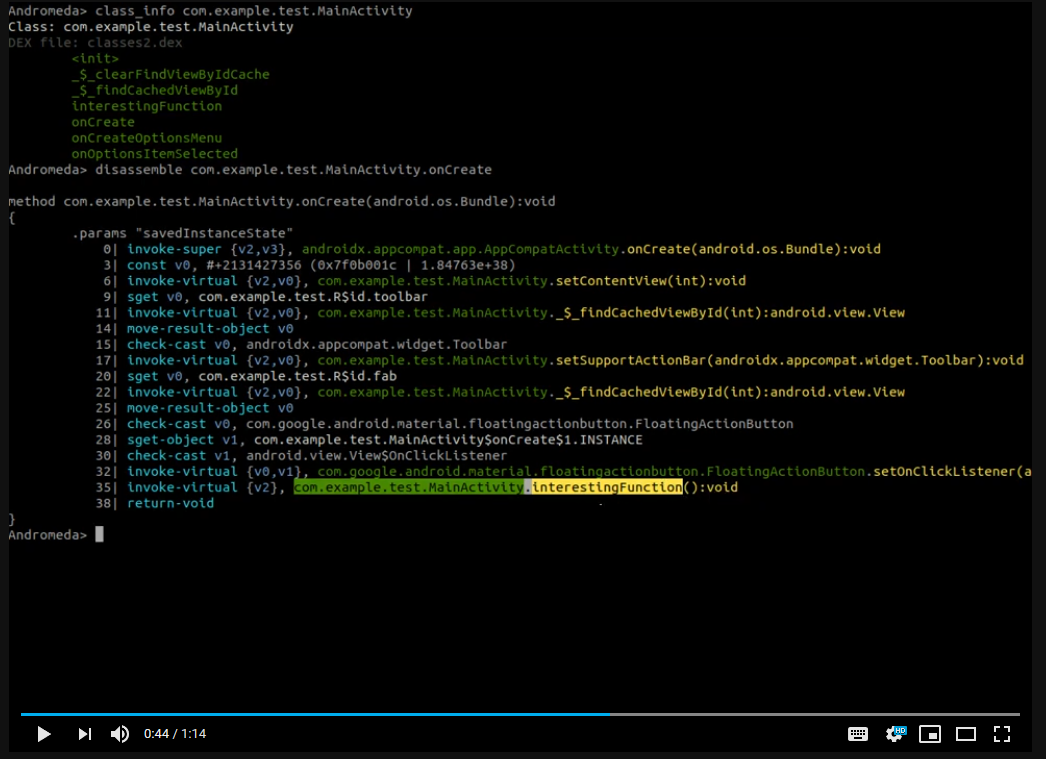 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 guelfoweb/peframe
PEframe is a open source tool to perform static analysis on Portable Executable malware and malicious MS Office documents.
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 t00sh/rop-tool
A tool to help you write binary exploits
 4w4k3/repy2exe
A Reverse Engineering Tool for py2exe applications.
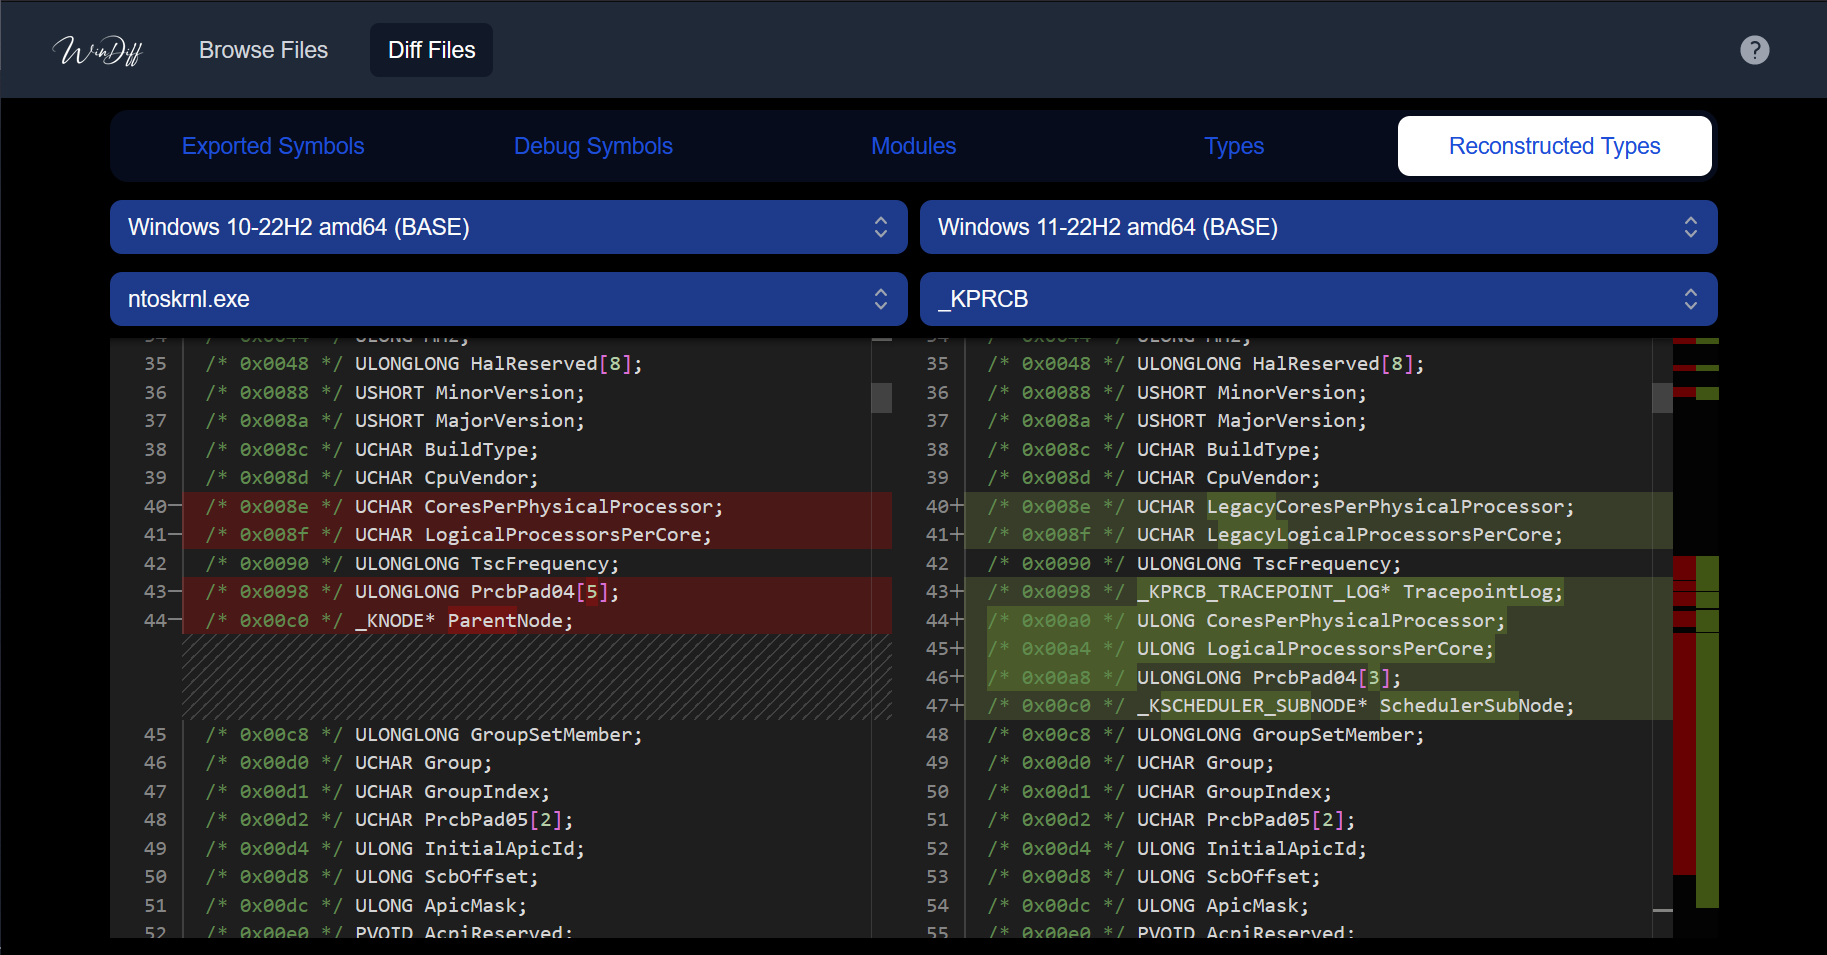 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
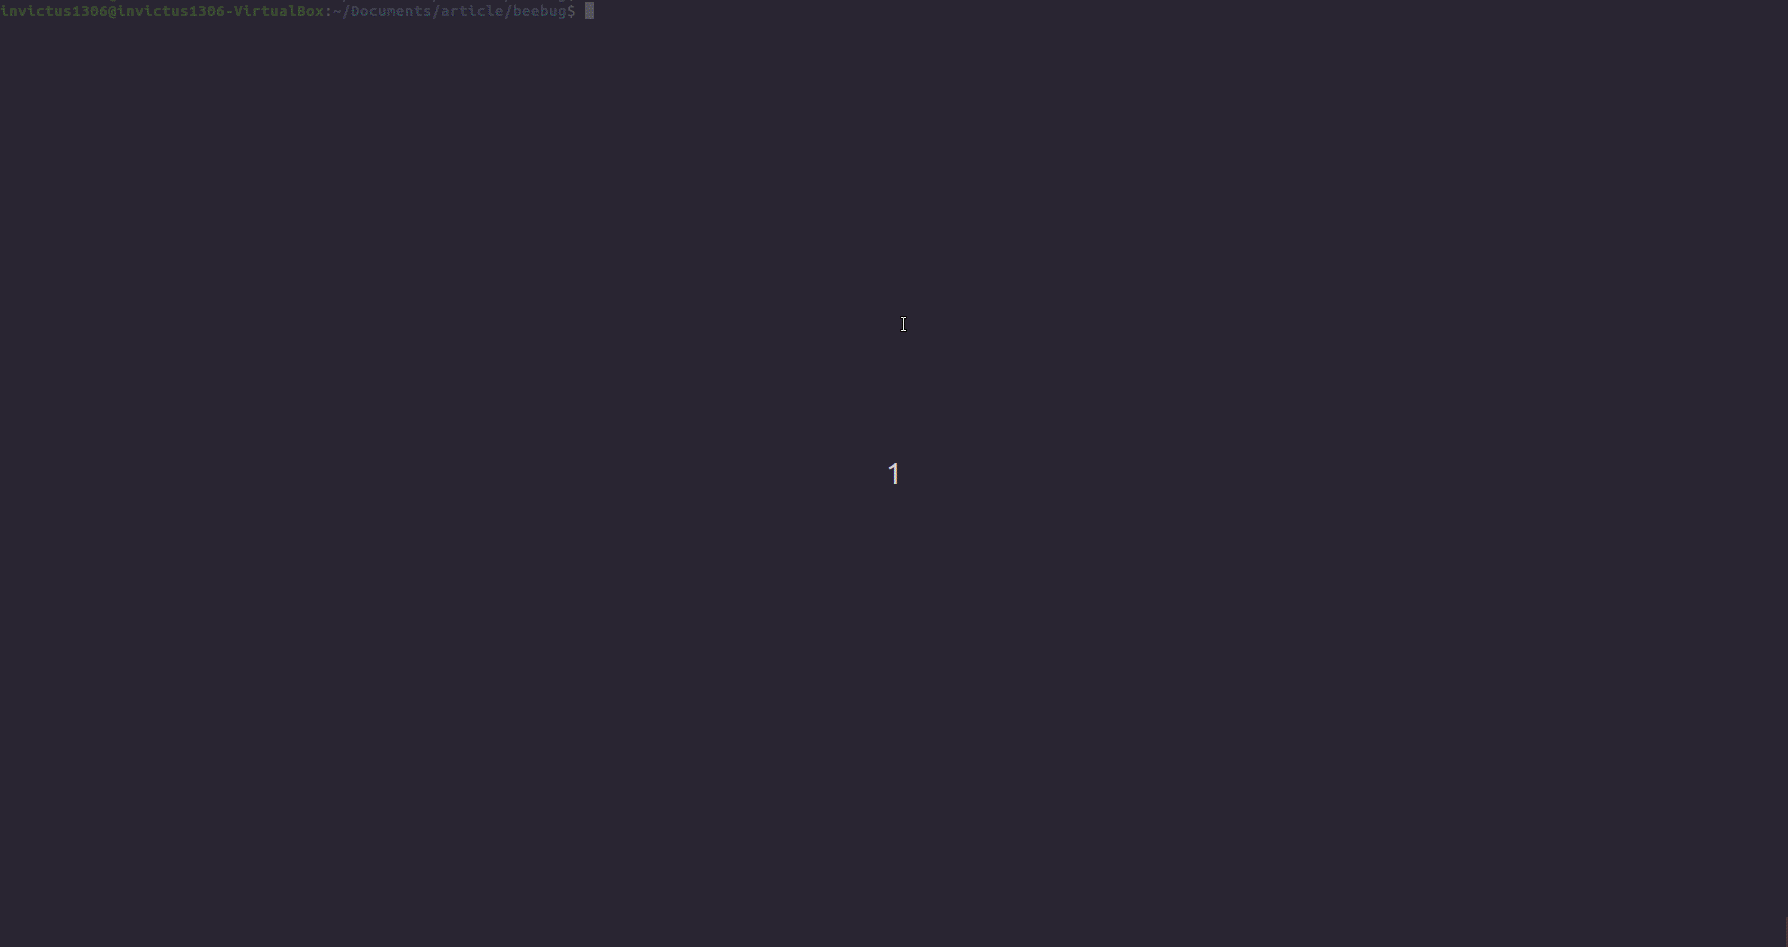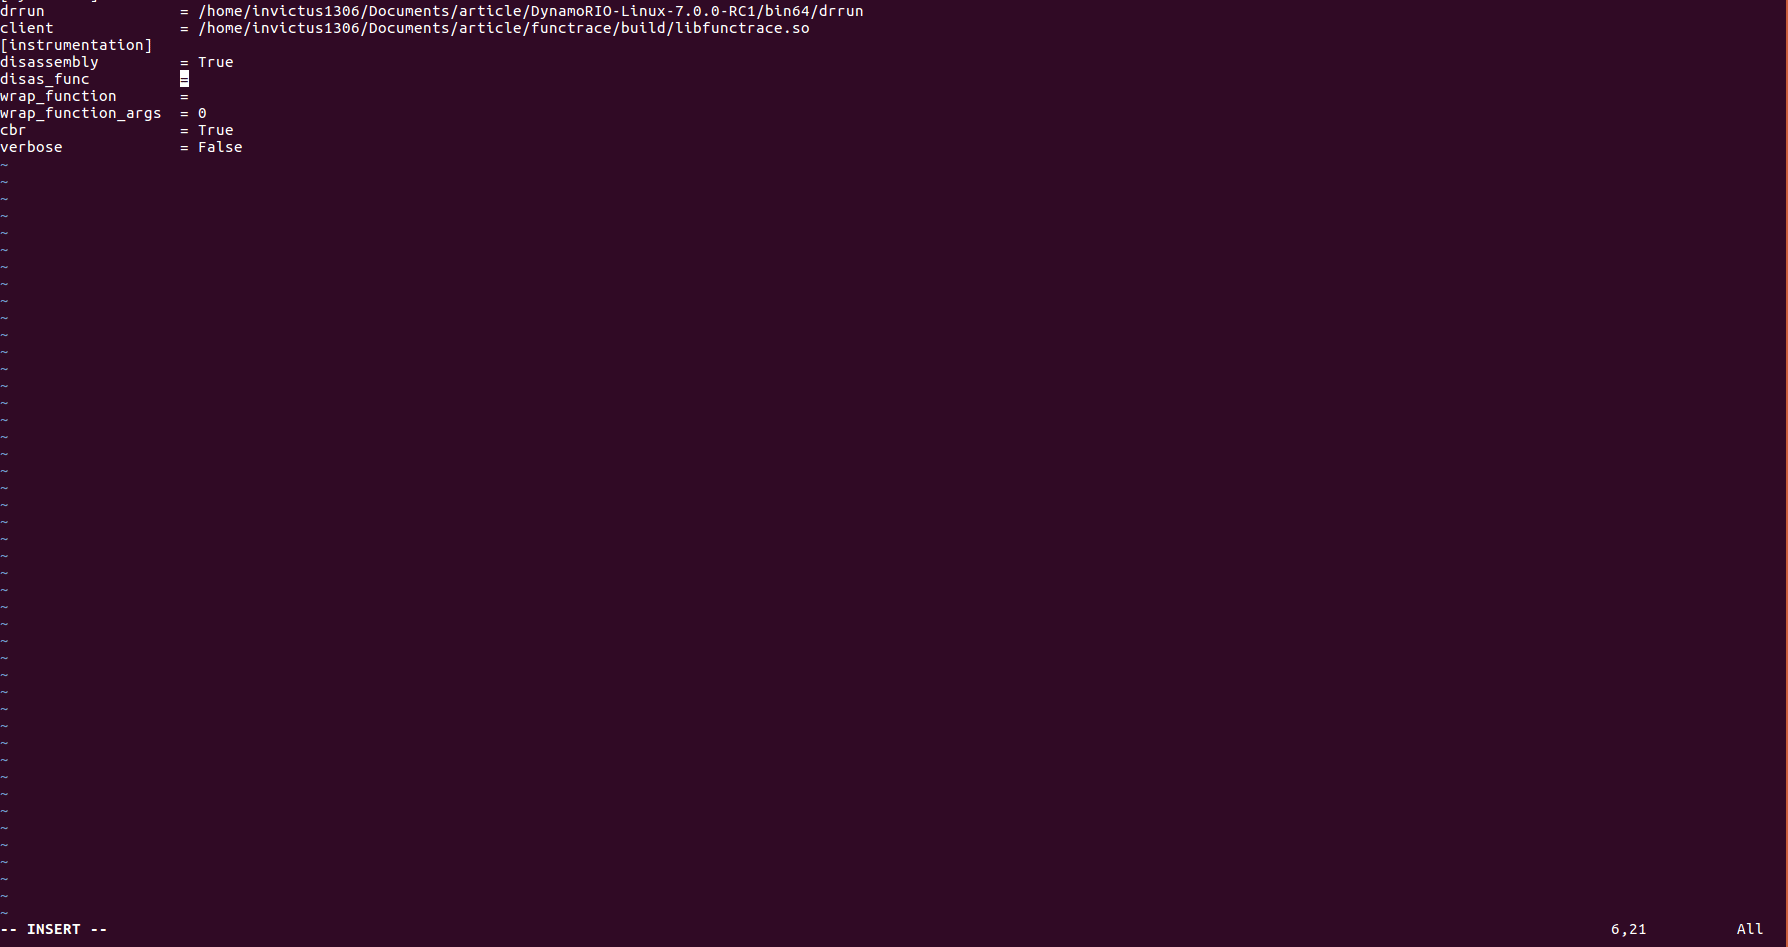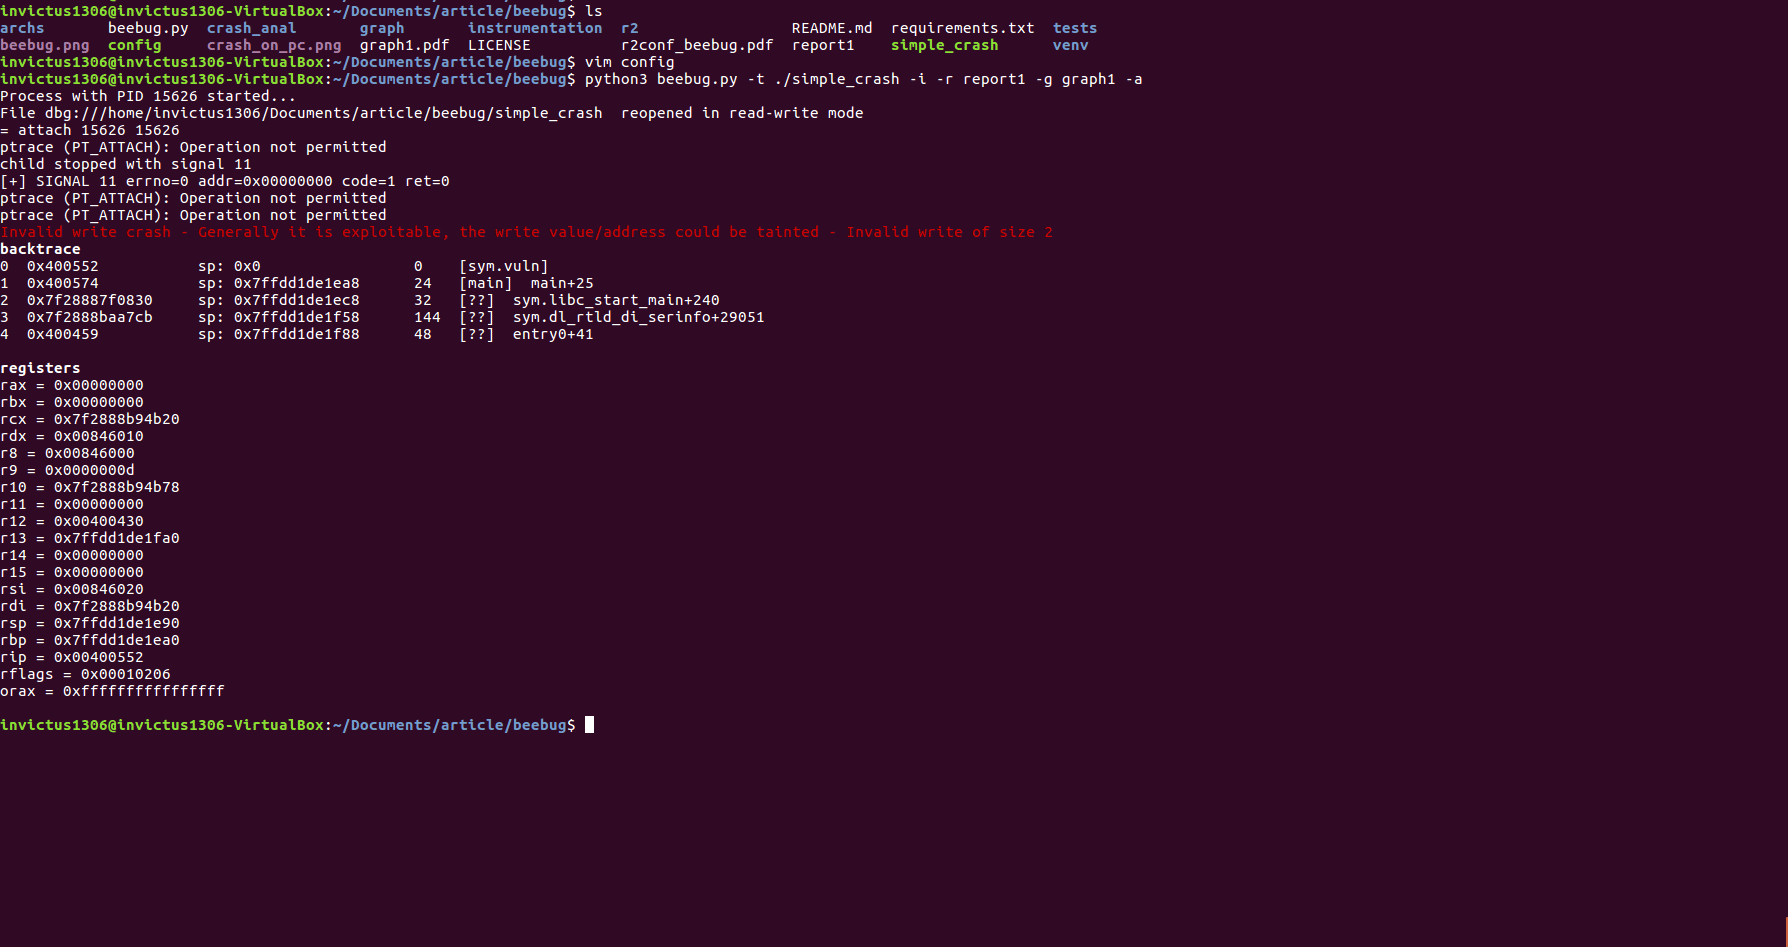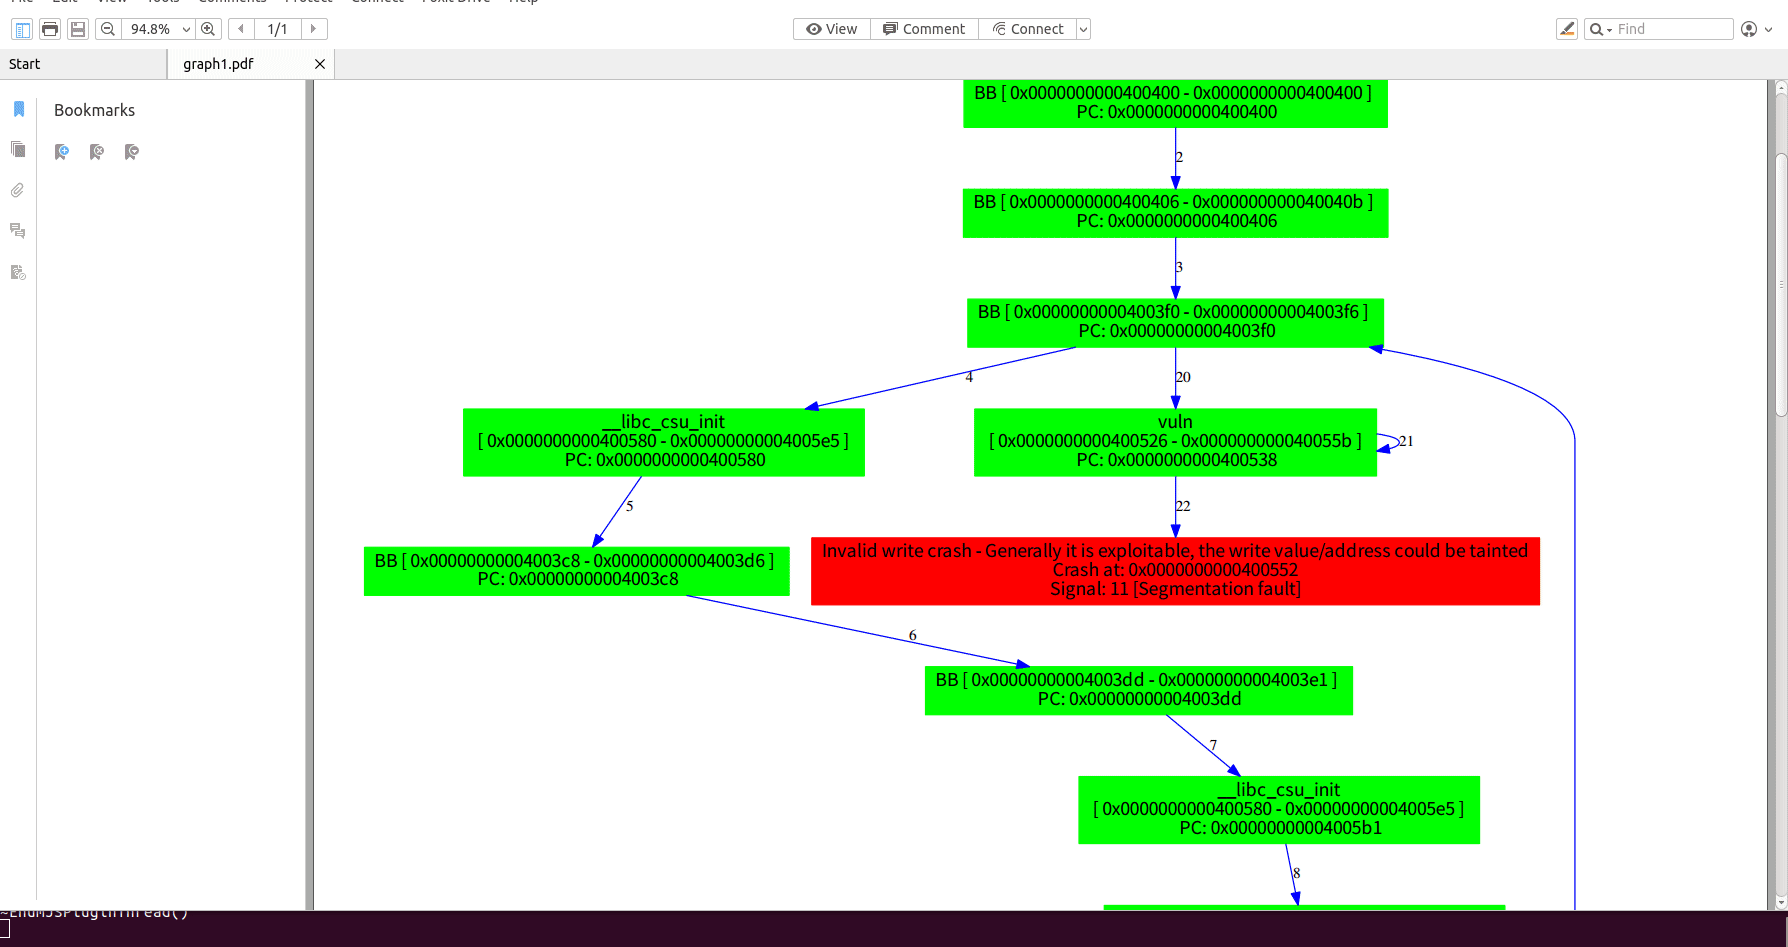
 jetp1ane/callisto
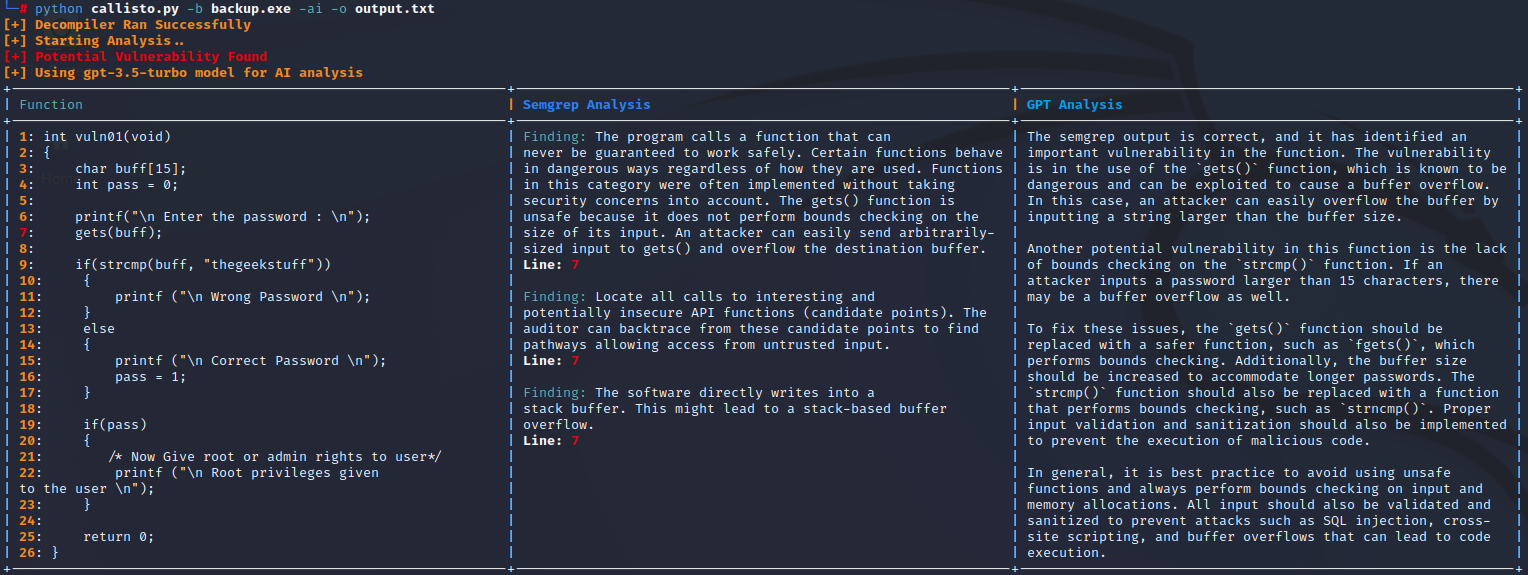
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
 secrary/drsemu
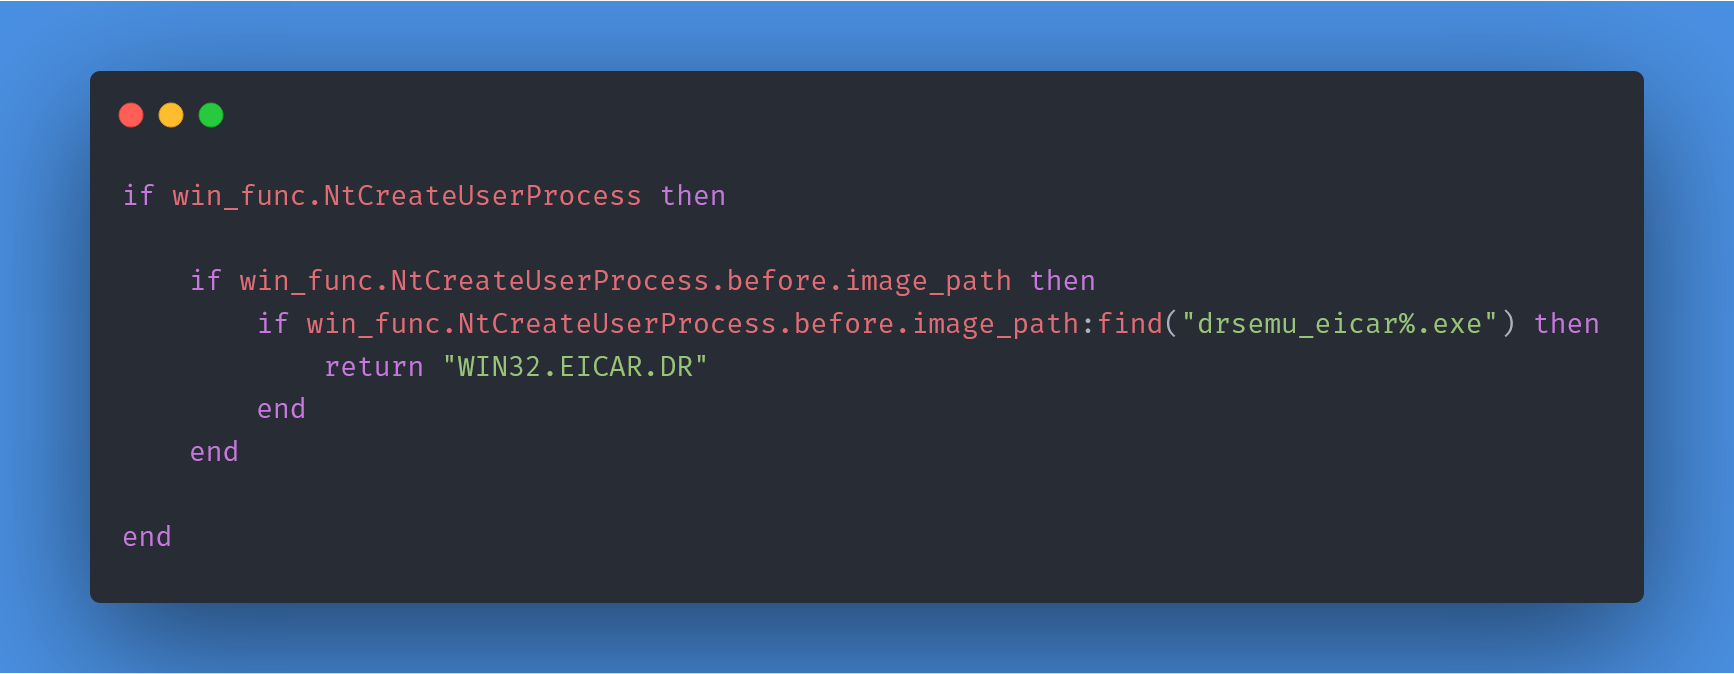
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
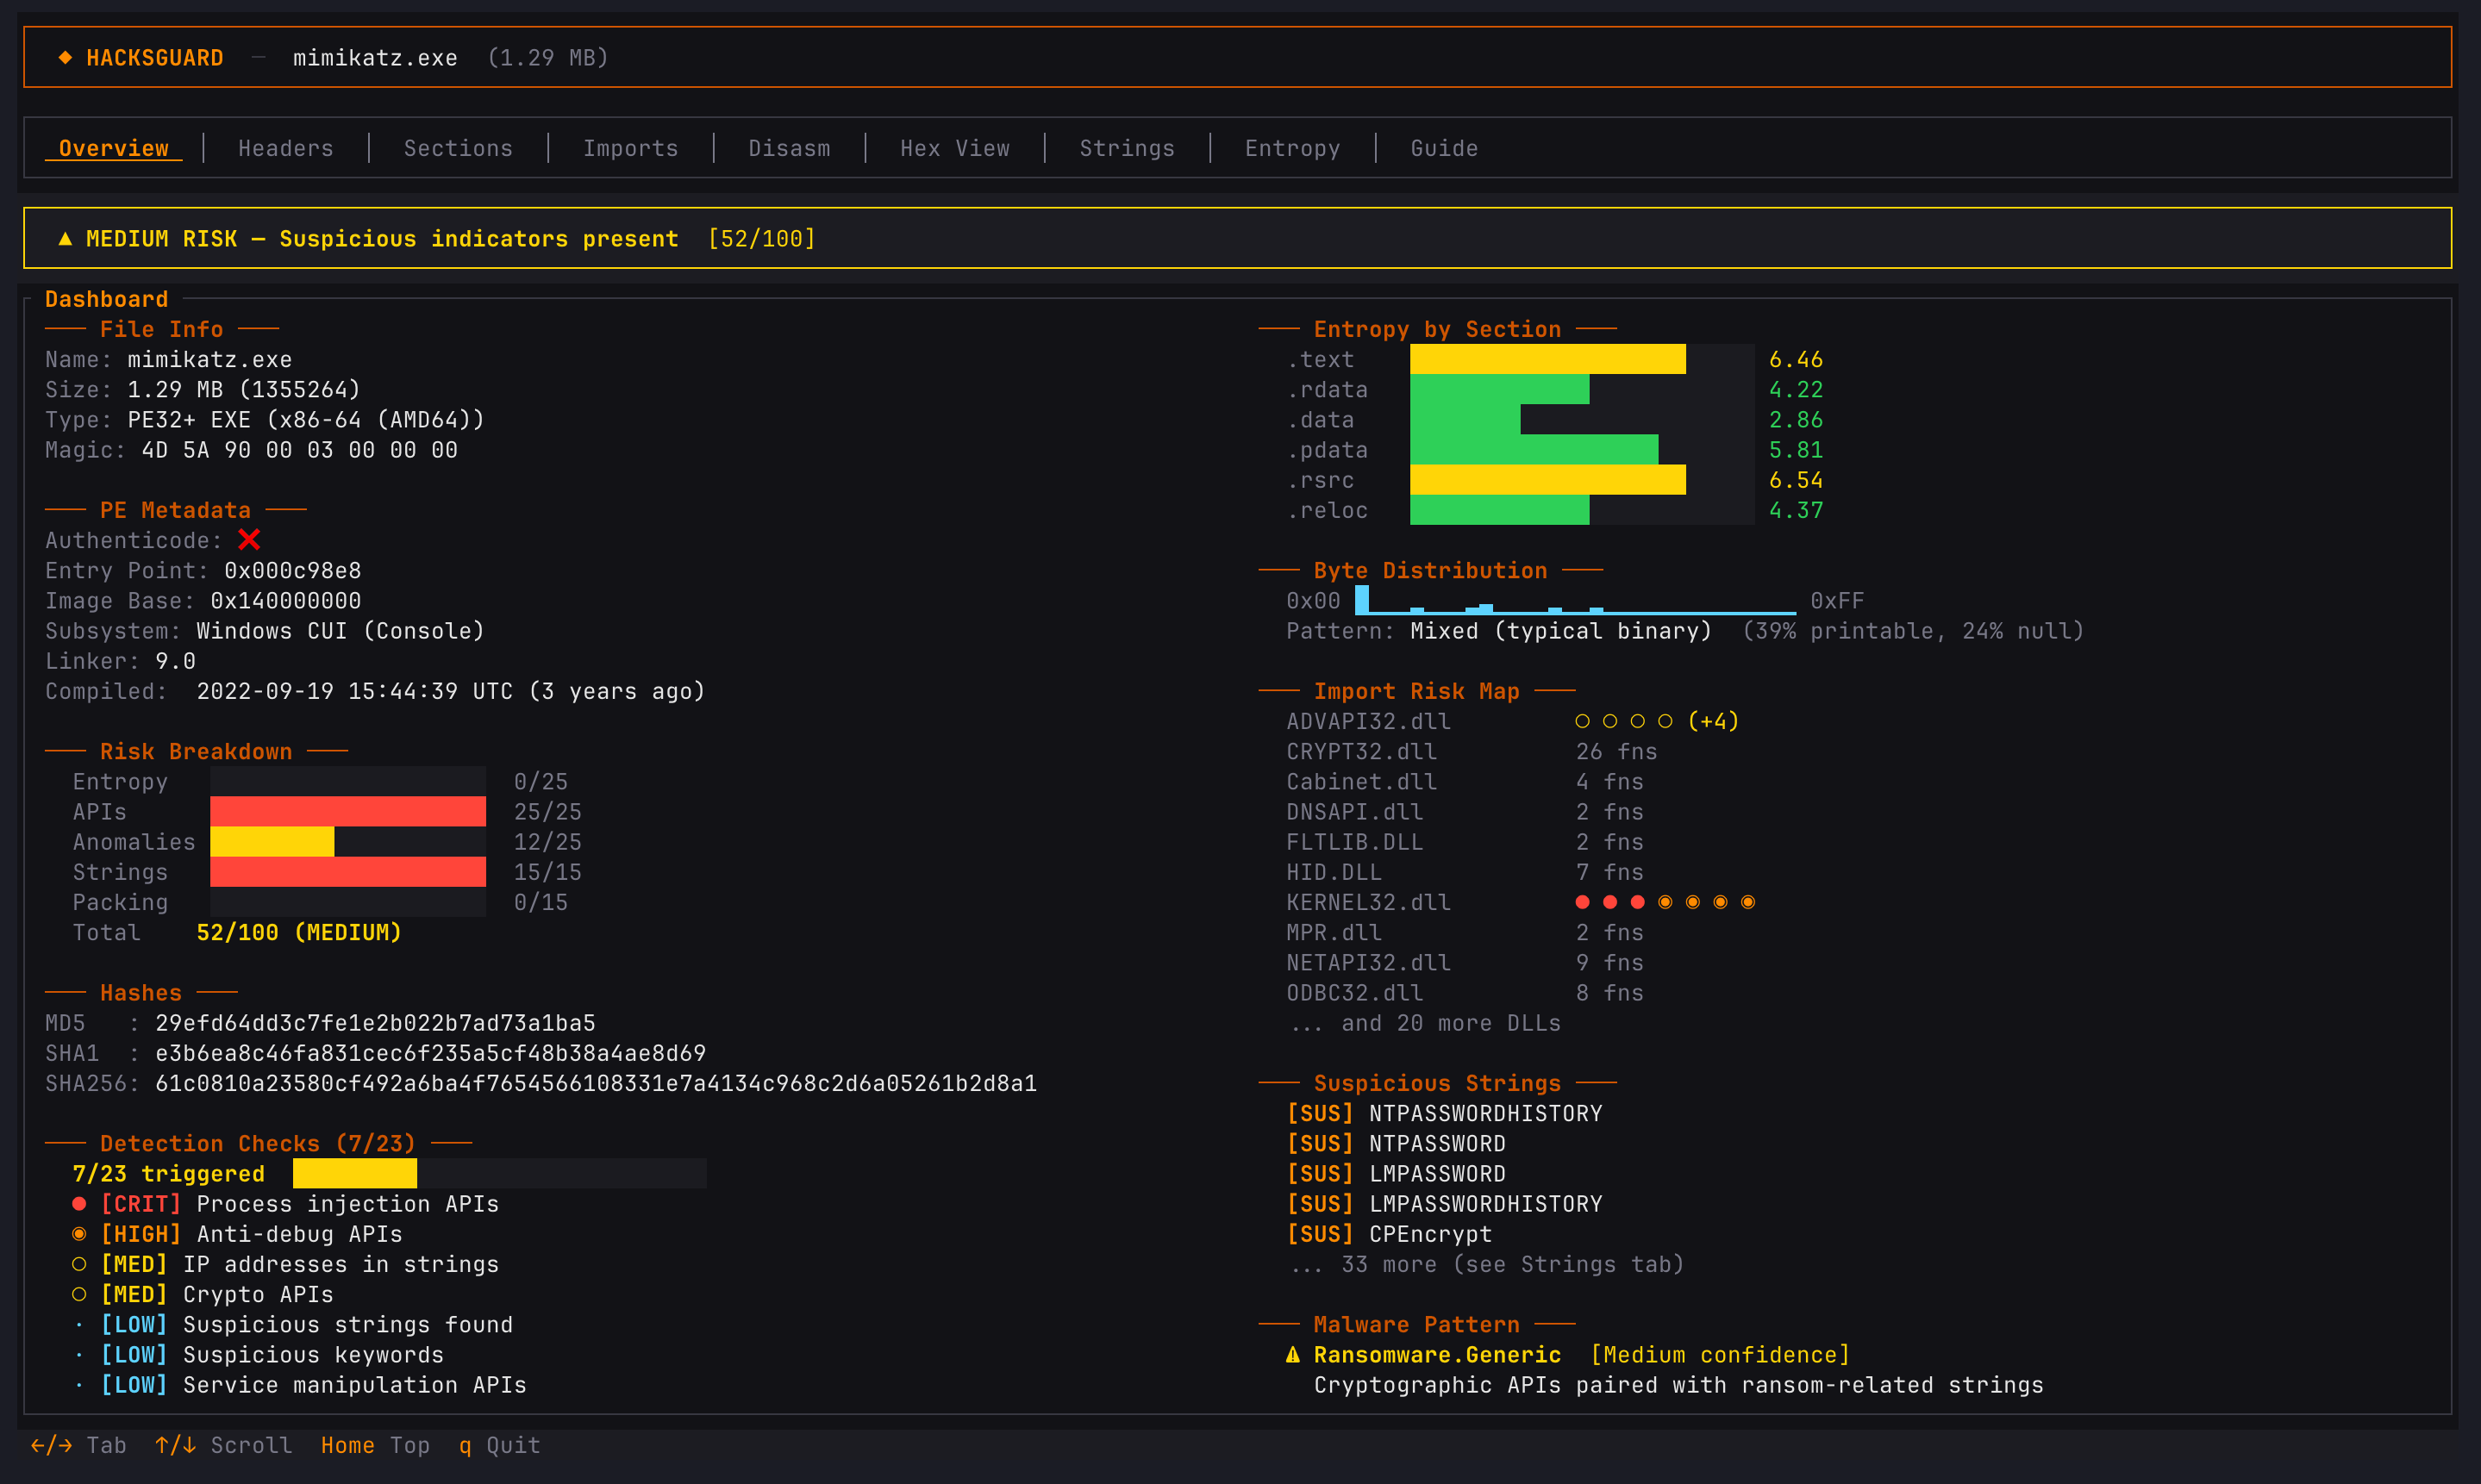 rhacknarok/hacksguard
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.