
workshop_firmware_reverse_engineering
 emproof-com/workshop_firmware_reverse_engineering
Workshop on firmware reverse engineering
binary-analysiseducationembedded-systems-security+6
453
emproof-com/workshop_firmware_reverse_engineeringWorkshop on firmware reverse engineering
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 remnux/distro
Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
 live-ctf/livectf-defcon30
Collection of DEF CON 30 CTF challenge binaries, build scripts, and solve scripts for practicing binary exploitation and reverse engineering.
 sofianehamlaoui/lockdoor-framework
🔐 Lockdoor Framework : A Penetration Testing framework with Cyber Security Resources
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
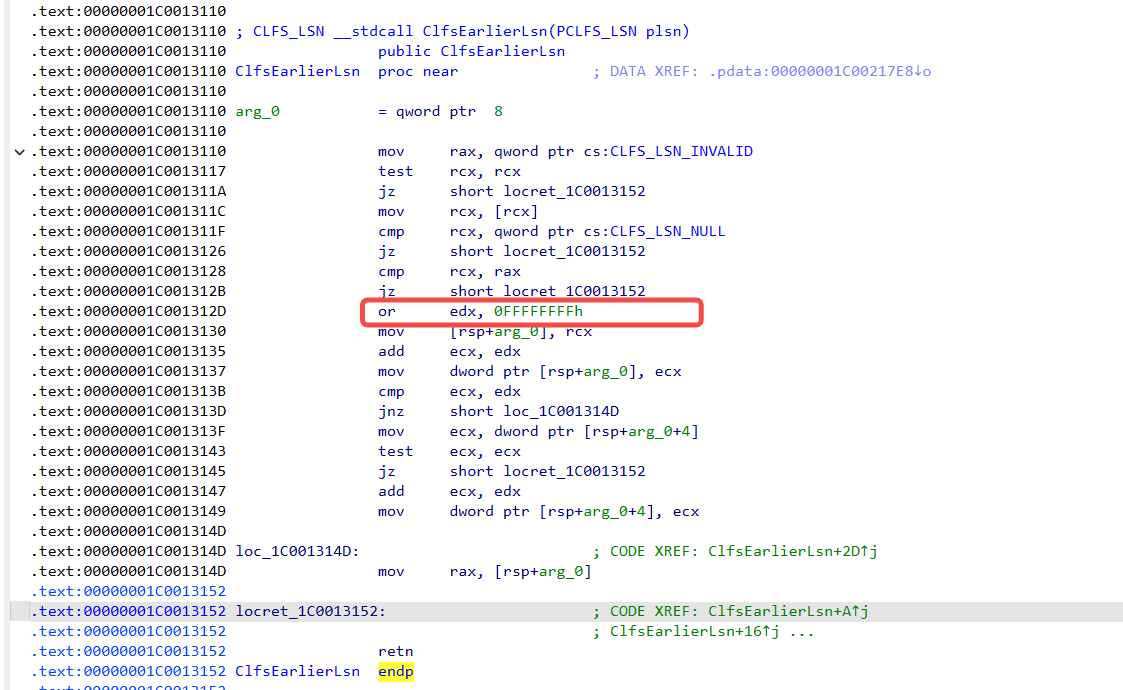 uname1able/cve-2022-24481-analysis
Deep-dive analysis of Windows CLFS type confusion (CVE-2022-24481) with root-cause explanation, exploitation flow, kernel gadget details, and working…
 thegaminggallifreyan/liberationplay-cve-2025-24132-airbourne-poc
POC for CVE-2025-24132 (AirBourne). Currently just triggers the overflow and causes a crash
 uoftctf/uoftctf-2025-chals-public
Challenge handouts, source code, and solutions for UofTCTF 2025

 sinakarvandi/hypervisor-from-scratch
Source code of a multiple series of tutorials about the hypervisor. Available at: https://rayanfam.com/tutorials
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 bmax121/apatch
The patching of Android kernel and Android system
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 thesecretclub/riscy-business
RISC-V Virtual Machine