
Archived
unicorn_pe
 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
binary-analysisdynamic-analysis-sandboxingexploitation+3
hzqst/unicorn_peEmulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 nccgroup/susanrtti
Another RTTI Parsing IDA plugin
 zhuowei/cheese
CVE-2025-21479 proof-of-concept, I think
 quosecgmbh/grap
Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
 proteqtum/interactive-binary-structures
Interactive documentation and visual reference for binary formats and system memory layouts.
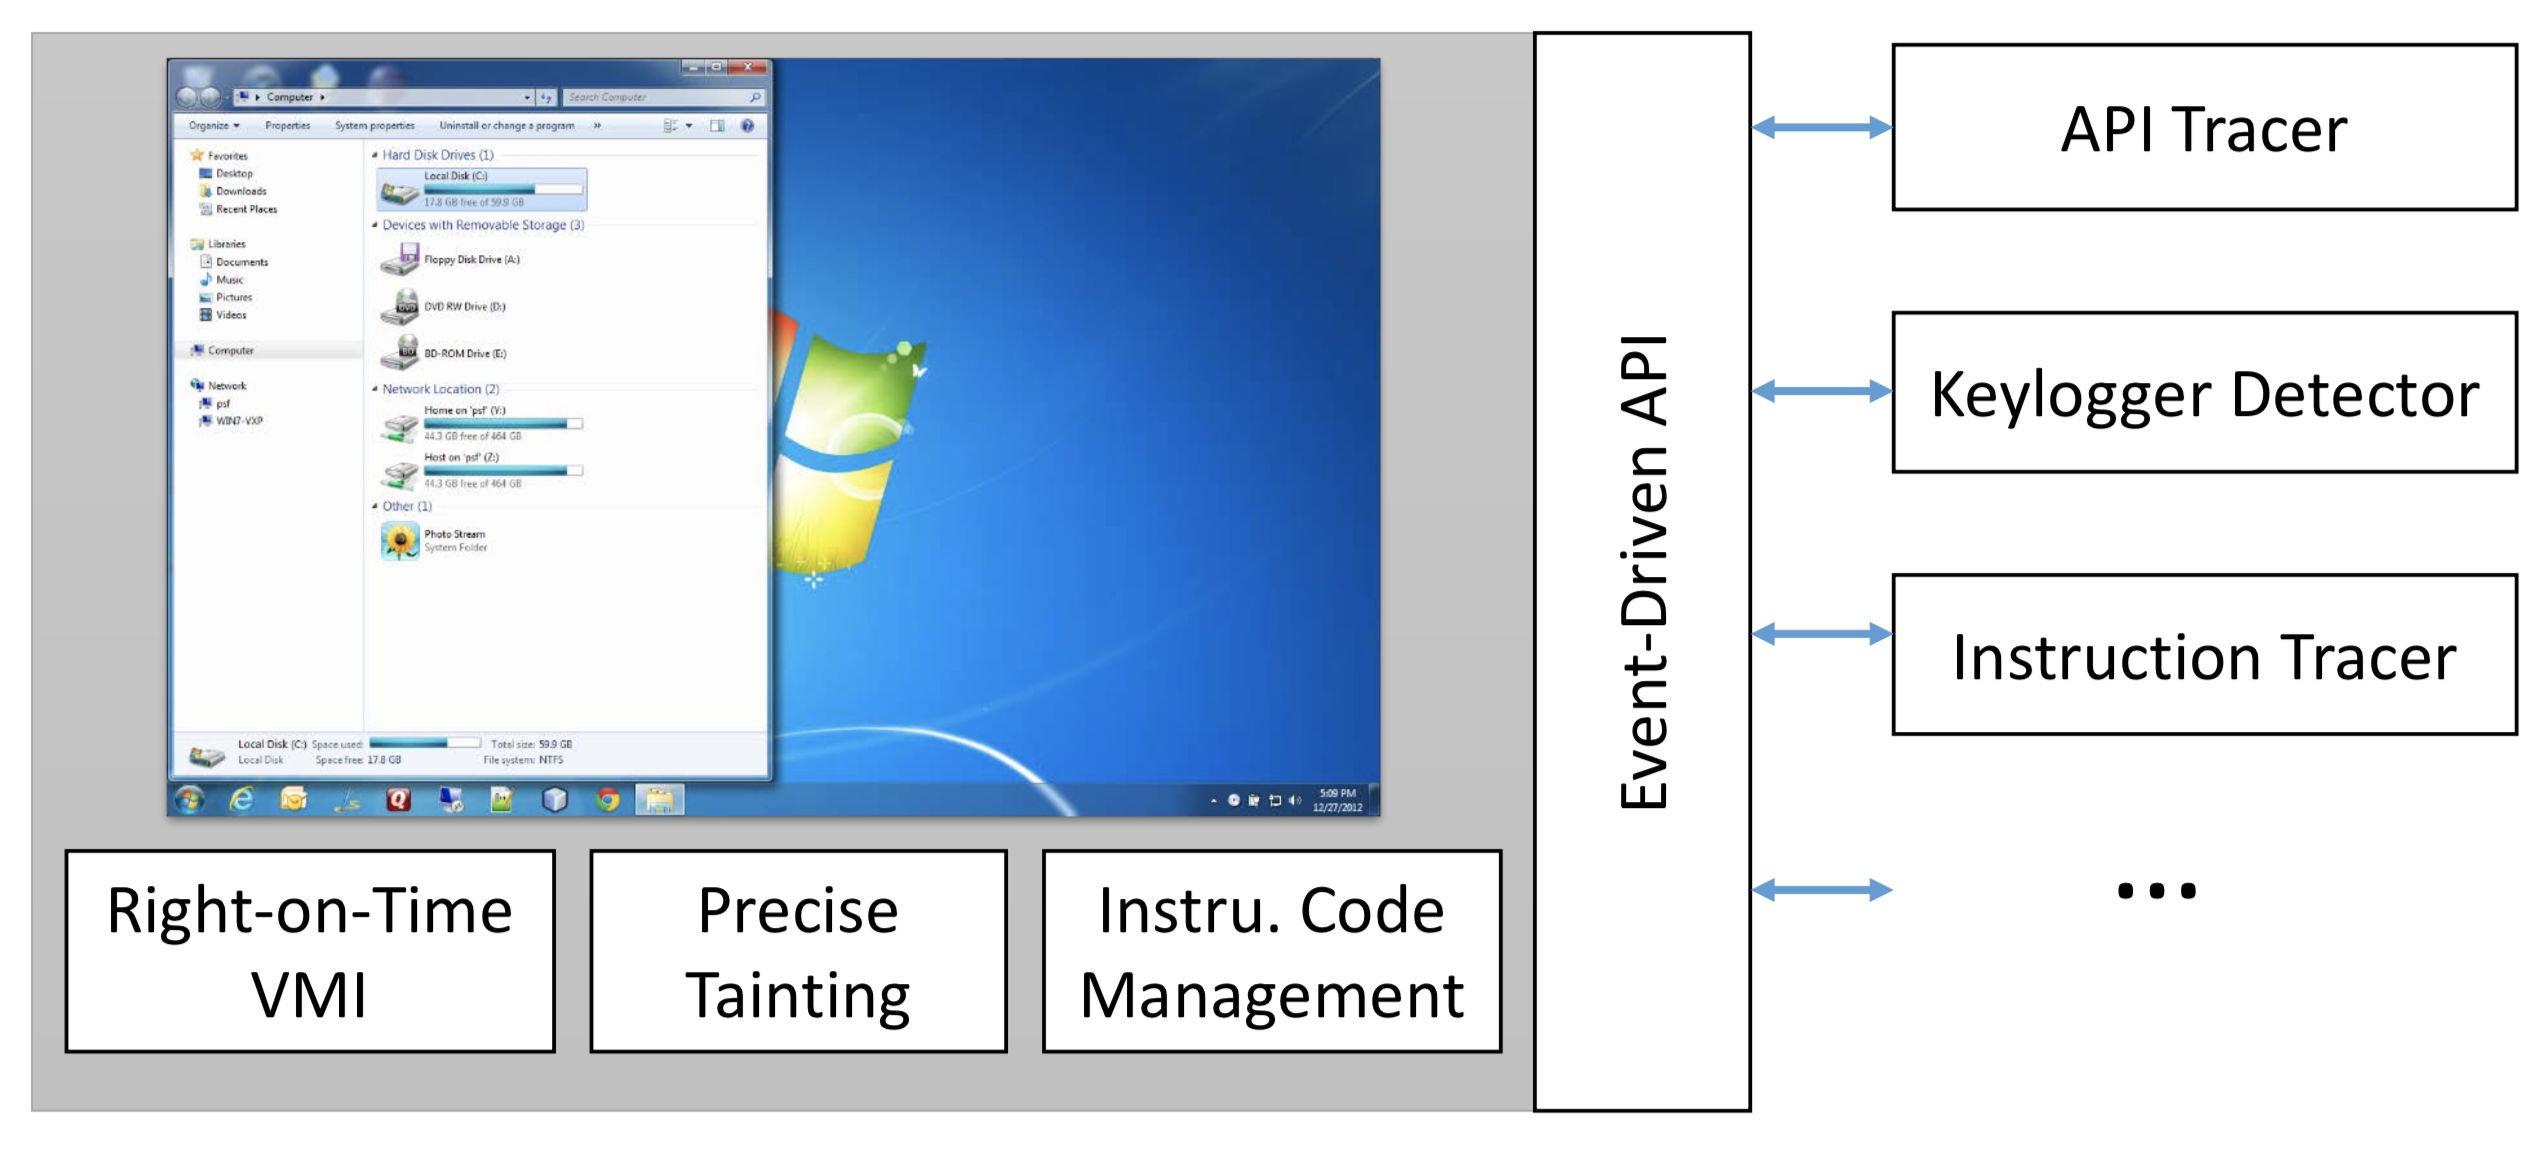 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 cryptogenic/ps5-ipv6-kernel-exploit
An experimental webkit-based kernel exploit (Arb. R/W) for the PS5 on <= 4.51FW
 wecooperate/imonitor
Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 reverseclabs/gwtmap
Maps attack surface of GWT applications by extracting obfuscated RPC endpoints and generating serialized request payloads for security testing.
 quarkslab/qsynthesis
Greybox Synthesizer geared for deobfuscation of assembly instructions.
 seemoo-lab/fitness-app
BLE-based Fitbit research tool for authentication replay, encrypted activity dump decryption, memory/firmware extraction, and custom firmware…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
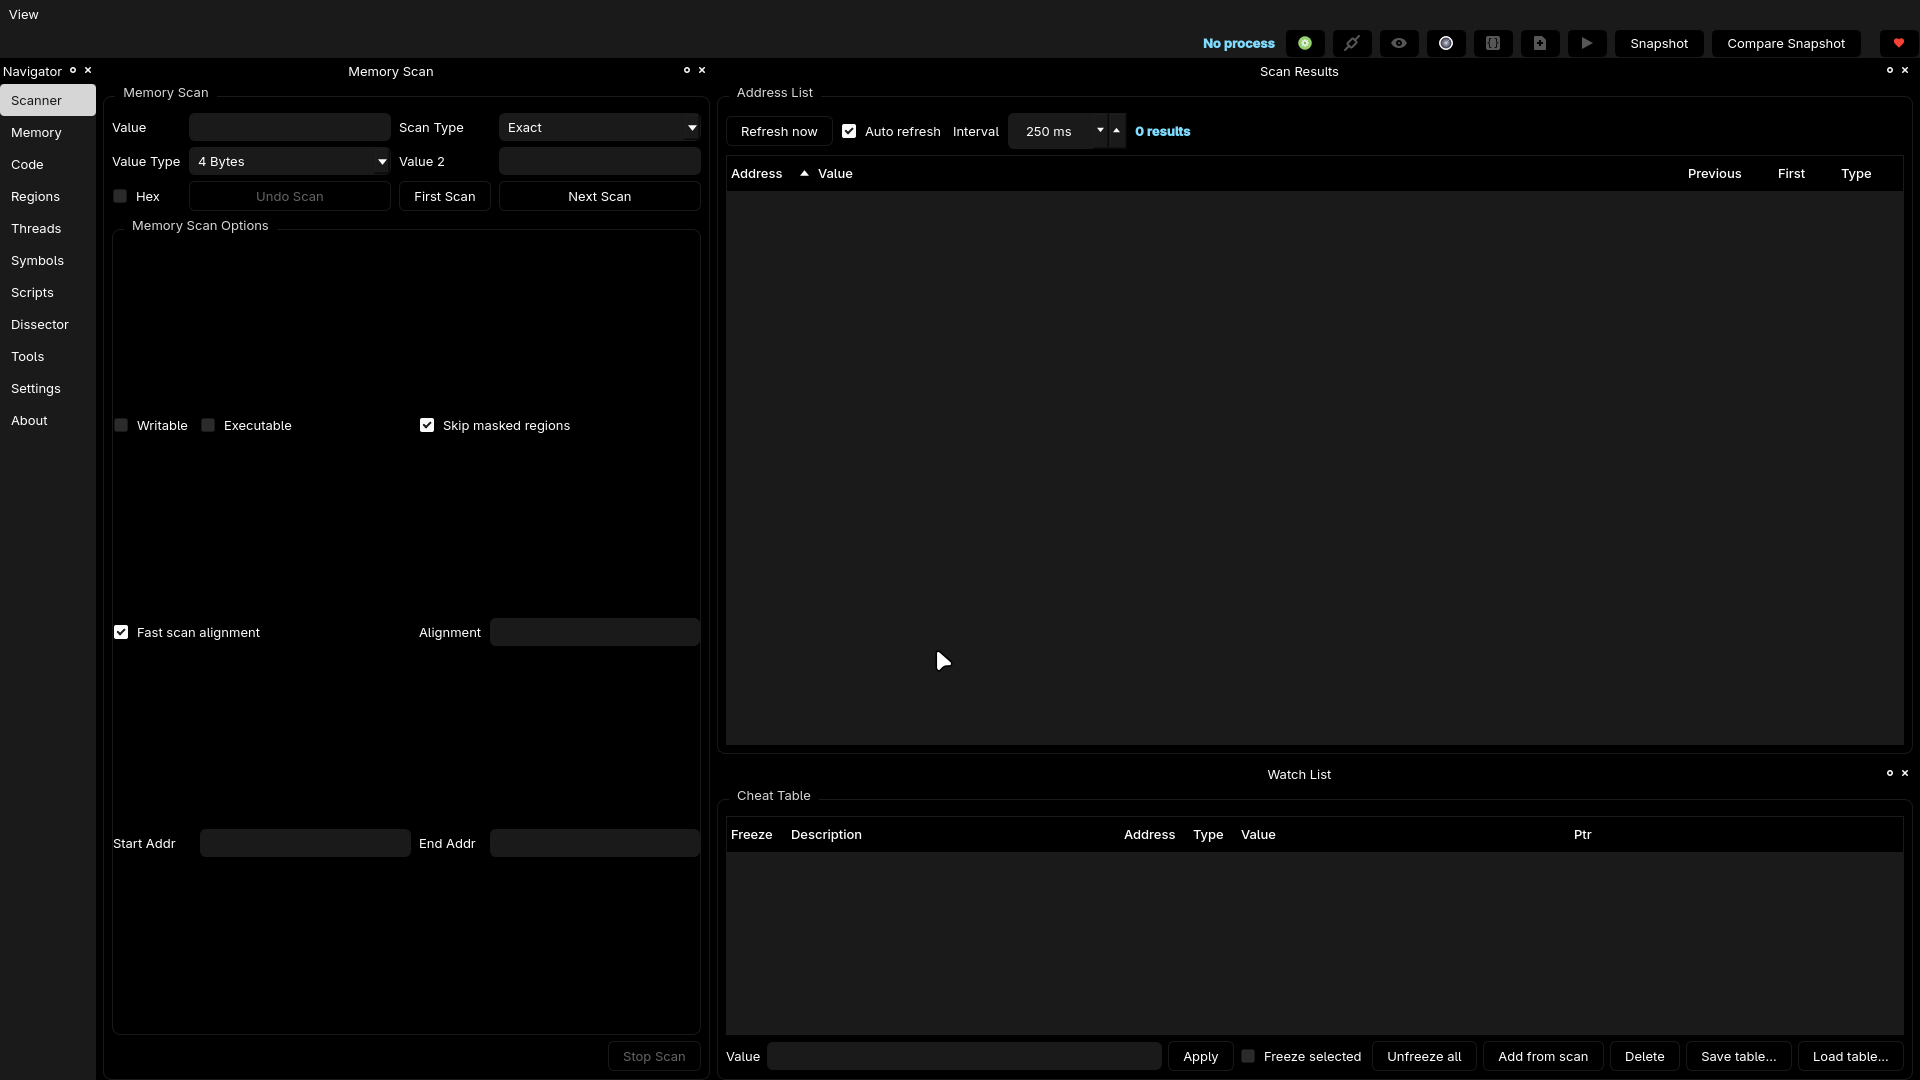 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 nccgroup/libmempool
Heap analysis tooling for mempool