
idahunt
 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
binary-analysisembedded-systems-securityfirmware-analysis+4
3943 years ago
nccgroup/idahuntidahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 colton1skees/dna
LLVM based static binary analysis framework
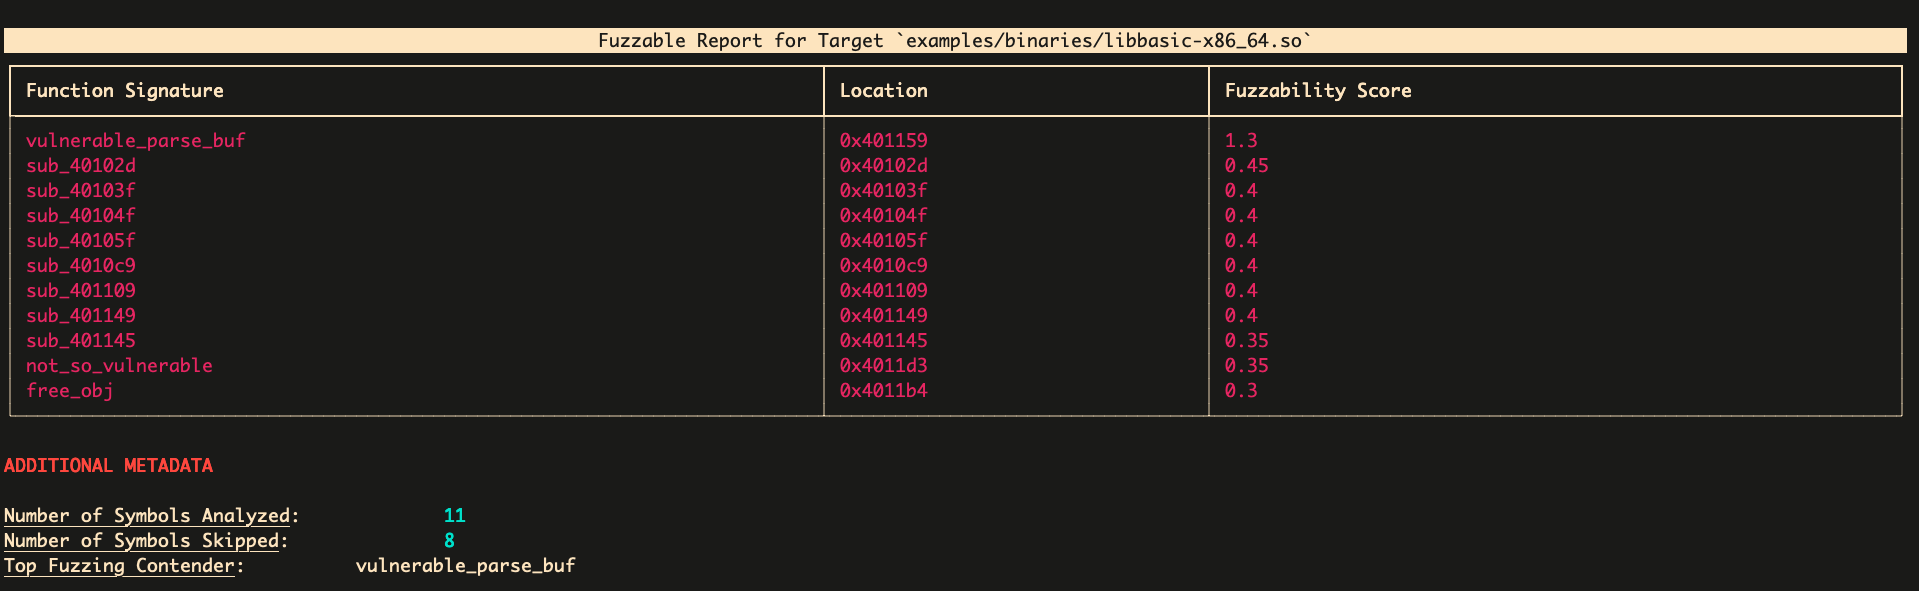 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
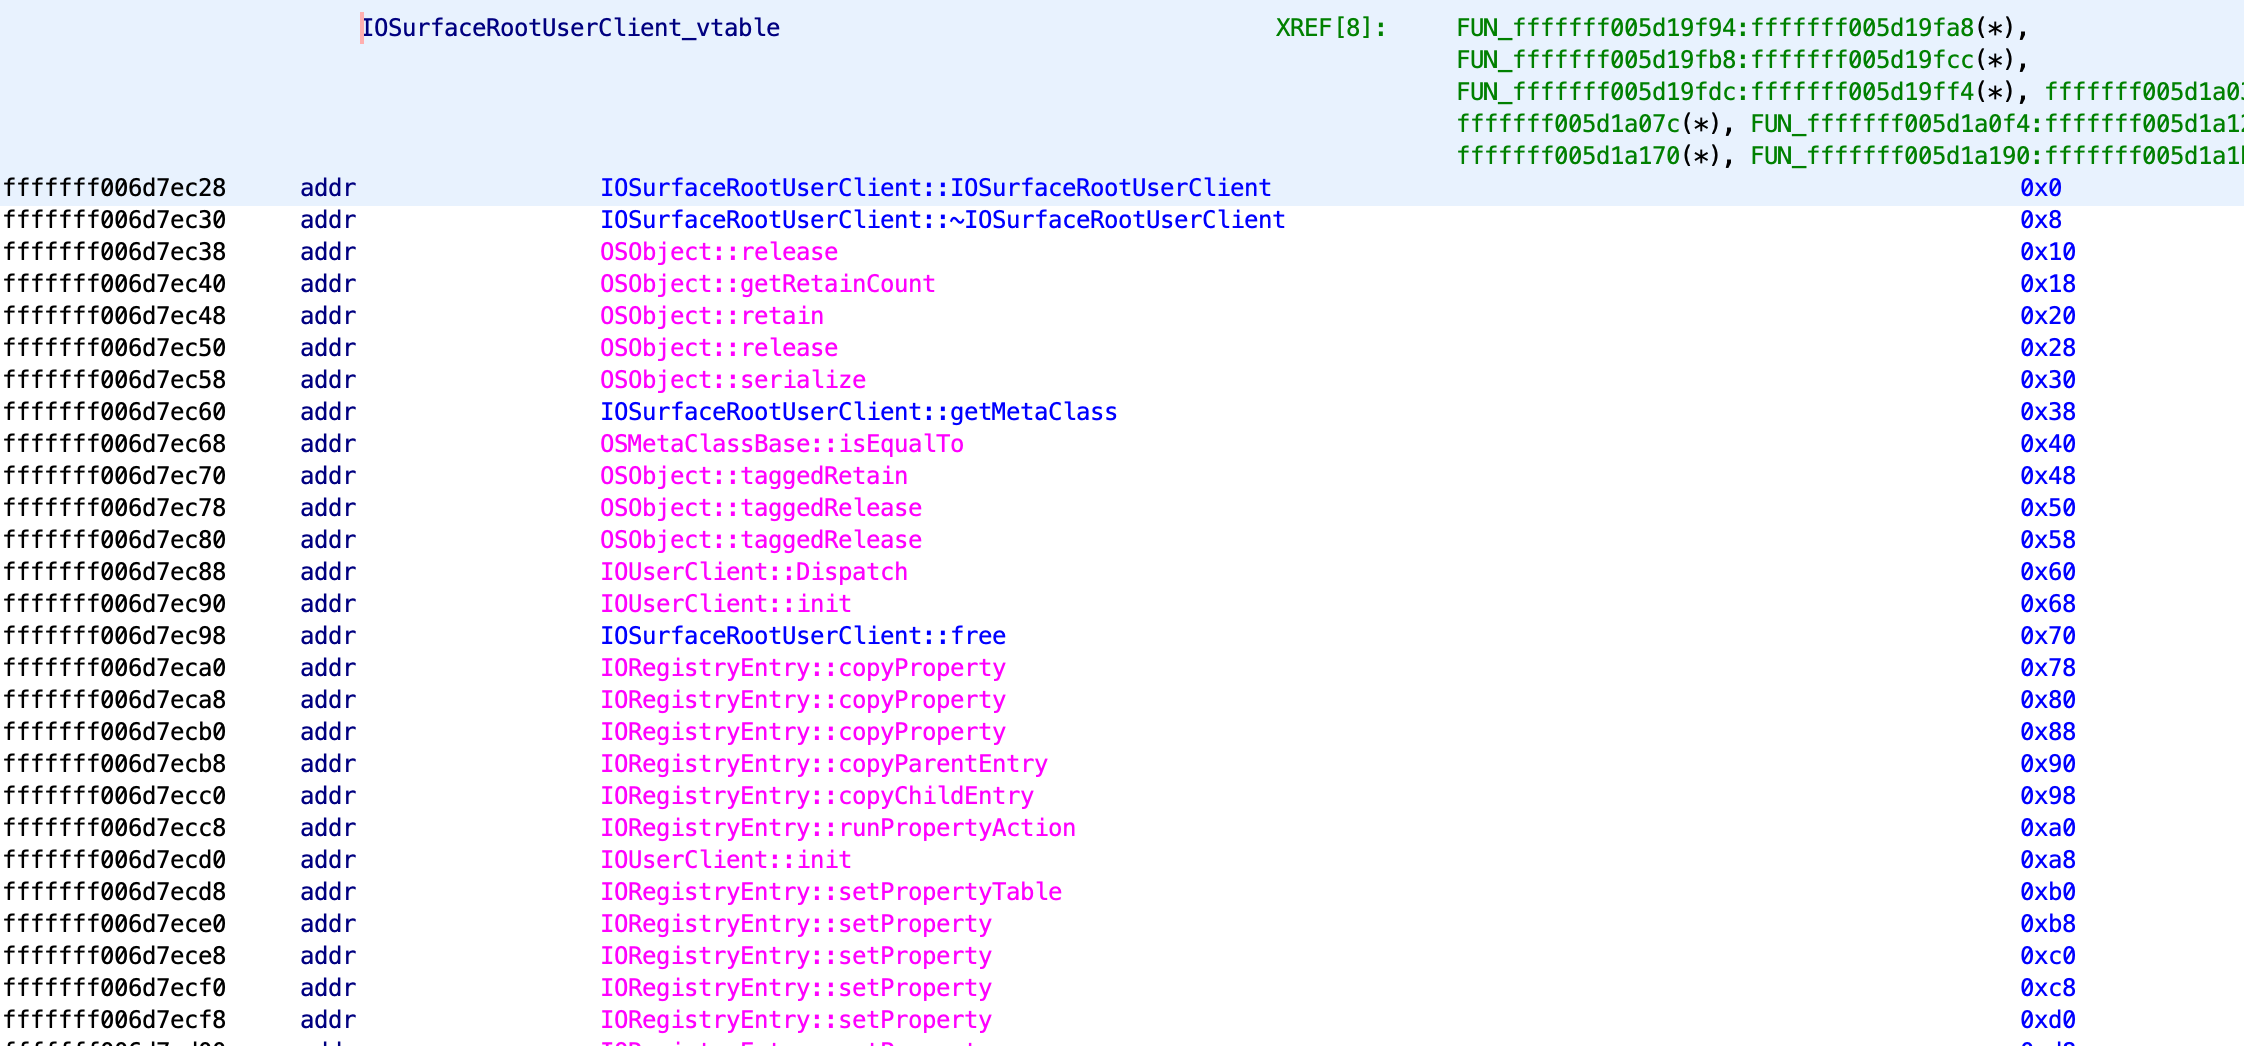 0x36/ghidra_kernelcache
a Ghidra framework for iOS kernelcache reverse engineering
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 nirizr/rematch
REmatch, a complete binary diffing framework that is free and strives to be open source and community driven.
 yifanlu/taihen
CFW framework for PS Vita
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
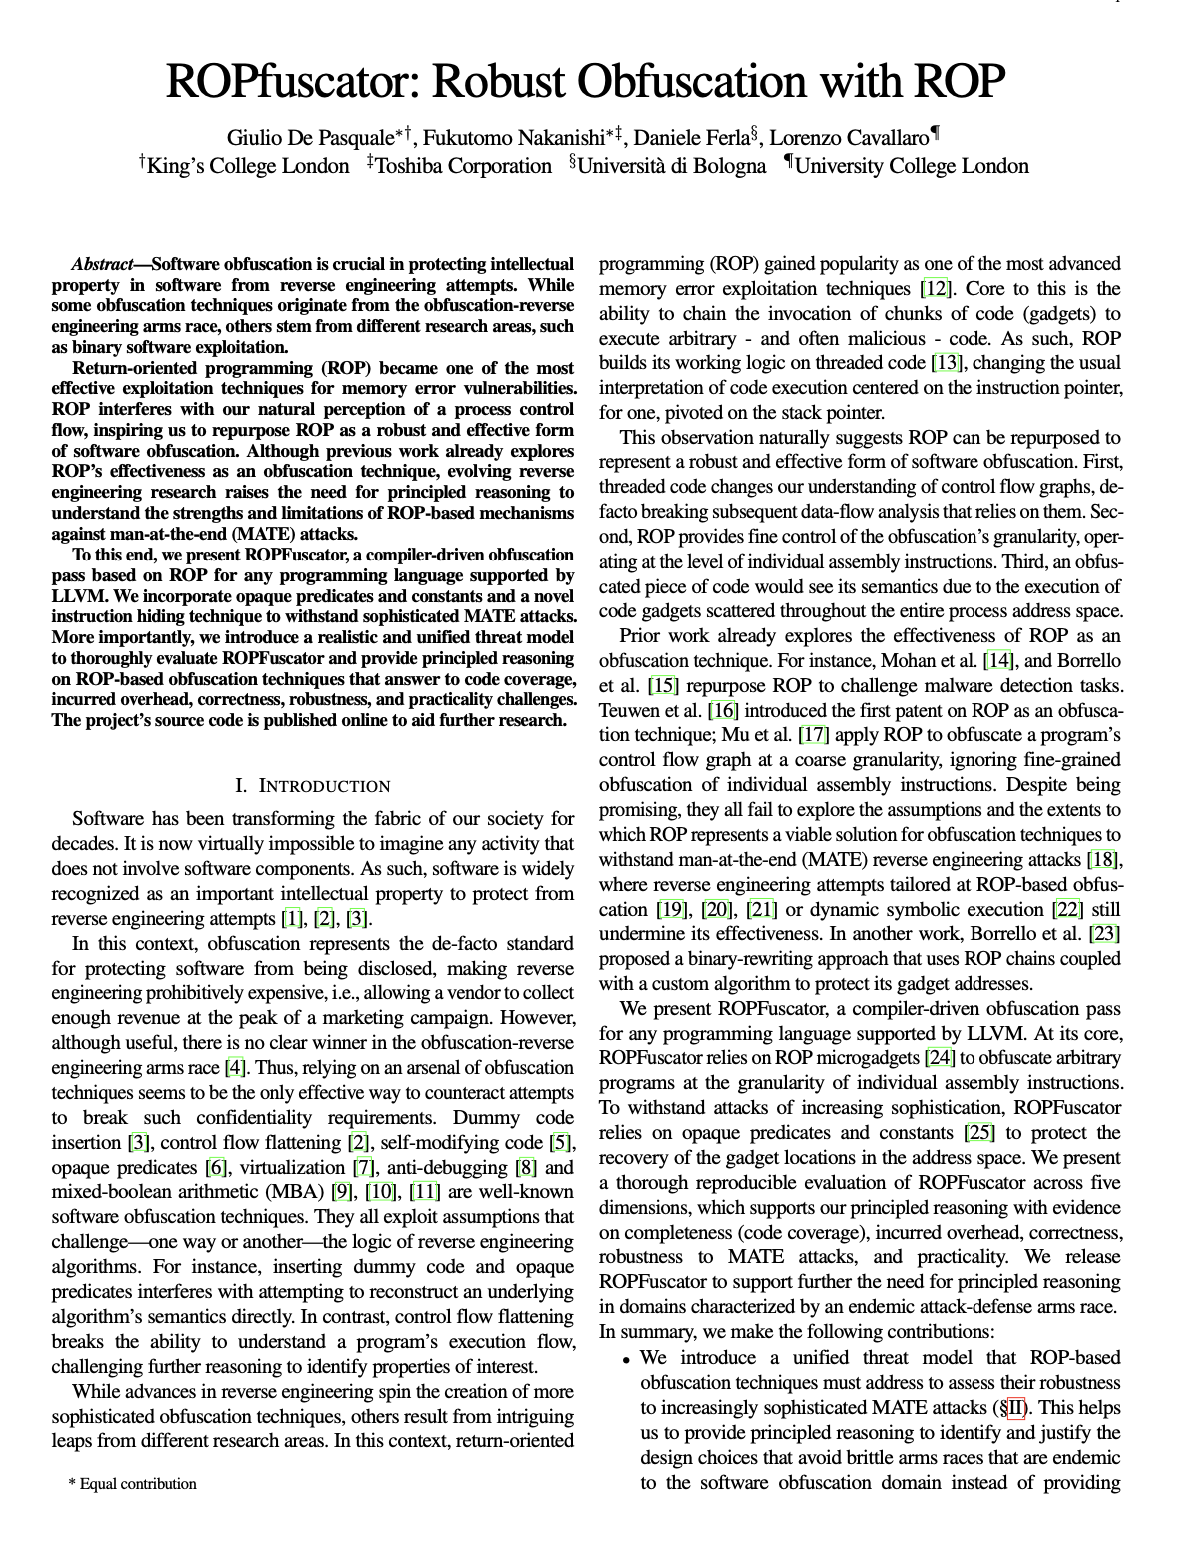 ropfuscator/ropfuscator
ROPfuscator is a fine-grained code obfuscation framework for C/C++ programs using ROP (return-oriented programming).
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 xepor/xepor
Flask-like routing framework for mitmproxy to intercept, modify, and spoof HTTP requests/responses. Enables rapid development of MITM scripts for…
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
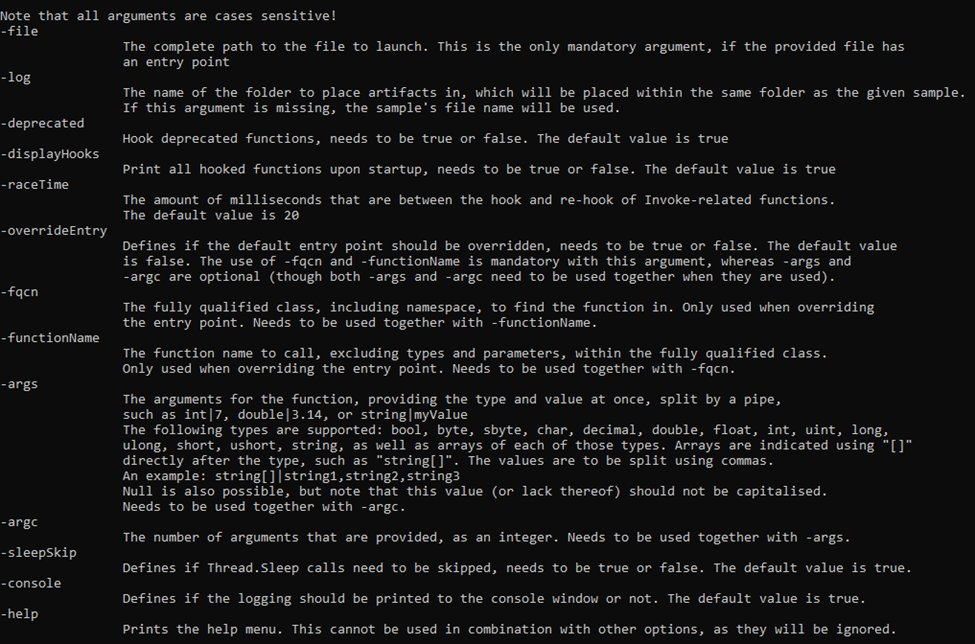 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics