
fusee-gelee
 oliviaholly/fusee-gelee
An implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.
binary-exploitationembedded-systems-securityexploitation+5
oliviaholly/fusee-geleeAn implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 beardypig/ghidra-emotionengine
Ghidra Processor for the Play Station 2's Emotion Engine MIPS based CPU
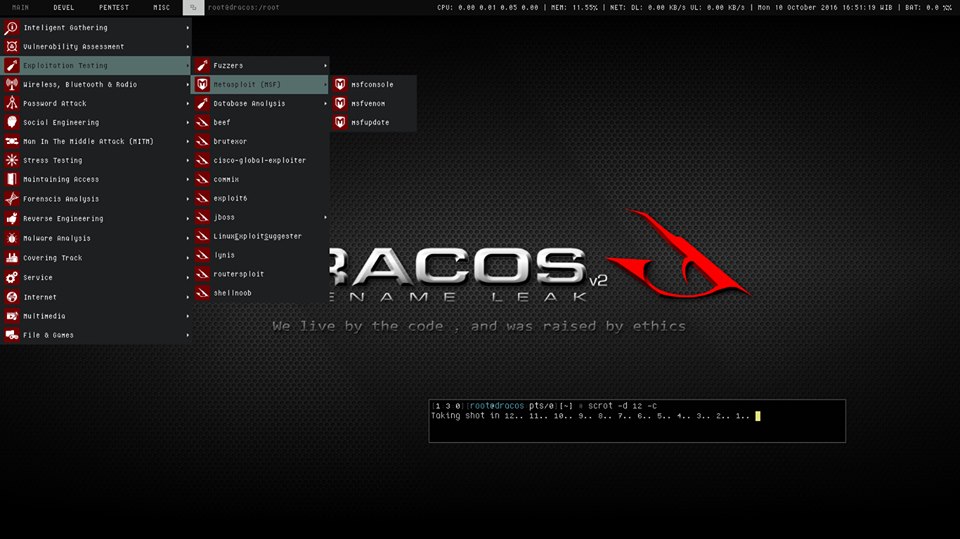 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 x86rc/vmp-lazy-unpack
Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
 lnversed/cve-2020-8423
Custom C exploit for CVE-2020-8423 targeting MIPS routers, featuring hooked open() syscall and tailored for Linux kernel 2.6.31.
 nccgroup/assethook
LD_PRELOAD magic for Android's AssetManager
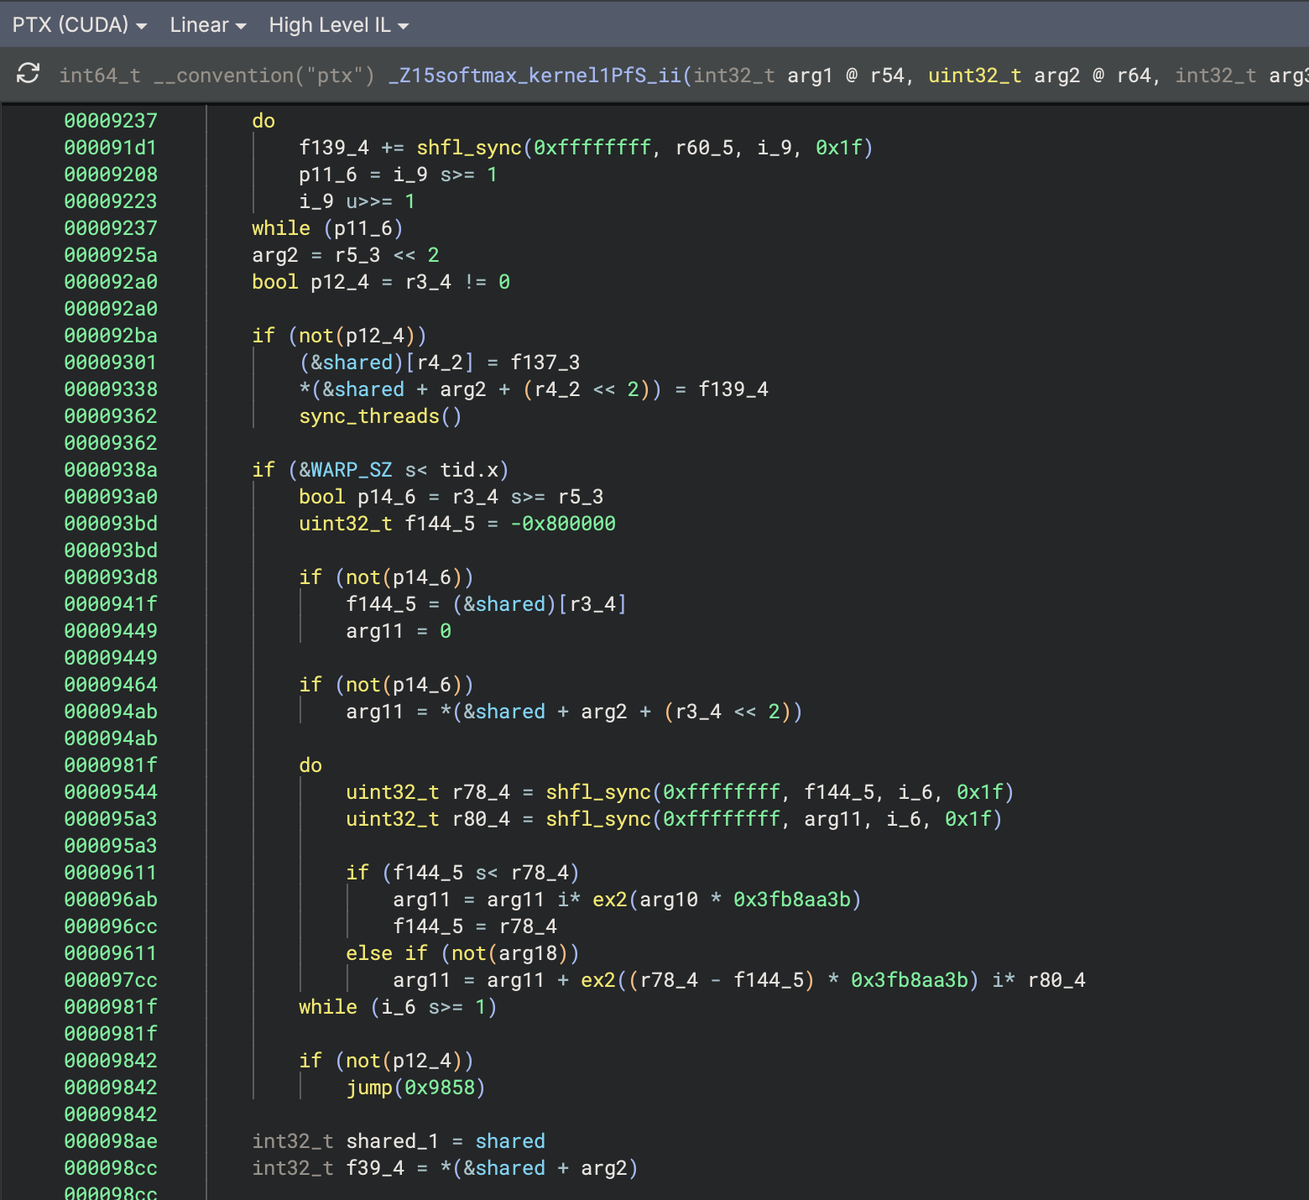 seekbytes/ptxninja
Binary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 abhi-r3v0/adhrit
Android Security Suite for in-depth reconnaissance and static bytecode analysis based on Ghera benchmarks.
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
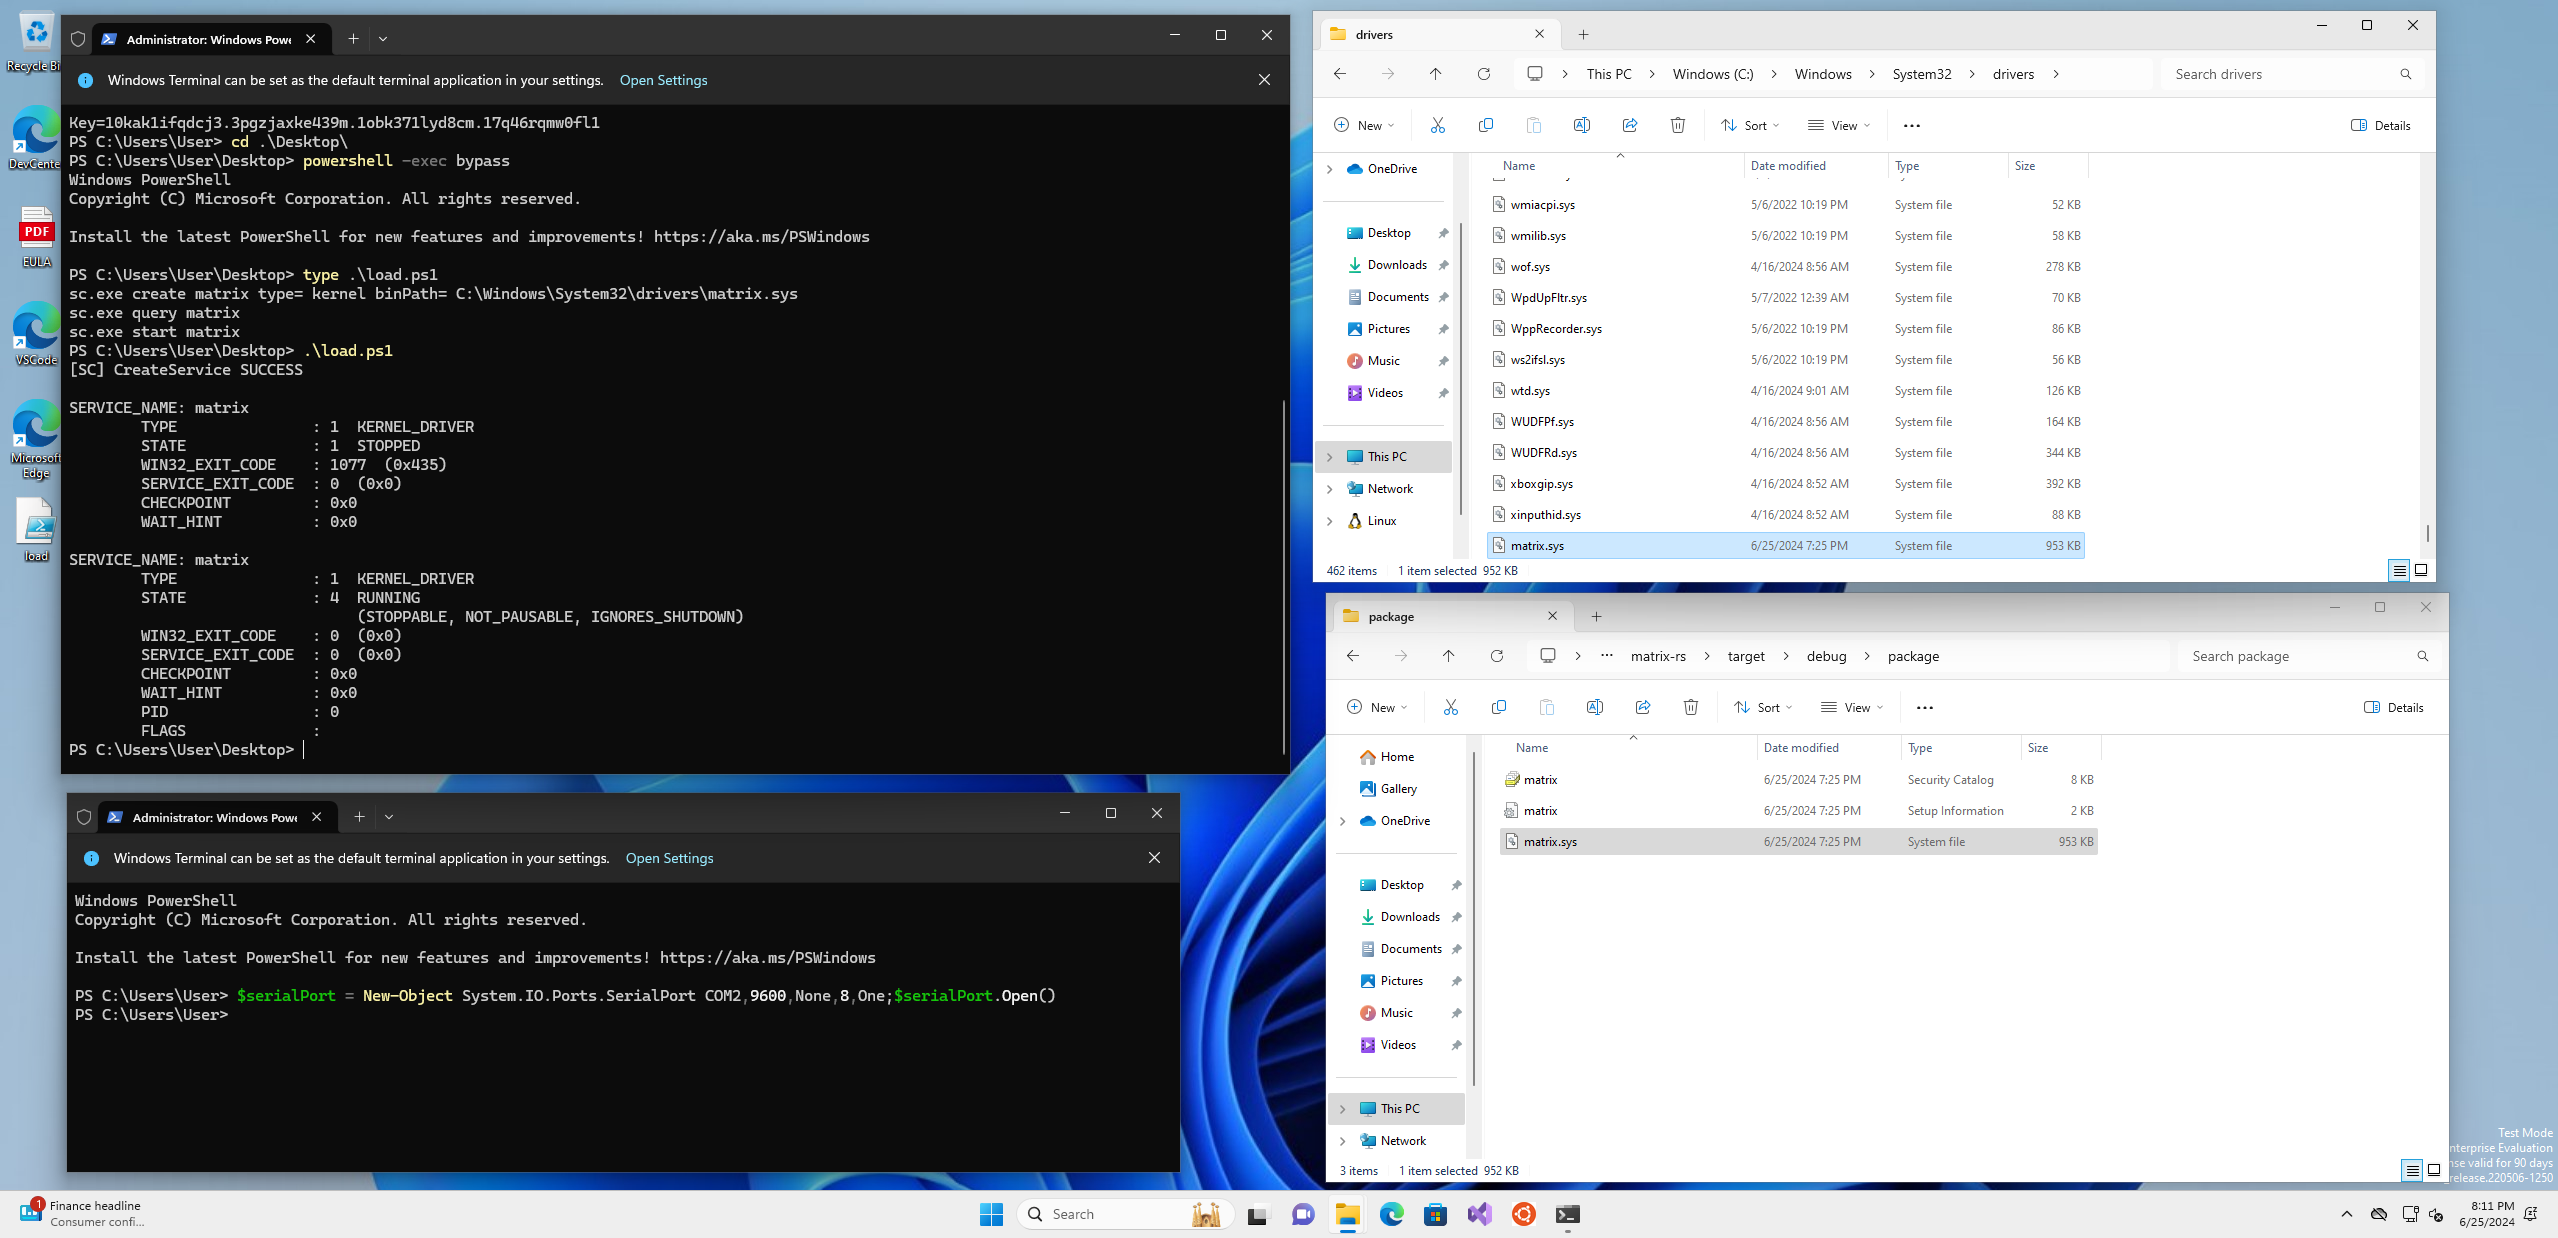 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)