
idalib-cli
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
ai-assisted-reversingbinary-analysiscode-analysis+5
22
ylca0/idalib-cliAgent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 de4dot/de4dot
.NET deobfuscator and unpacker.
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 eset/malware-research
Code written as part of our various malware investigations
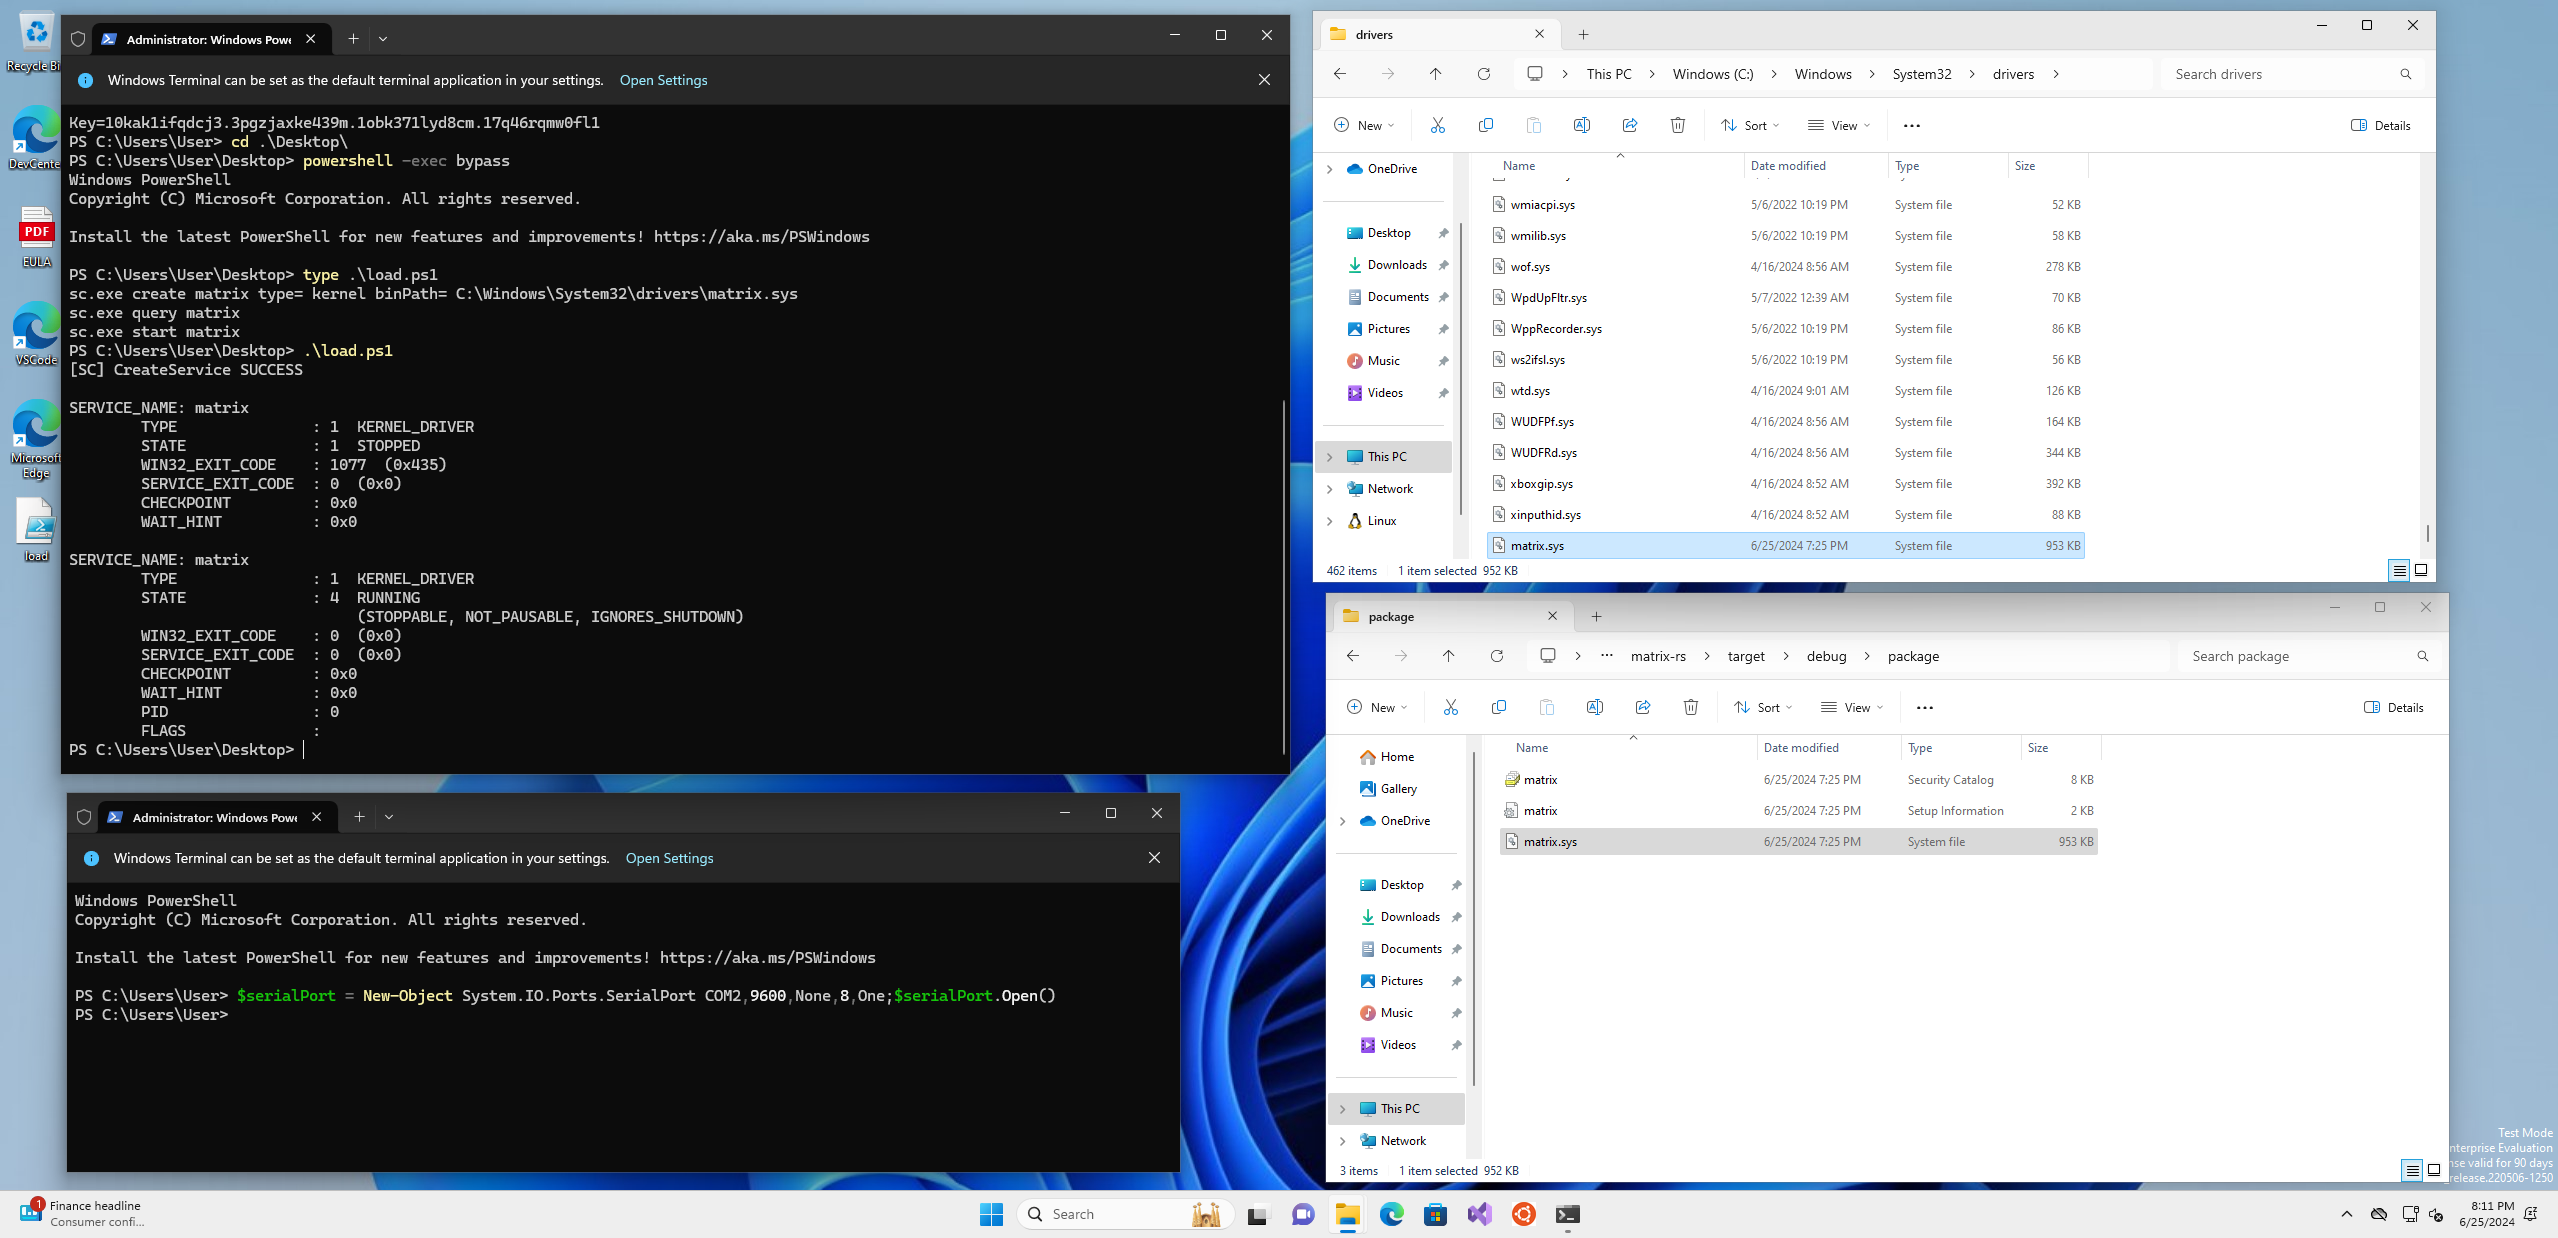 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 niklashigi/apk-mitm
🤖 A CLI application that automatically prepares Android APK files for HTTPS inspection
 cy-clon3/awesome-ios-security
A curated list of awesome iOS application security resources.
 soulghost/iblessing
iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can…
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
 stefan2200/aparoid
Static and dynamic Android application security analysis
 commando-x/vuln-bank-mobile
A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!