
TXDXCristhian_2023-CVE-38831
 cristhiansm0/txdxcristhian_2023-cve-38831
CVE-2023-38831 WinRAR lab: detection with Sysmon/Wazuh, reverse engineering with Ghidra, patch analysis, and remediation.
educationincident-responselabs-practice+3
cristhiansm0/txdxcristhian_2023-cve-38831CVE-2023-38831 WinRAR lab: detection with Sysmon/Wazuh, reverse engineering with Ghidra, patch analysis, and remediation.
 faizan-khanx/cve-2024-38063
CVE-2024-38063 - Remotely Exploiting The Kernel Via IPv6
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
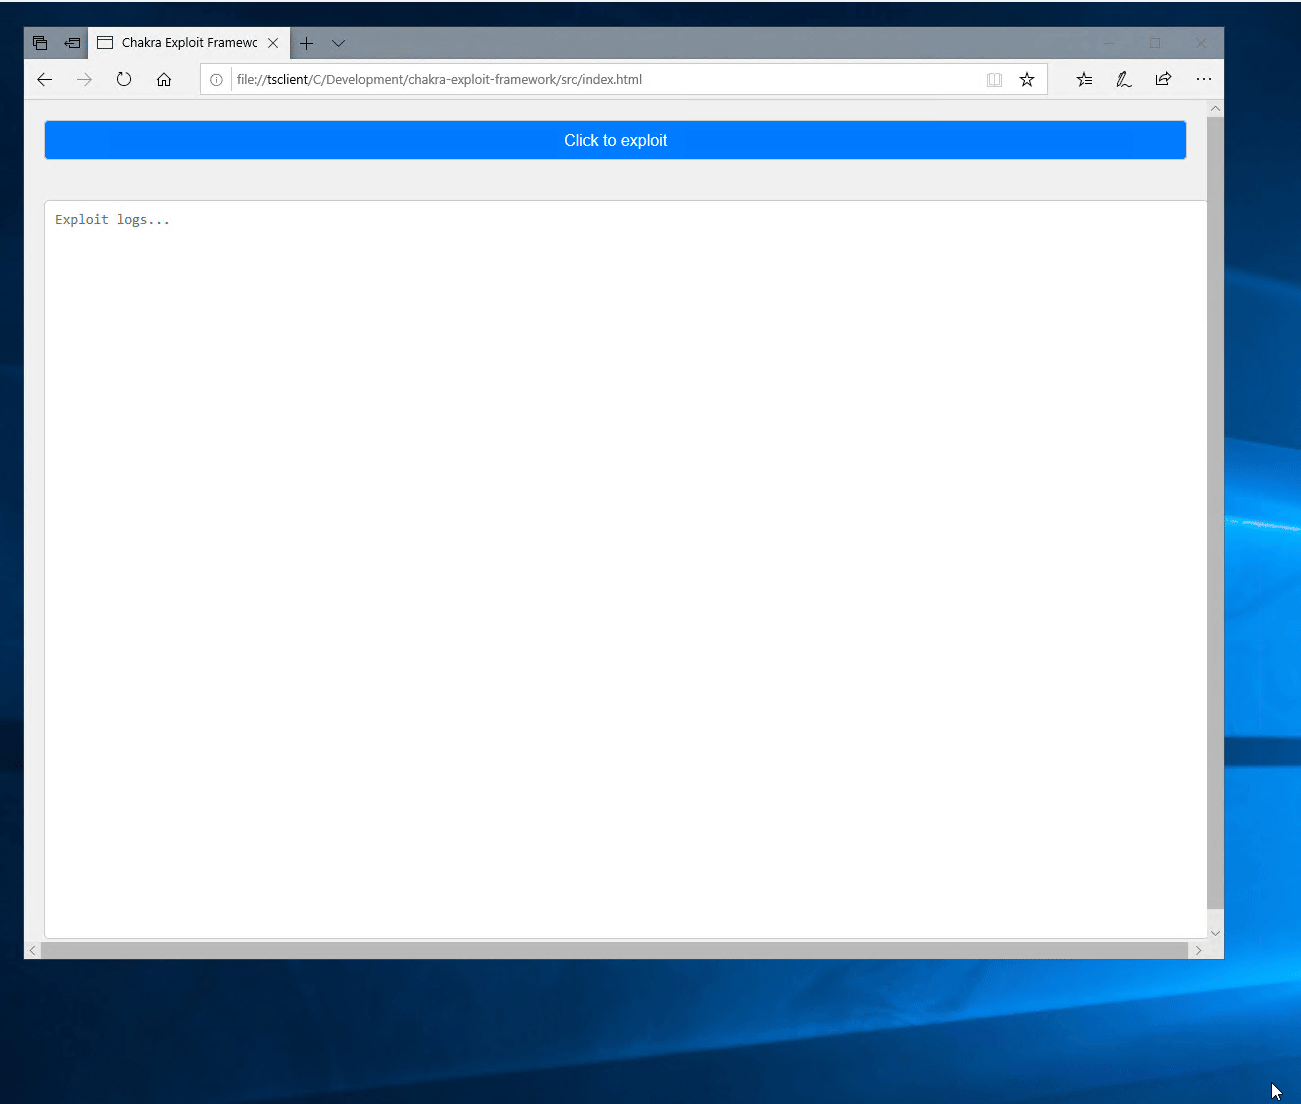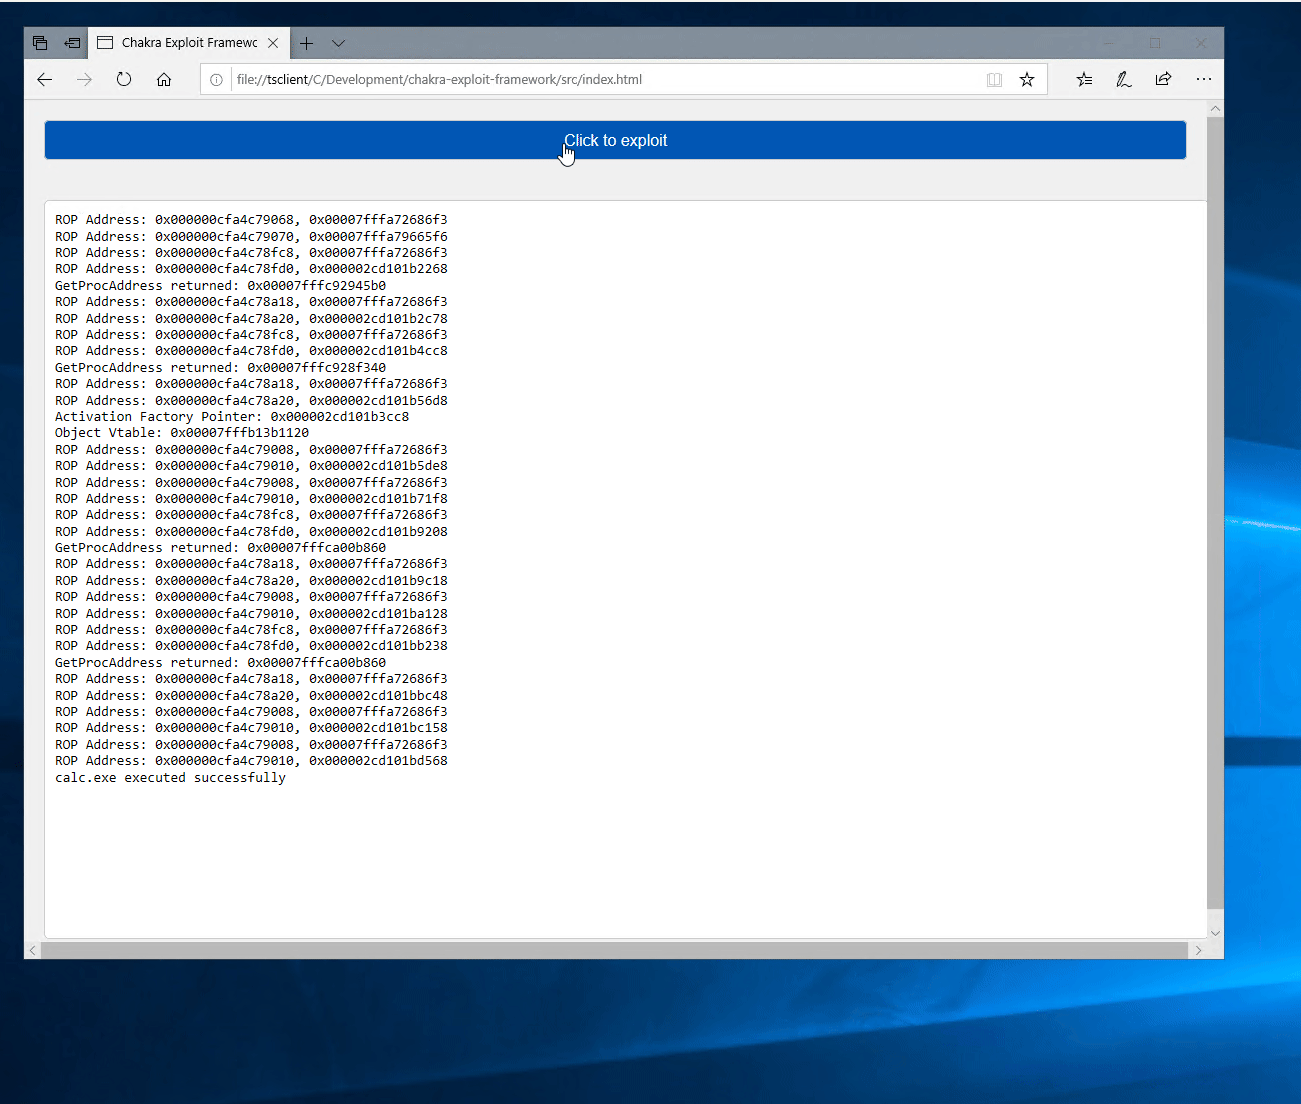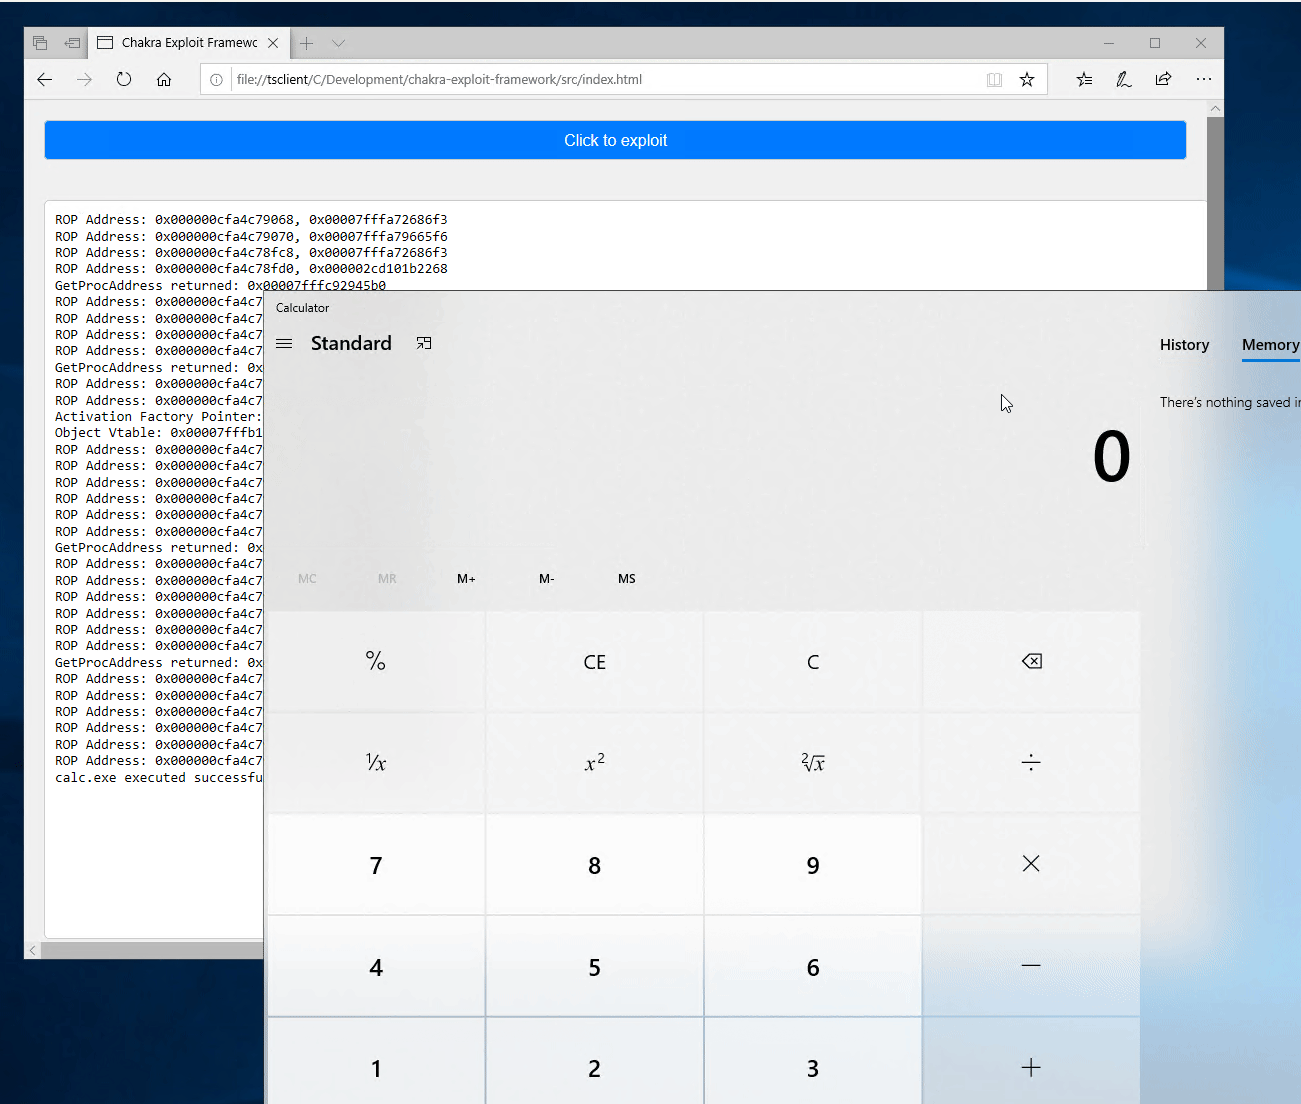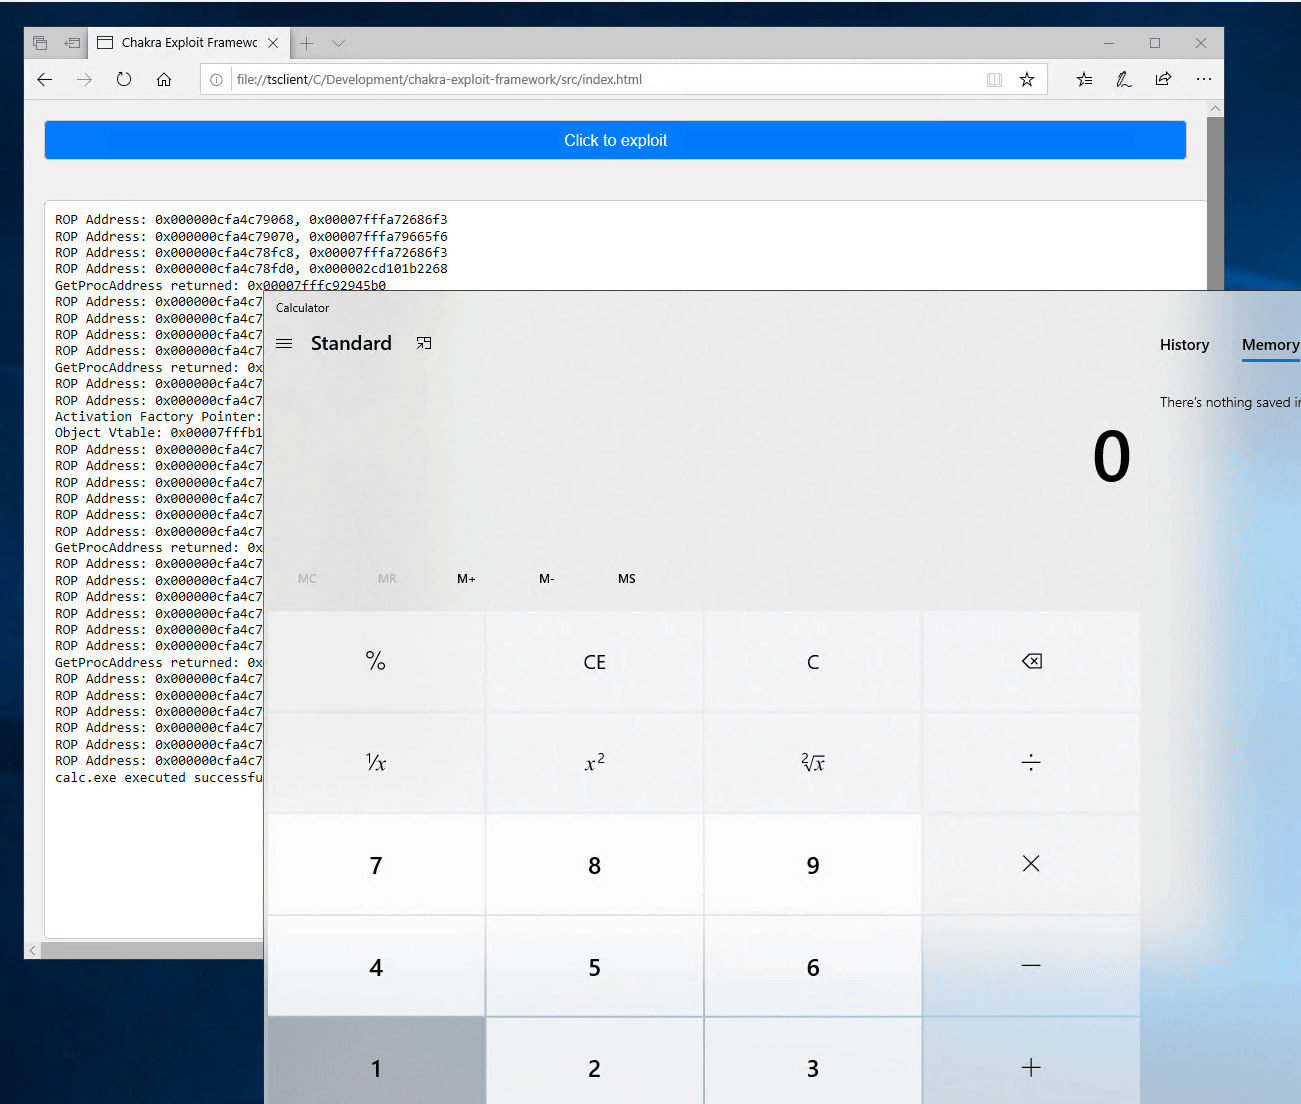 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 yeonnic/look-at-the-xnu-through-a-tube-cve-2018-4242-write-up-translation-
Detailed technical write-up and translation of CVE-2018-4242, an XNU kernel vulnerability in AppleHV, with PoC code, reverse engineering analysis,…
 highandhigh/cve-2015-0057
Detailed technical analysis and exploit implementation for CVE-2015-0057, a win32k.sys use-after-free vulnerability, covering 32-bit and 64-bit…
 sastraadiwiguna-purpleeliteteaming/cisco-ios-exploitation-jaguar_tooth-cve-2017-6742-reconstruction
Comprehensive 100% Unrestricted Technical Analysis of JAGUAR_TOOTH Malware (APT28). High-precision reconstruction of Cisco IOS SNMP exploitation, ROP…
 kylvgoi/cve-2019-1663
Educational exploit for CVE-2019-1663 targeting a stack-based buffer overflow in Cisco RV routers. Includes a Python exploit script, reverse shell…
 nuky-alt/cve-2025-8088
Proof-of-concept exploit and technical analysis for a WinRAR path traversal vulnerability enabling code execution via crafted archives with binary…
 jgs-developer/cve-2025-5548
Stack-based buffer overflow exploit for FreeFloat FTP Server, demonstrating reverse engineering, EIP control, and shellcode execution for educational…
 psycho-prince/cve-2025-56513-nicehash-update-chain-compromise
Critical supply-chain vulnerability research on NiceHash QuickMiner update mechanism (CVE-2025-56513). Includes technical analysis, attack scenarios,…
 whs-segfault/cve-2021-39863
Exploit for Adobe Acrobat Reader DC heap buffer overflow (CVE-2021-39863) with ASLR/DEP bypass, including root cause analysis and reversed vulnerable…
 themalwareguardian/cve-2025-34096
SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.
 shinycolumn/cve-2025-56802
AES-CFB Key Generation and Management Vulnerability in Reolink Desktop Application
 greycat-amc/cve-2025-5548
Analisis de CVE relacionada con stack overflow
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
 uky007/cve-2025-62215_analysis
CVE-2025-62215 exploit development using Claude Code Agent Team
 thomrgn/xzutils_backdoor_obfuscation
Script to obfuscate a payload the same way as it was done by the XZ utils attack (CVE-2024-3094)