

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
193
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 threatlabz/tools
Tools developed by the Zscaler ThreatLabz Threat Intelligence team
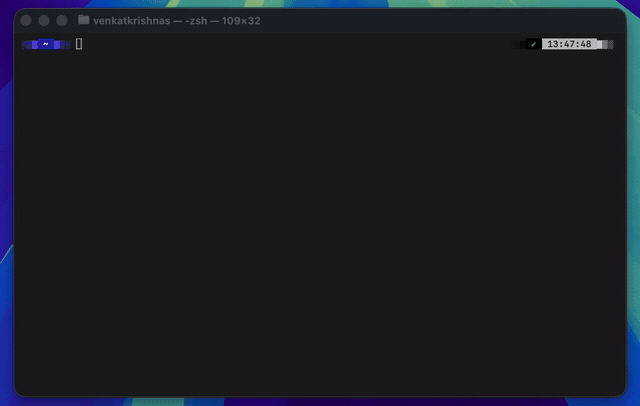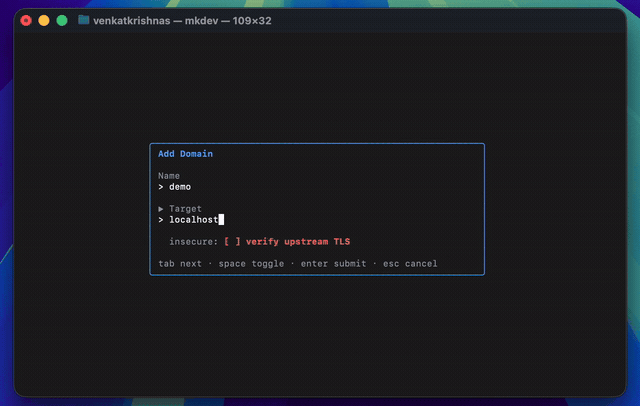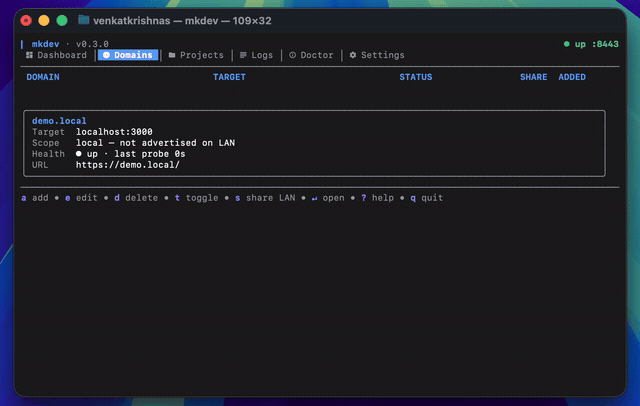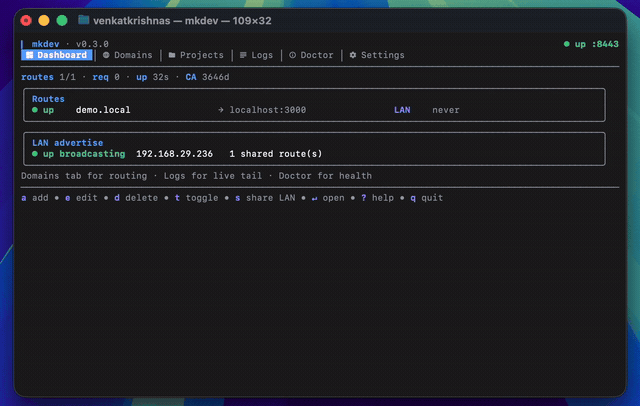 venkatkrishna07/mkdev
Trusted localhost HTTPS — local CA, /etc/hosts, mDNS LAN sharing, reverse proxy. Maps https://name.local → localhost:port
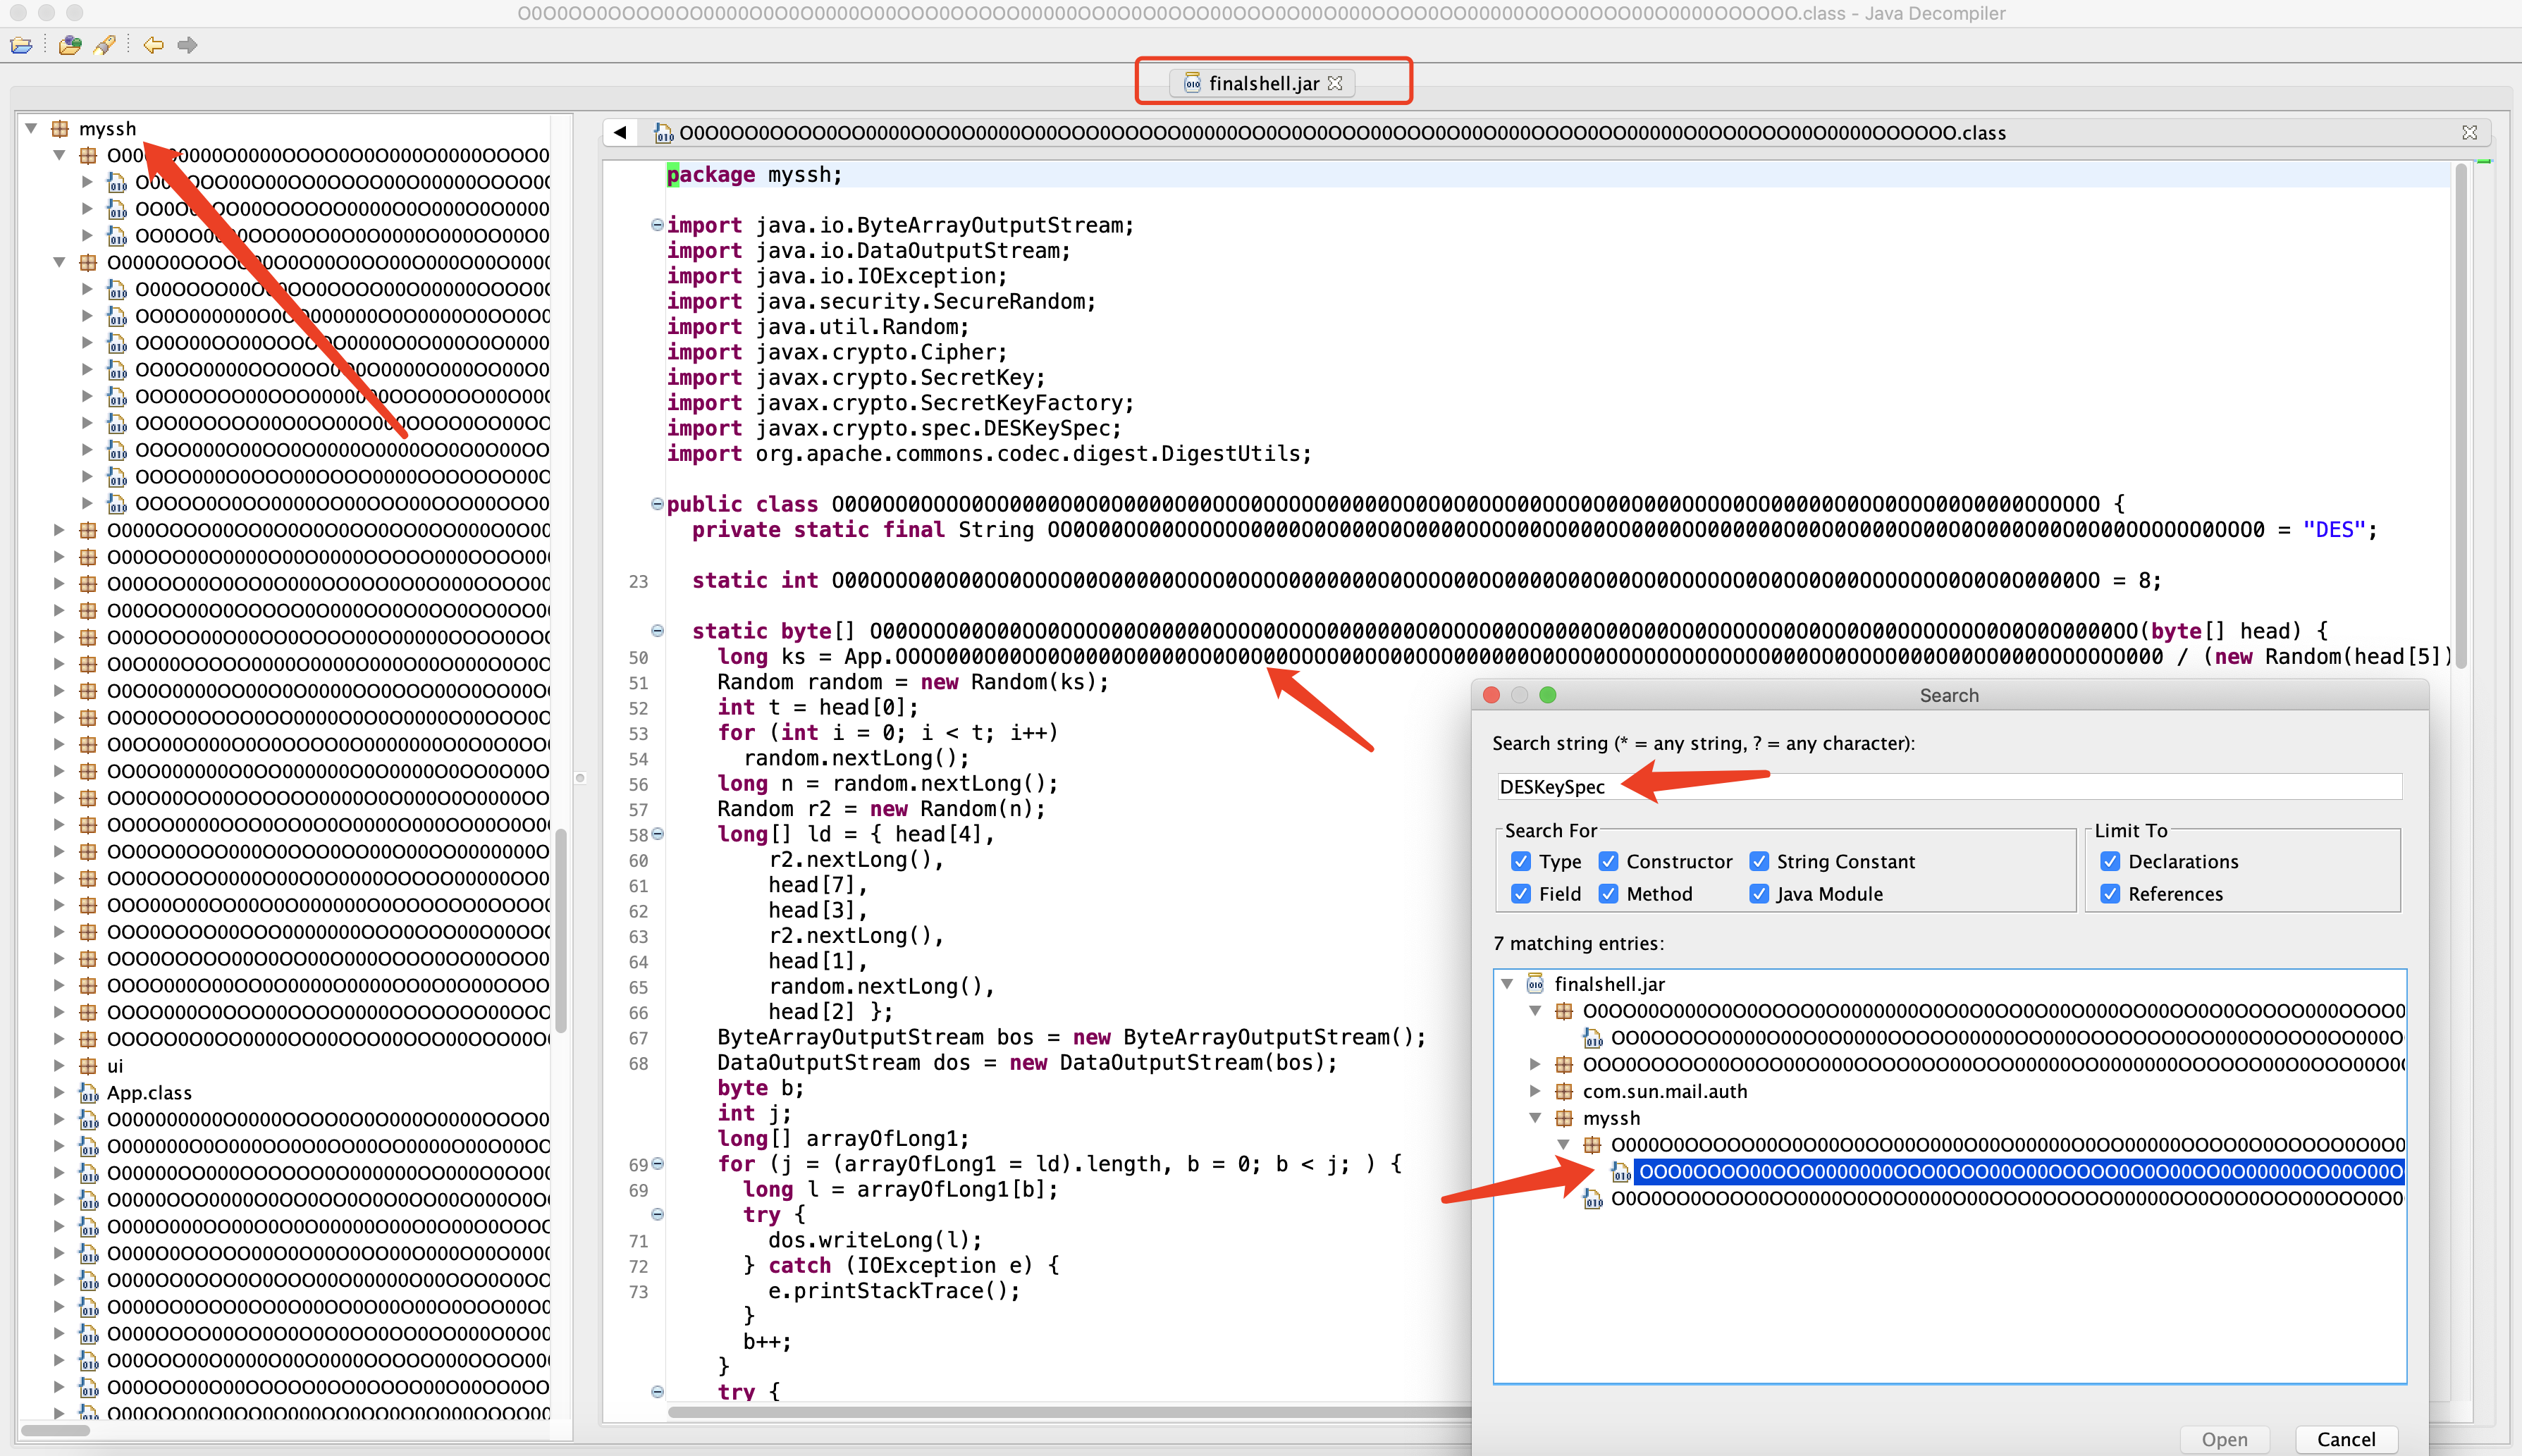 jas502n/finalshelldecodepass
FinalShellDecodePass 加密解密
 x86byte/sbox
Compile-time AES string obfuscation for C++
 lawndoc/mediator
An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
 kcreyts/plugxdecoder
Decodes PlugX traffic and encrypted/compressed artifacts
 nccgroup/pip3line
The Swiss army knife of byte manipulation
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 reecdeep/hivev5_file_decryptor
Hive v5 file decryption algorithm
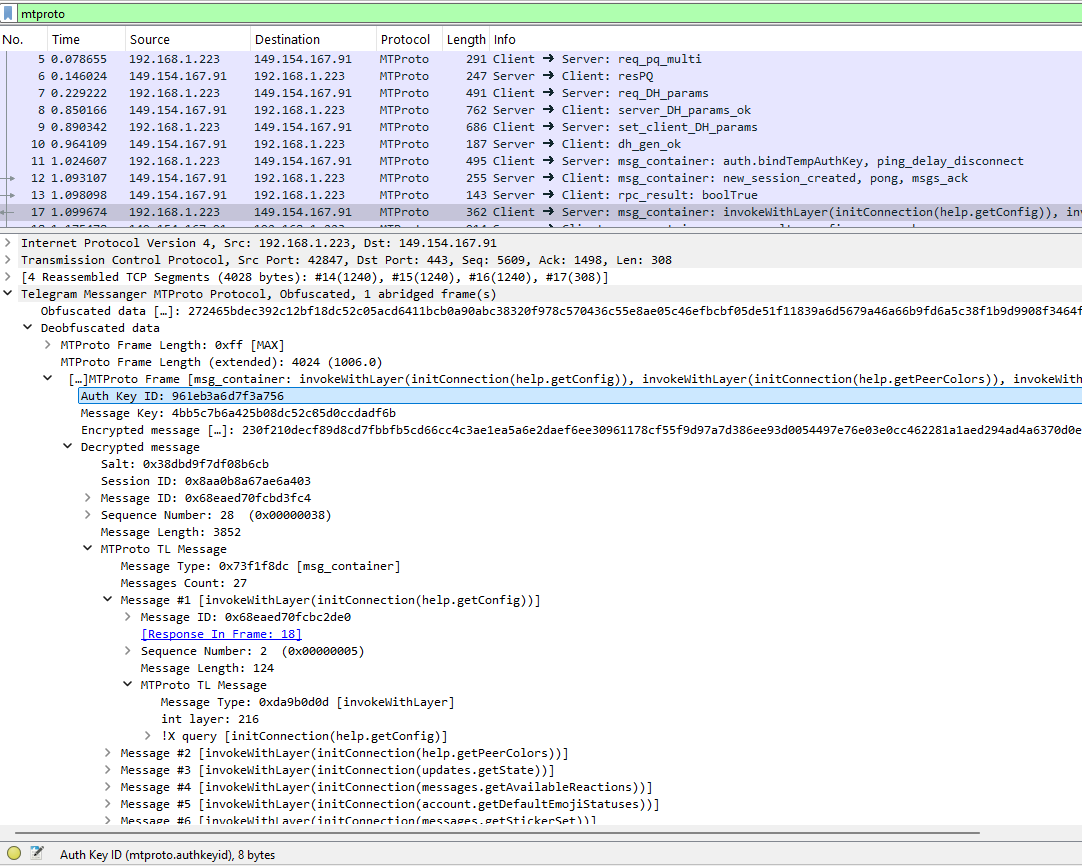 tomer8007/mtproto-dissector
Wireshark plugin for dissecting the Telegram protocol
 farghlymal/config-extractors
Extracts and decrypts malware configuration data from captured samples, automating C2 endpoint discovery, credential extraction, and indicator triage…
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan
 jas502n/phpstudy-backdoor
phpstudy dll backdoor for v2016 and v2018
 iss4cf0ng/openshell
Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…
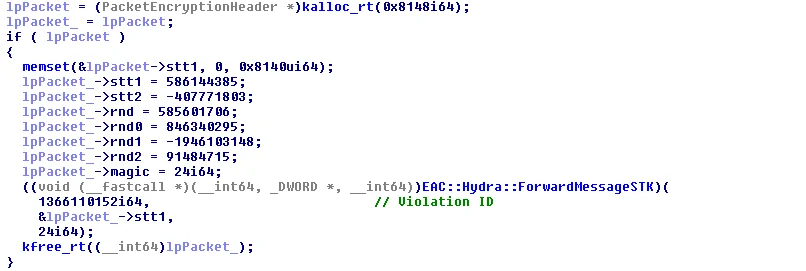 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 eastarctica/cve-2026-43813
CVE-2026-43813: CloudAttestation enforceEnvironment bypass