
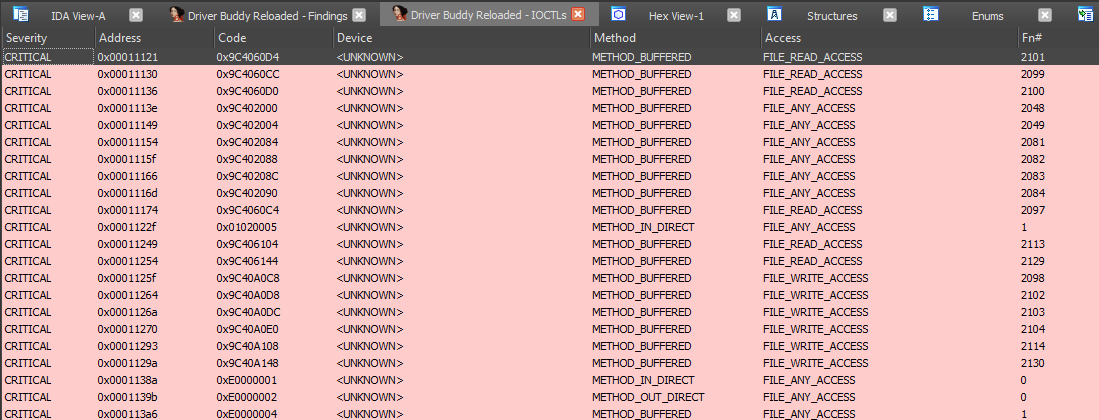
DriverBuddyReloaded
 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
binary-analysisdebuggersreverse-engineering+2
440
voidsec/driverbuddyreloadedDriver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
 oalabs/blobrunner
Quickly debug shellcode extracted during malware analysis
 hfiref0x/wdextract
Extract Windows Defender database from vdm files and unpack it
 nirizr/rematch
REmatch, a complete binary diffing framework that is free and strives to be open source and community driven.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery
 lucamassarelli/yarasafe
SAFE embeddings to match functions in yara
 adamlaurie/hdmi-sniff
sniff HDMI DDC (I2C) traffic
 nozominetworks/upx-recovery-tool
Automates repair of malformed UPX headers in ELF binaries, restoring magic, filesize, blocksize, and overlay fields so standard unpackers can process…
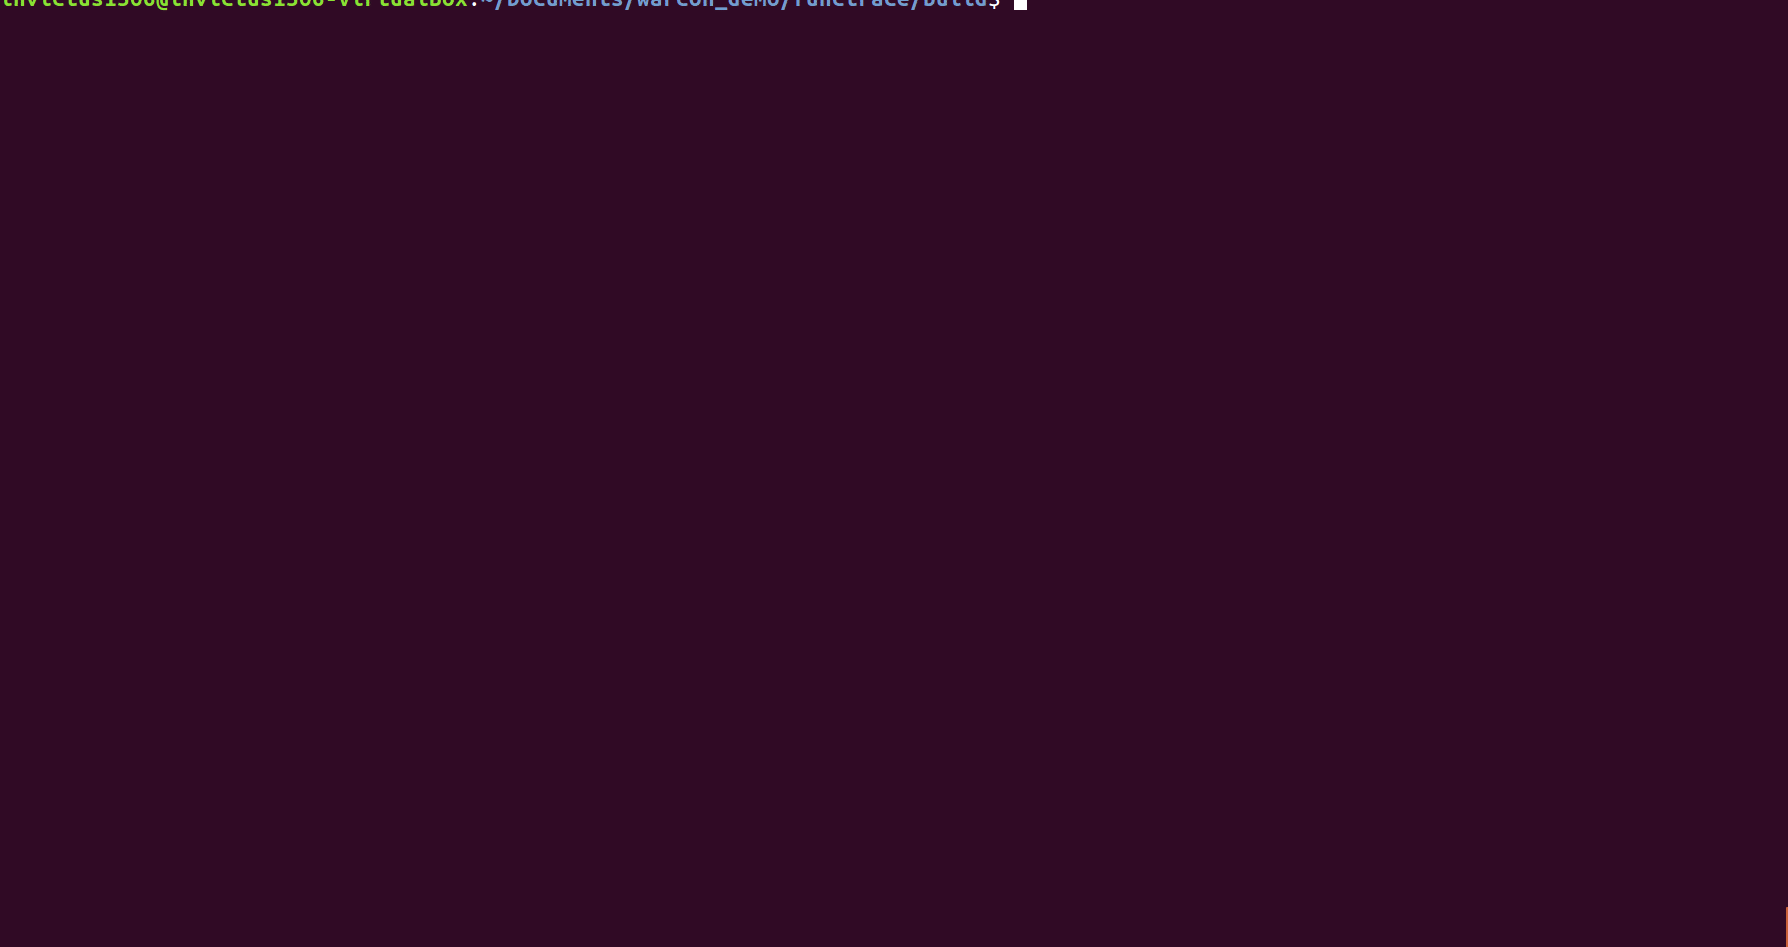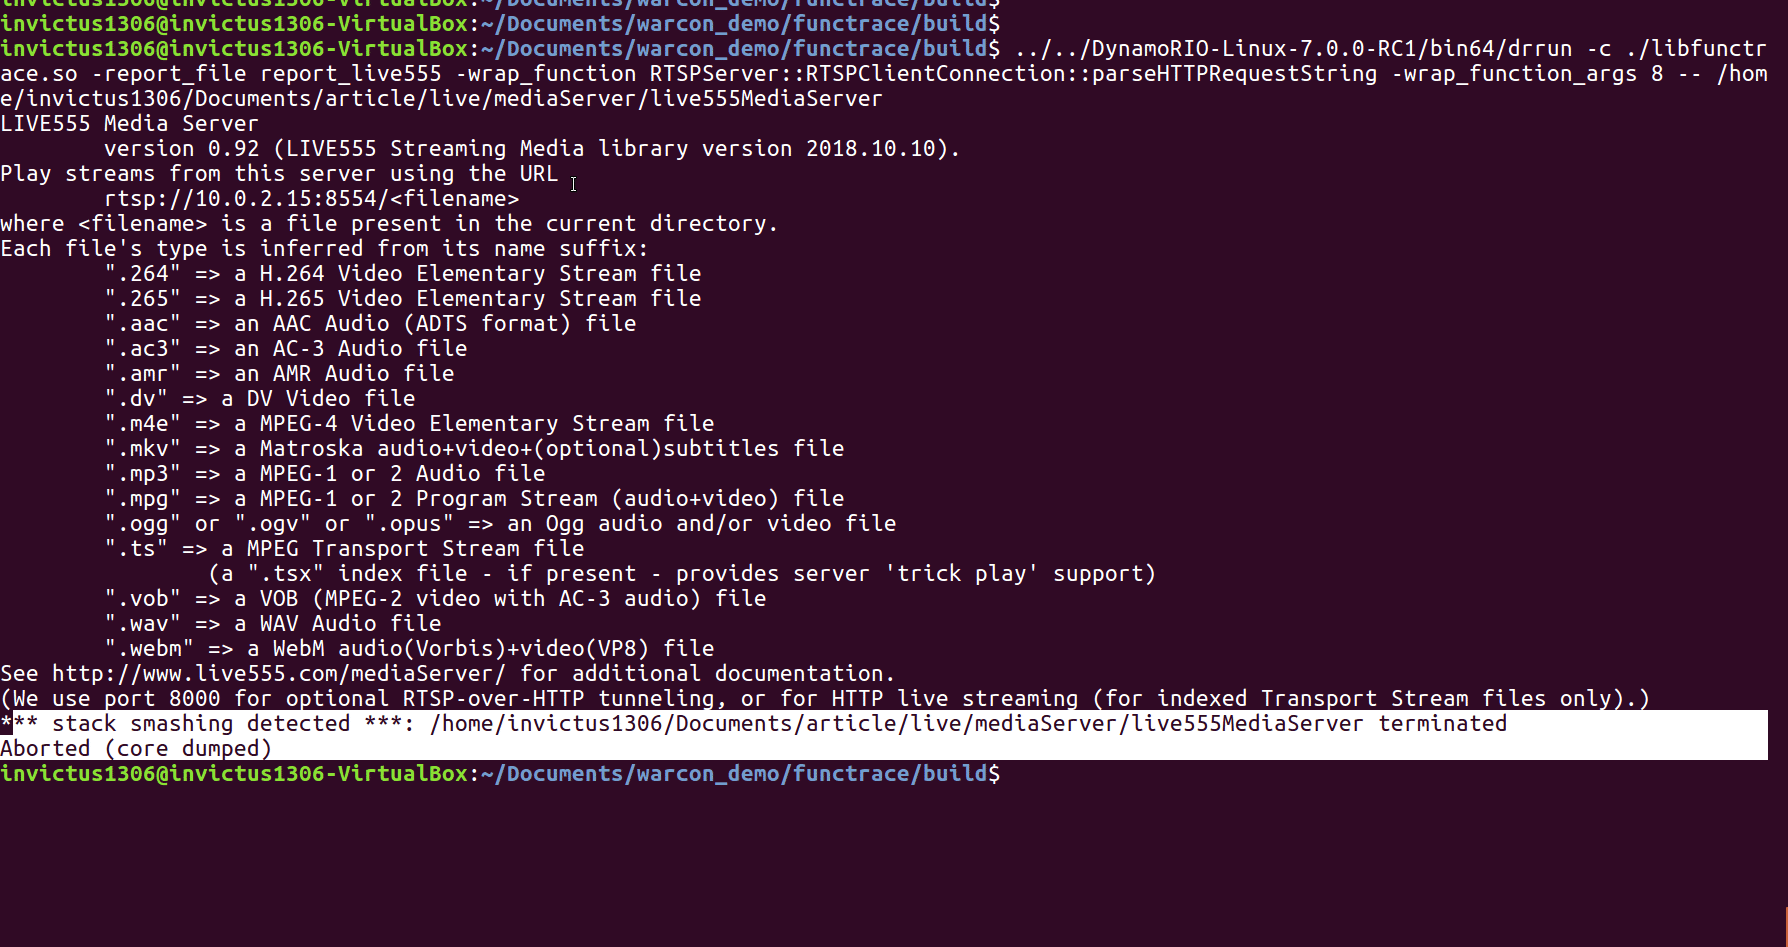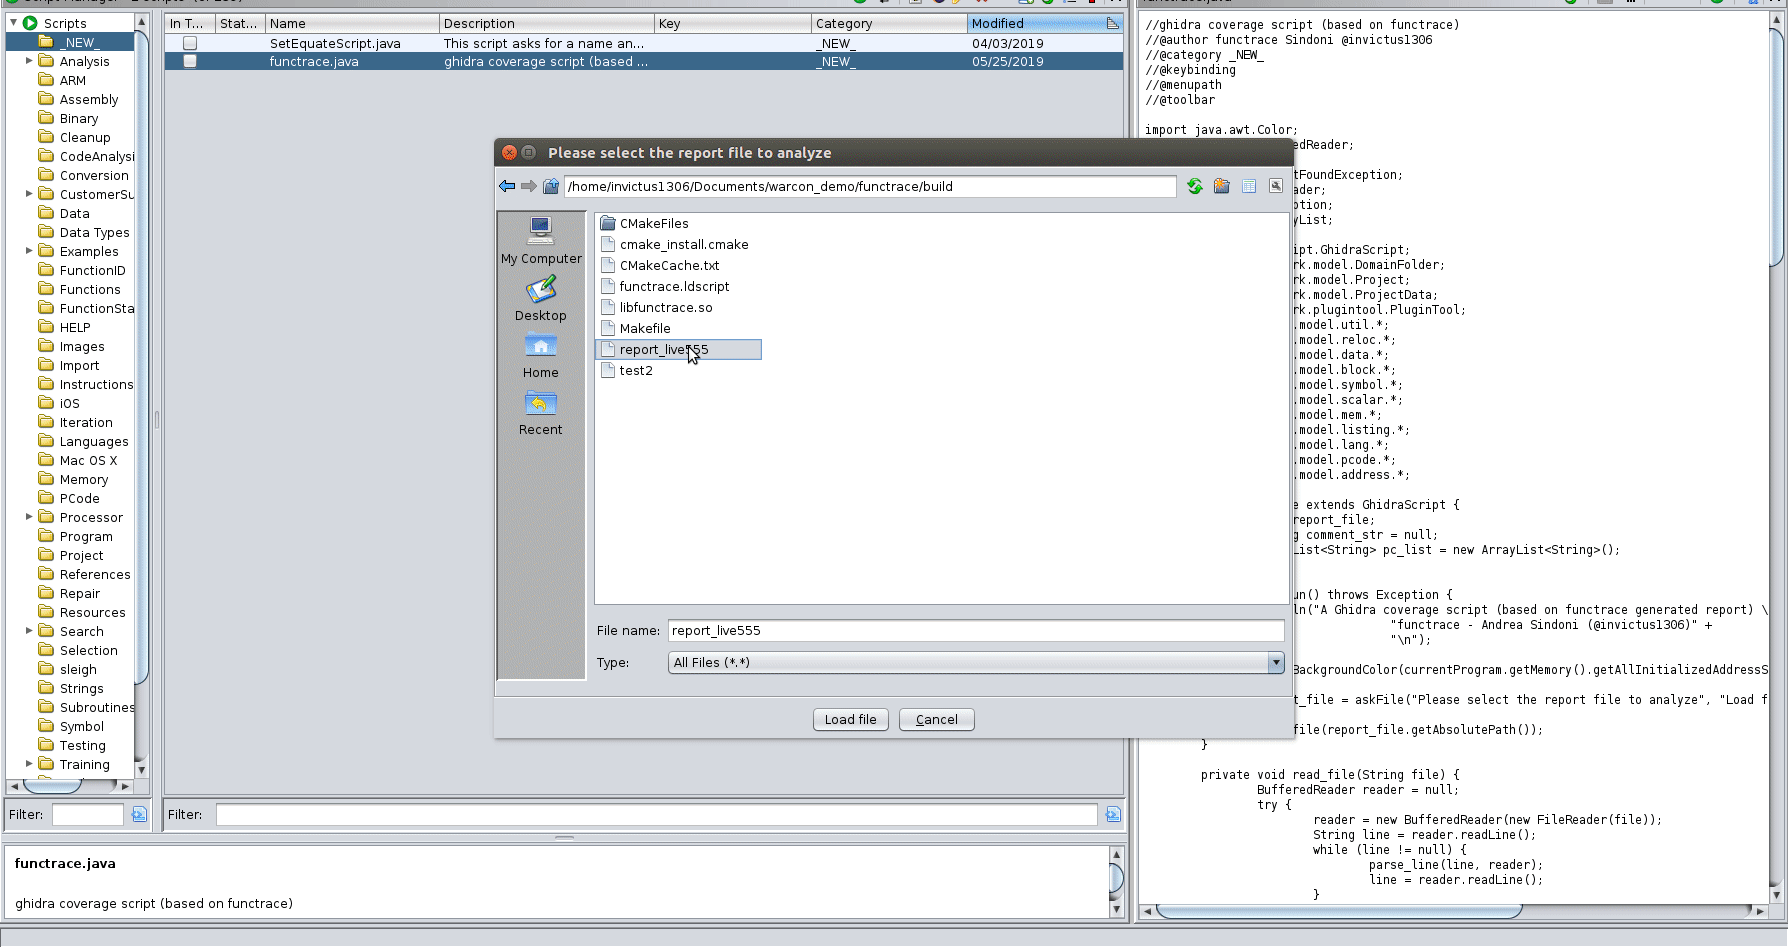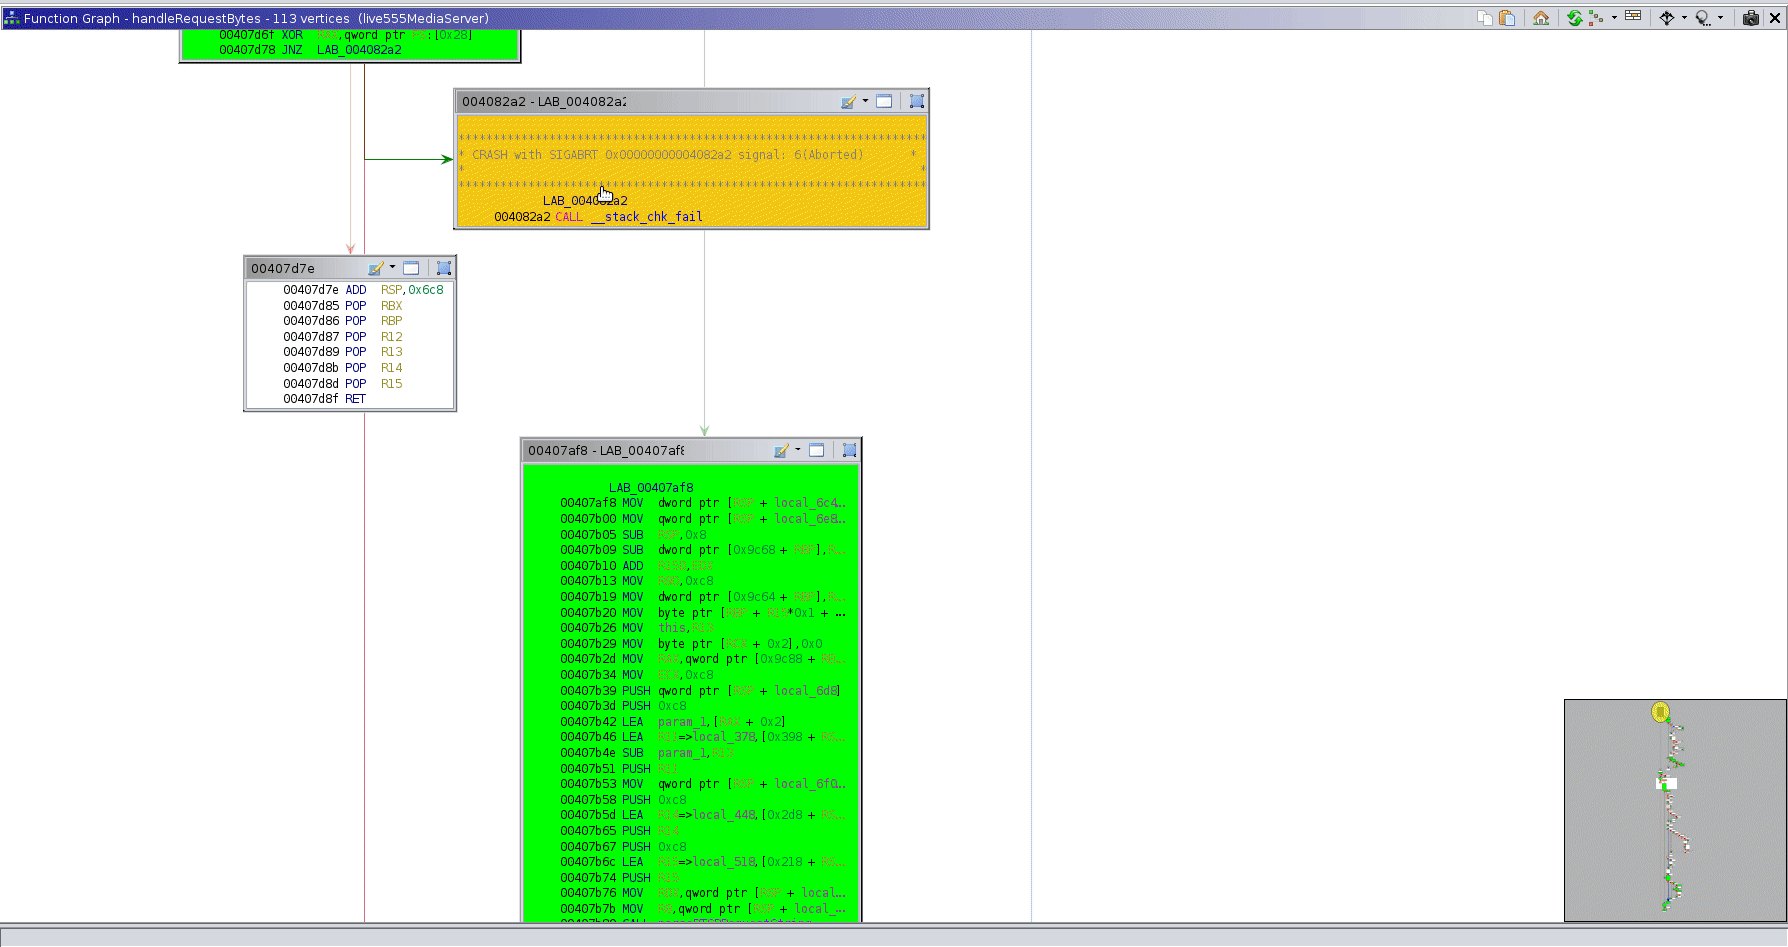 invictus1306/functrace
A function tracer
 nccgroup/datajackproxy
Datajack Proxy allows you to intercept TLS traffic in native x86 applications across platforms
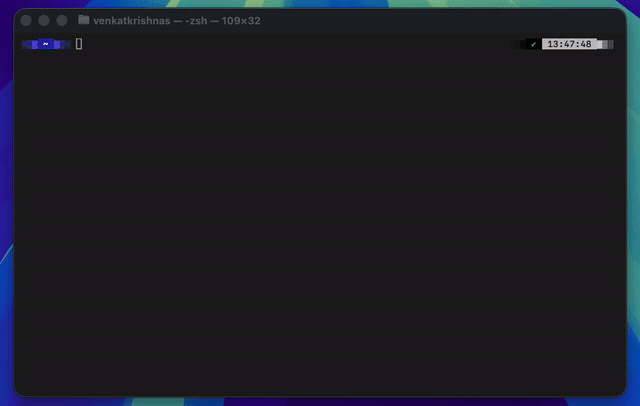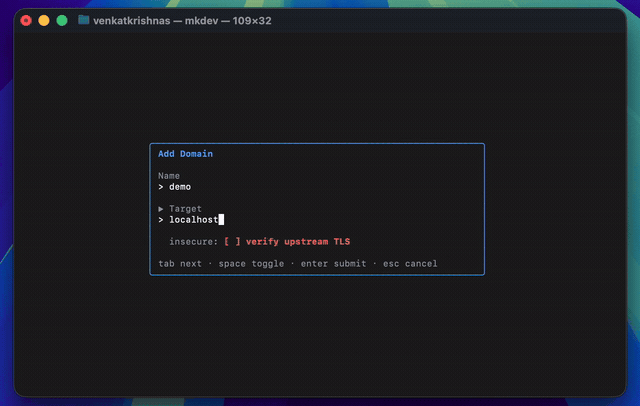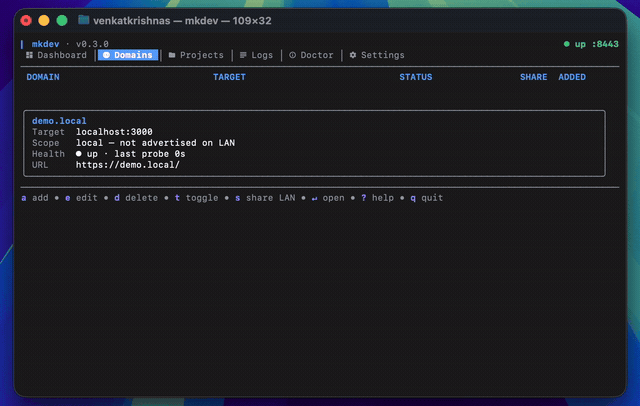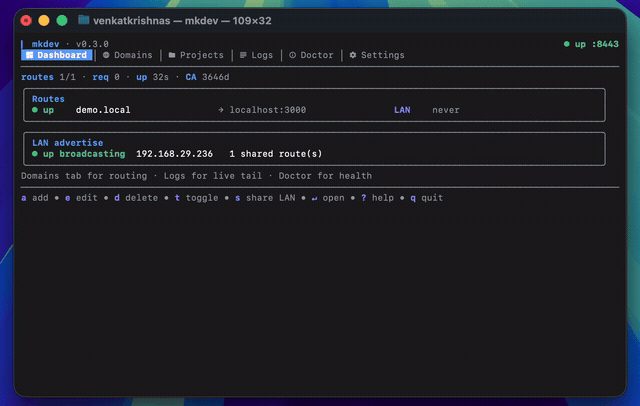 venkatkrishna07/mkdev
Trusted localhost HTTPS — local CA, /etc/hosts, mDNS LAN sharing, reverse proxy. Maps https://name.local → localhost:port
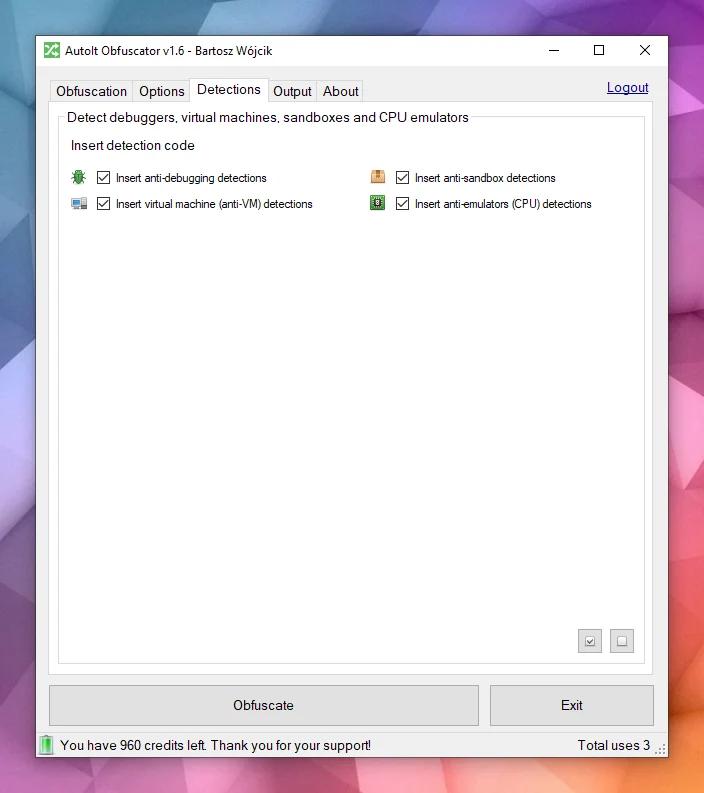 pelock/autoit-obfuscator
Obfuscates AutoIt scripts to protect source code from analysis, reverse engineering, and decompilation using advanced obfuscation and polymorphic…
 bishopfox/sonicrack
Decrypt encrypted SonicOSX firmware images
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 dodo-sec/kpot-string-decrypter
IDA python scripts to decrypt strings from KPOT and set those as comments