
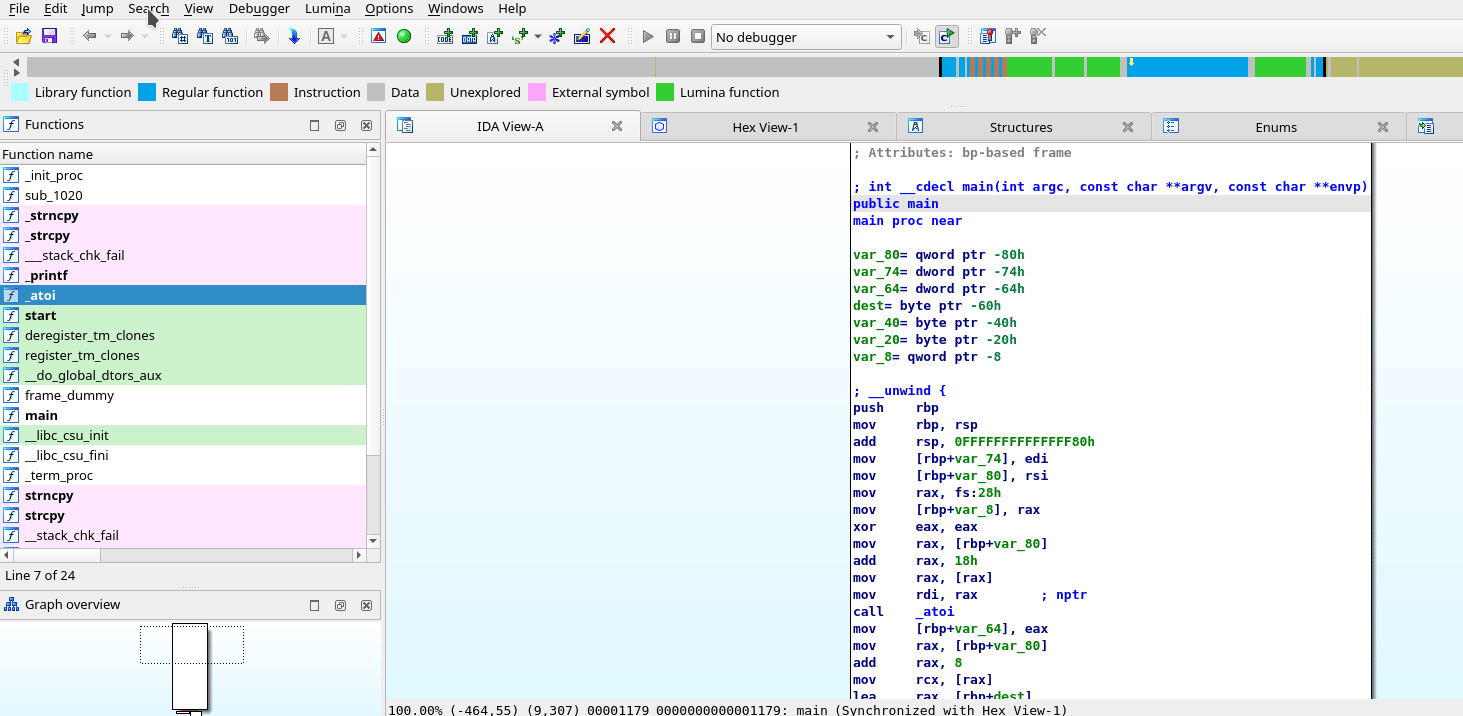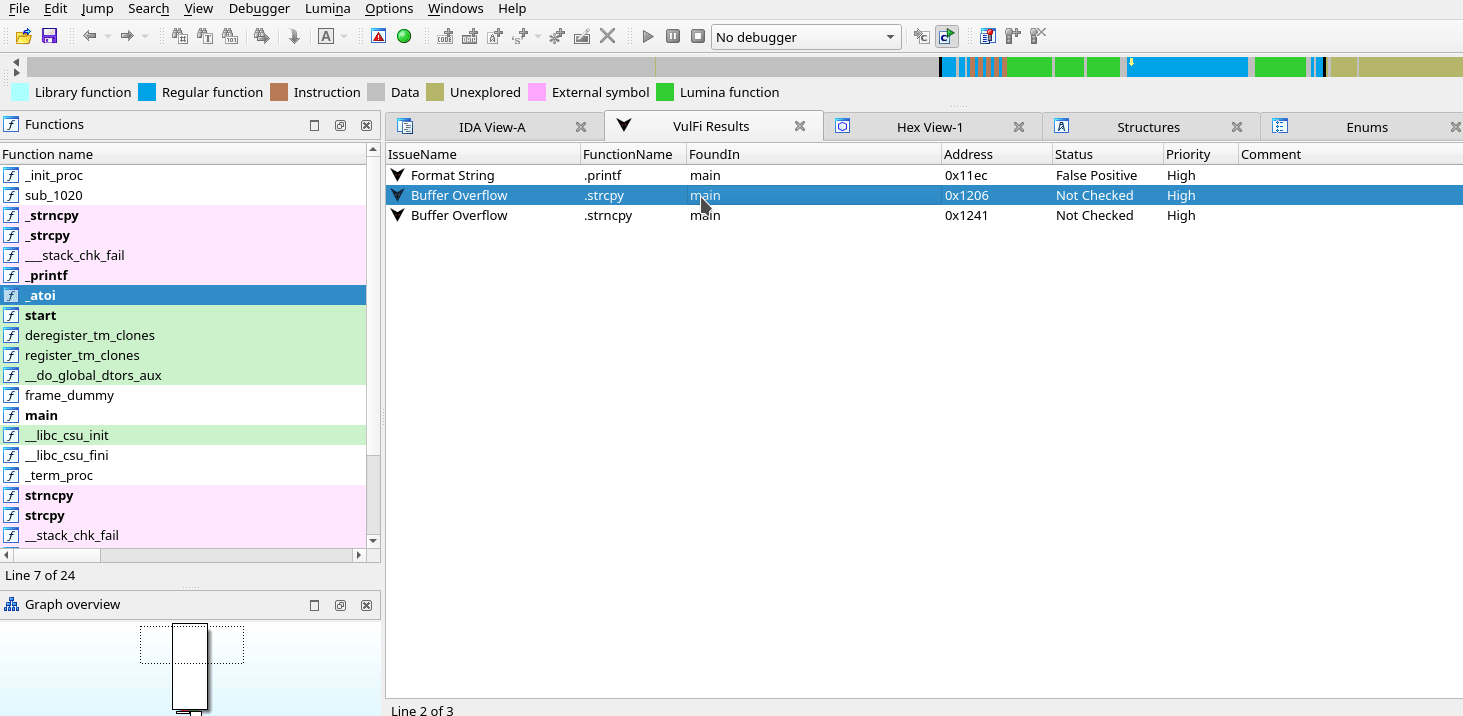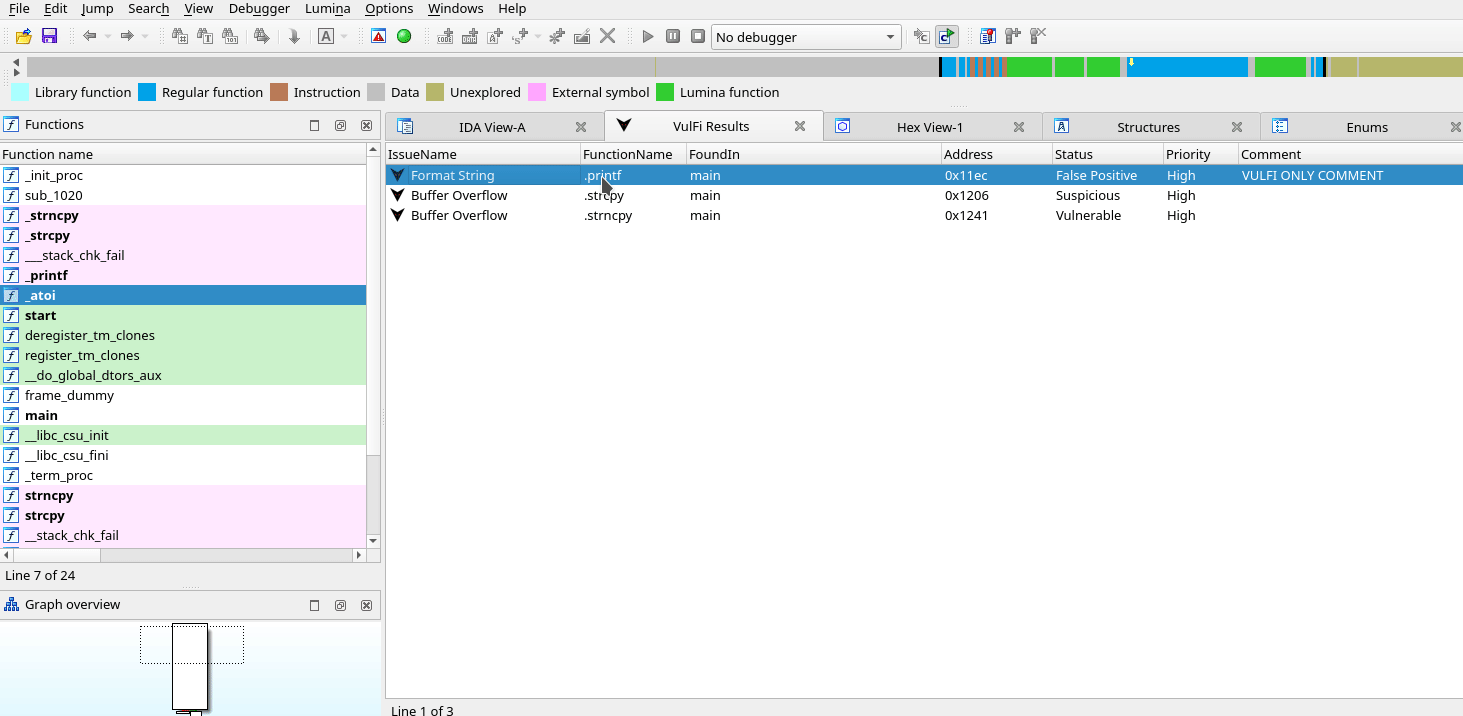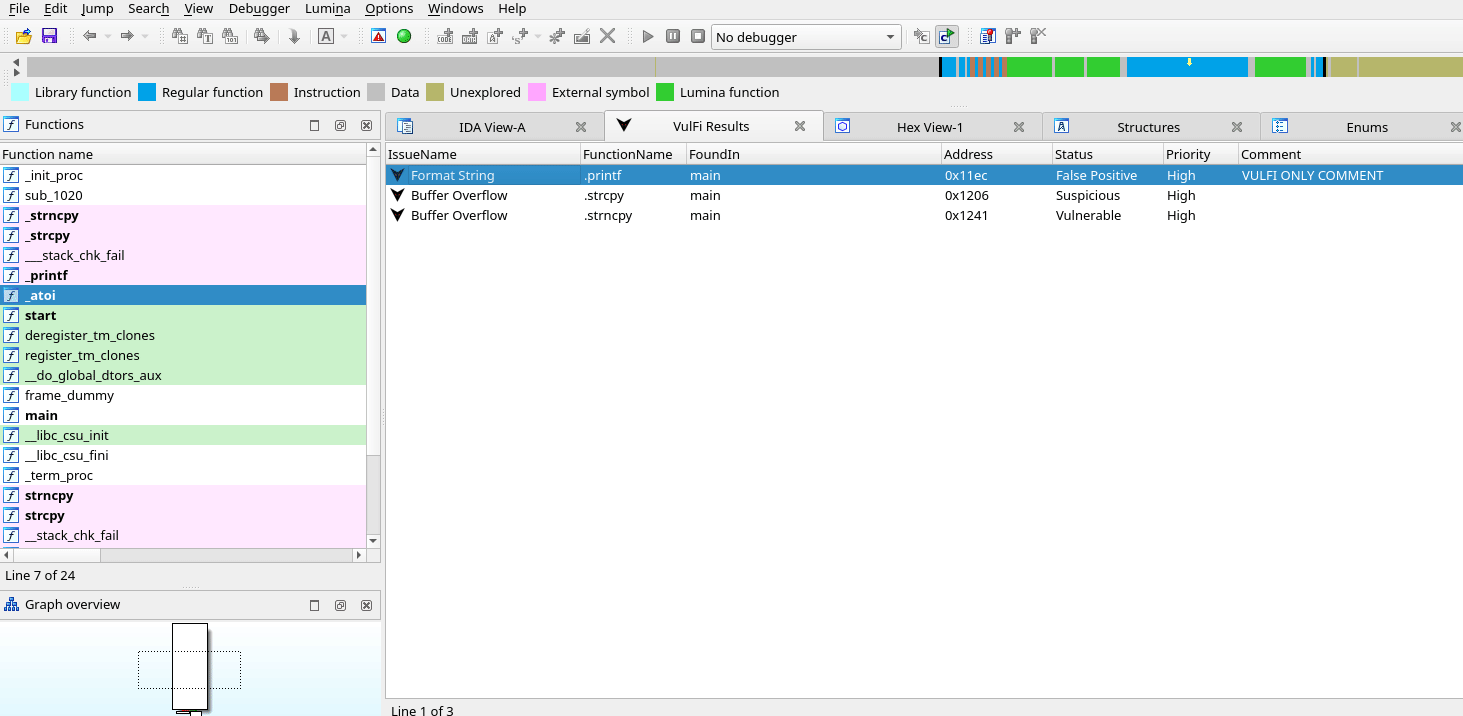
VulFi
 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
binary-analysisreverse-engineeringstatic-analysis+1
6701 year ago
accenture/vulfiIDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
 oalabs/blobrunner
Quickly debug shellcode extracted during malware analysis
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
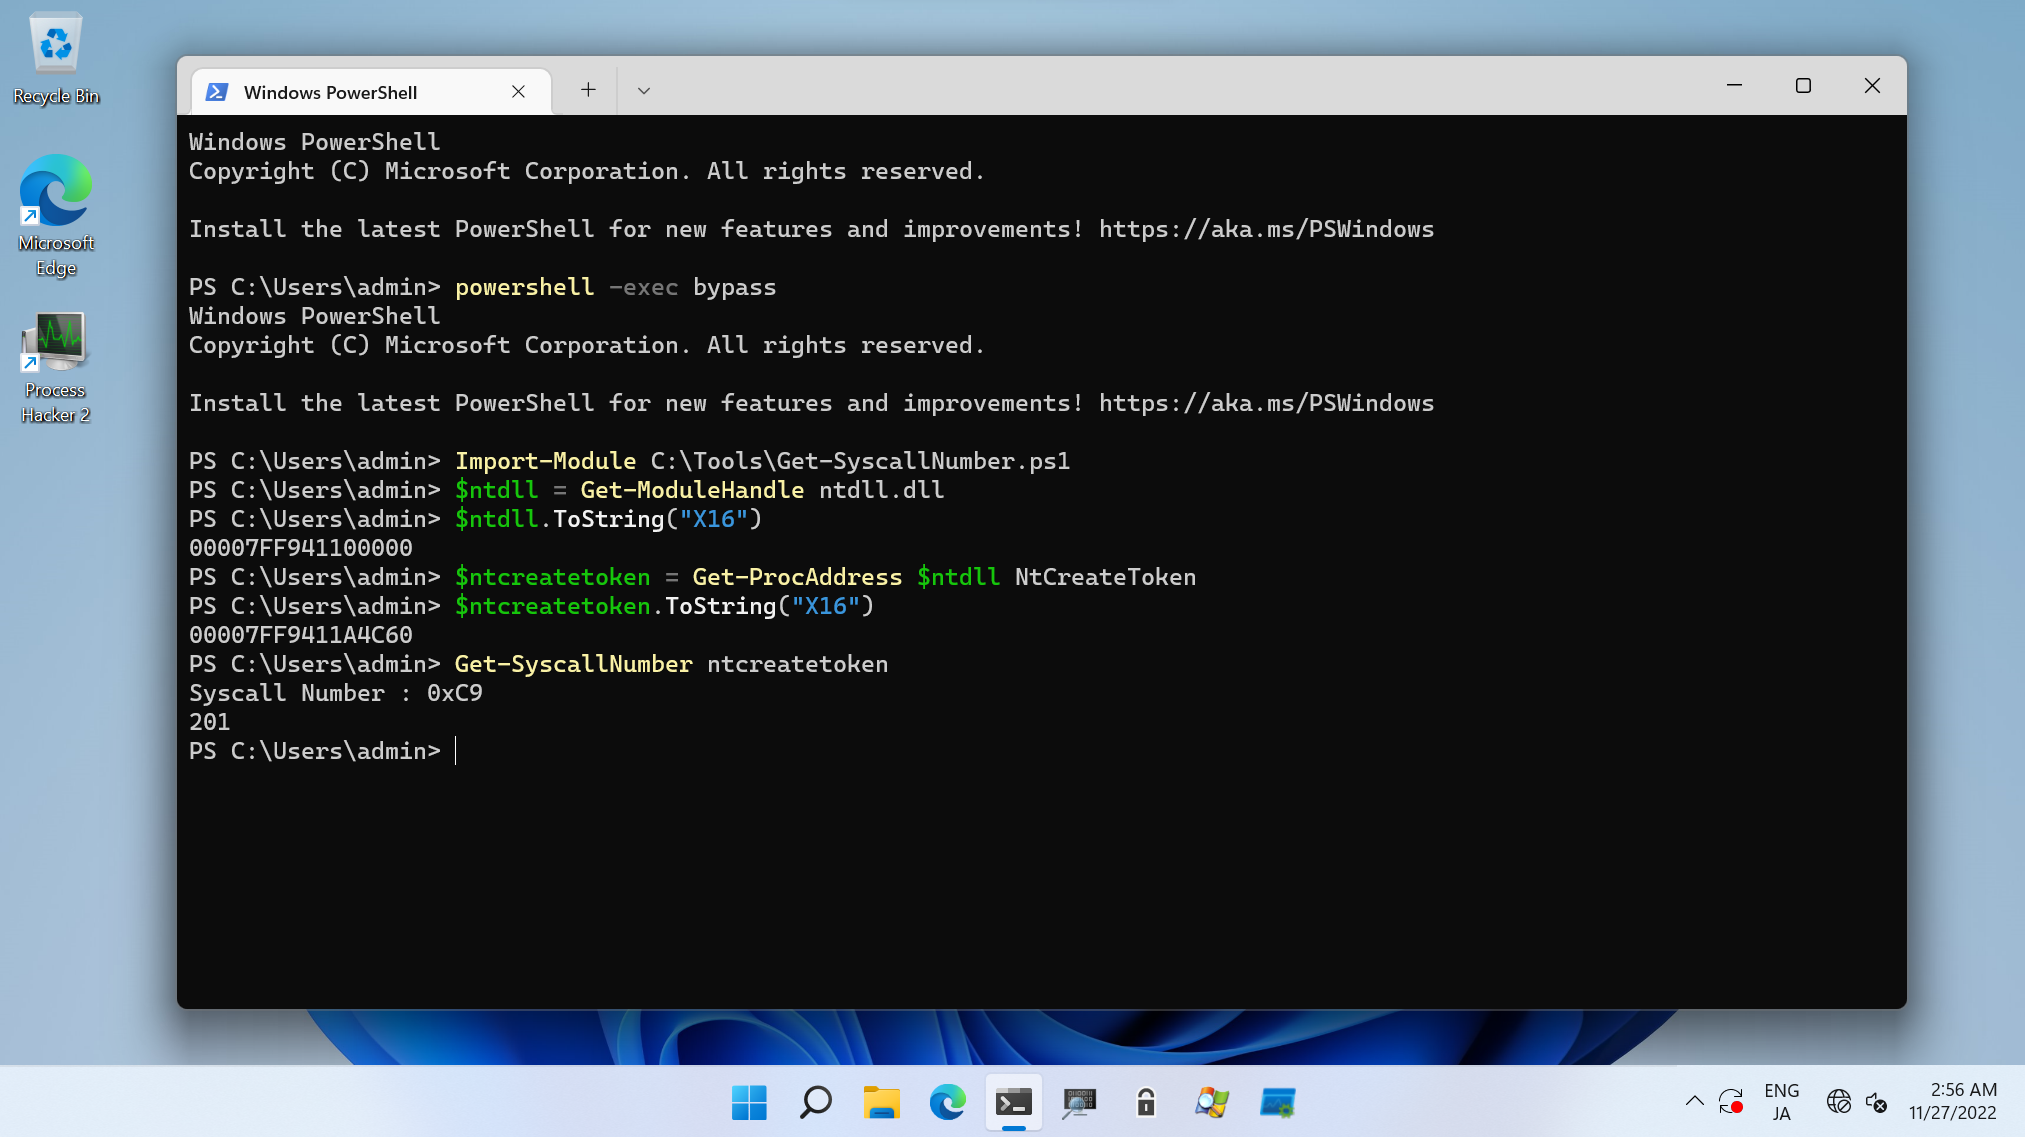 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 malwarecantfly/vba2graph
Vba2Graph - Generate call graphs from VBA code, for easier analysis of malicious documents.
 secrary/infectpe
InfectPE - Inject custom code into PE file [This project is not maintained anymore]
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
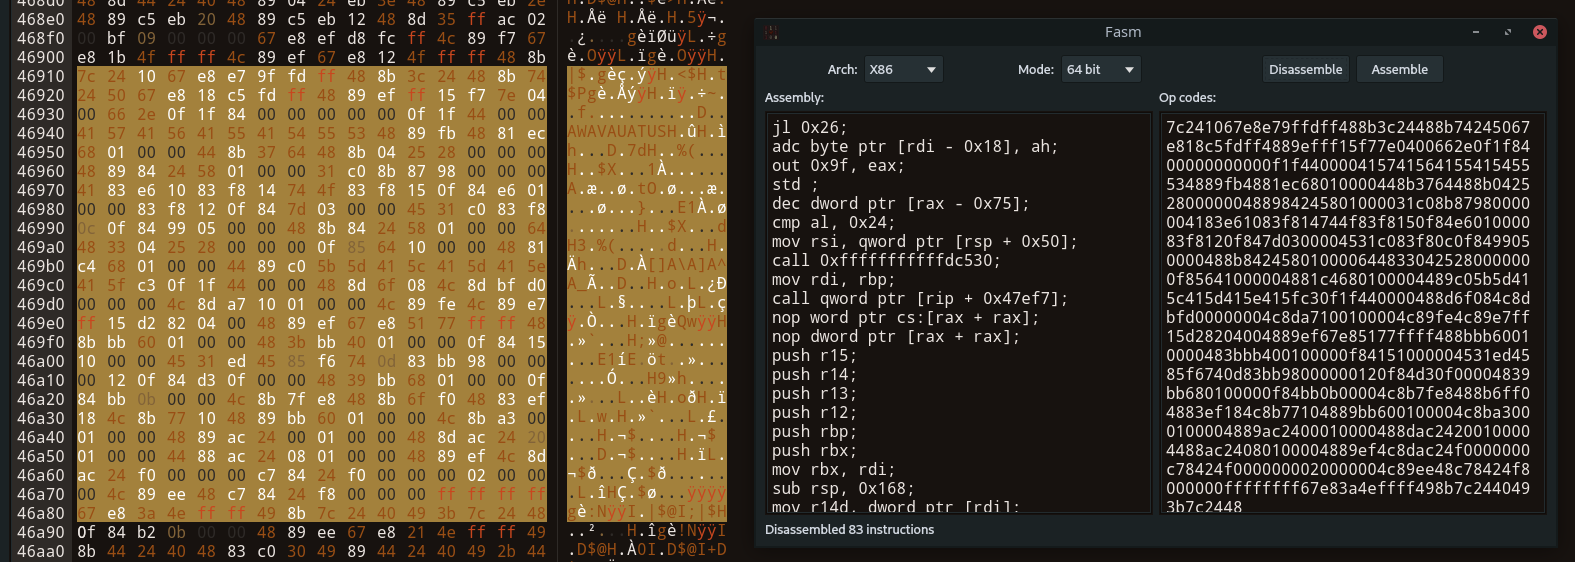 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 reverseclabs/gwtmap
Maps attack surface of GWT applications by extracting obfuscated RPC endpoints and generating serialized request payloads for security testing.
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
 thelicato/secbutler
The perfect butler for pentesters, bug-bounty hunters and security researchers
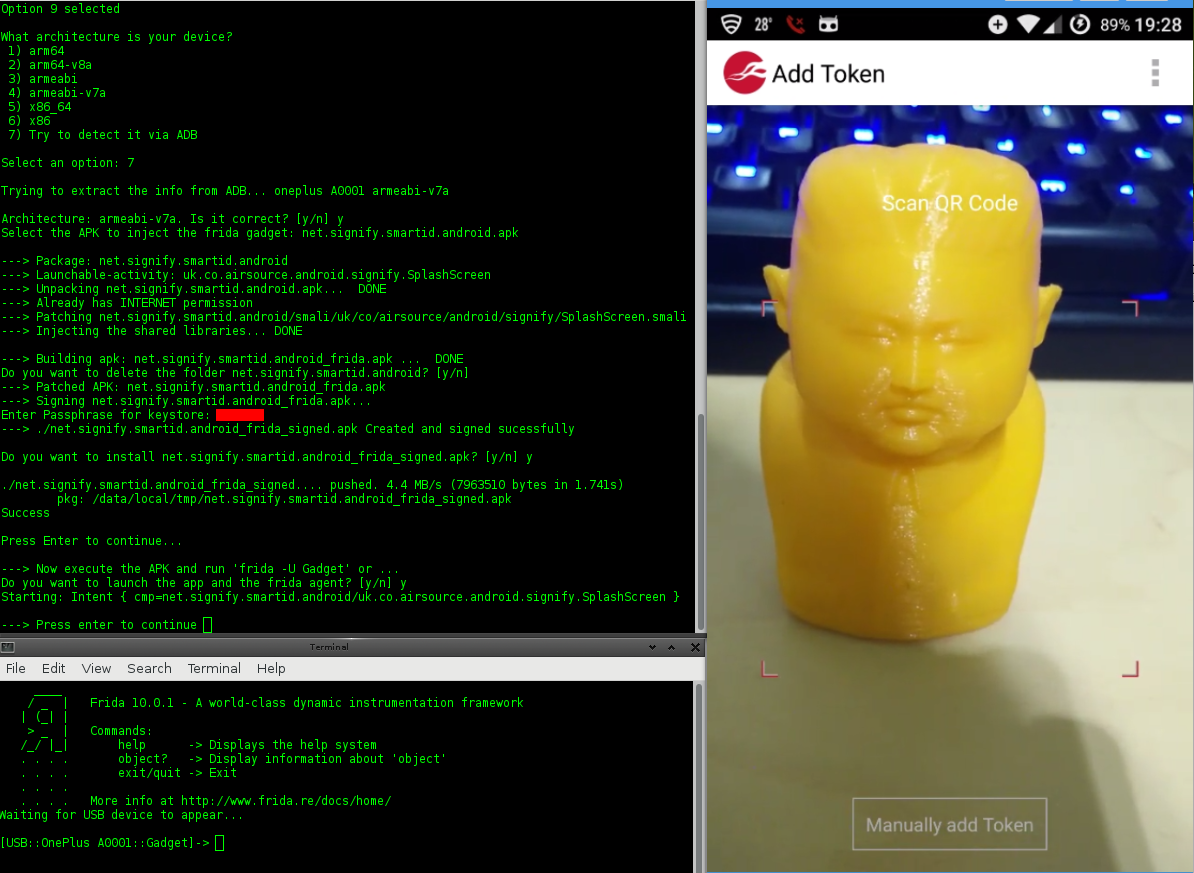 nccgroup/lazydroid
bash script to facilitate some aspects of an Android application assessment