

NTDLL-reconstruction
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
binary-exploitationdefensive-toolsids-ips-evasion+6
33
sk4r4b/ntdll-reconstructionA technique that mixes NTDLL unhooking and hellsgate gate varients
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
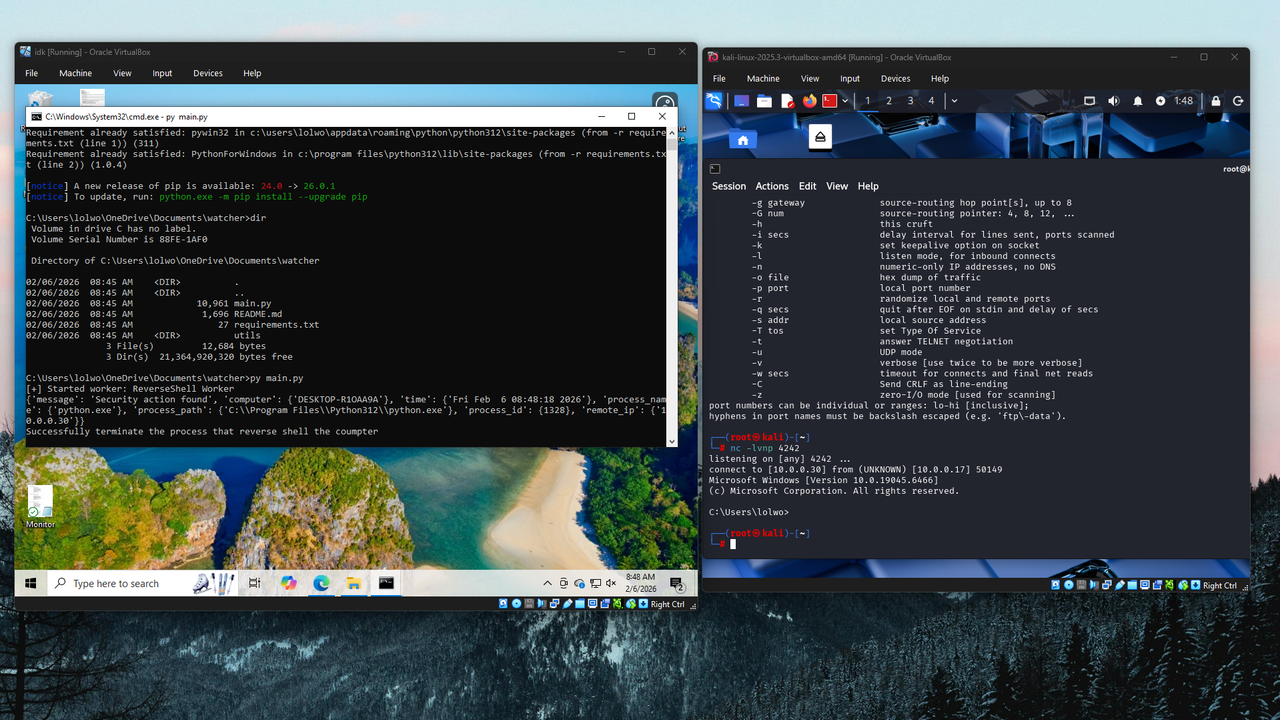 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
 kiexitdispatcher/godefender
Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
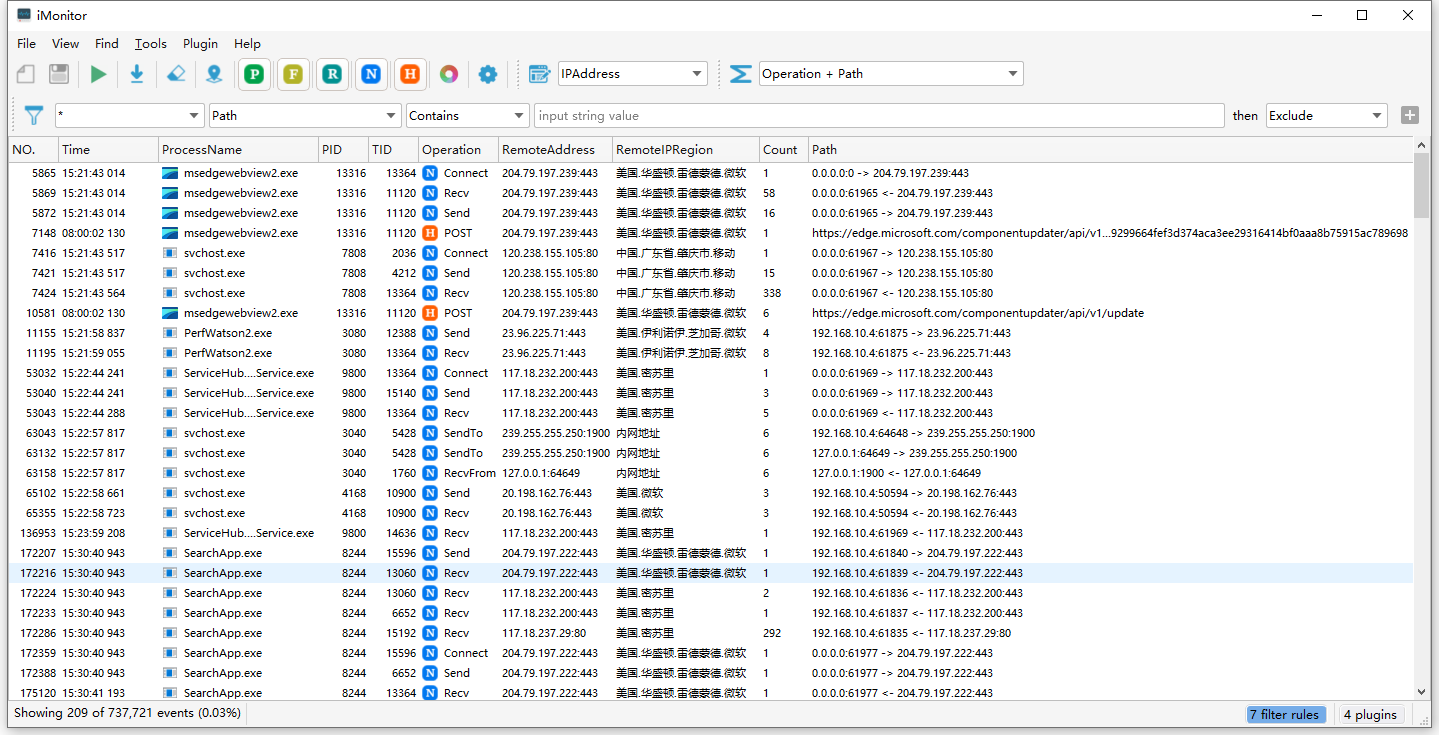 wecooperate/imonitor
Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
 calligraf0/cve-2024-0311
Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
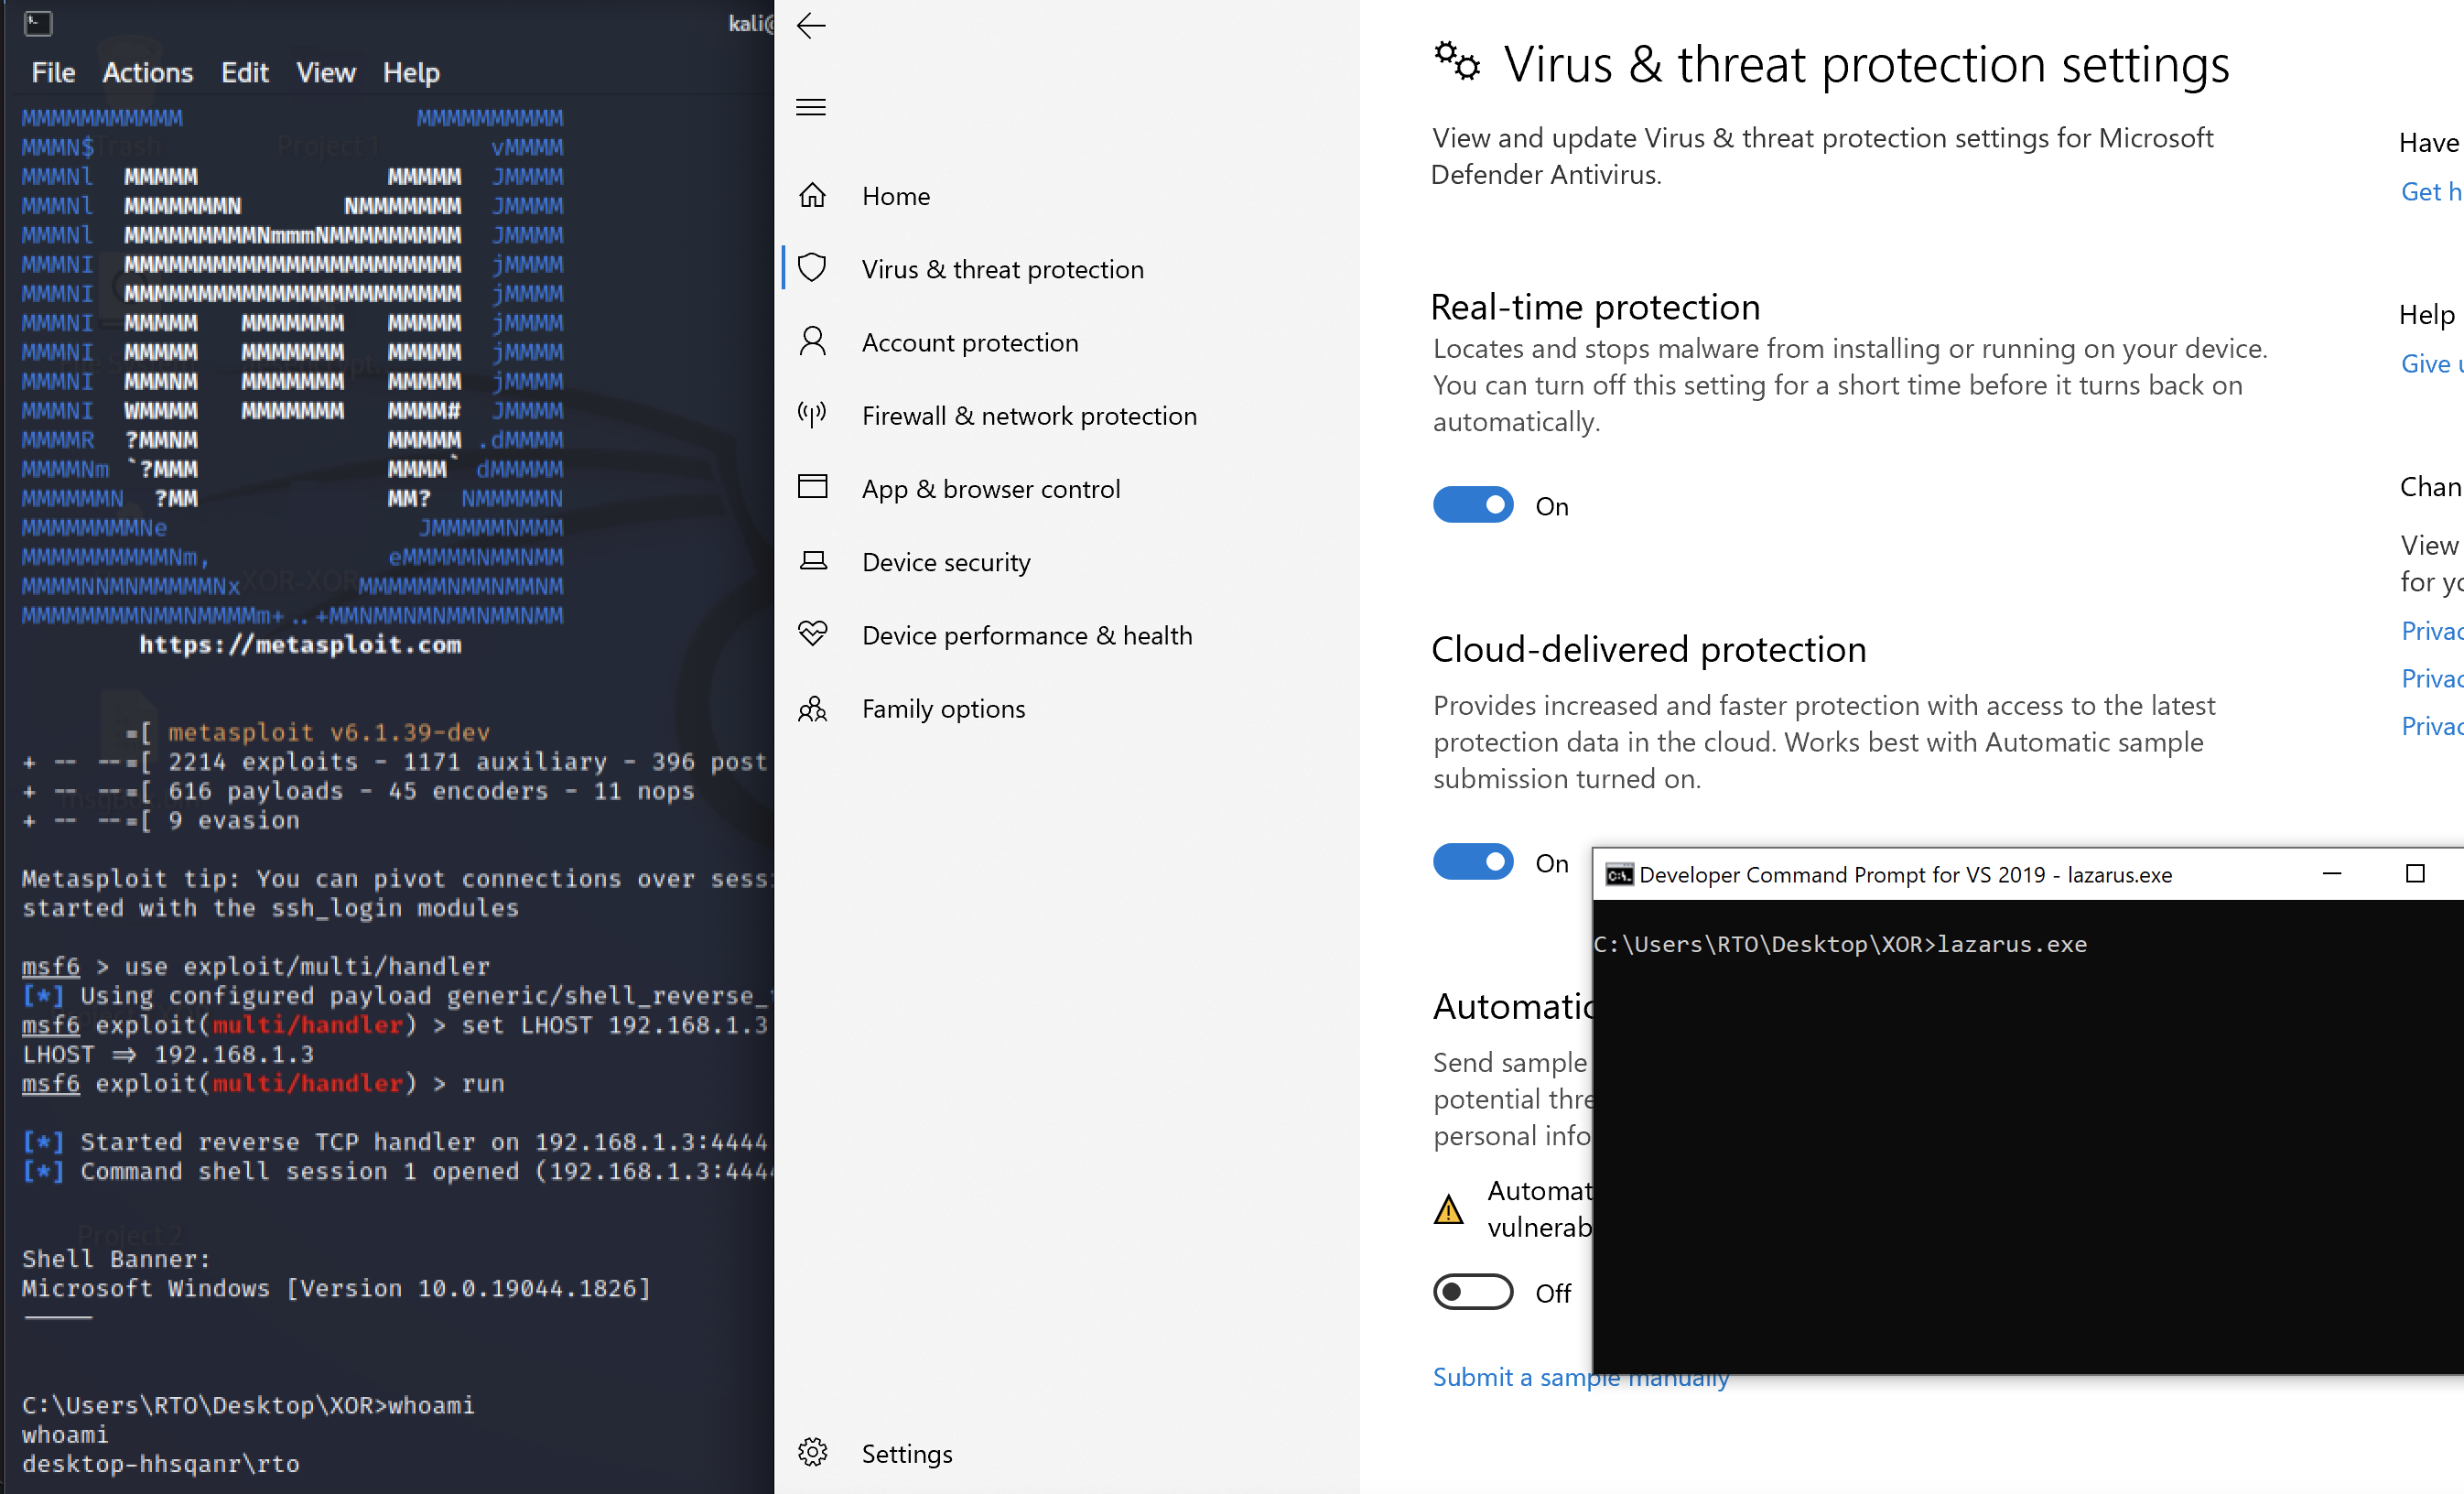 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 gmh5225/no-access-protection-x86
It encrypts the text section and set the protection to NO_ACCESS.
 synacktiv/amsi-bypass
Lists of AMSI triggers (VBA, JScript / VBScript)
 cylancevulnresearch/reflectivedllrefresher
Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone