
unblob
 onekey-sec/unblob
Extract files from any kind of container formats
binary-analysisdata-recoveryembedded-systems-security+3
onekey-sec/unblobExtract files from any kind of container formats
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
 libriscv/libloong
The fastest LoongArch sandbox
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
 aeromodes/8cryptdo
Reverse-engineered docs and tools for 8BitDo firmware encryption
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 d6fault/cve-2026-95675
Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.
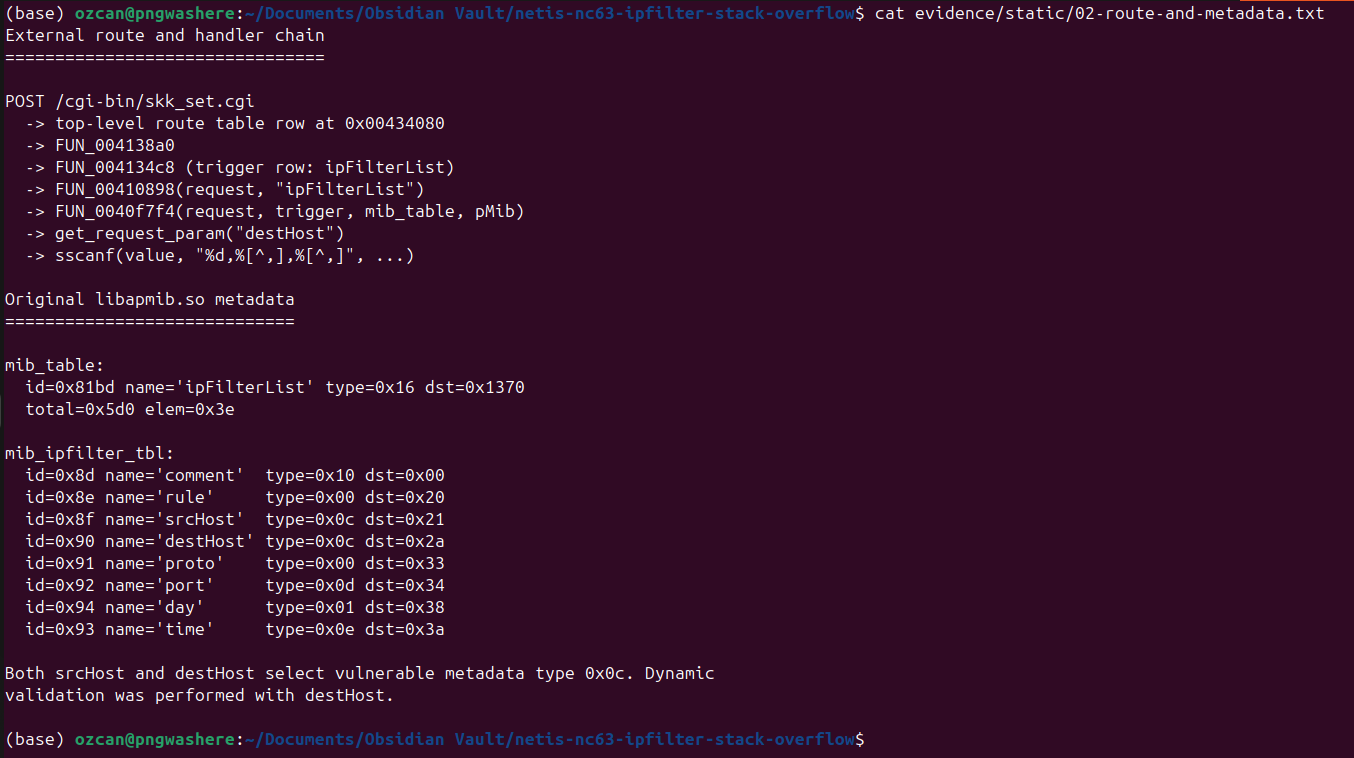 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
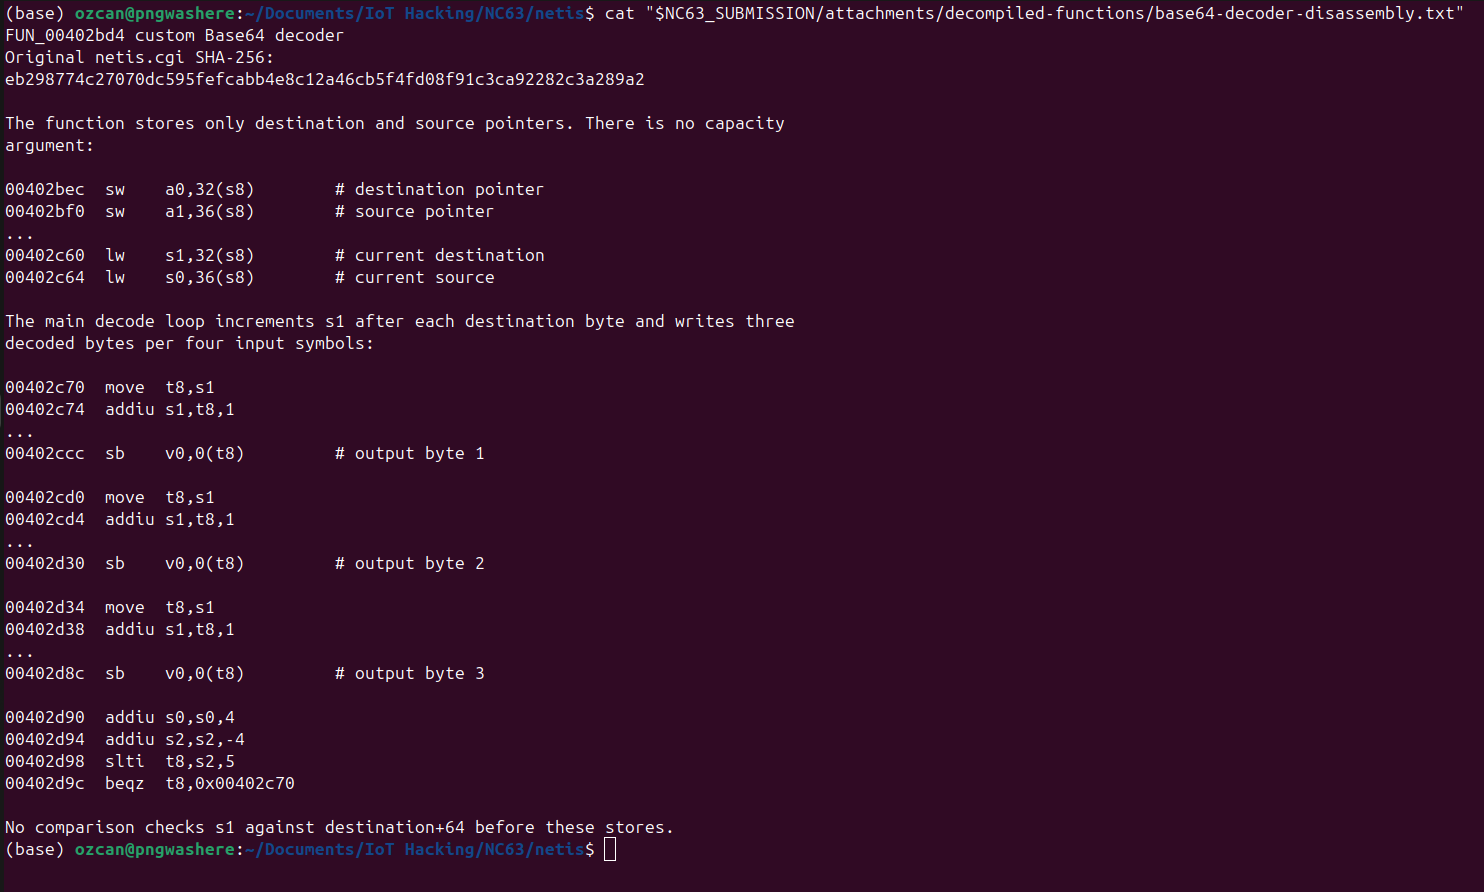 ozcanpng/cve-2026-76070
Original research and PoC for a pre-auth Base64-decoded password stack buffer overflow in Netis NC63 login.cgi
 peterlinccl/vulnerability-dlink-cve-2025-14659
Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…
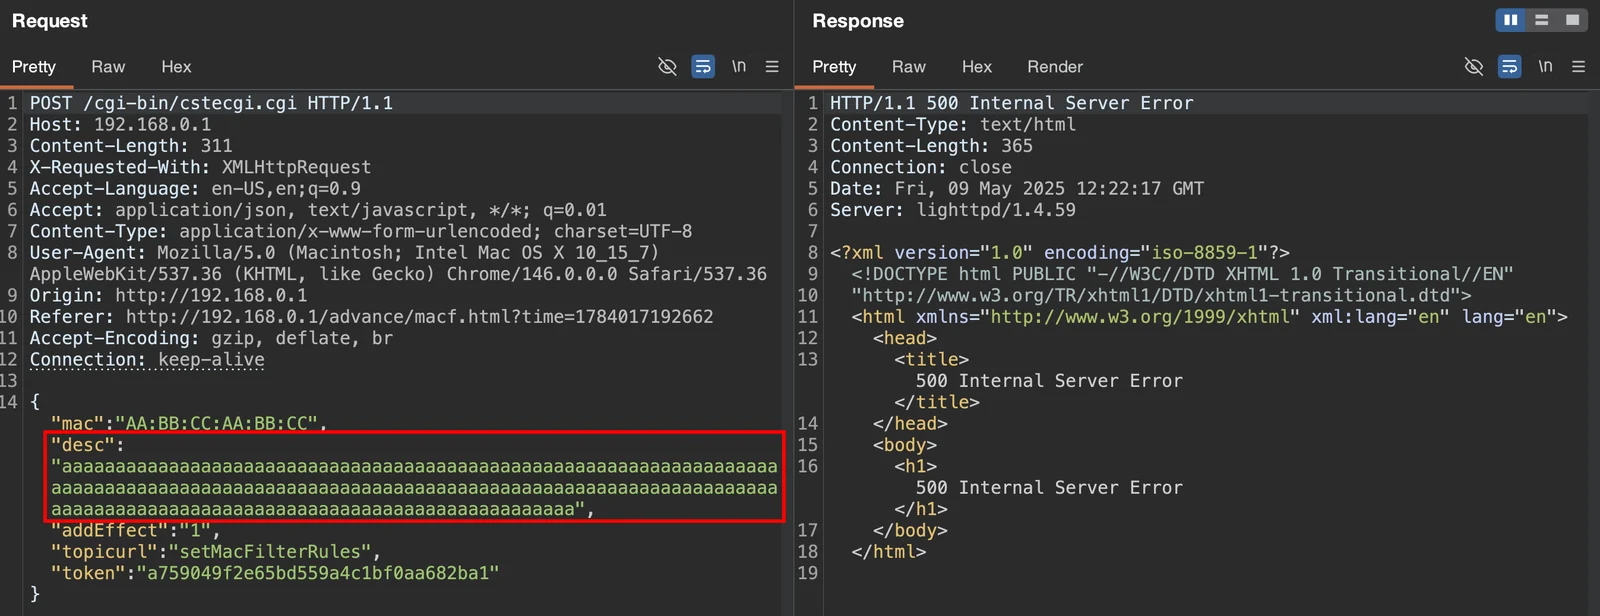 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…