

jadx
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
android-securitybinary-analysisdebuggers+5
skylot/jadxCommand-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…

 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
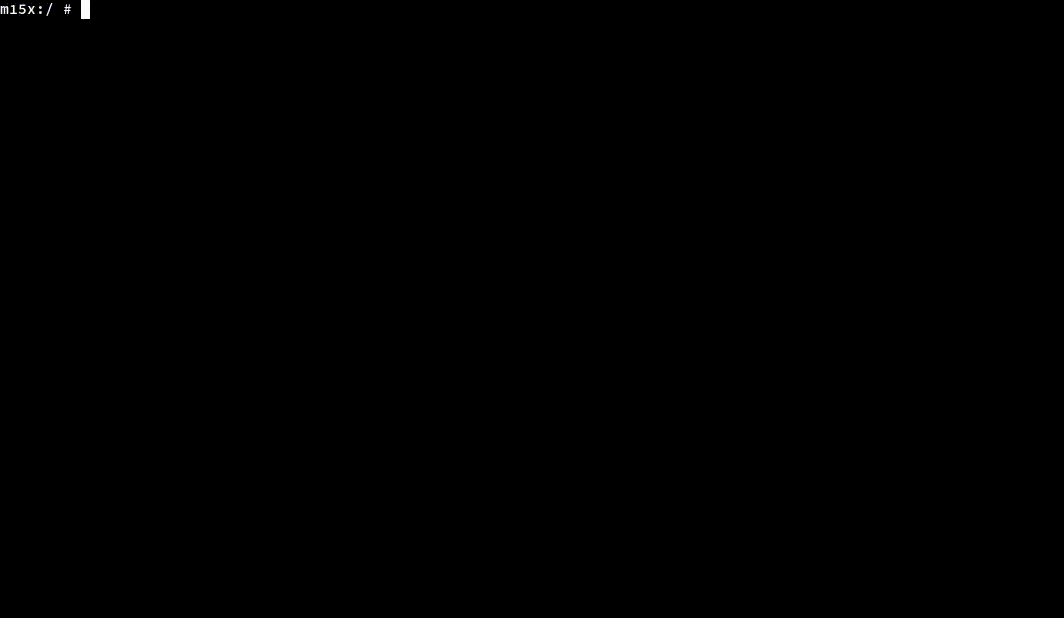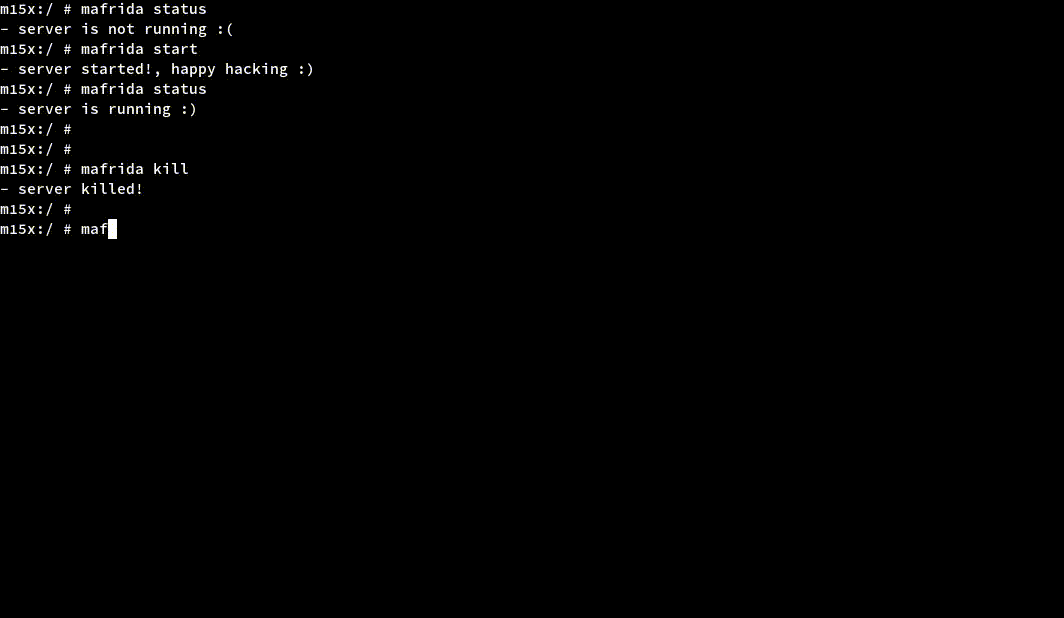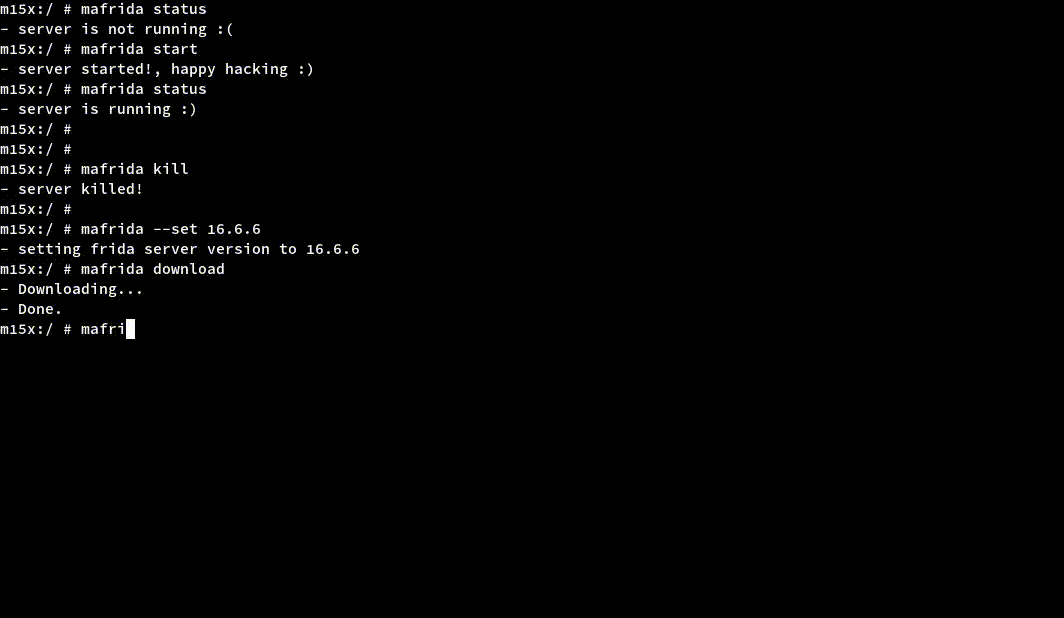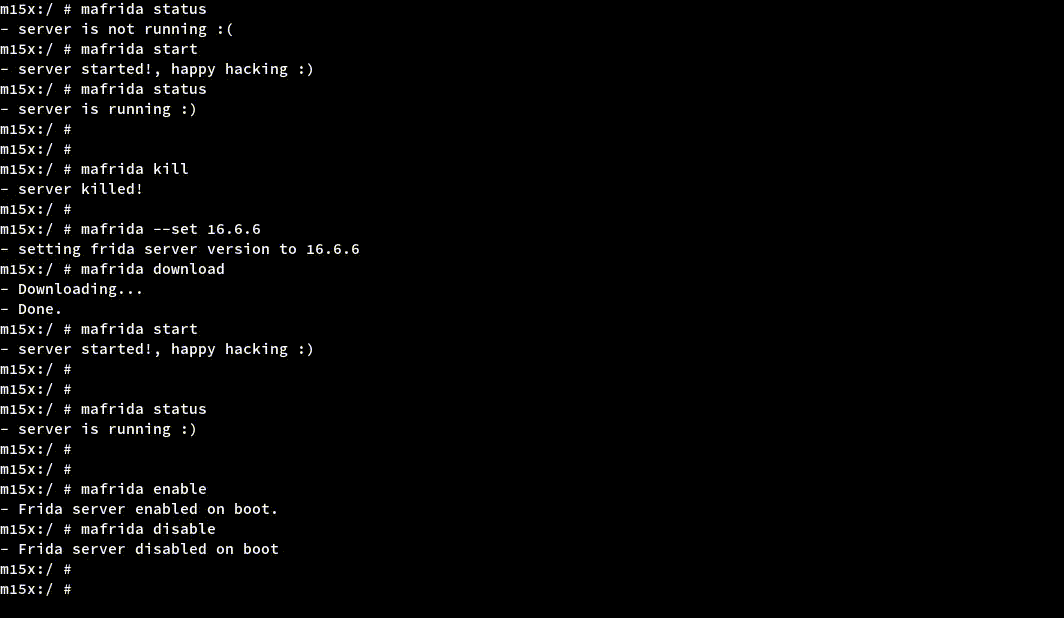 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
 netspooky/scare
A multi-arch assembly REPL and emulator for your command line.
 zznop/drow
Injects code into ELF executables post-build
 leandrofroes/gftrace
A command line Windows API tracing tool for Golang binaries.