

distro
 remnux/distro
Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
digital-forensicsdynamic-analysis-sandboxingforensics+5
117
remnux/distroProvides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
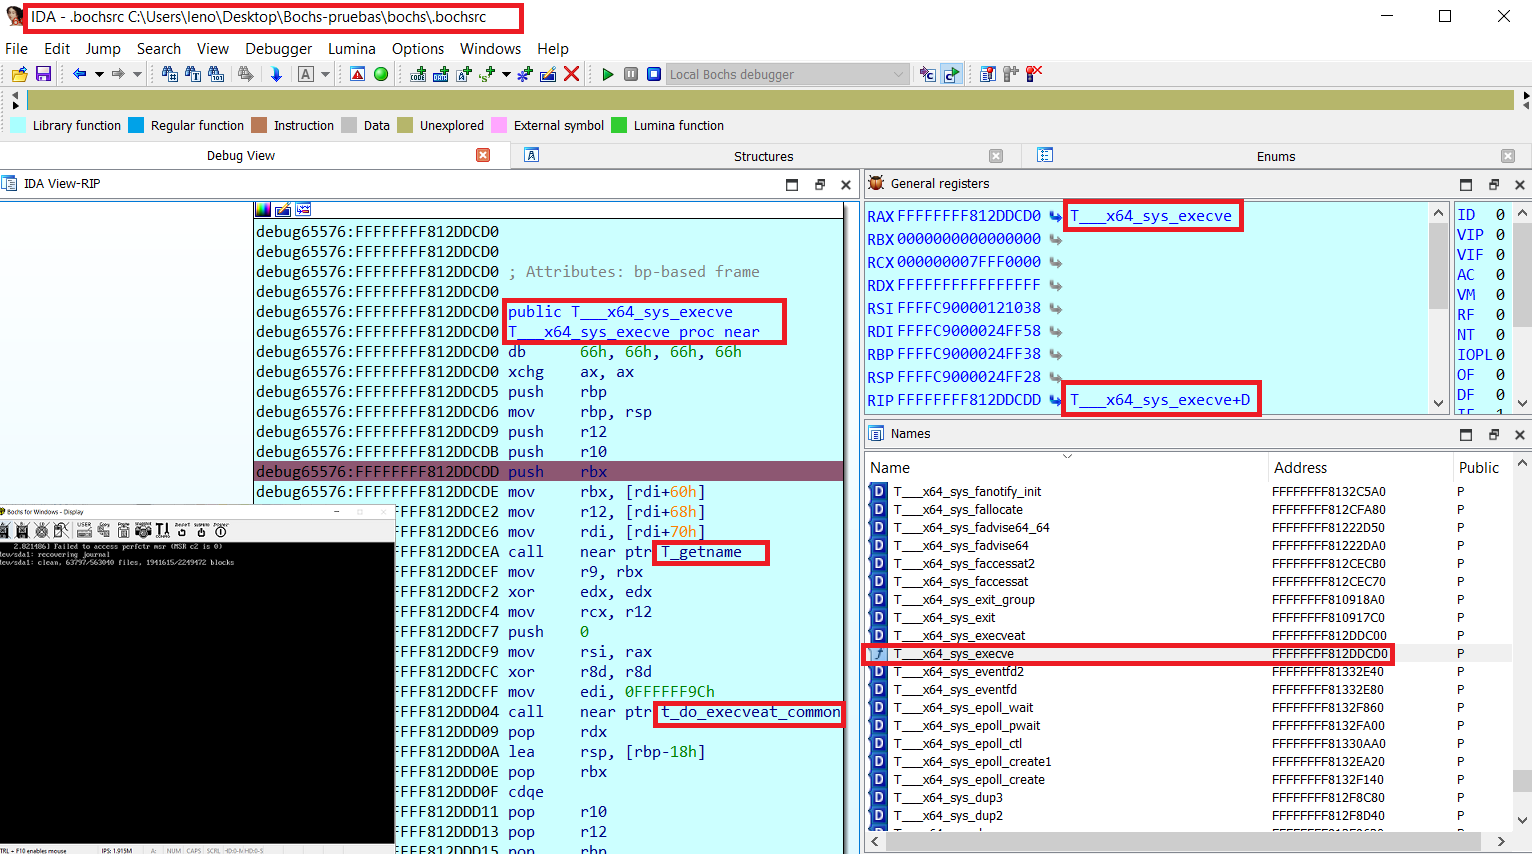 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…