ReflectiveDLLRefresher

Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.

Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.

Clean Indirect Syscalls with Syscall Tampering.

A technique that mixes NTDLL unhooking and hellsgate gate varients

Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…

Decrypt encrypted SonicOSX firmware images

Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…

BYOVD: Use 360 WFP driver to block EDR/XDR network connection.

A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…

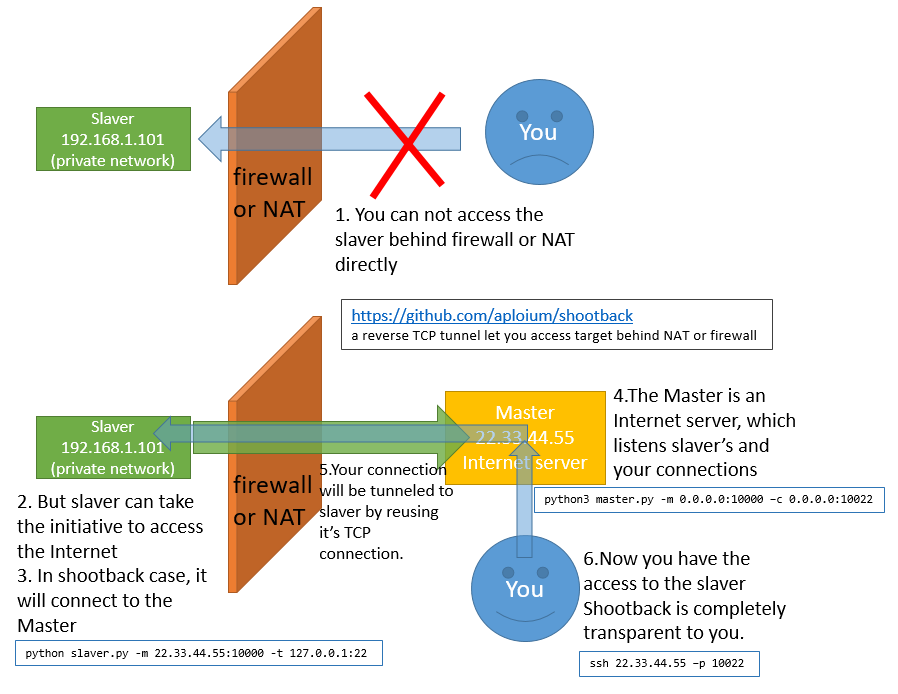
a reverse TCP tunnel let you access target behind NAT or firewall

Platform independent peCloak fork based on Capstone