

radare2-scripts
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
binary-analysisdigital-forensicsmalware-analysis+3
32
withsecurelabs/radare2-scriptsCollection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
 oalabs/hashdb
Assortment of hashing algorithms used in malware
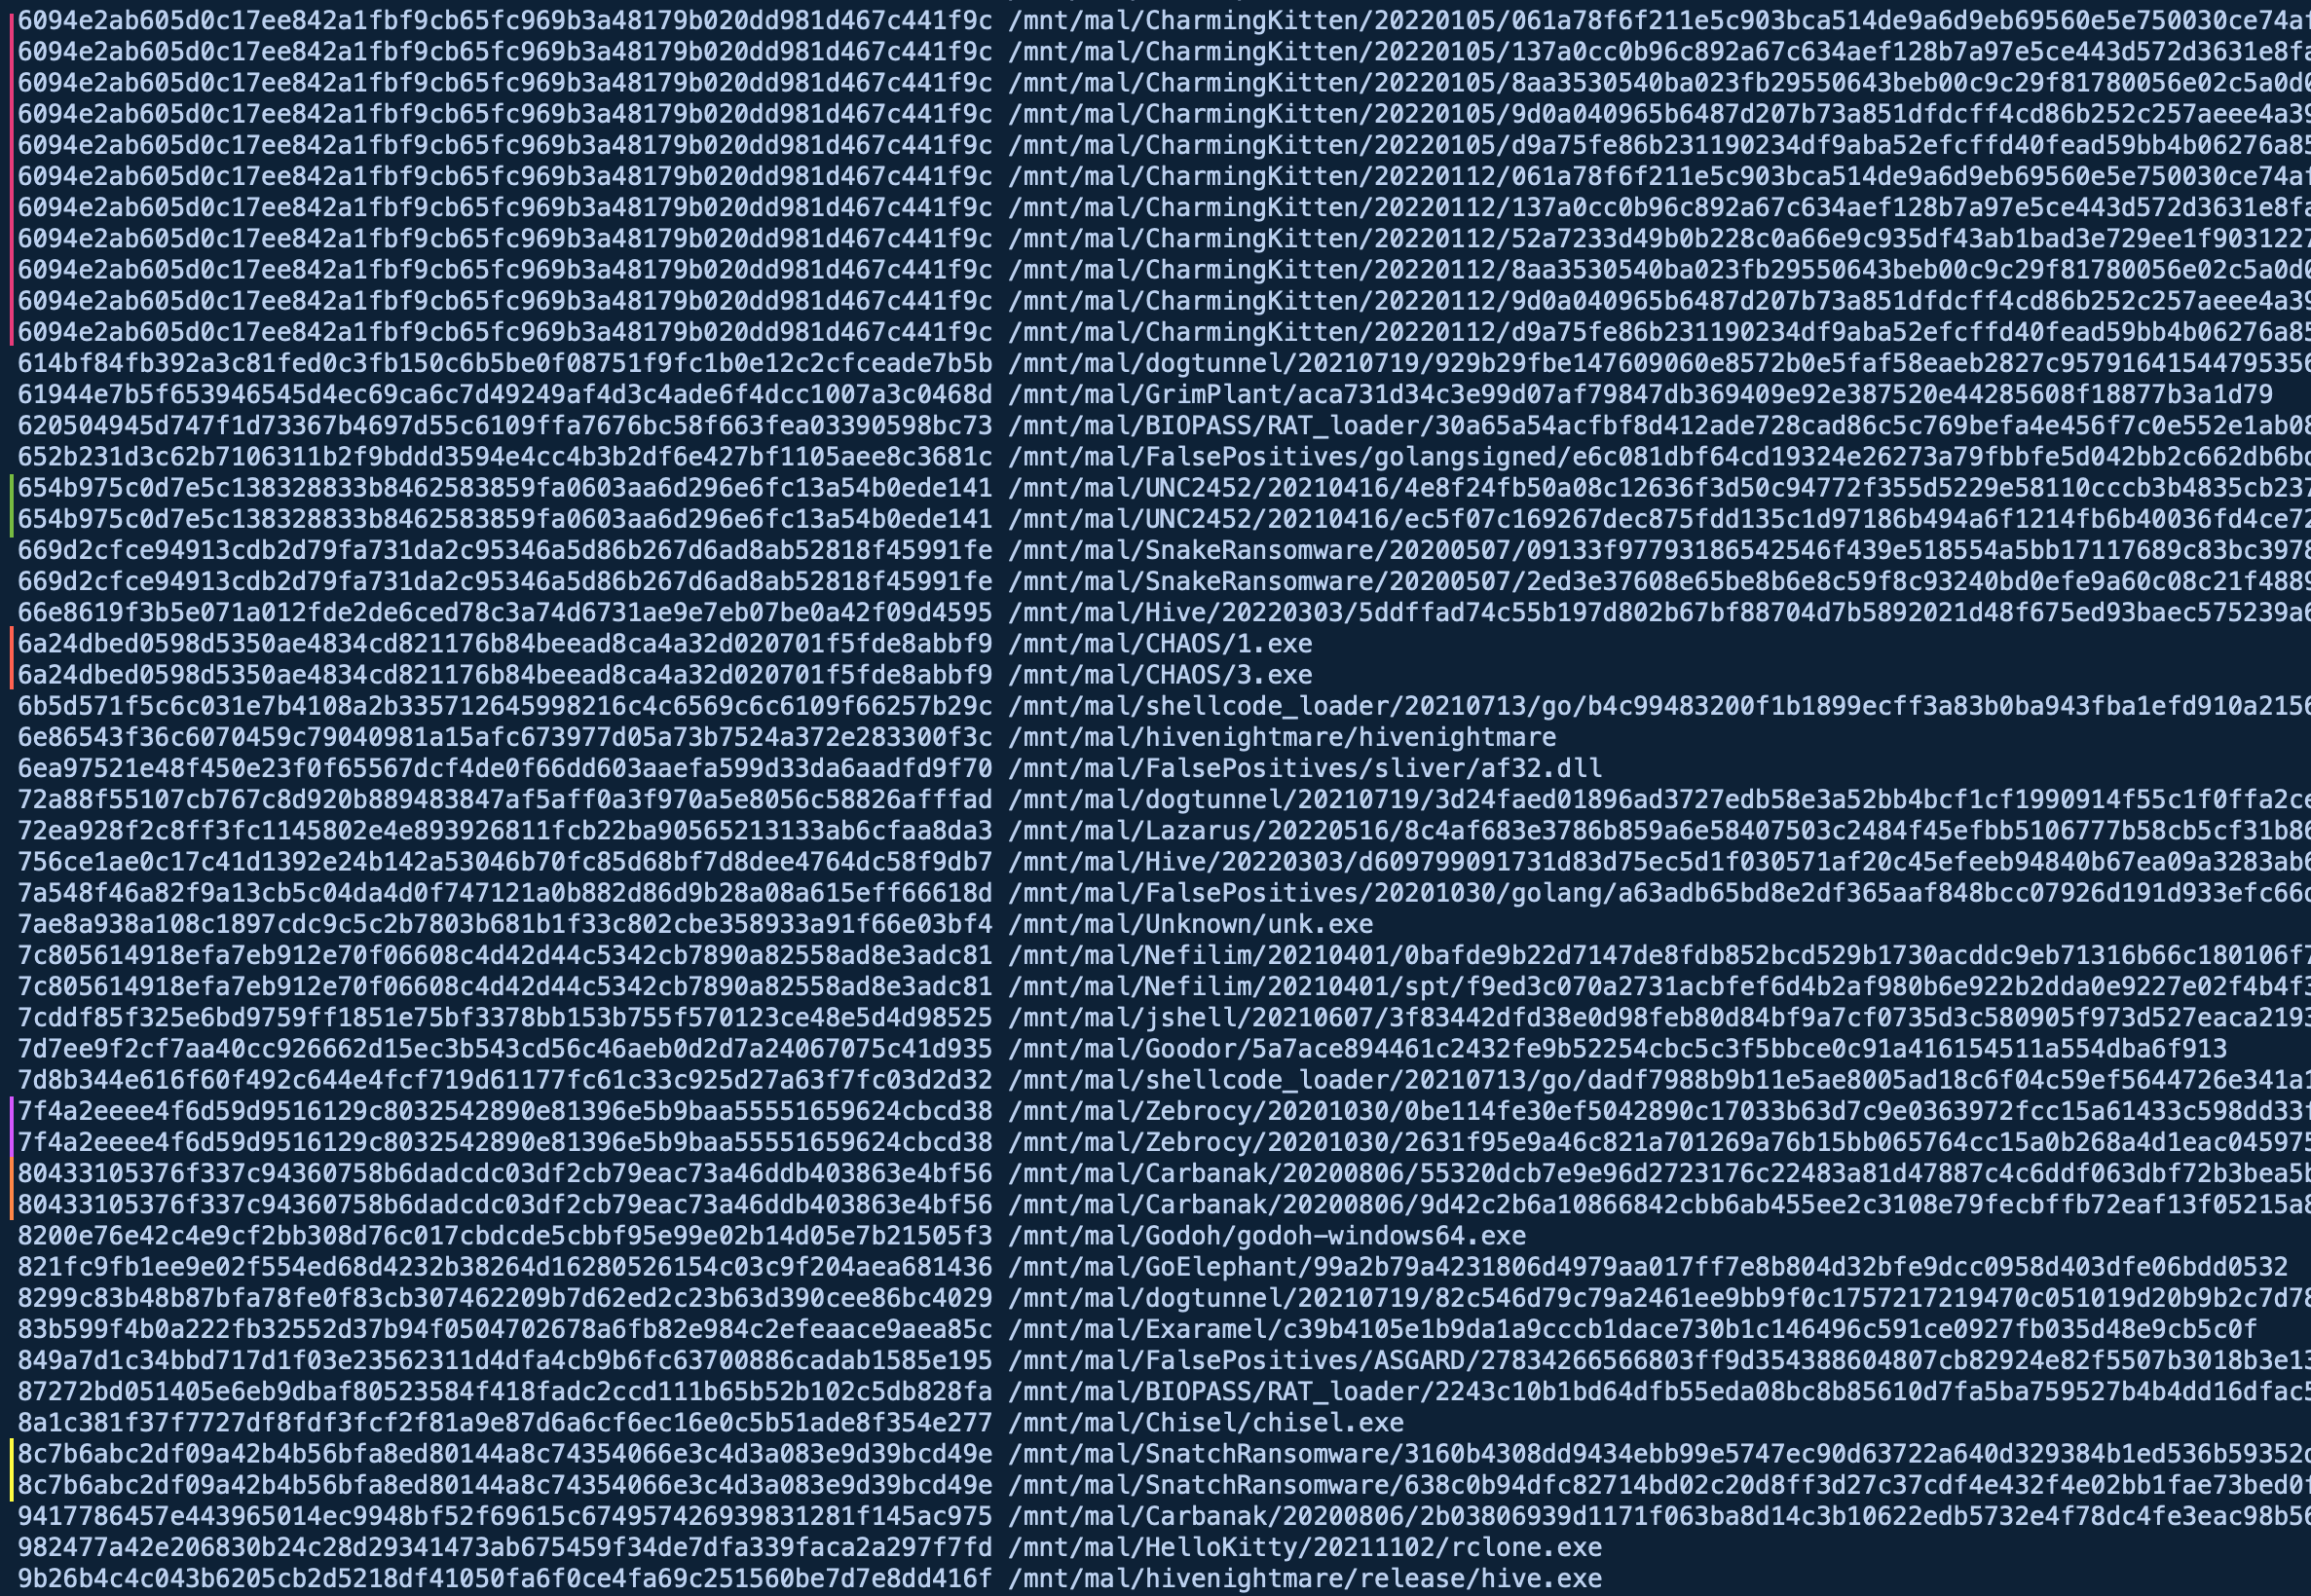 nextronsystems/gimphash
Imphash-like calculation on Golang binaries
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 ea/xfg_analyzer
A Binary Ninja plugin that uses bruteforced XFG hashes to recover precise function prototypes
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
 xoreaxlmbdx/die-in-browser
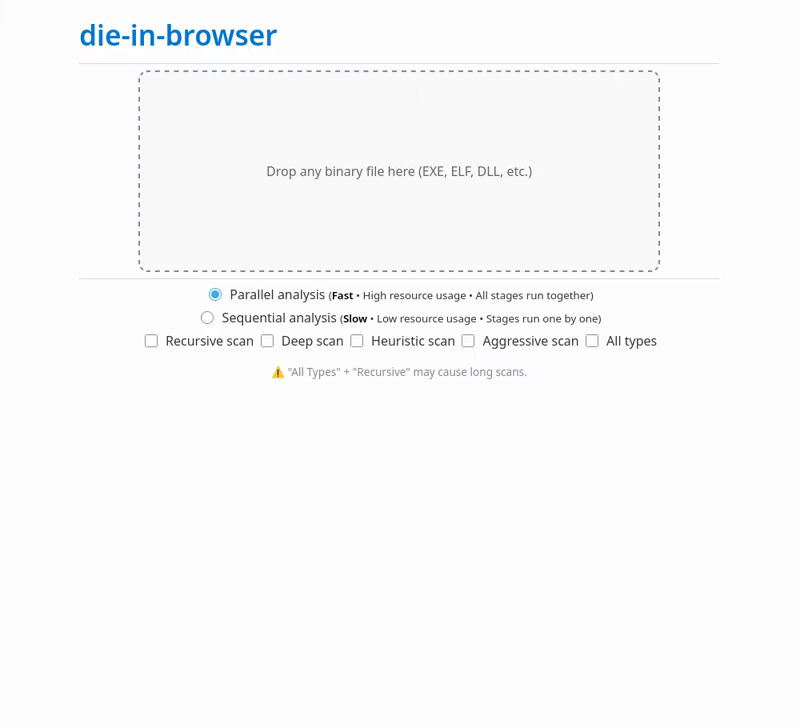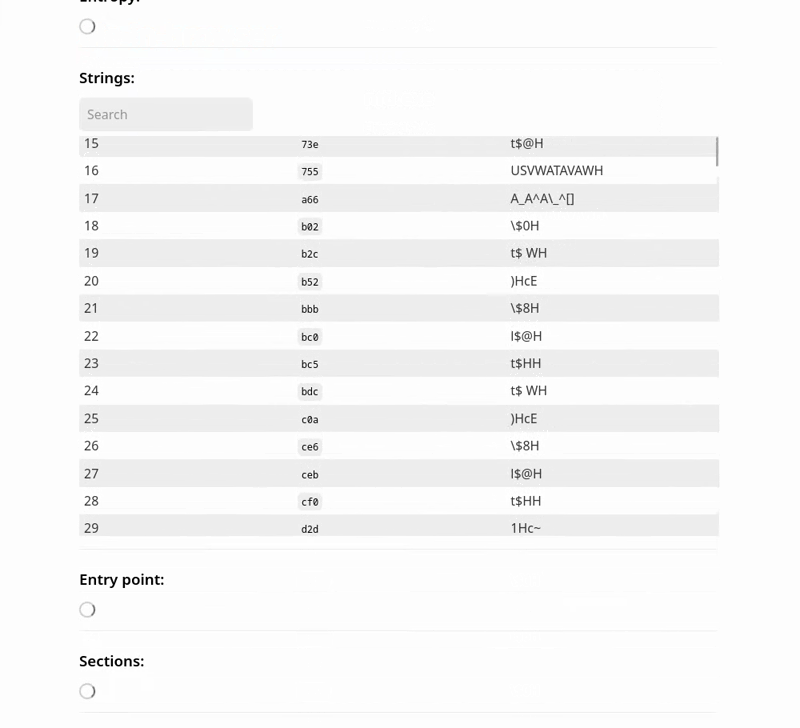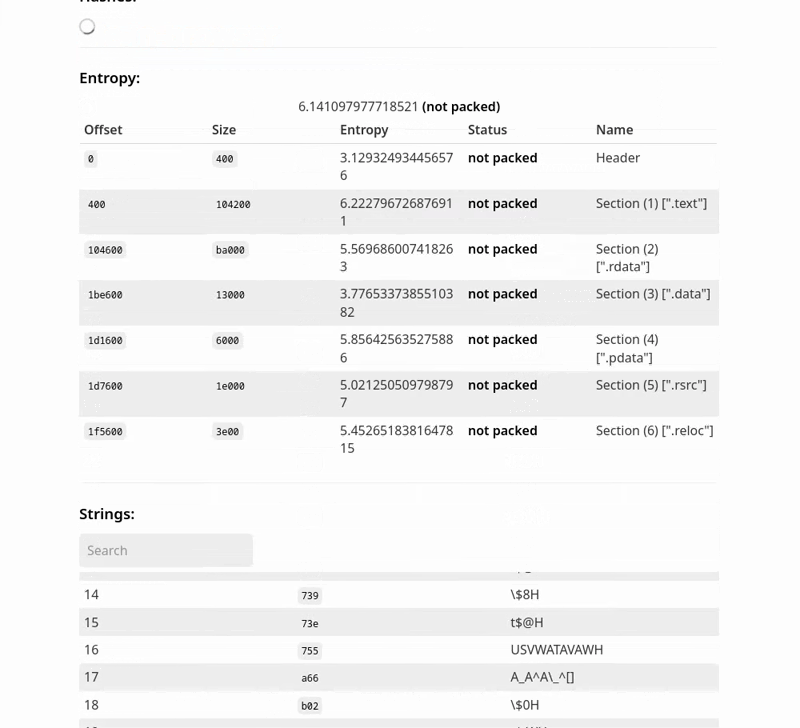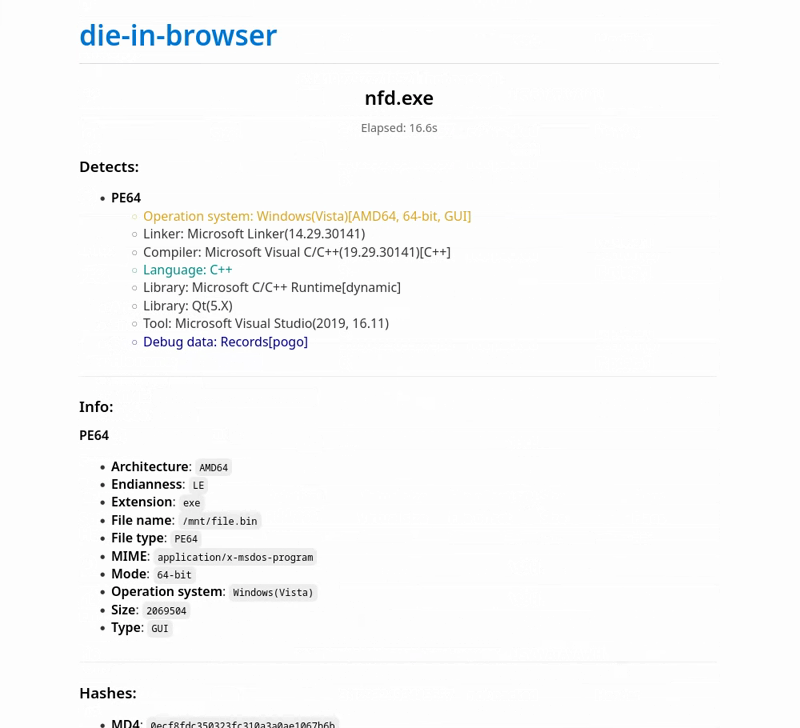
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
 n1ght-w0lf/uchihash
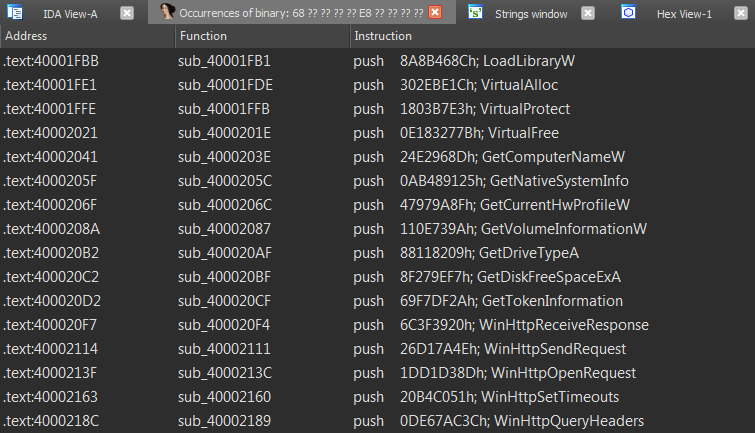
A small utility to deal with malware embedded hashes.
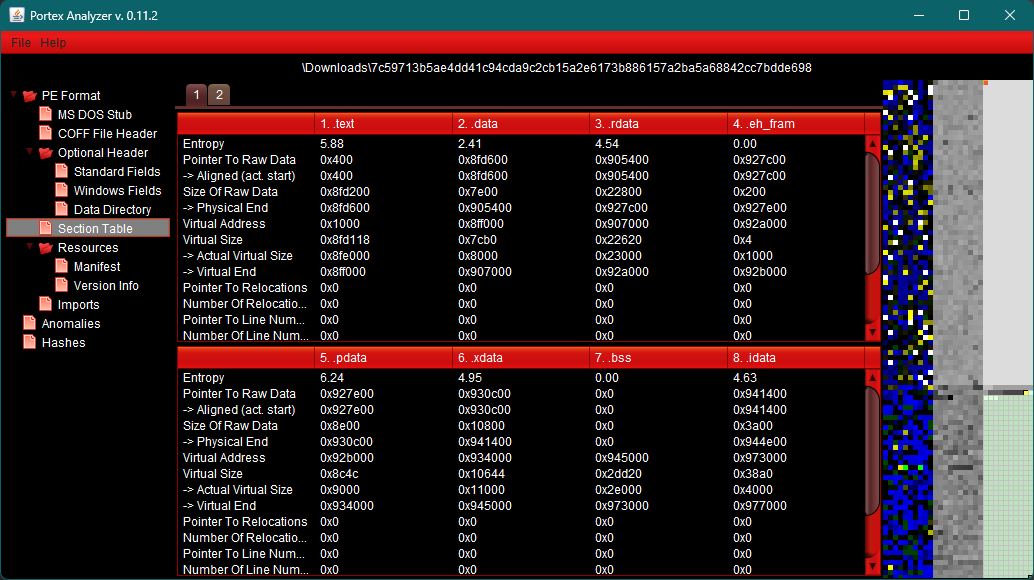 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
 oalabs/hashdb-ida
HashDB API hash lookup plugin for IDA Pro