

scan
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
binary-analysiscode-analysisdefensive-tools+9
514 days ago
atomdrift-project/scan0-day malware detection for binaries, source & scripts (that doesn't suck)
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 imeiplus/ghostlock-pfem10
GhostLock (CVE-2026-43499) for OPPO Find X5 Pro (PFEM10) — OPlus watchdog & heap-spray detector reverse engineering
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 cxlfhx/ghostlock-pfem10
GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes
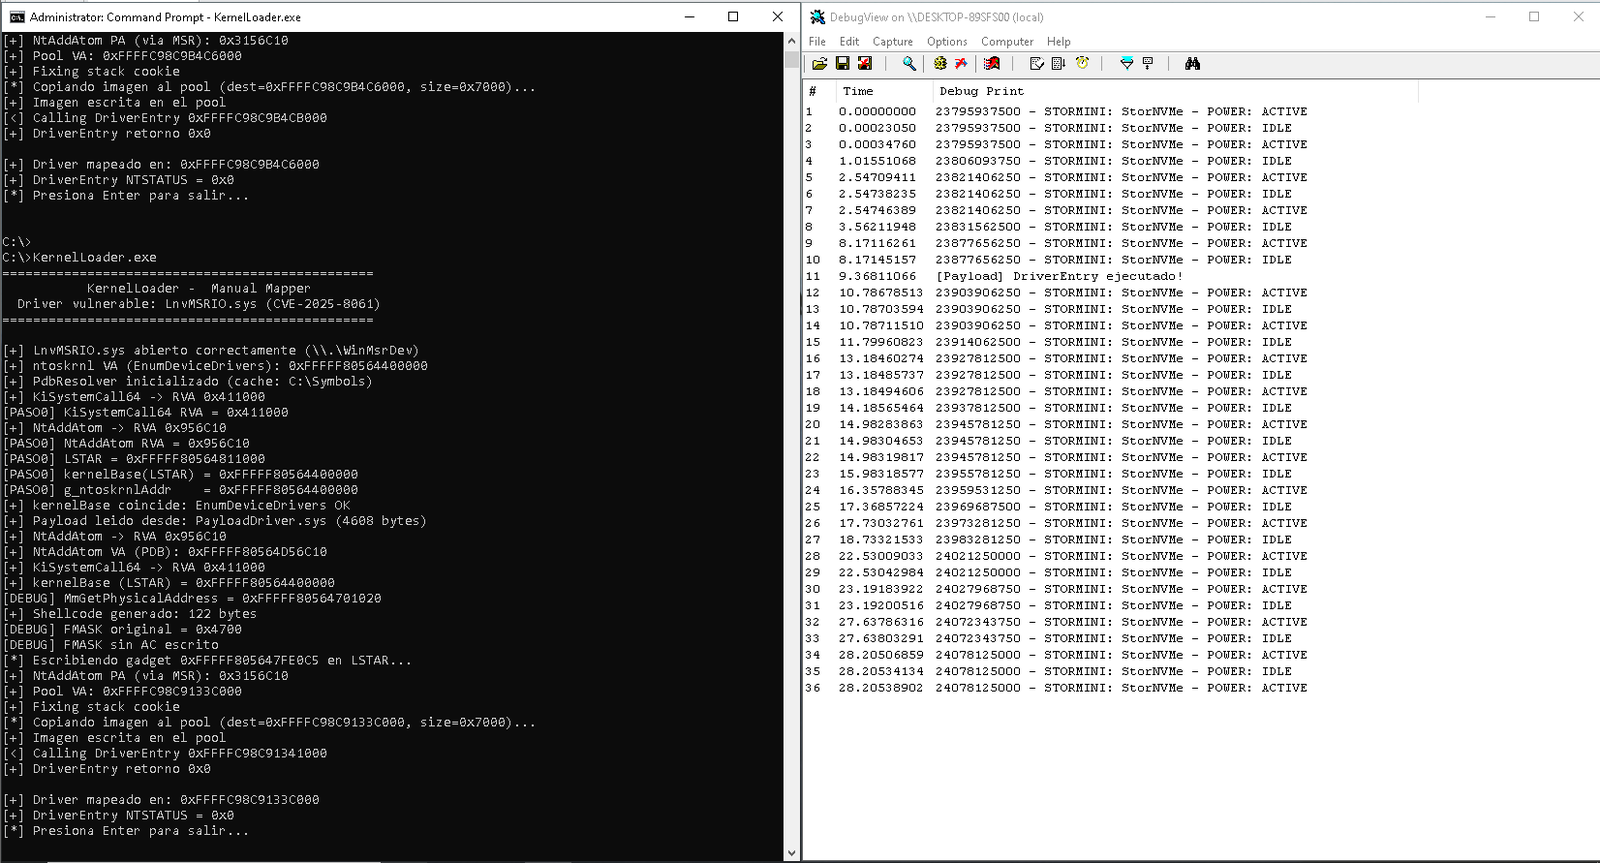 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 ymsniper/umbra
External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
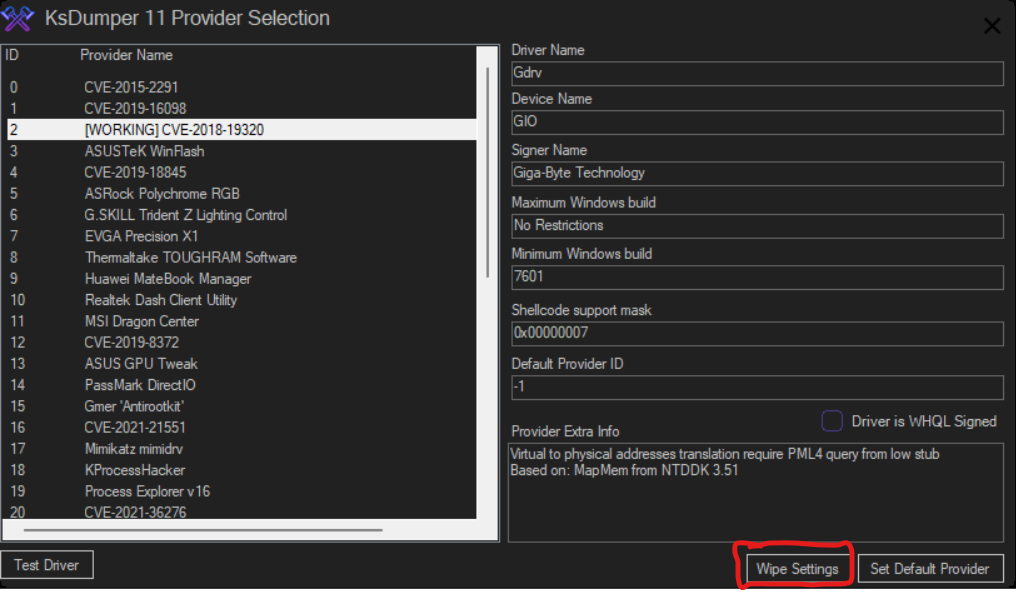 mastercodeon314/ksdumper-11
A revival of the classic and legendary KsDumper
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 wzhdgithub/ghostlock
CVE-2026-43499 futex PI stack UAF ???????? - Android GKI 6.1~6.12 ??????? pselect() + futex PI ????????????,??? root ??? SELinux??? OPPO Find…
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.