ReflectiveDLLRefresher

Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.

Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.

Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…

Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…

Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor

C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…

Debugger utilizing stealth hooks to hide from debugger detection

Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…

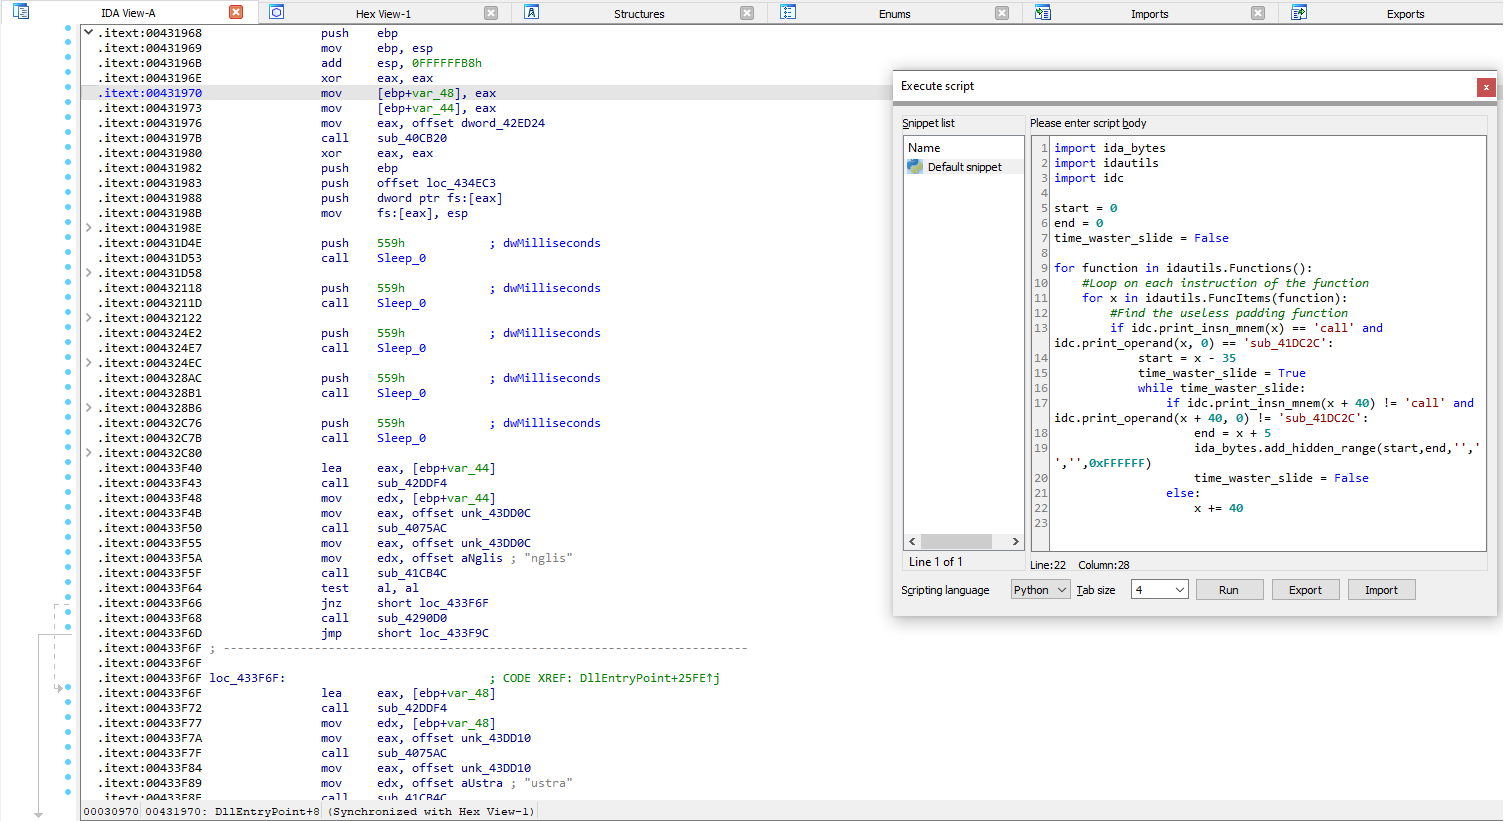
IDA python script for deobfuscating Astaroth/Guildma injector DLL

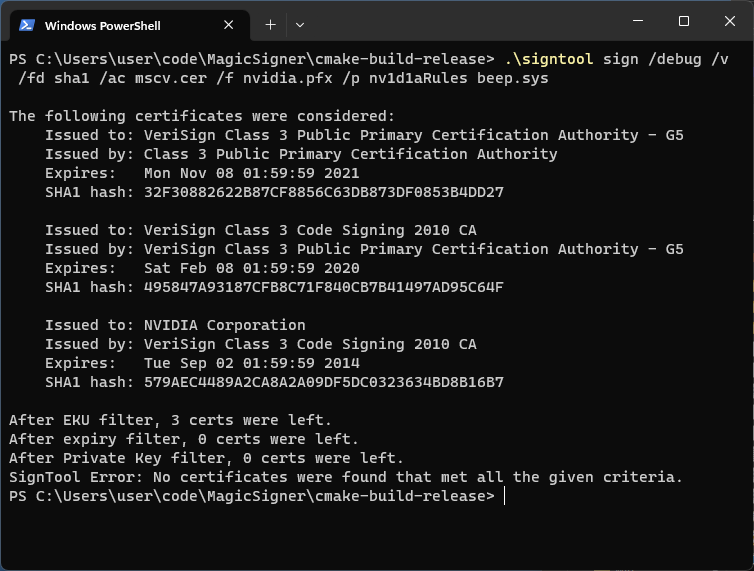
Signtool for expired certificates

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

Generate a proxy dll for arbitrary dll

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

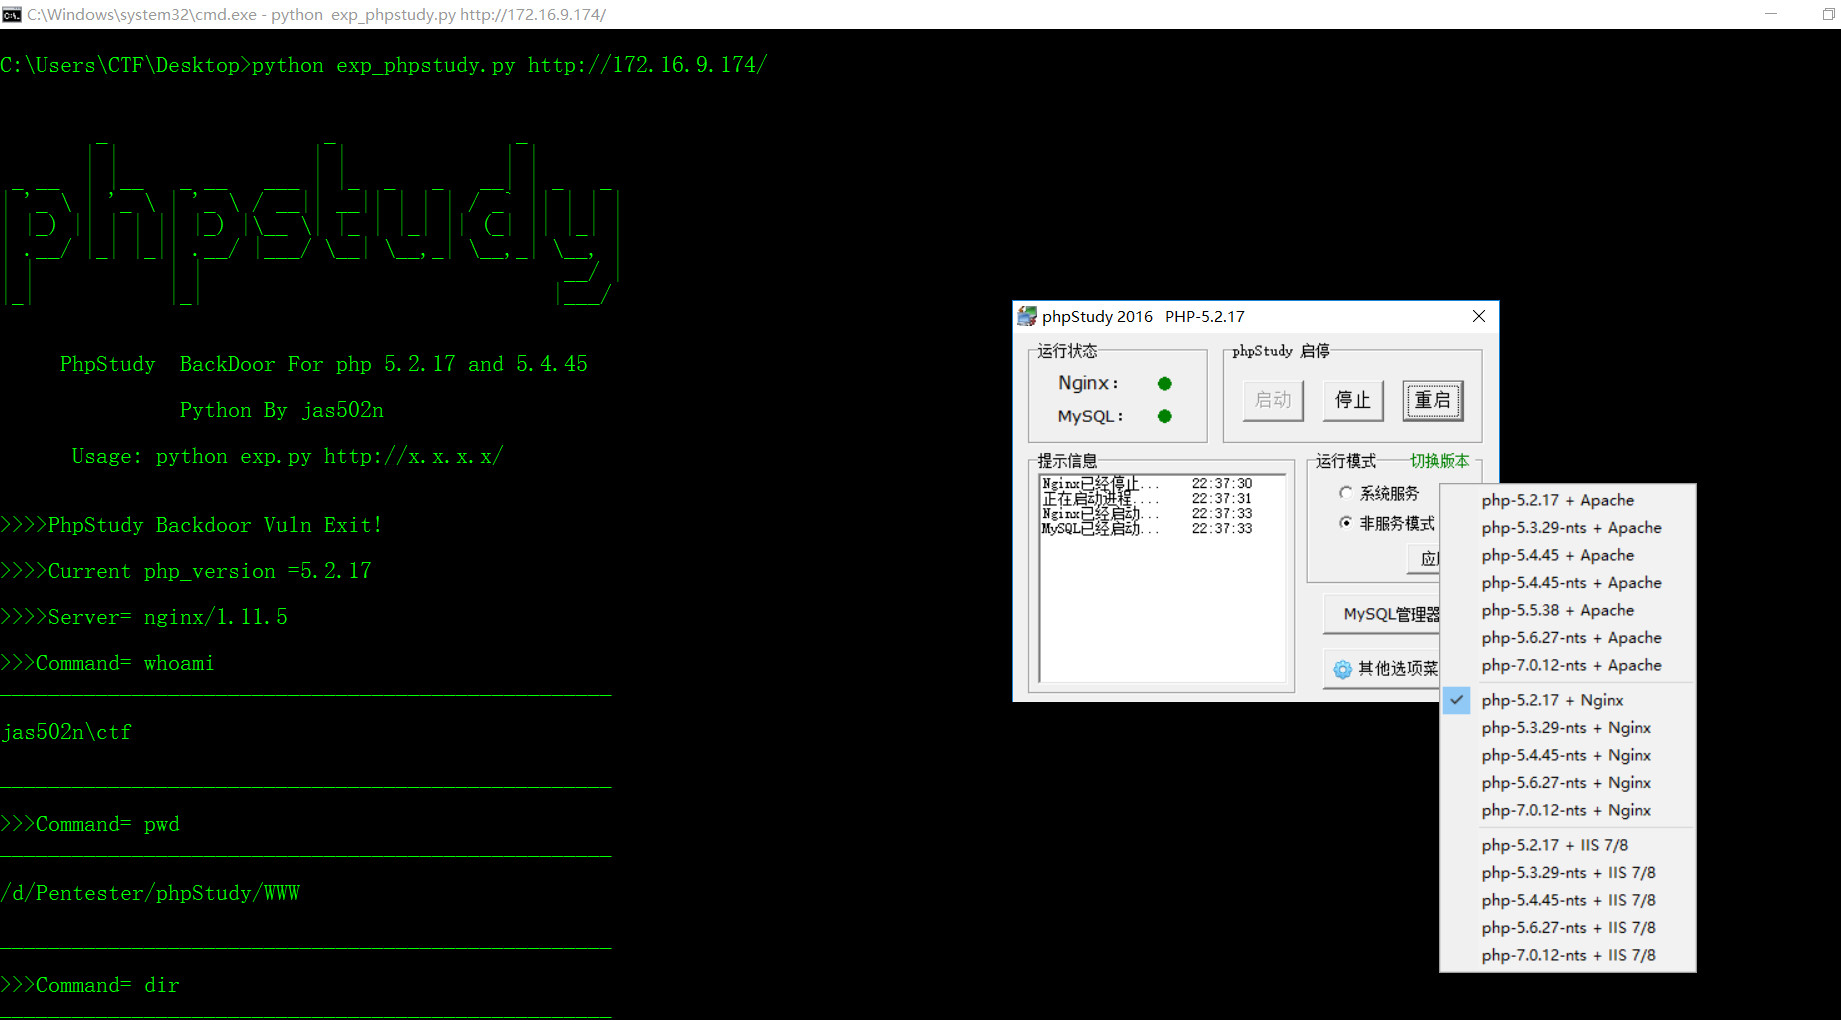
phpstudy dll backdoor for v2016 and v2018

Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…