
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
32 results
umbra preview

umbra

GitHubymsniper/umbra

External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…
exploitationmemory-forensicsred-teaming+1
14
2 days ago
efiSeek preview

efiSeek

GitHubdsecurity/efiseek

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
binary-analysisembedded-systems-securityfirmware-analysis+3
4072 years ago
ghostlock-app preview

ghostlock-app

GitHubyukonga/ghostlock-app

GhostLock One-Tap Execution App (CVE-2026-43499)
android-securitybinary-analysisexploitation+4
8187 days ago
F9360-CVE43499 preview

F9360-CVE43499

GitHube-r-butch/f9360-cve43499

SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
android-securitybinary-exploitationeducation+5
415 days ago
YARA_for_config_extraction preview

YARA_for_config_extraction

GitHubtheatha/yara_for_config_extraction

Tutorial and source code for building a custom YARA module in C to extract malware configurations, with a practical Danabot example and reusable…
binary-analysiseducationmalware-analysis+1
82 years ago
machofile preview

machofile

GitHubpstirparo/machofile

machofile is a module to parse Mach-O binary files
binary-analysisforensicsmalware-analysis+2
997 months ago
CVE-2025-3052 preview

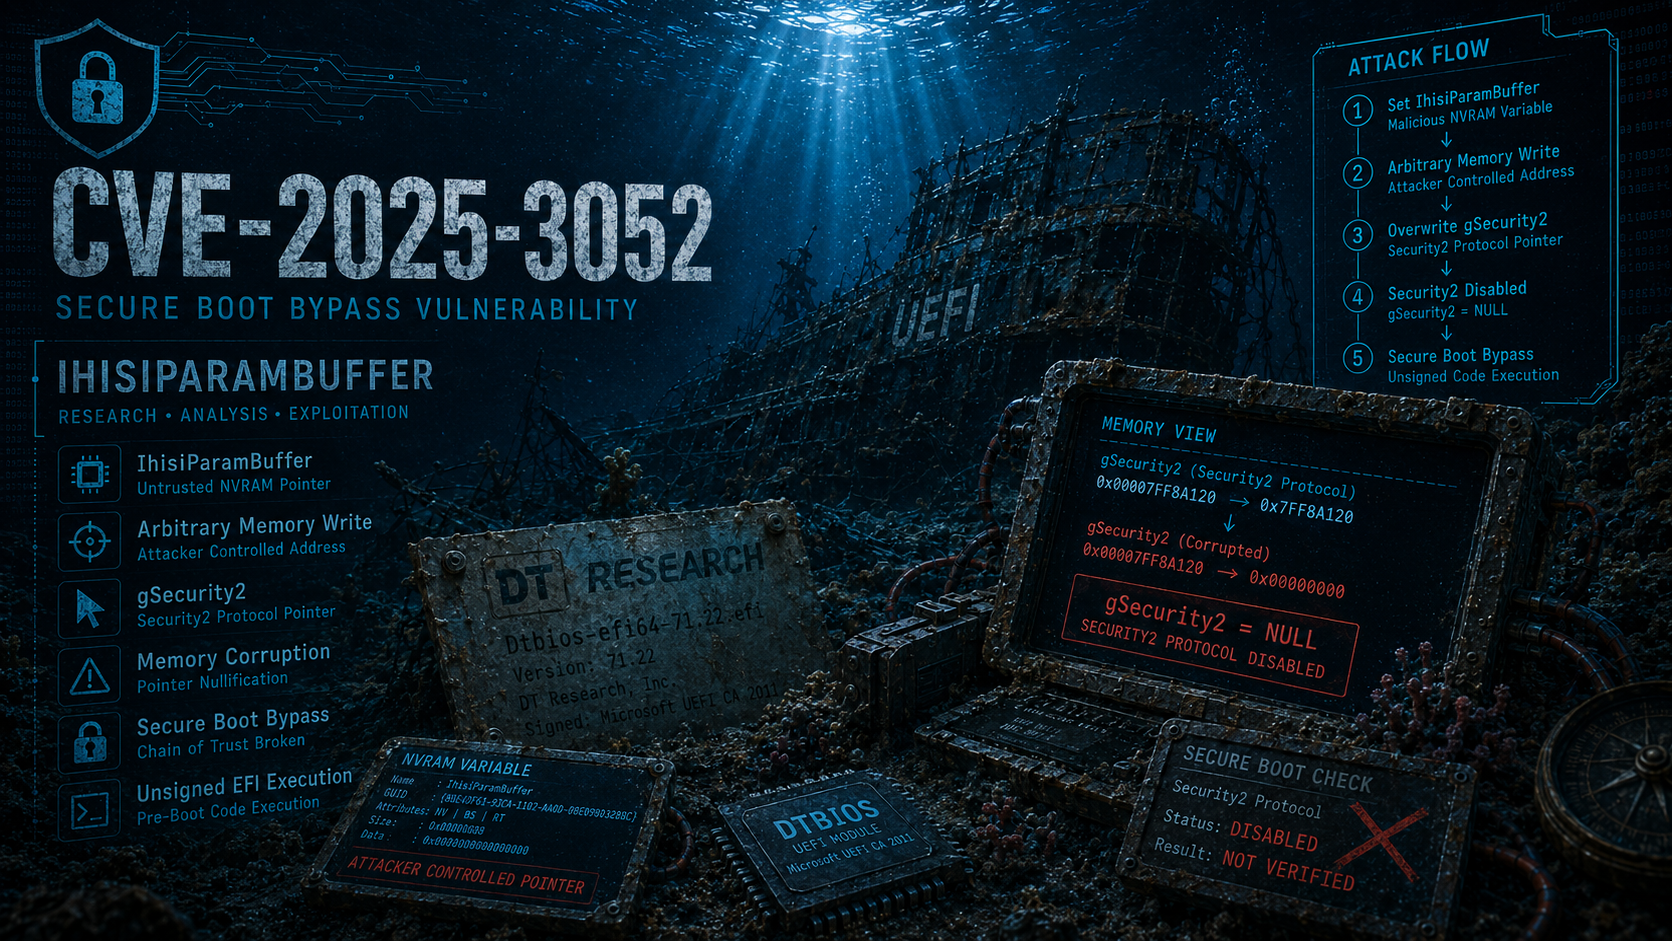
CVE-2025-3052

GitHubthemalwareguardian/cve-2025-3052

Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
binary-analysiseducationembedded-systems-security+5
1 month ago
ida_kcpp preview

ida_kcpp

GitHubcellebrite-labs/ida_kcpp

An IDAPython module for enhancing c++ support on top of ida_kernelcache

binary-analysisios-securitymobile-security+2
1441 month ago
ghidra-nanomips preview

ghidra-nanomips

GitHubnccgroup/ghidra-nanomips

nanoMIPS module for Ghidra
binary-analysisembedded-systems-securityreverse-engineering+1
5610 months ago
rpef preview

rpef

GitHubmncoppola/rpef

Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers

embedded-systems-securityexploitationfirmware-analysis+6
12412 years ago
amtracker preview

amtracker

GitHubjacobsoo/amtracker

Android Malware Tracker

android-securitycommand-and-controlinformation-gathering+3
292 years ago
MalConfig preview

MalConfig

GitHubjacobsoo/malconfig

This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
android-securitycommand-and-controlinformation-gathering+3
77 years ago
ShadeBIOS preview

ShadeBIOS

GitHubffri/shadebios

PoC code of Shade BIOS (stripped) presented at Black Hat USA 2025
binary-analysiseducationembedded-systems-security+5
681 year ago
CVE-2023-33668 preview

CVE-2023-33668

GitHublodi-g/cve-2023-33668

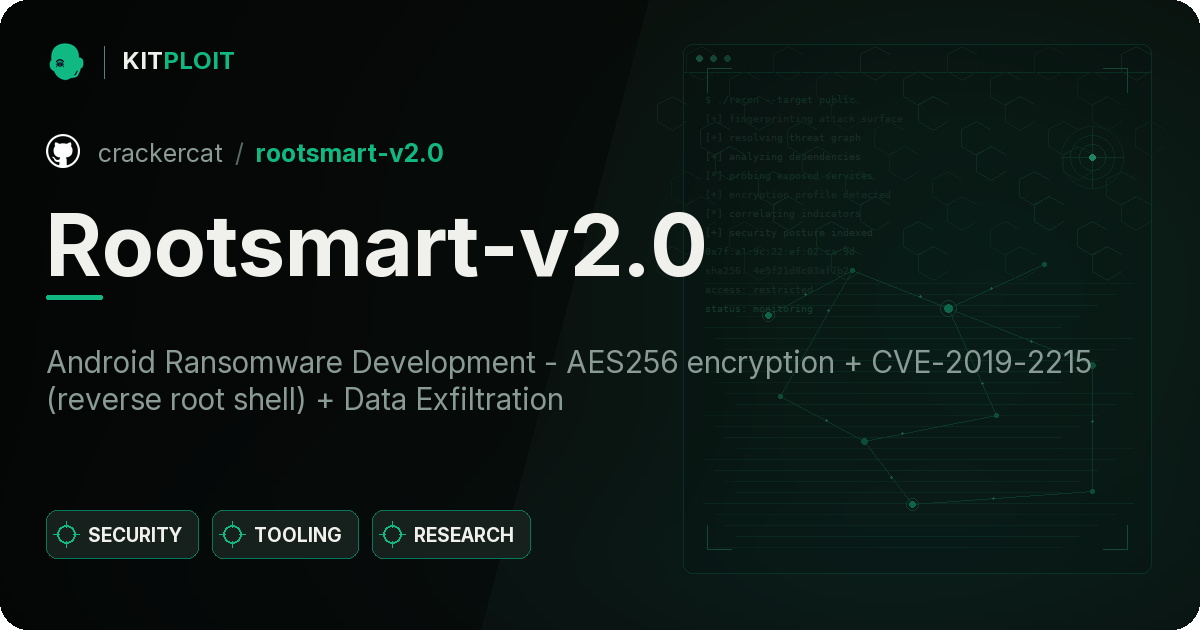
Technical analysis and proof-of-concept bypass for CVE-2023-33668 in DigiExam proctoring software, demonstrating weak VM detection and native module…
binary-analysiseducationexploitation+3
23 years ago
Rootsmart-v2.0 preview

Rootsmart-v2.0

GitHubcrackercat/rootsmart-v2.0

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration

android-securitycommand-and-controldata-exfiltration+8
24 years ago
drvtrace preview

drvtrace

GitHubeversinc33/drvtrace

WinDbg plugin to trace module transitions from a debugged driver.
binary-analysisdebuggersreverse-engineering
548 months ago
Ghidra_v810_v830 preview

Ghidra_v810_v830

GitHub20enderdude20/ghidra_v810_v830

Ghidra processor description module for NEC/Renesas v810 and v830 families
binary-analysisembedded-systems-securityfirmware-analysis+3
75 months ago
pefile preview

pefile

GitHuberocarrera/pefile

pefile is a Python module to read and work with PE (Portable Executable) files

binary-analysisforensicsmalware-analysis+3
2.1k3 days ago
Previous12Next