

disrobe
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
android-securitybinary-analysisfirmware-analysis+4
167
1-3-7/disrobeRust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 rva3/cve-2026-40003
Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
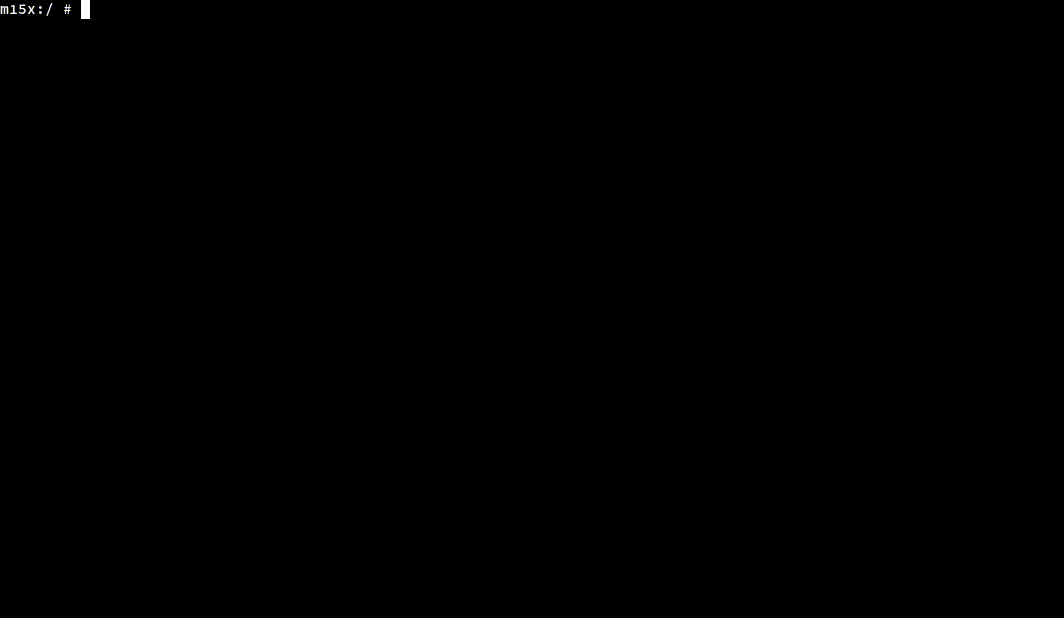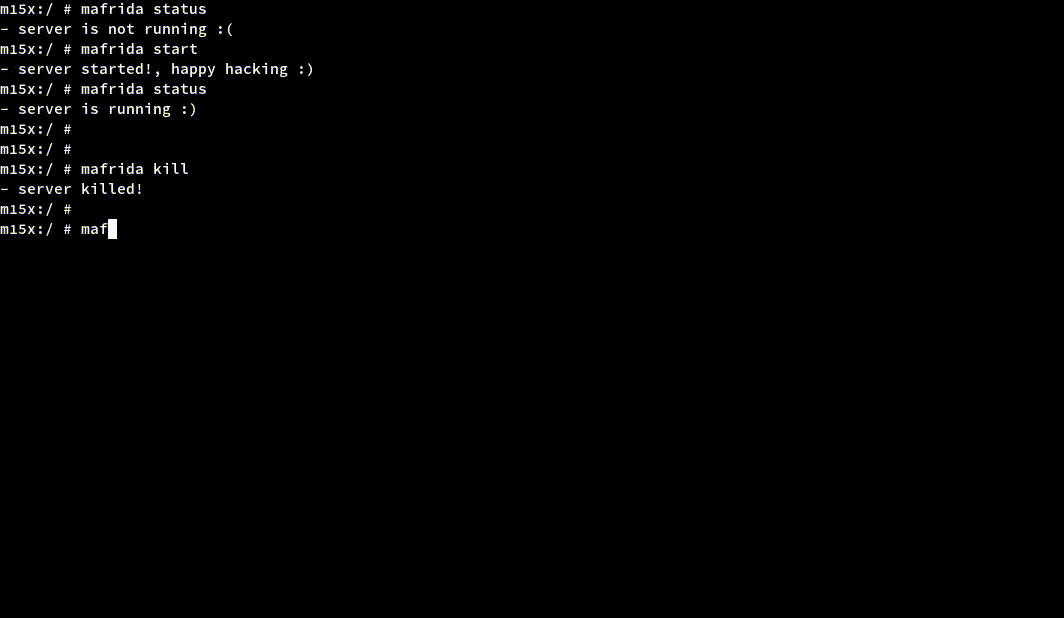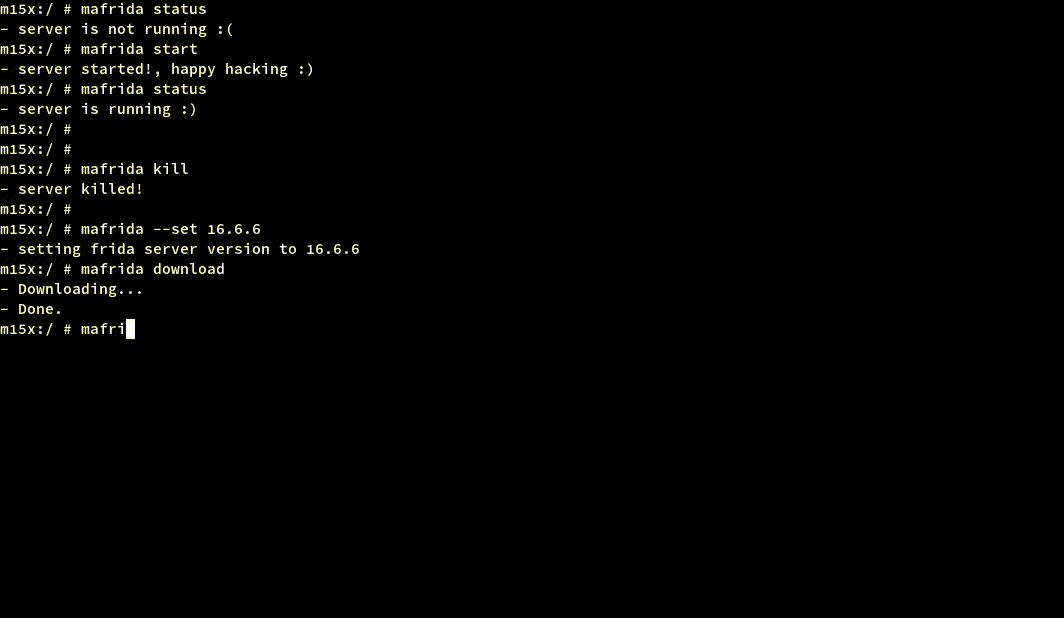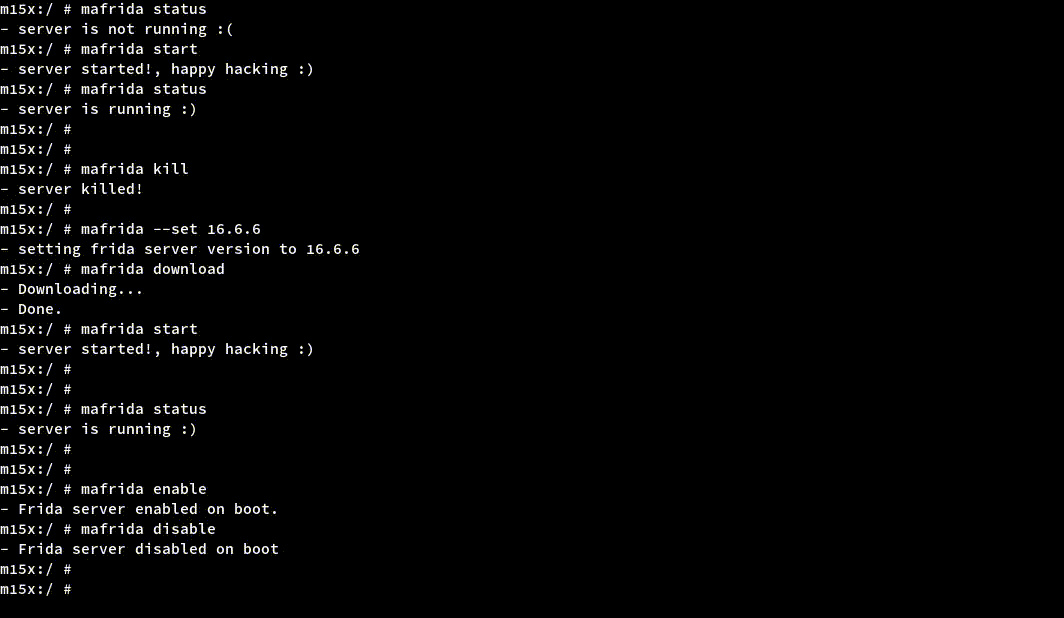 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 joxeankoret/diaphora
Diaphora, the most advanced Free and Open Source program diffing tool.
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.

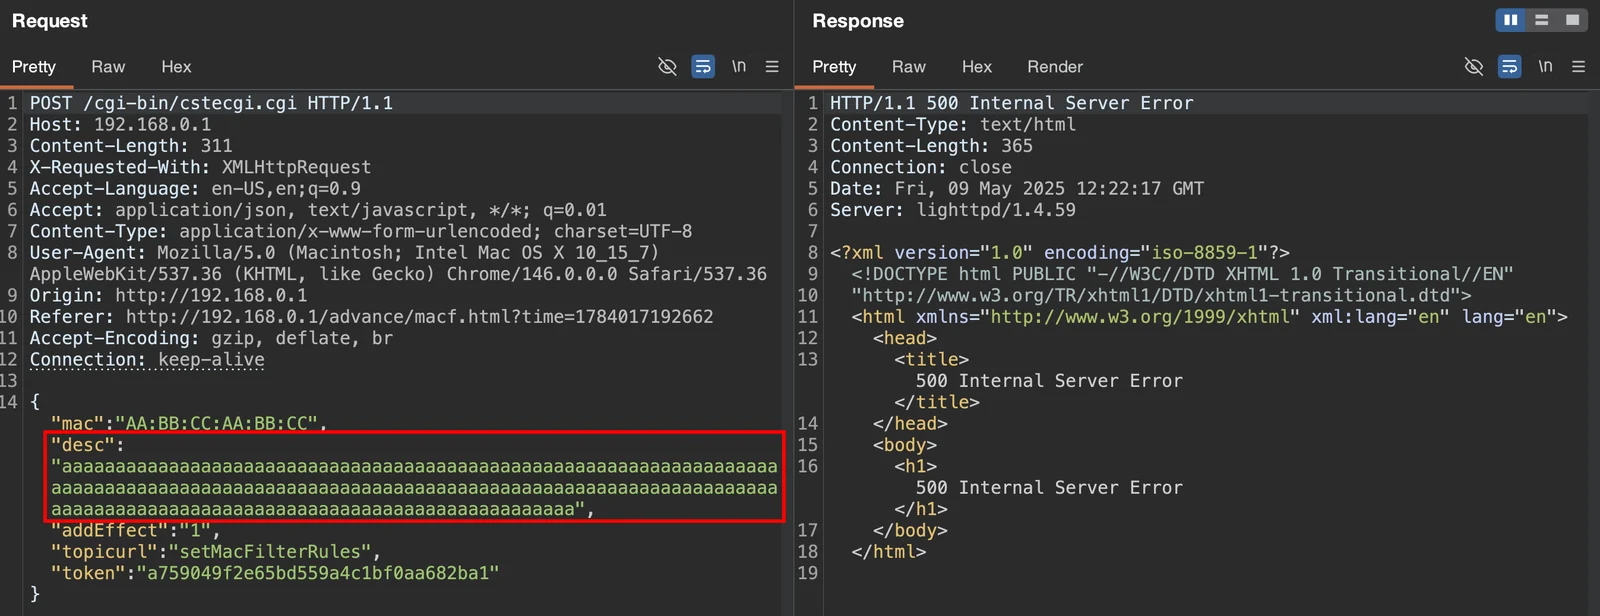 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 p0dalirius/pdbdownload
An utility to download PDB files associated with a Portable Executable (PE).
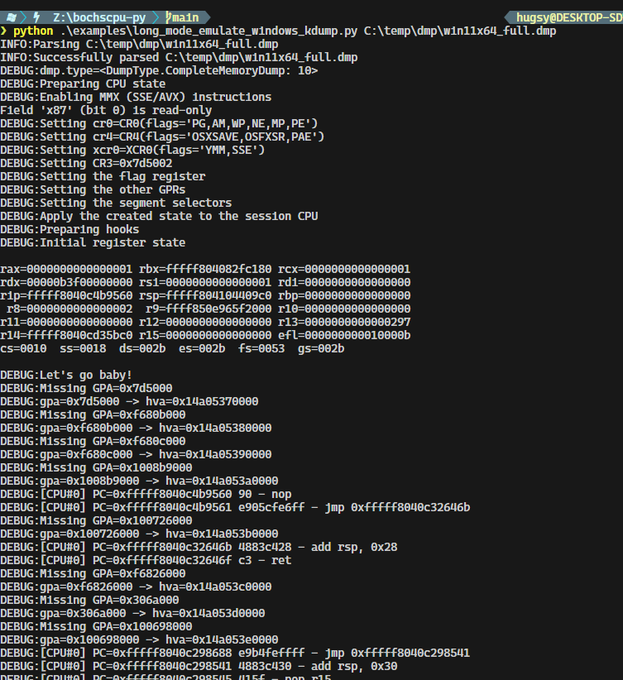 hugsy/bochscpu-python
Python bindings for BochsCPU
 xernary/cve-2025-15545
Proof of Concept for CVE-2025-15545