

ceasta
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
169
ngwg/ceastadisassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 grecandrei/ida-pro-mcp
Local-first, deterministic MCP server for IDA Pro/Home: 109 strict-schema reverse-engineering operations, evidence-backed findings, and policy-gated…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 maximilianfeix/hexvero
Know what changed inside your app: inspect Electron apps and binaries, trace findings to file and line, compare releases. Locally, without executing…
 nemo22/retrokit
Headless-Ghidra toolkit for reverse engineering 32-bit DOS and Win32 games (1993-2010): own LE/LX loader, Watcom calling conventions, library…
 cpkt9762/ida-cli
Headless IDA Pro MCP server for AI-assisted binary analysis, powered by idalib
 xteardx/diaphora-mcp
MCP server for automated binary diffing.
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 rshipp/awesome-malware-analysis
Defund the Police.
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
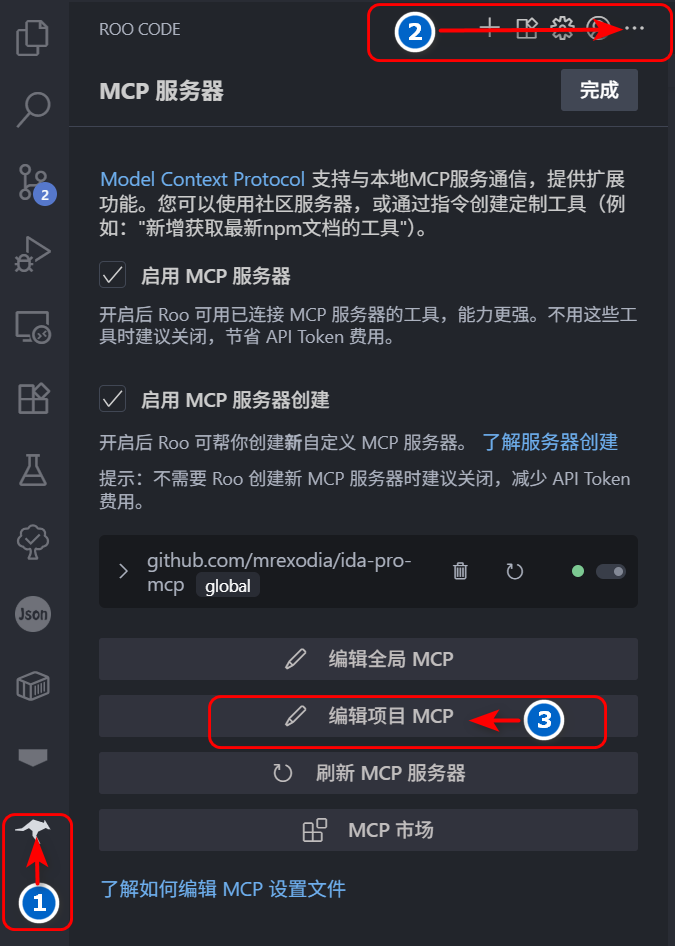 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 lawndoc/mediator
An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.