
Apkx-Hunter
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
android-securityinformation-gatheringmachine-learning+7
98
syscallx-18113/apkx-hunterC-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
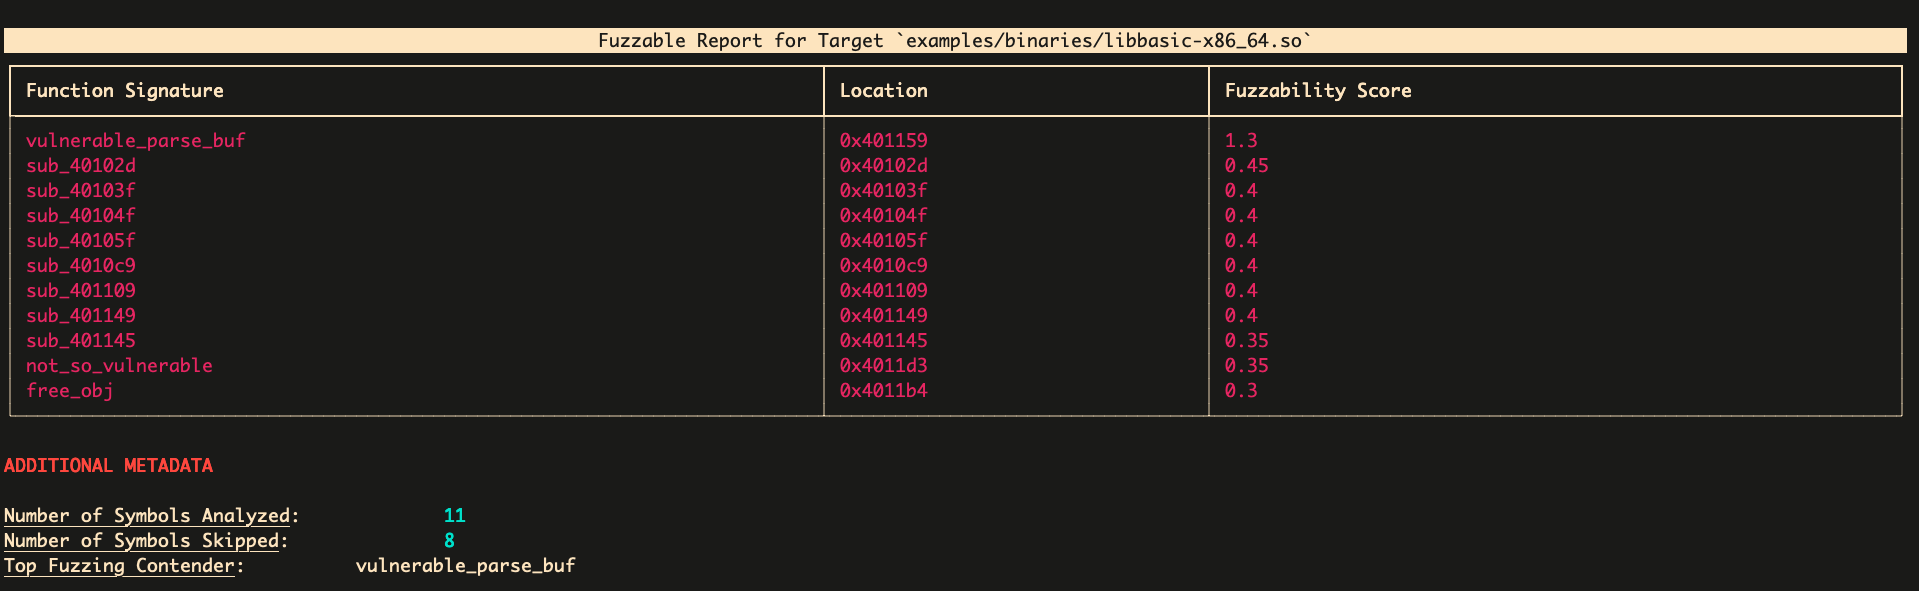 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 openrce/paimei
A reverse engineering framework written in Python.
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 stefan2200/aparoid
Static and dynamic Android application security analysis
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 colton1skees/dna
LLVM based static binary analysis framework
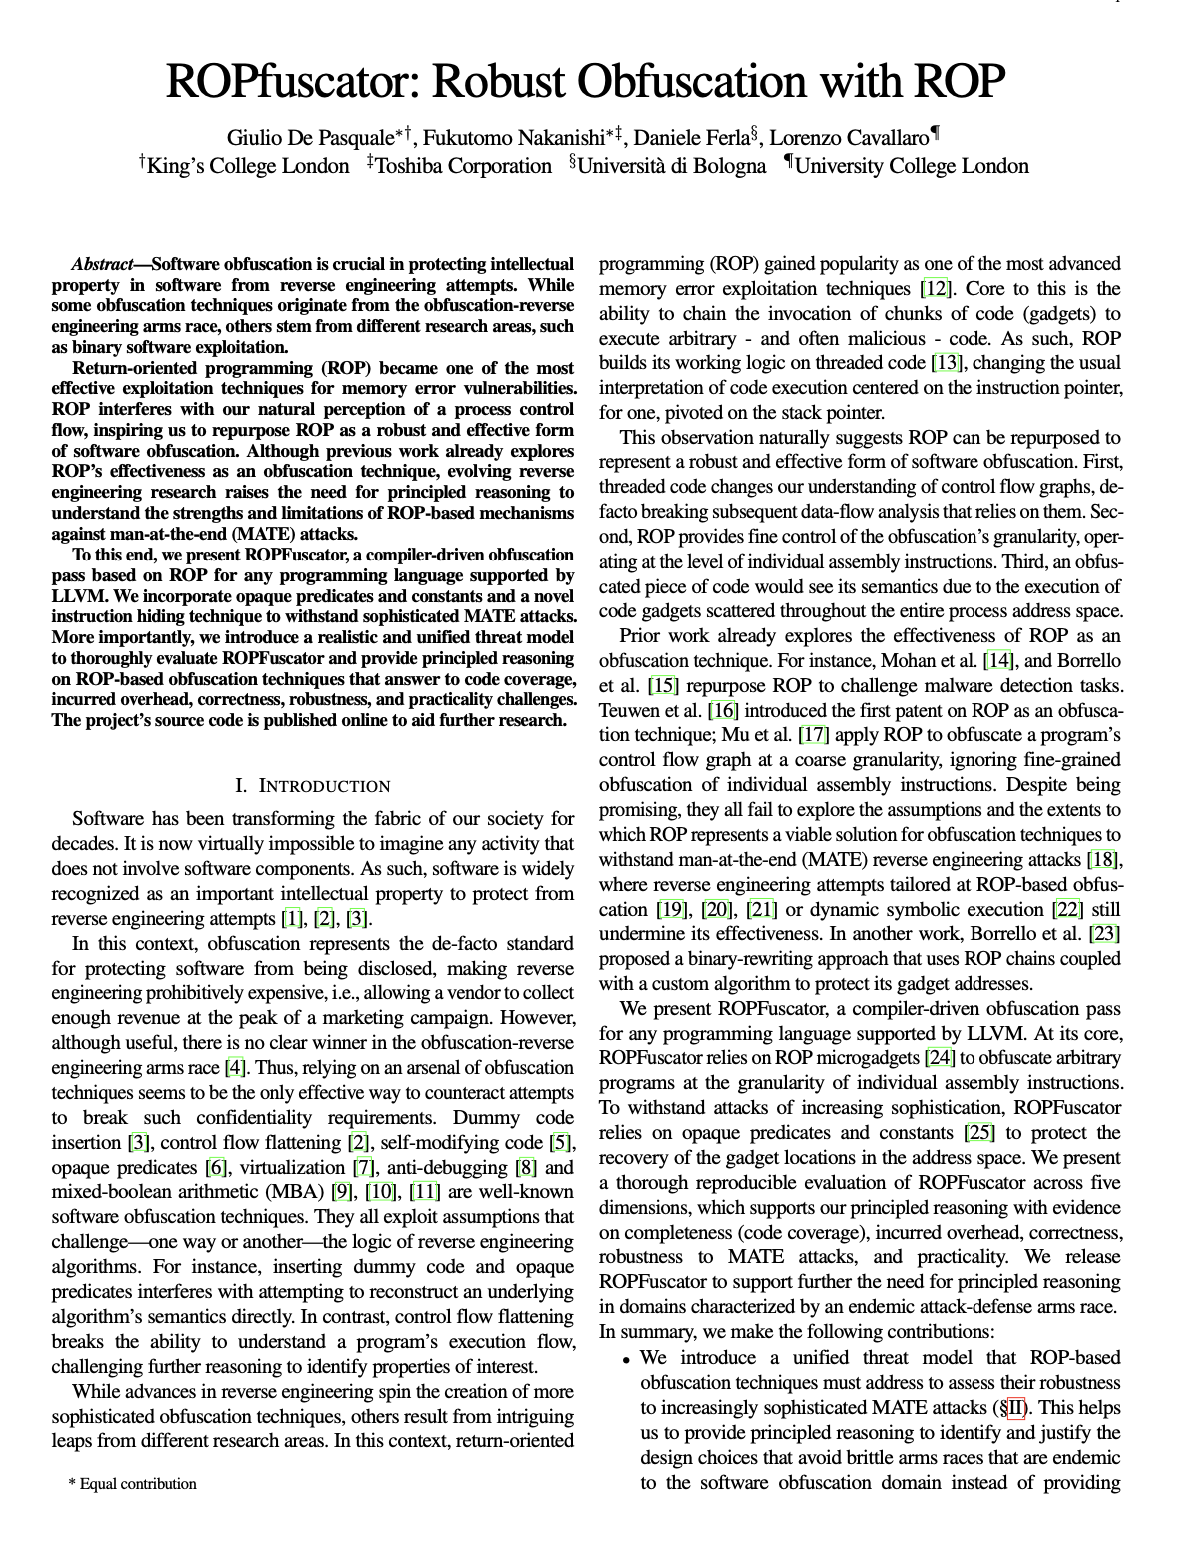 ropfuscator/ropfuscator
ROPfuscator is a fine-grained code obfuscation framework for C/C++ programs using ROP (return-oriented programming).
 mrphrazer/msynth
Code deobfuscation framework to simplify Mixed Boolean-Arithmetic (MBA) expressions