razer-lycosa-kernel-lpe-BYOVD-Vulnerability-PoC

Two kernel vulnerabilities in Razer Lycosa.sys (CWE-125 memory disclosure + CWE-121 stack overflow) chained to local privilege escalation.…

Two kernel vulnerabilities in Razer Lycosa.sys (CWE-125 memory disclosure + CWE-121 stack overflow) chained to local privilege escalation.…

Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…

Proof-of-concept local privilege escalation exploiting Gigabyte gdrv3.sys IOCTLs to write the SYSTEM token into a user process via an unchecked…

Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…

Research repository for CVE-2025-38502, a Linux kernel BPF cgroup local storage out-of-bounds access via tail calls enabling local privilege…

Detailed technical analysis and proof-of-concept exploit for CVE-2024-30051, a heap-based buffer overflow in the Windows DWM Core Library enabling…

Educational proof-of-concept for CVE-2015-2291 local privilege escalation via Intel Ethernet driver IOCTL abuse, demonstrating arbitrary kernel…

Docker-based CVE-2023-4911 lab for analyzing glibc ld.so buffer overflow and developing a local privilege escalation exploit with GDB debugging.

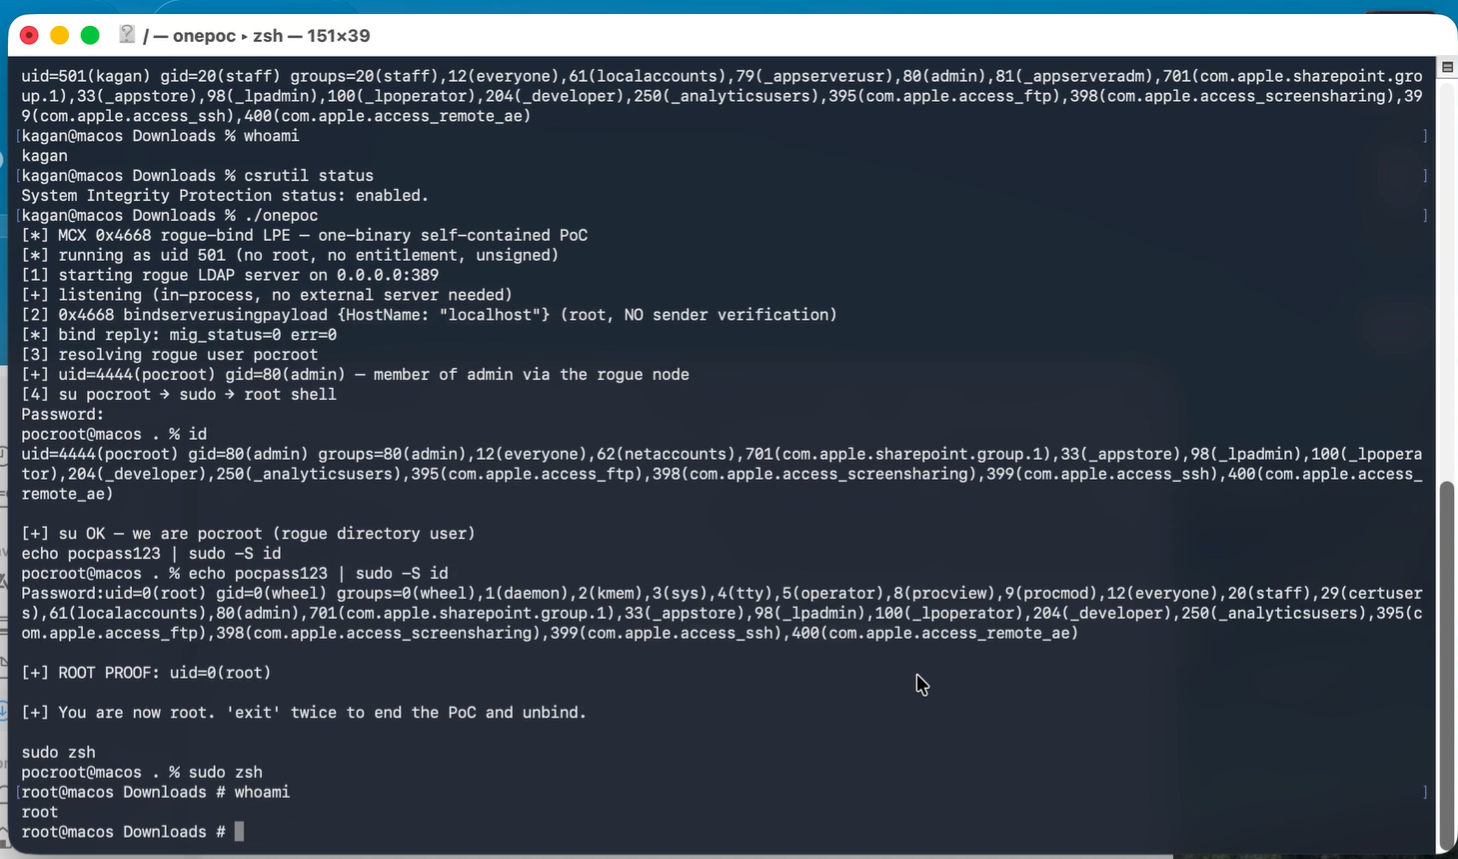
Documentation and research notes for CVE-2026-43786, a macOS local privilege-escalation flaw caused by improper entitlement validation, covering root…

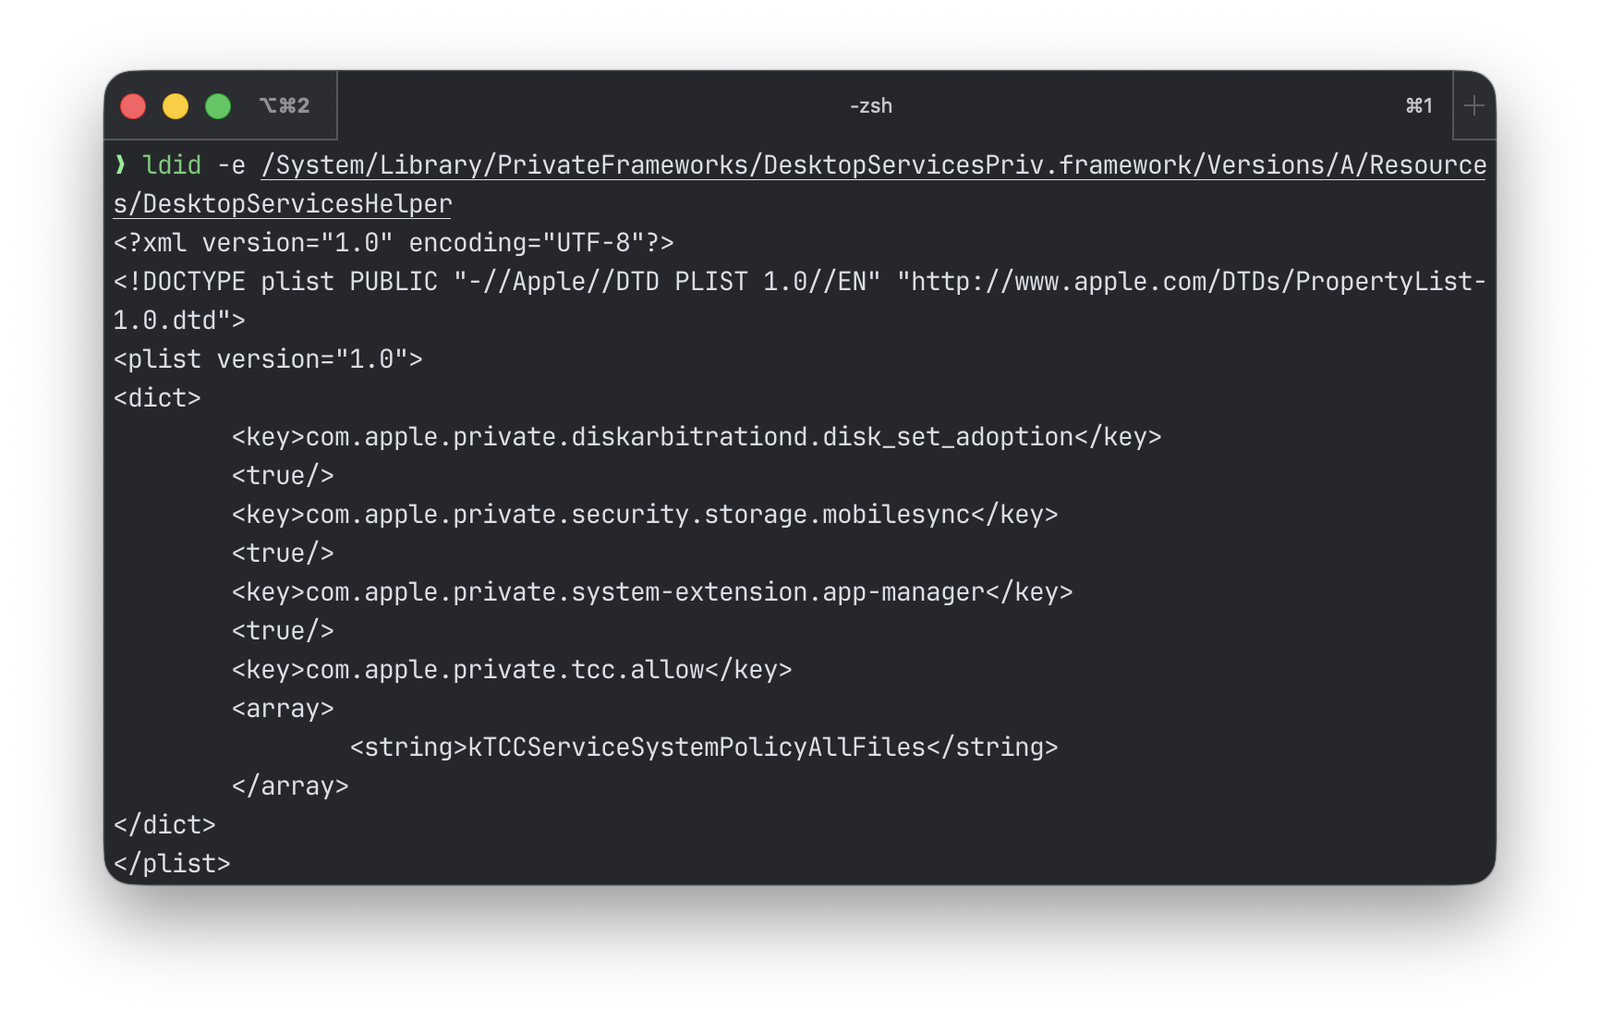
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…

Local privilege escalation exploit for Android Binder bug CVE-2020-0041 (Pixel 3a)

Local privilege escalation exploit for Pixel 3 (CVE-2020-0041) that disables SELinux and spawns a root shell via kernel memory corruption and offset…

Local privilege escalation exploit for CVE-2020-1066 targeting Windows 7 and Server 2008 R2. Leverages arbitrary file replacement via Windows…

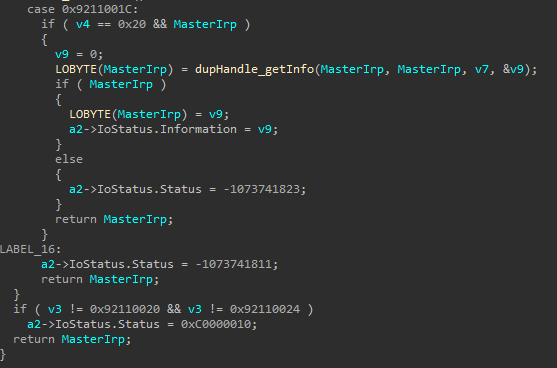
Exploit for a LogMeIn/GoTo Windows kernel driver race condition that duplicates SYSTEM handles, enabling thread-token impersonation and local…

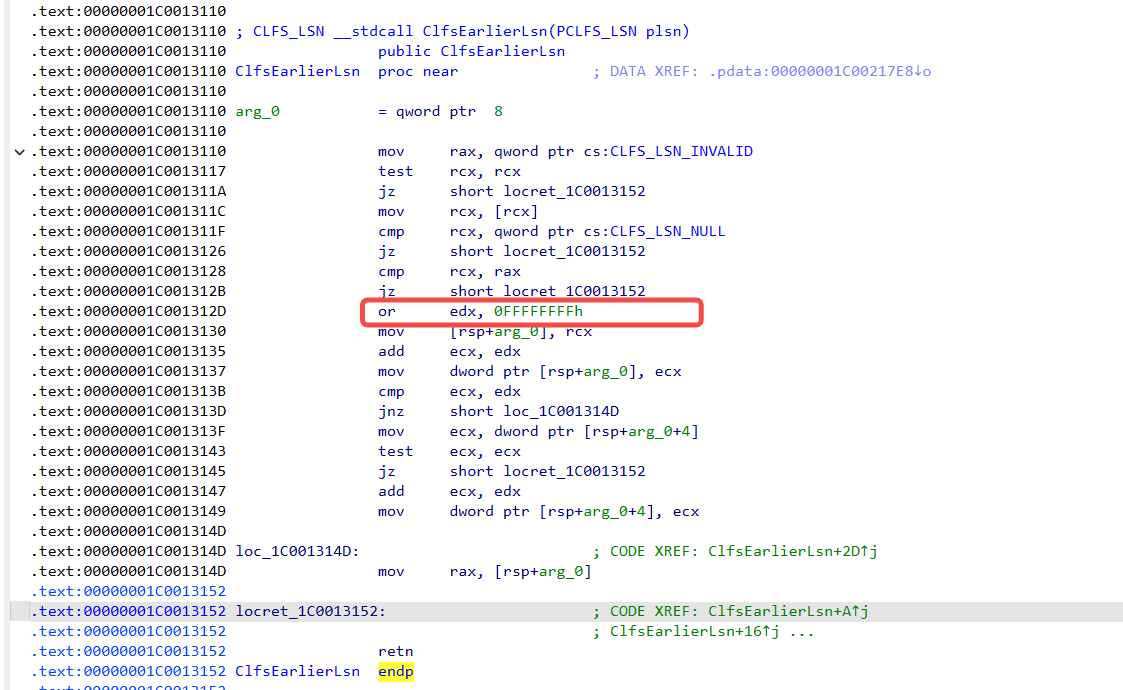
Deep-dive analysis of Windows CLFS type confusion (CVE-2022-24481) with root-cause explanation, exploitation flow, kernel gadget details, and working…

Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…