

Archived
Lime-RAT
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
command-and-controlcryptographydata-exfiltration+7
1.1k
 revoltsecurities/cve-2023-22527
Exploitation tool for CVE-2023-22527 targeting Confluence servers, enabling remote code execution with support for multiple targets, concurrency, and…

 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 ilikenwf/darkagent
DarkAgent Remote Administration Tool RAT by DragonHunter
 danithehack3r/cve-2023-38646
Exploit for CVE-2023-38646 in Metabase 0.46.6, enabling remote code execution via crafted requests and setup token retrieval.
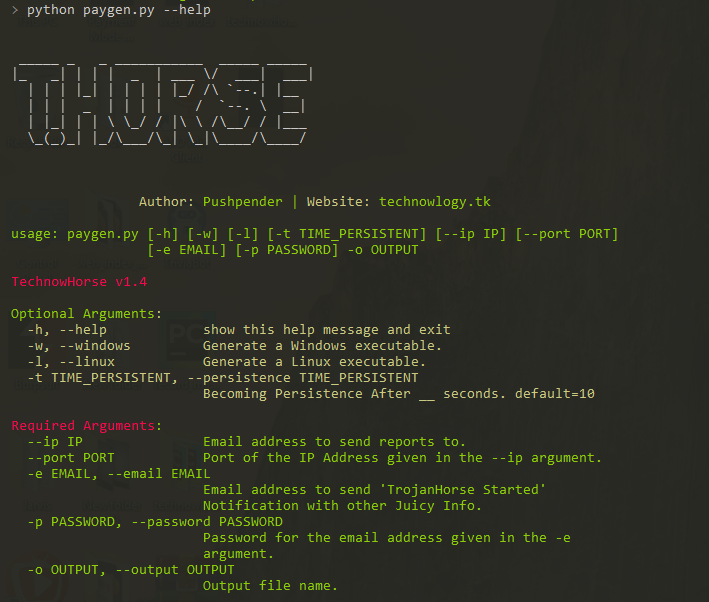 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
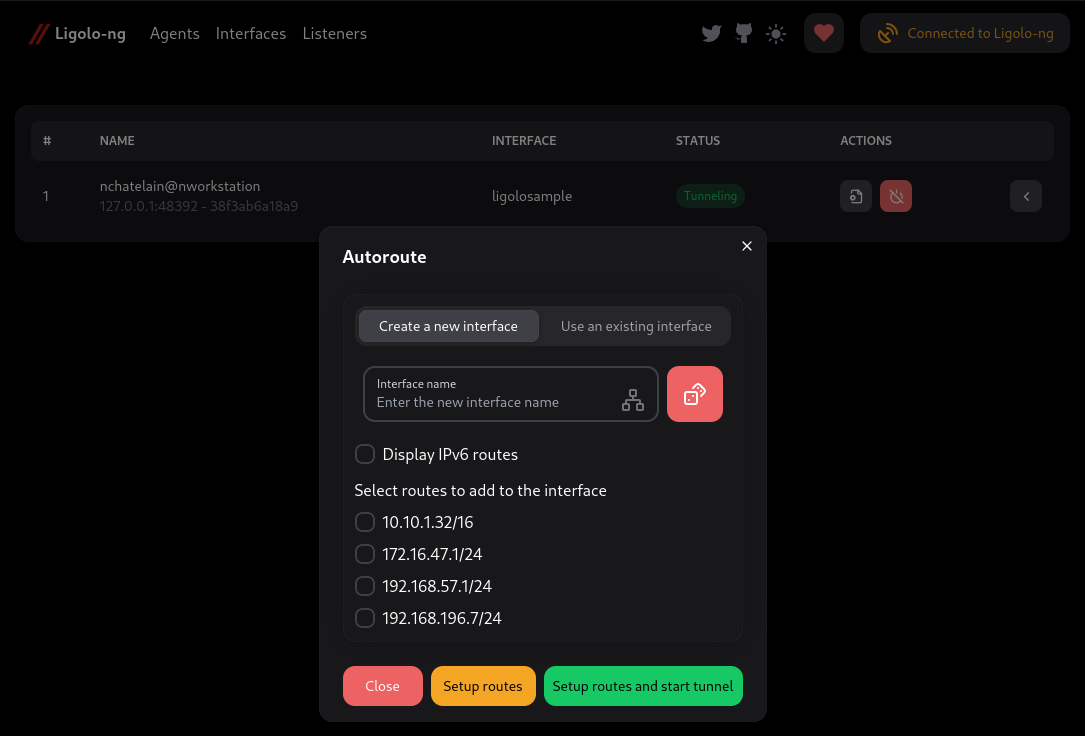 nicocha30/ligolo-ng
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 qwqdanchun/dcrat
A simple remote tool in C#.
 machine1337/pyfud
CROSS PLATFORM REMOTE ACCESS TROJAN (RAT)
 jofpin/backcookie
Small backdoor using cookie.
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 mr-un1k0d3r/thundershell
Python / C# Unmanaged PowerShell based RAT