
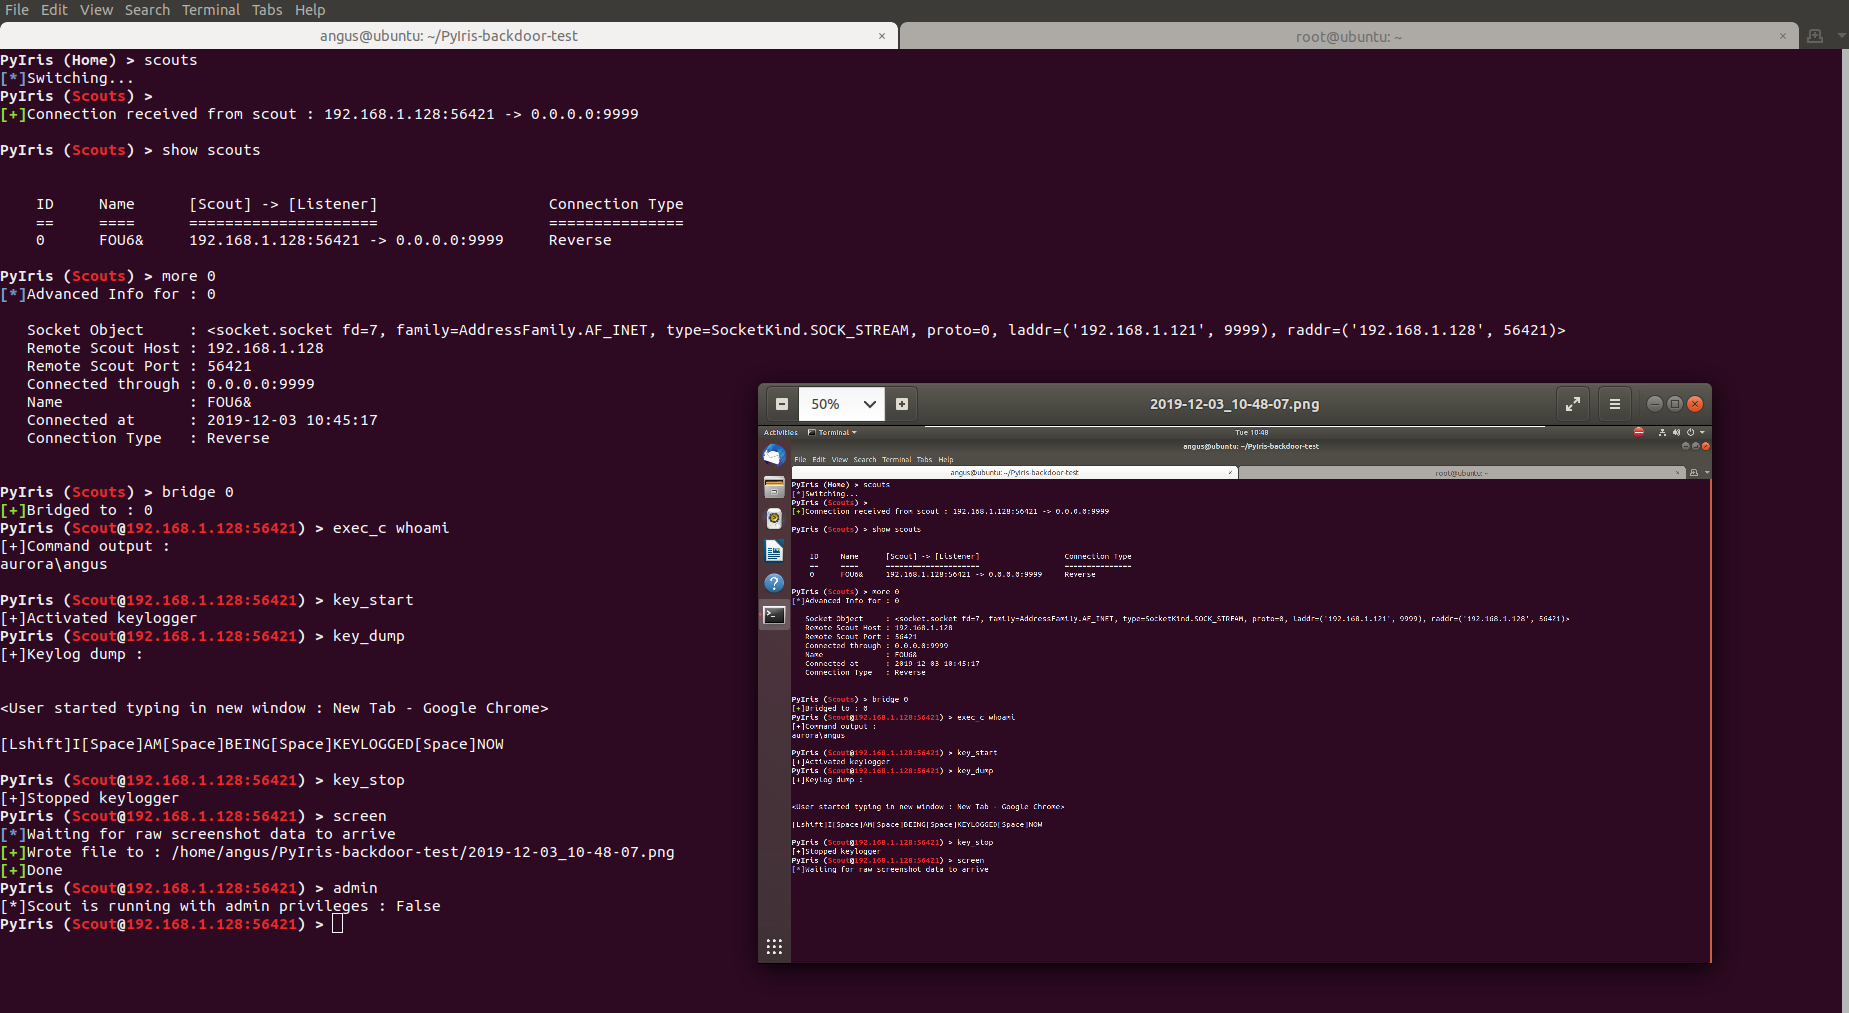
PyIris
 not-sekiun/pyiris
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
command-and-controlexploitationpayload-generation+4
3251 month ago
not-sekiun/pyirisPyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
 rvrsh3ll/rendezvousrat
Self-healing RAT utilizing libp2p
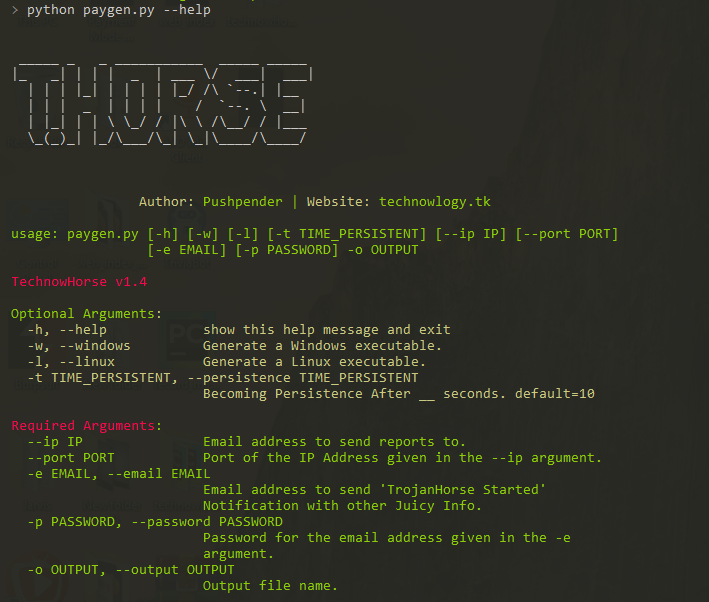 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
 dobin/antnium
A C2 framework for initial access in Go
 bishopfox/sliver
Adversary Emulation Framework
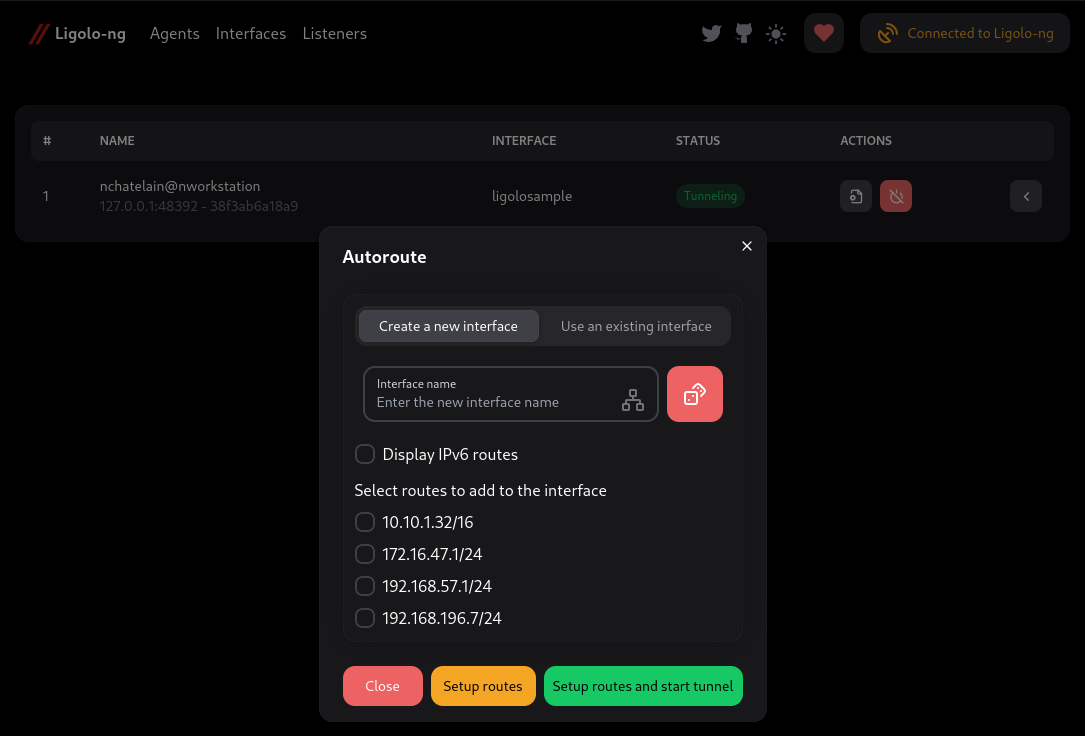 nicocha30/ligolo-ng
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 roccomuso/netrat
Damn easy multiplatform Node.js RAT generator.
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.