
Reverse_HTTPS_Bot
 ahhh/reverse_https_bot
A python based https remote access trojan for penetration testing
command-and-controlpayload-developmentpenetration-testing+3
84
ahhh/reverse_https_botA python based https remote access trojan for penetration testing
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 mwsrc/betterrat
Better Remote Access Trojan
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 jofpin/backcookie
Small backdoor using cookie.
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 demon-i386/zoshrinkc2
DNS over HTTPS targeted malware (only runs once)
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…

 rvrsh3ll/rendezvousrat
Self-healing RAT utilizing libp2p
 ahhh/ntp_trojan
Reverse NTP remote access trojan in python, for penetration testers
 nyan-x-cat/njrat-0.7d-stub-csharp
njRAT C# Stub - Fixed For PowerShell
 roccomuso/netrat
Damn easy multiplatform Node.js RAT generator.
 yschgroup/skyrat
SkyRAT - Powershell Remote Administration Tool
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 gsoffmarket/malvinci
This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…

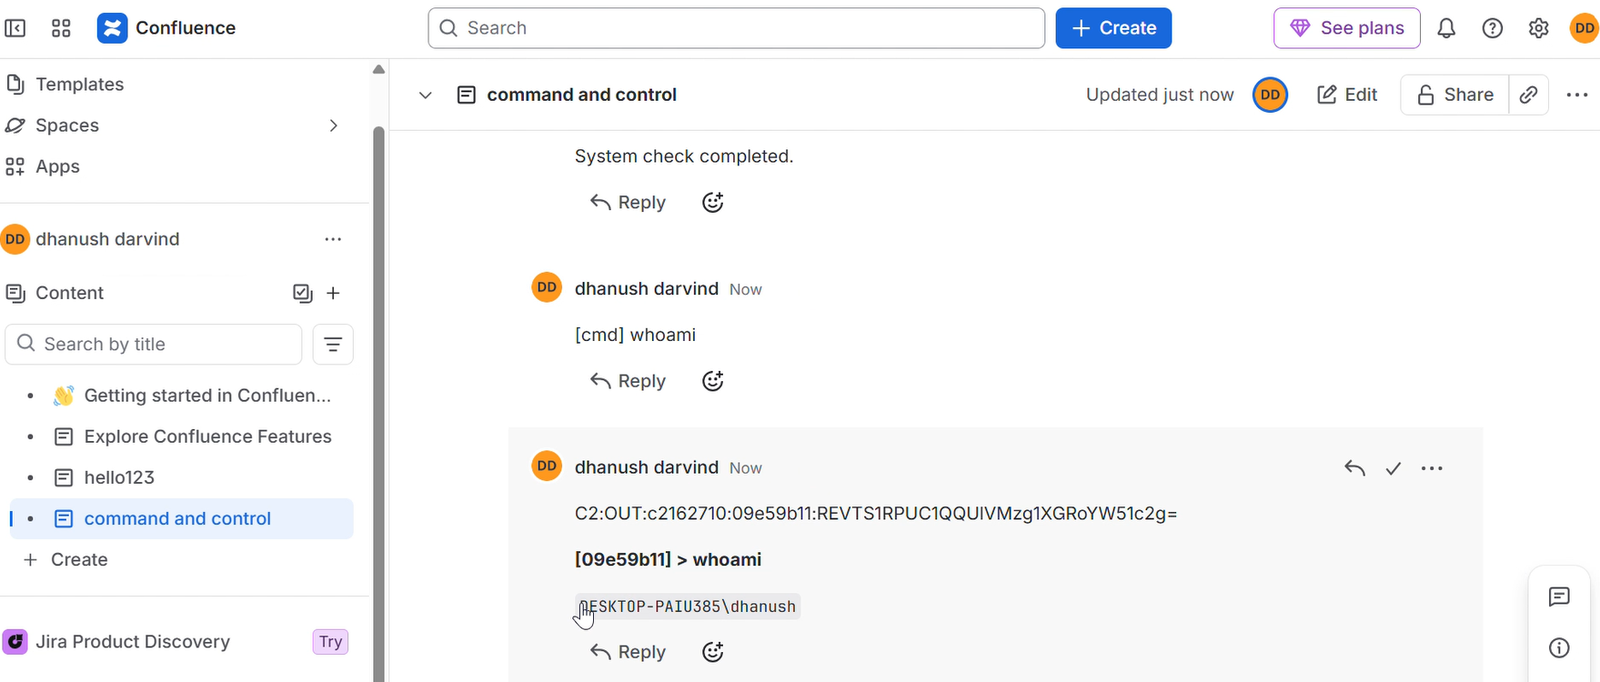 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.