
Archived
caldera-crater
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
command-and-controlpayload-developmentpenetration-testing+3
mitre/caldera-craterC# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
 cisco-talos/remcos-decoder
Talos Decryptor POC for Remcos RAT version 2.0.5 and earlier
 rapid7/metasploit-javapayload
Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.
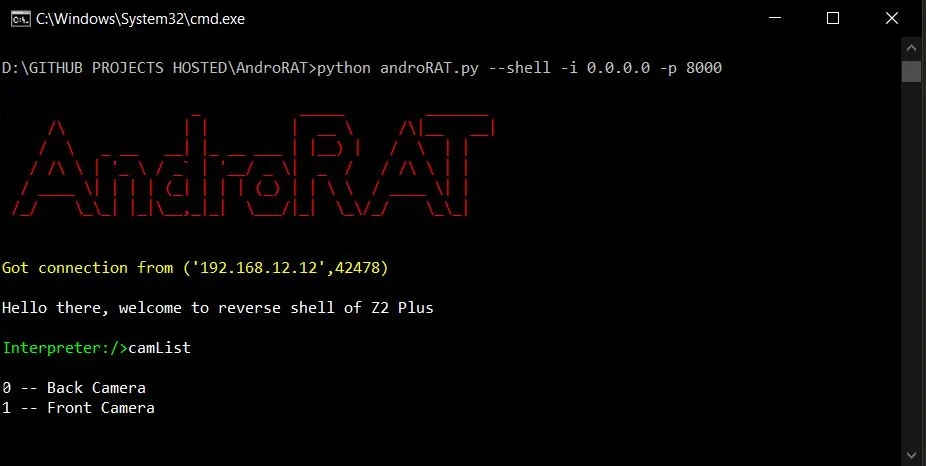 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 xsanflip/begal-c2
Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 bishopfox/sliver
Adversary Emulation Framework
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
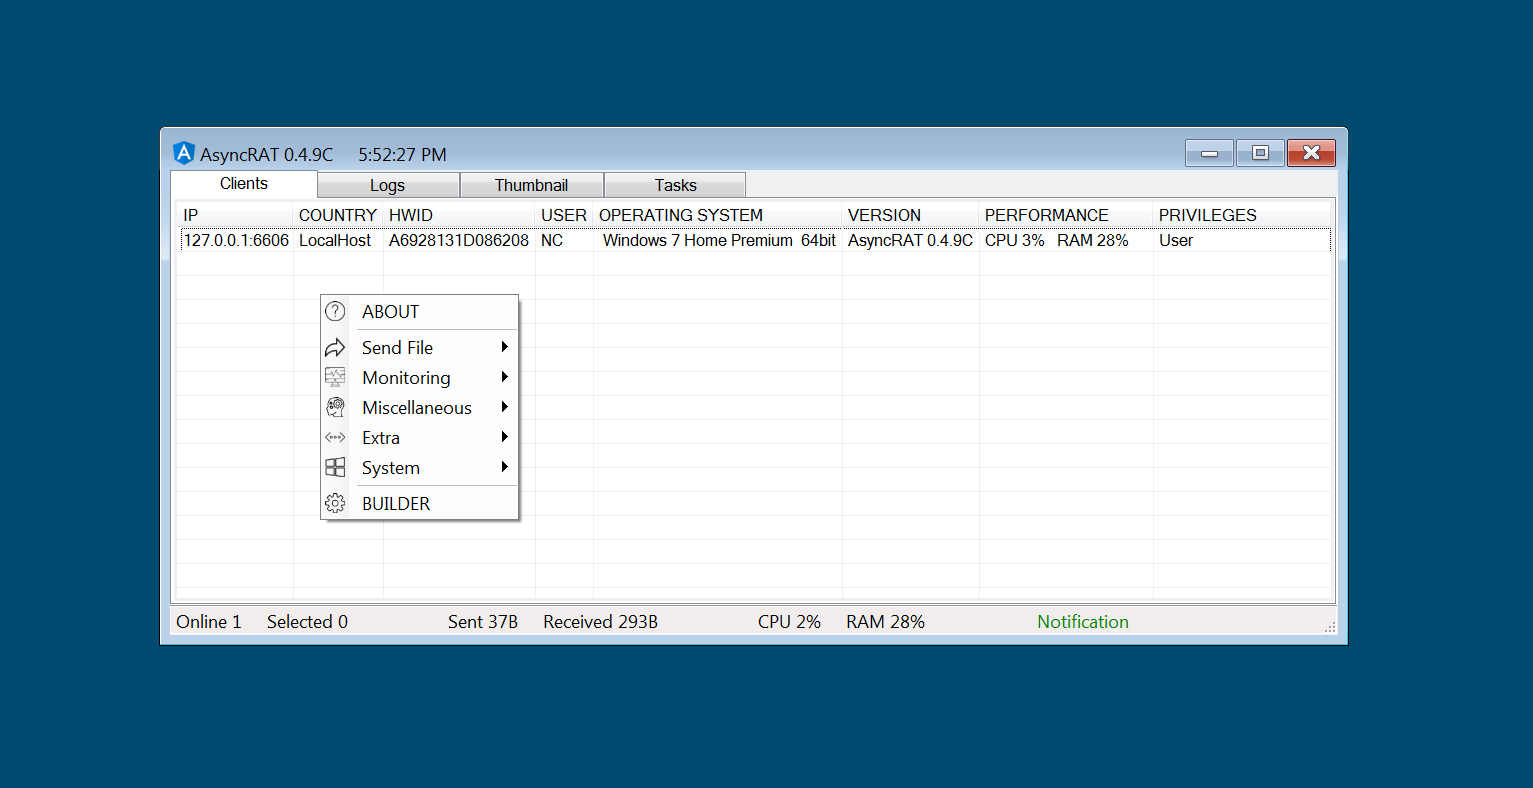 nyan-x-cat/asyncrat-c-sharp
Open-Source Remote Administration Tool For Windows C# (RAT)
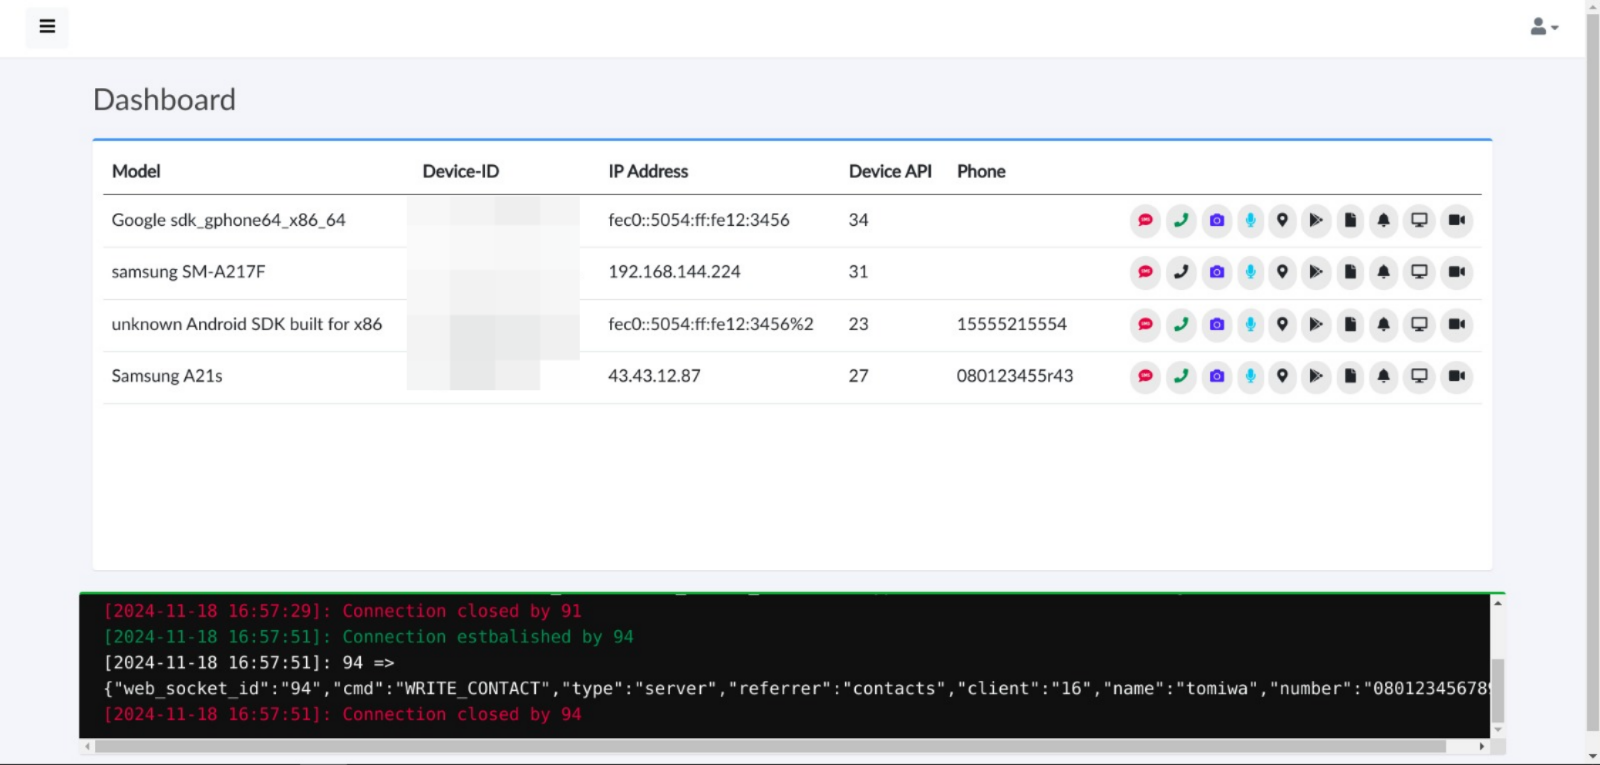 tomiwa-ot/moukthar
Android remote administration tool
 0xislamtaha/python-rootkit
Python Remote Administration Tool (RAT) to gain meterpreter session
 ilikenwf/darkagent
DarkAgent Remote Administration Tool RAT by DragonHunter
 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
 parsingteam/teleshadow2
TeleShadow - Telegram Desktop Session Stealer (Windows)
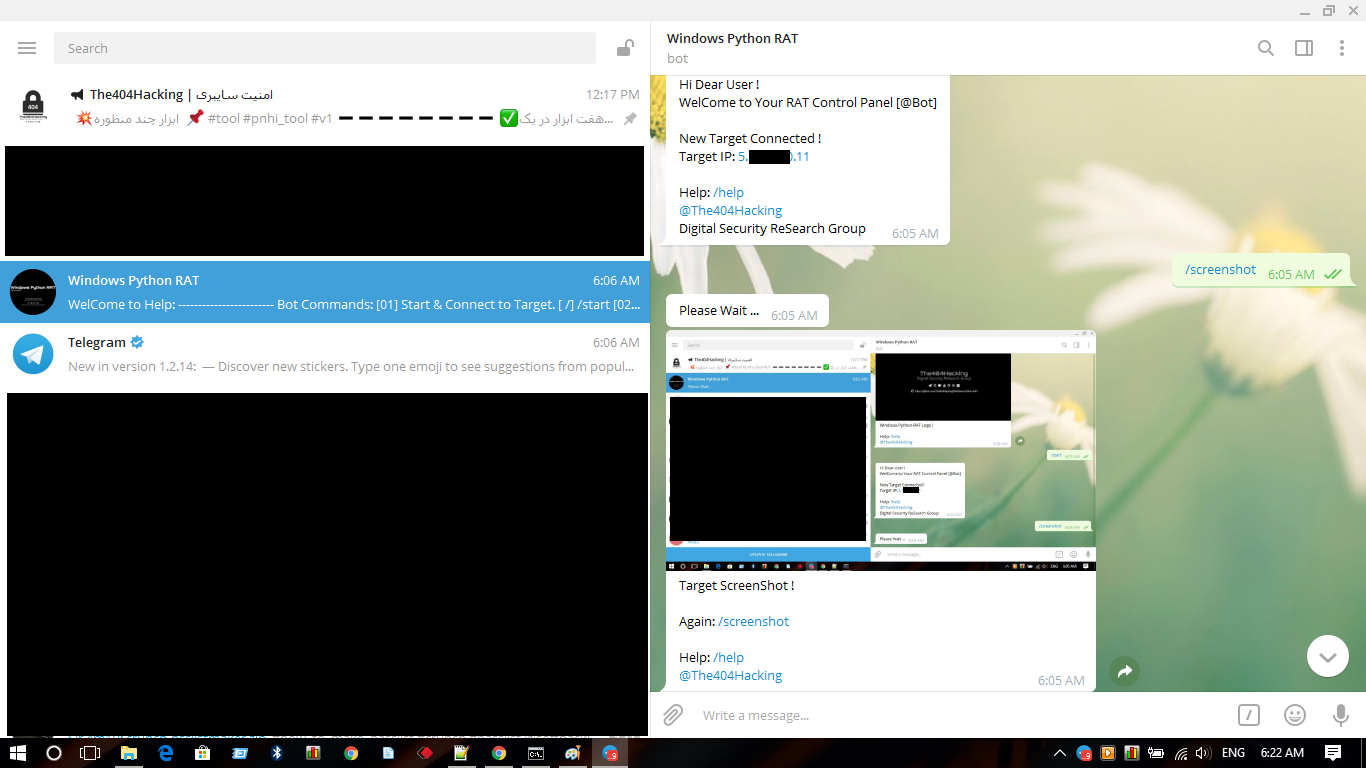 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 stphivos/rat-shell
Windows Remote Access Trojan (RAT)
 roccomuso/netrat
Damn easy multiplatform Node.js RAT generator.
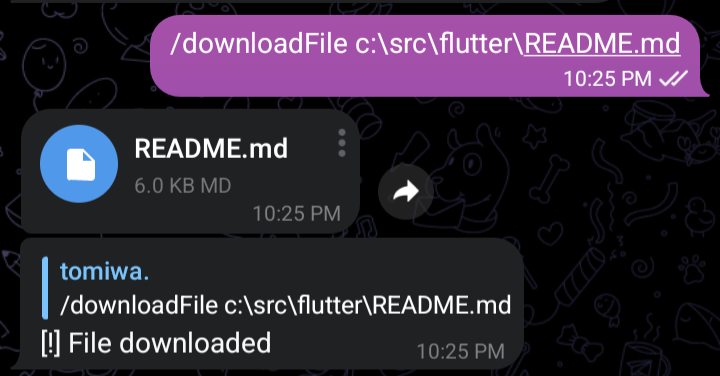 tomiwa-ot/telegram-c2
Control a system remotely via telegram