

TornadoC2
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
command-and-controlcryptographyids-ips-evasion+9
34
kamalx06/tornadoc2Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 correcthorsebatterystaple-sudo/orwell-rat-and-botnet
Orwell is a RAT and Botnet designed as a trio of programs.
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
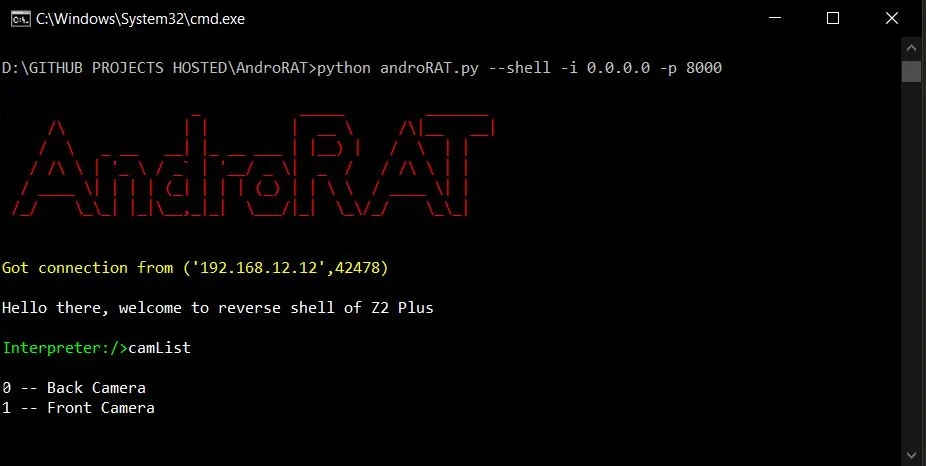 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 bishopfox/sliver
Adversary Emulation Framework
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
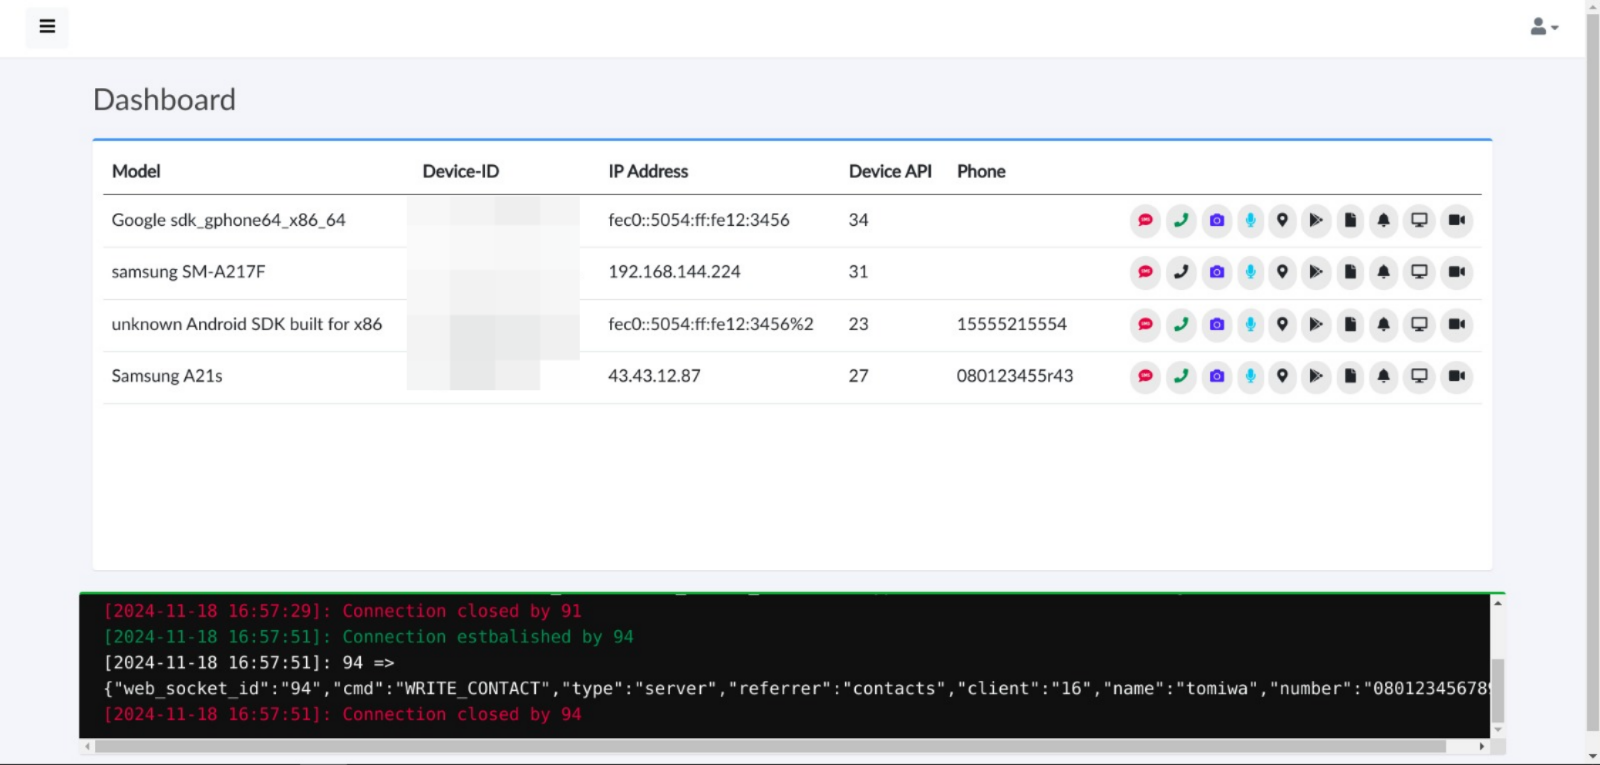 tomiwa-ot/moukthar
Android remote administration tool
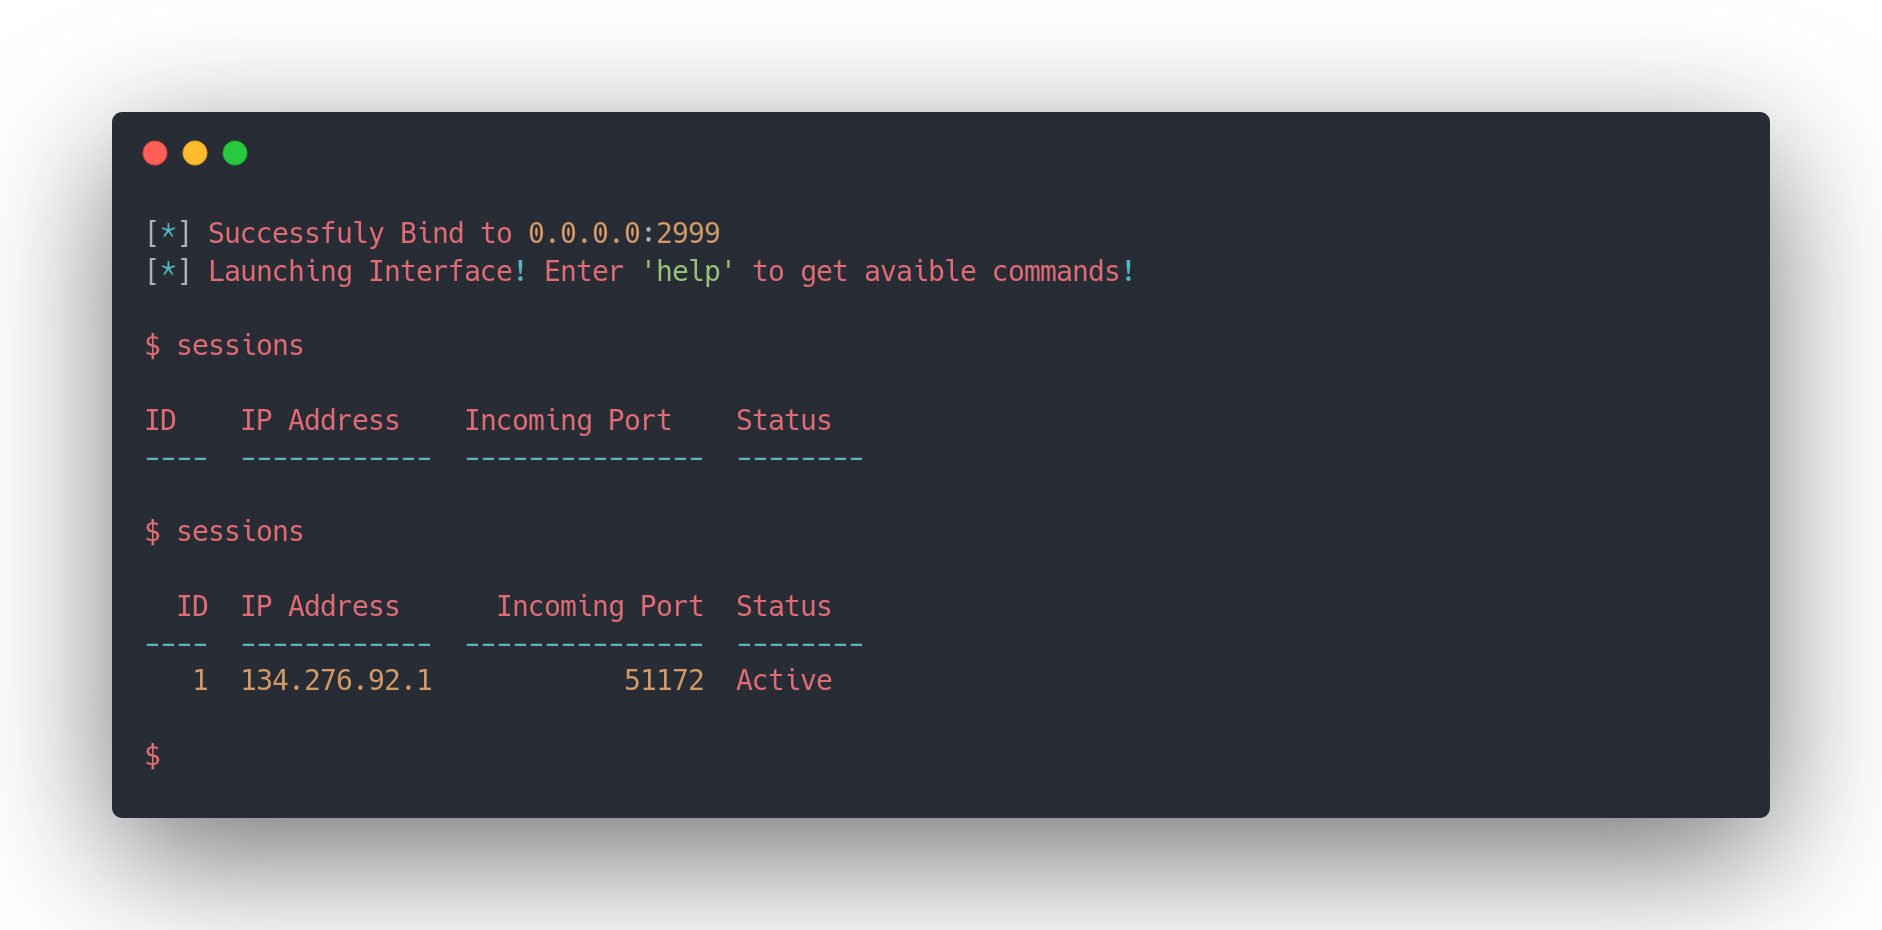 hash3lizer/sillyrat
A Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️
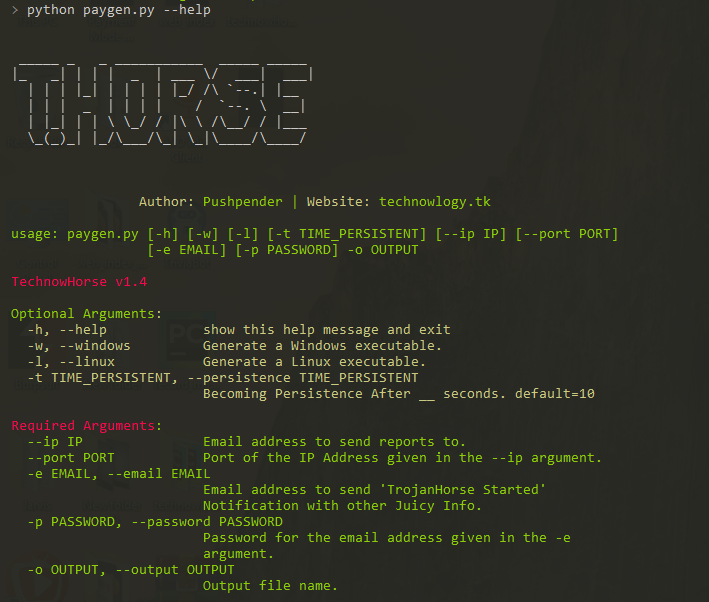 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 rvrsh3ll/rendezvousrat
Self-healing RAT utilizing libp2p
 dobin/antnium
A C2 framework for initial access in Go
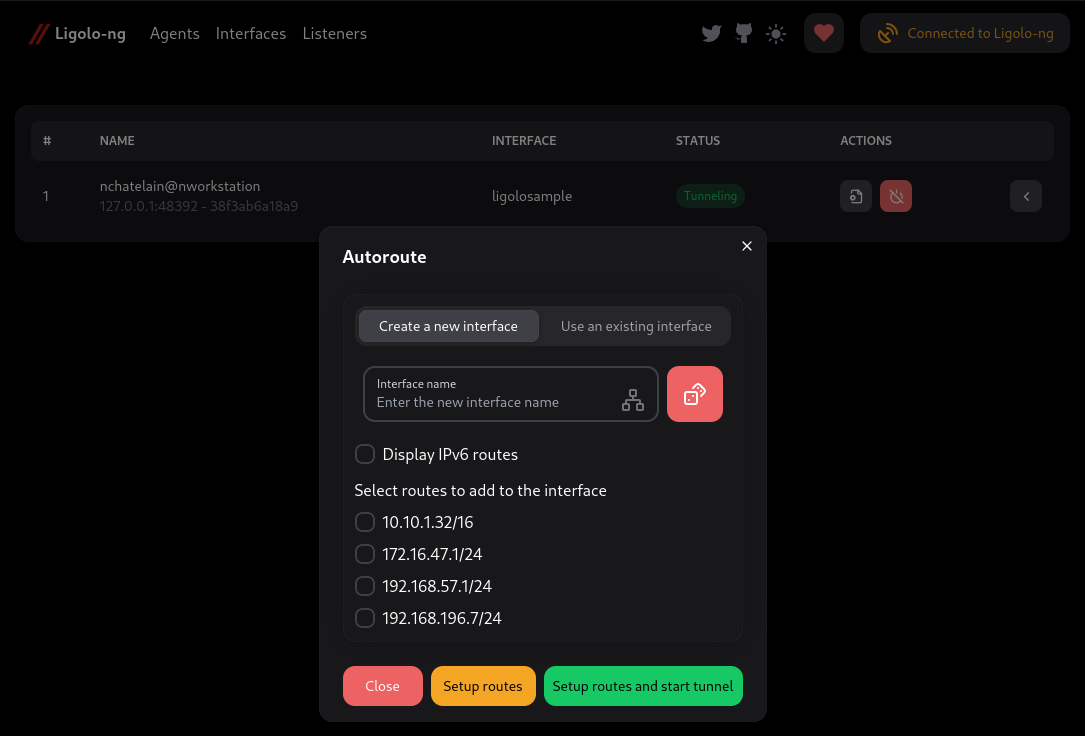 nicocha30/ligolo-ng
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 machine1337/pyfud
CROSS PLATFORM REMOTE ACCESS TROJAN (RAT)
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.