

FUD-C2-Framework
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
8
x3r0day/fud-c2-frameworkA fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 danithehack3r/cve-2023-38646
Exploit for CVE-2023-38646 in Metabase 0.46.6, enabling remote code execution via crafted requests and setup token retrieval.
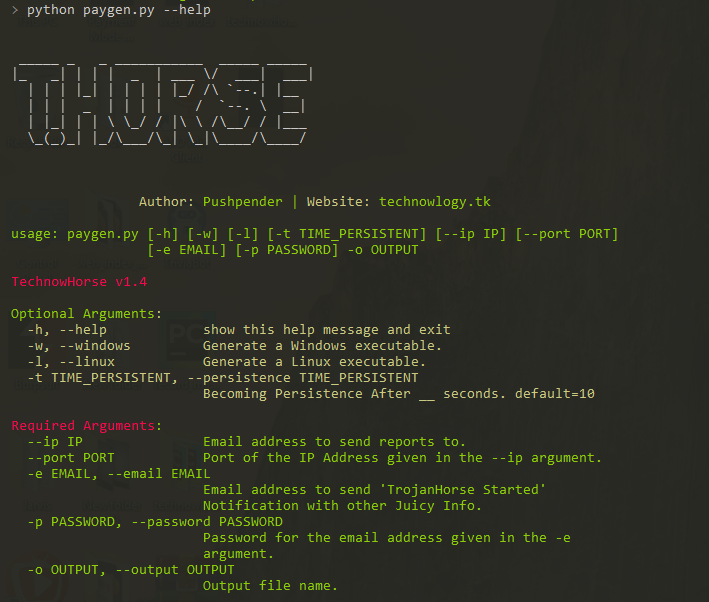 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 retrobyte/shadowtech-rat
An example of a remote administration tool.
 alanbaumgartner/aurora
Aurora Remote Administration Tool
 grisuno/blacksandbeacon
Linux C2 beacon with native in-memory ELF BOF loader, AES-256-CFB encrypted polling, and a Python C2 server for fileless post-exploitation modules.
 cisco-talos/remcos-decoder
Talos Decryptor POC for Remcos RAT version 2.0.5 and earlier
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.

 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
 qwqdanchun/dcrat
A simple remote tool in C#.
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 mr-un1k0d3r/thundershell
Python / C# Unmanaged PowerShell based RAT
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
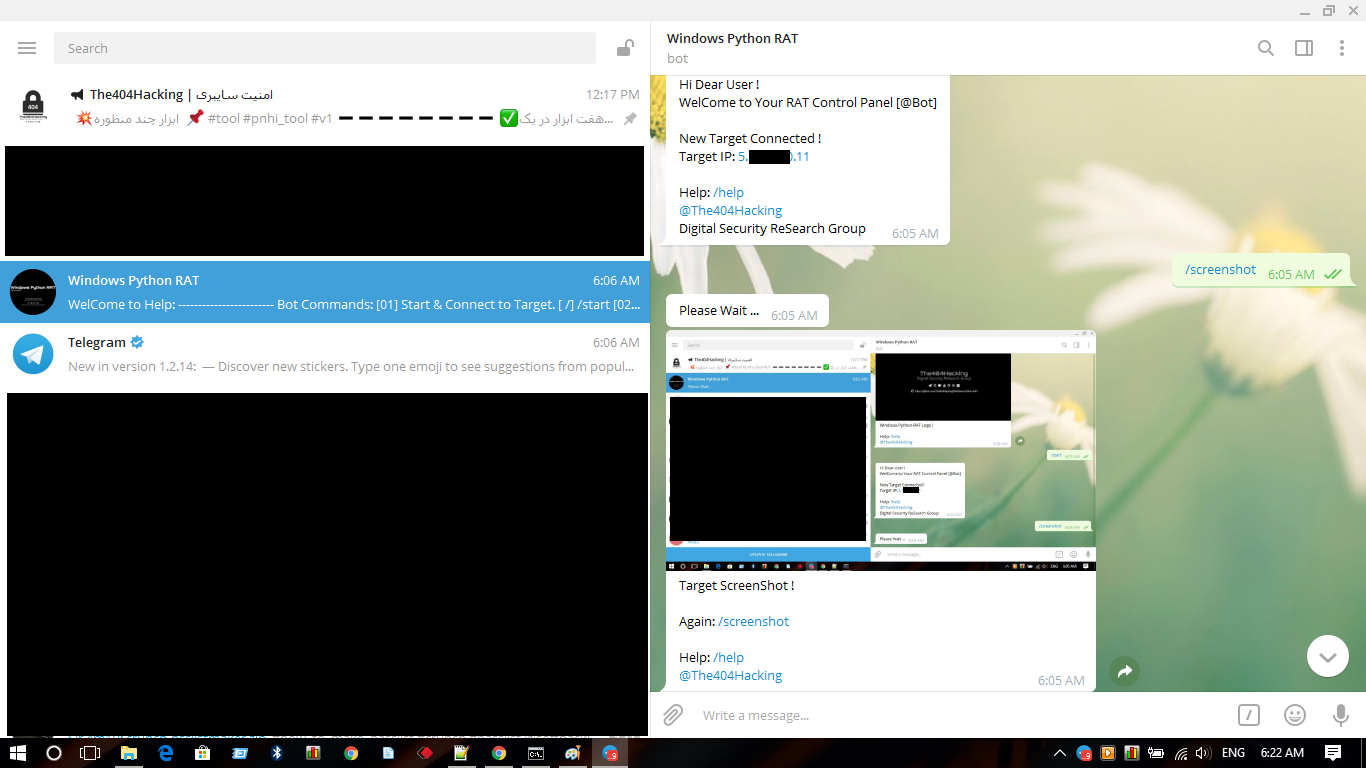 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.