AhsayCBS-Auth-Bypass-RCE
 horizon3ai/ahsaycbs-auth-bypass-rce
A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
authenticationexploitationpayload-development+5
4
horizon3ai/ahsaycbs-auth-bypass-rceA proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 simoesctt/ctt-enhanced-cve-2026-46339-exploit-engine
Python framework exploiting CVE-2026-46339 for unauthenticated RCE on 9Router via MCP bridge, using temporal sharding and dispersion to evade…
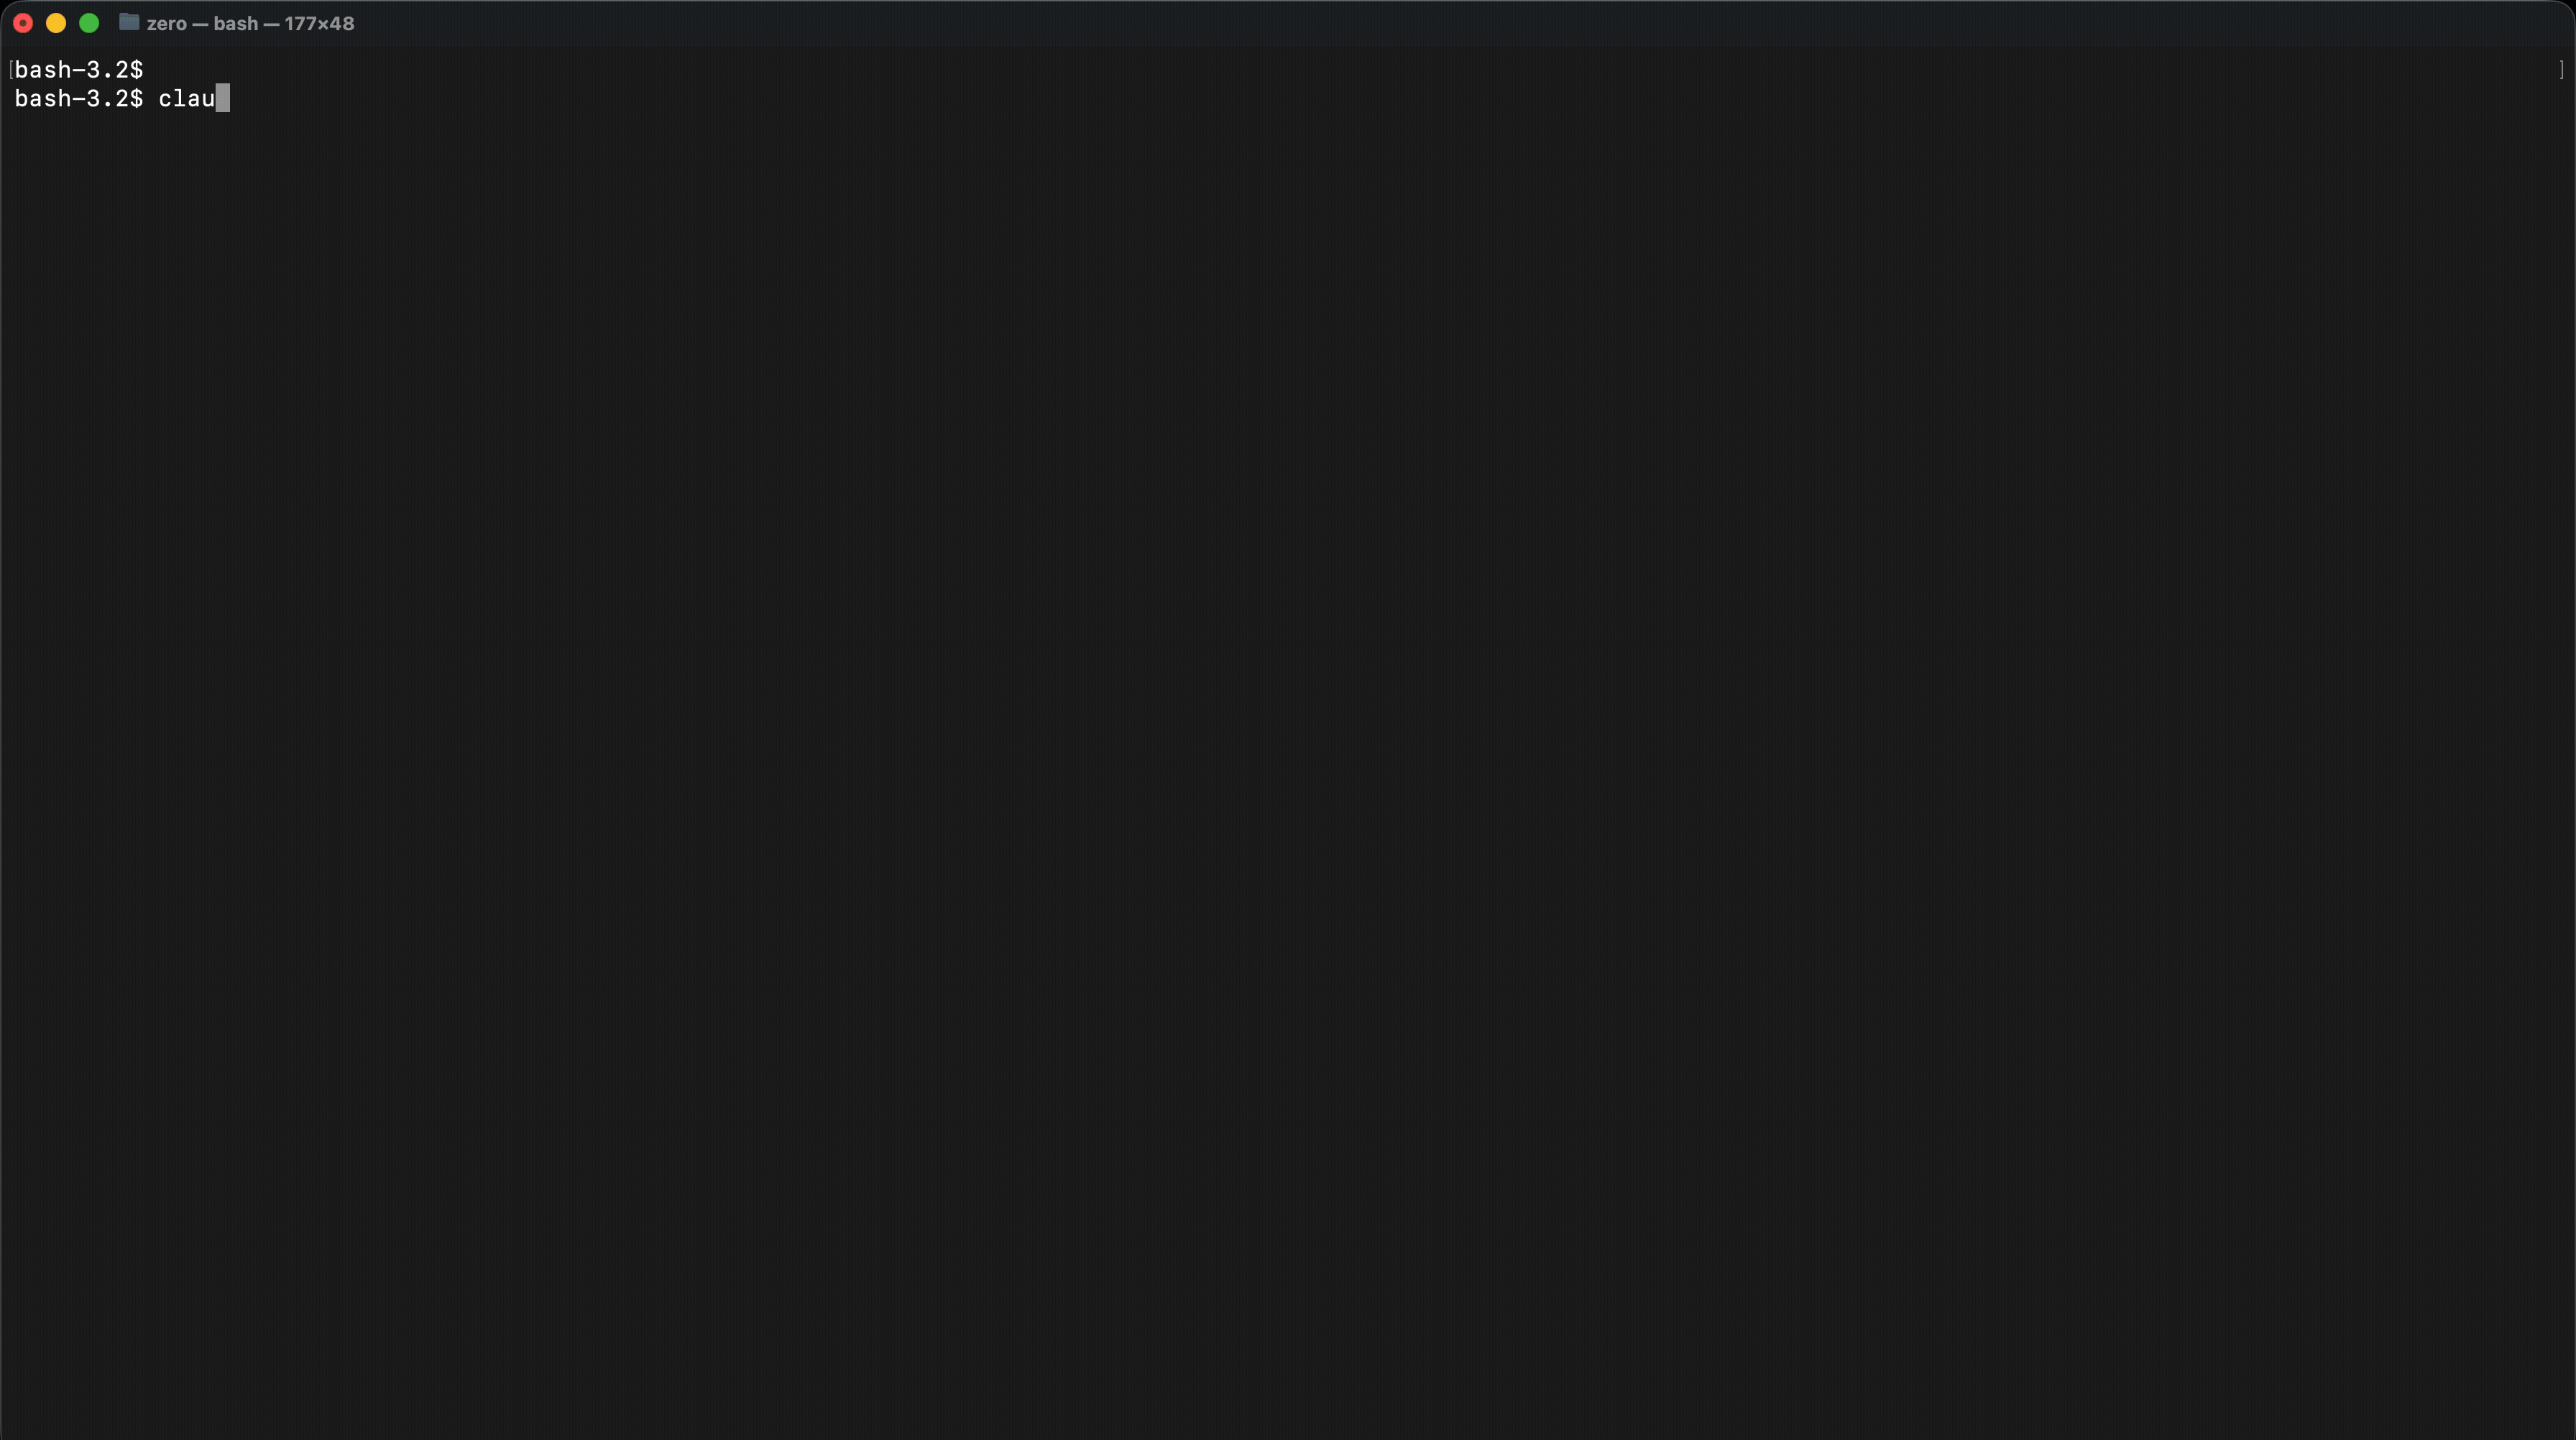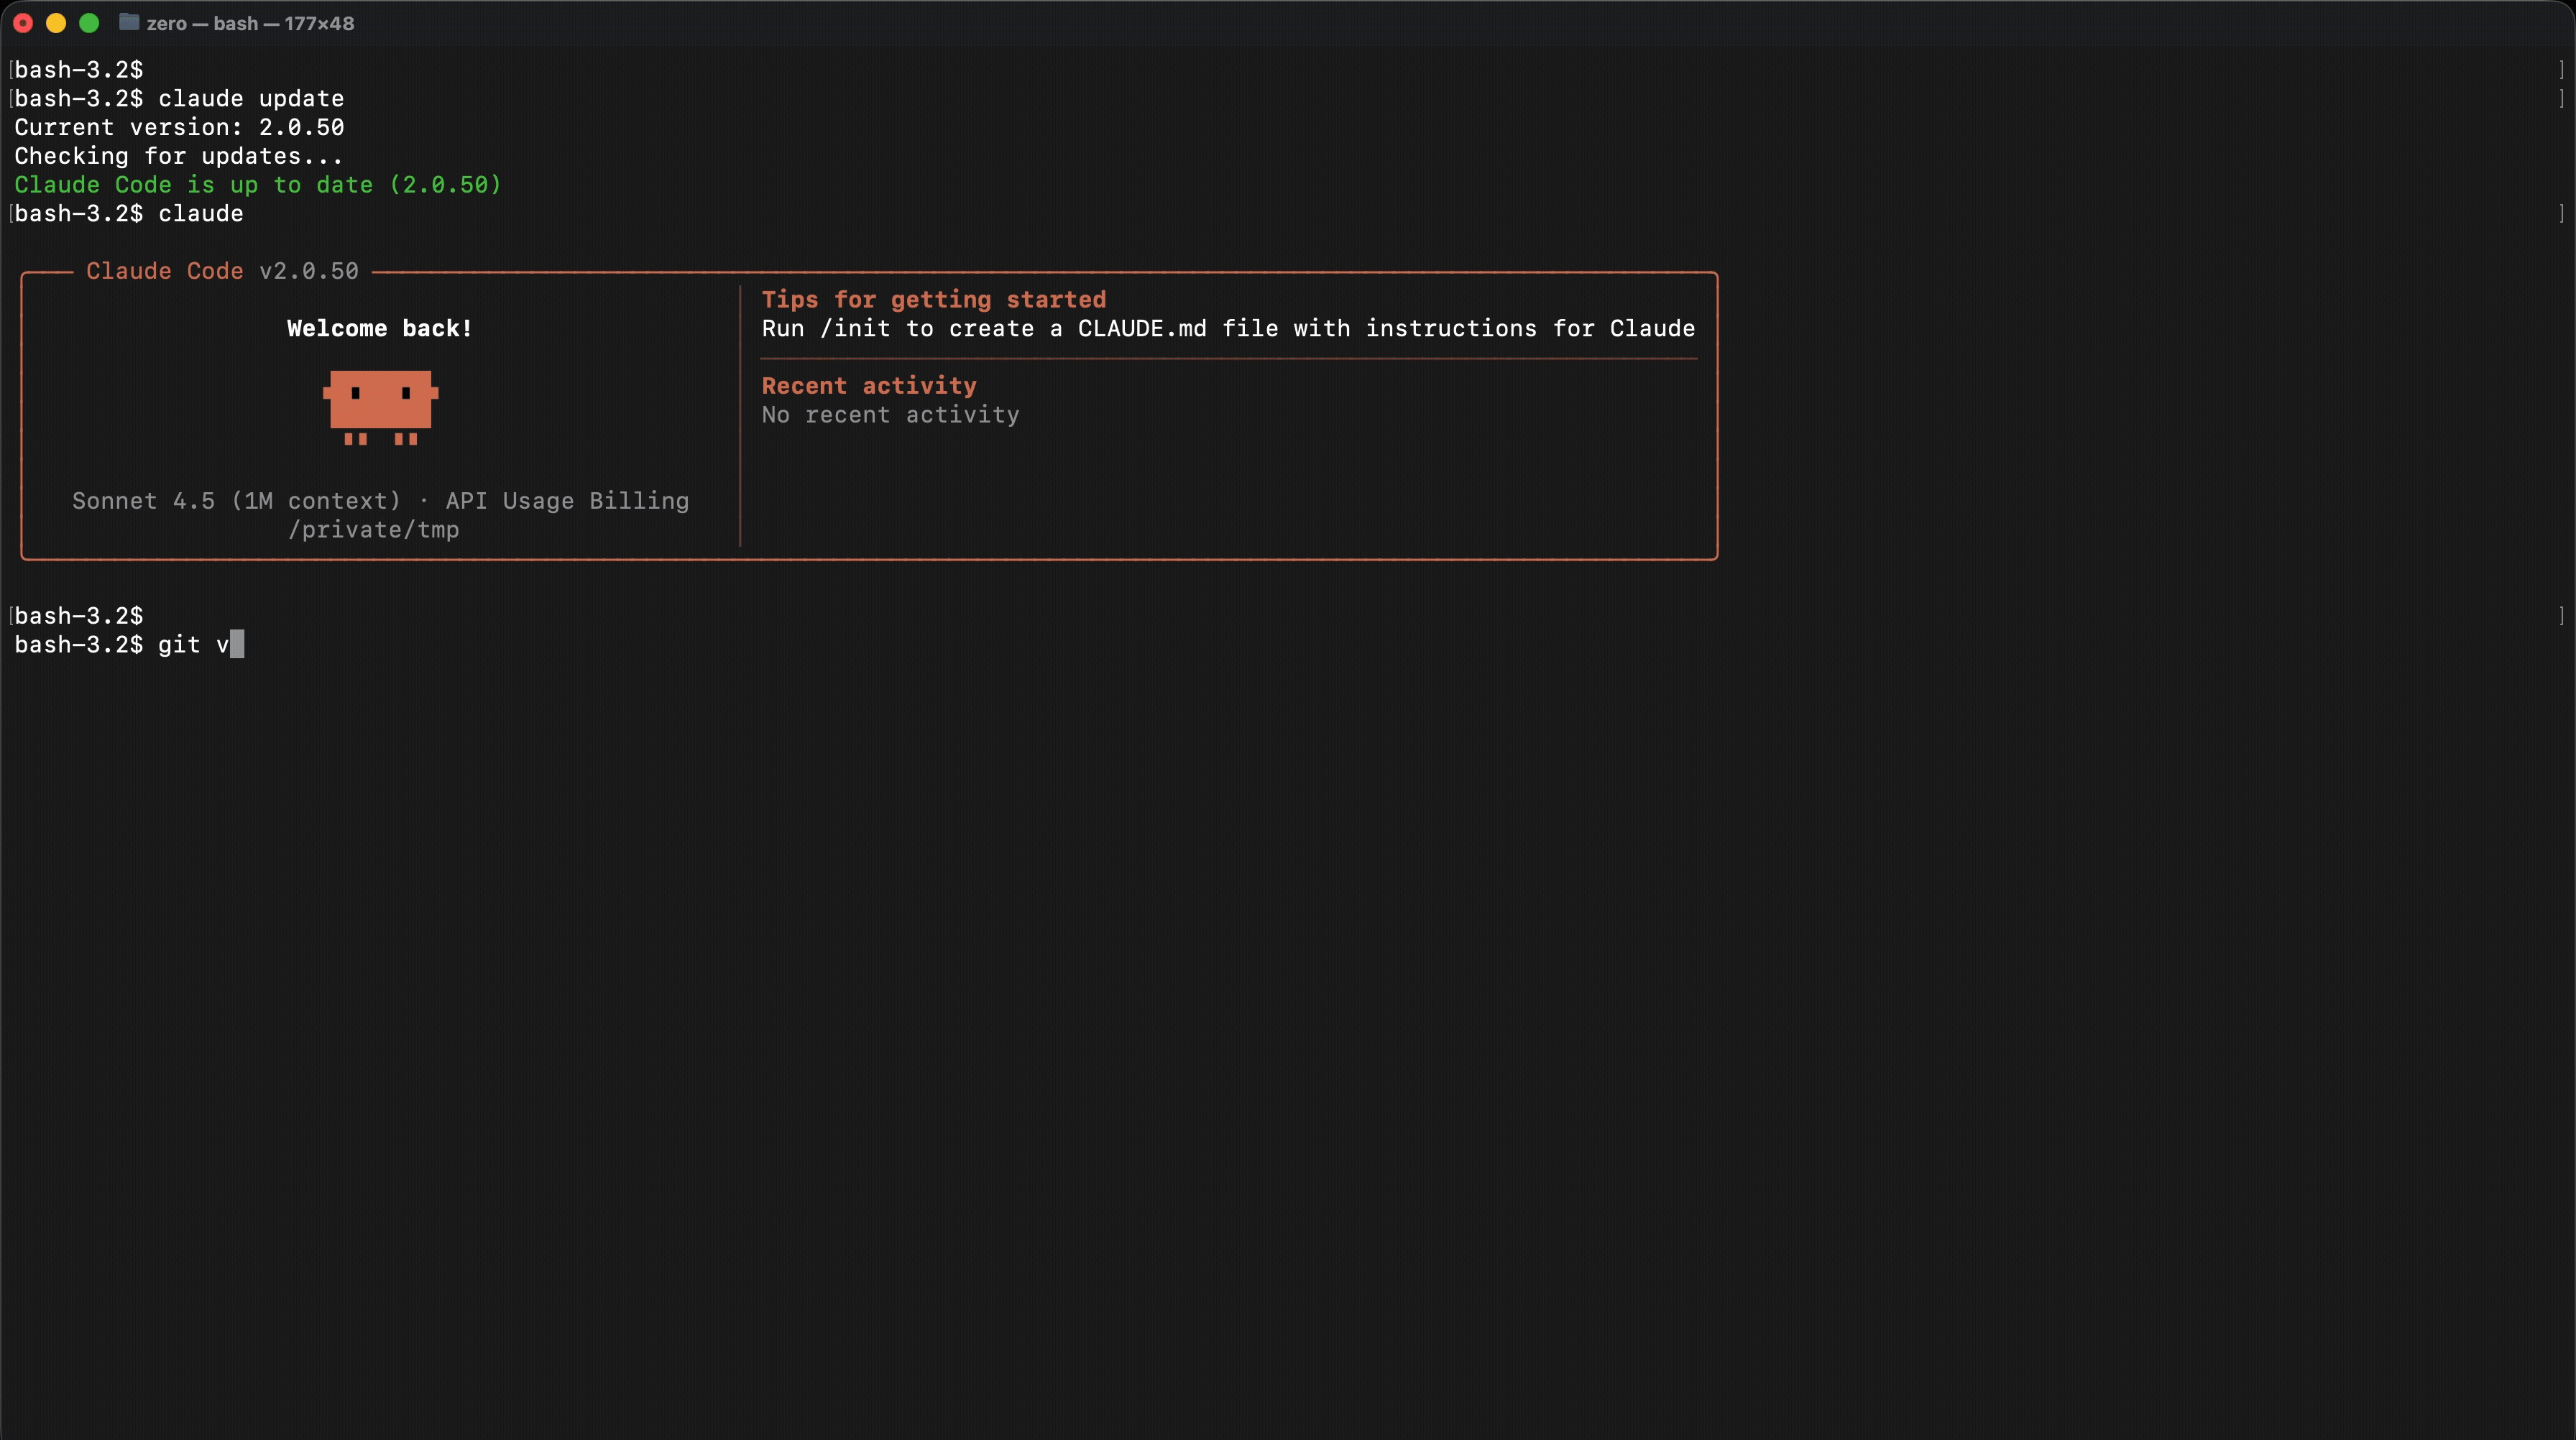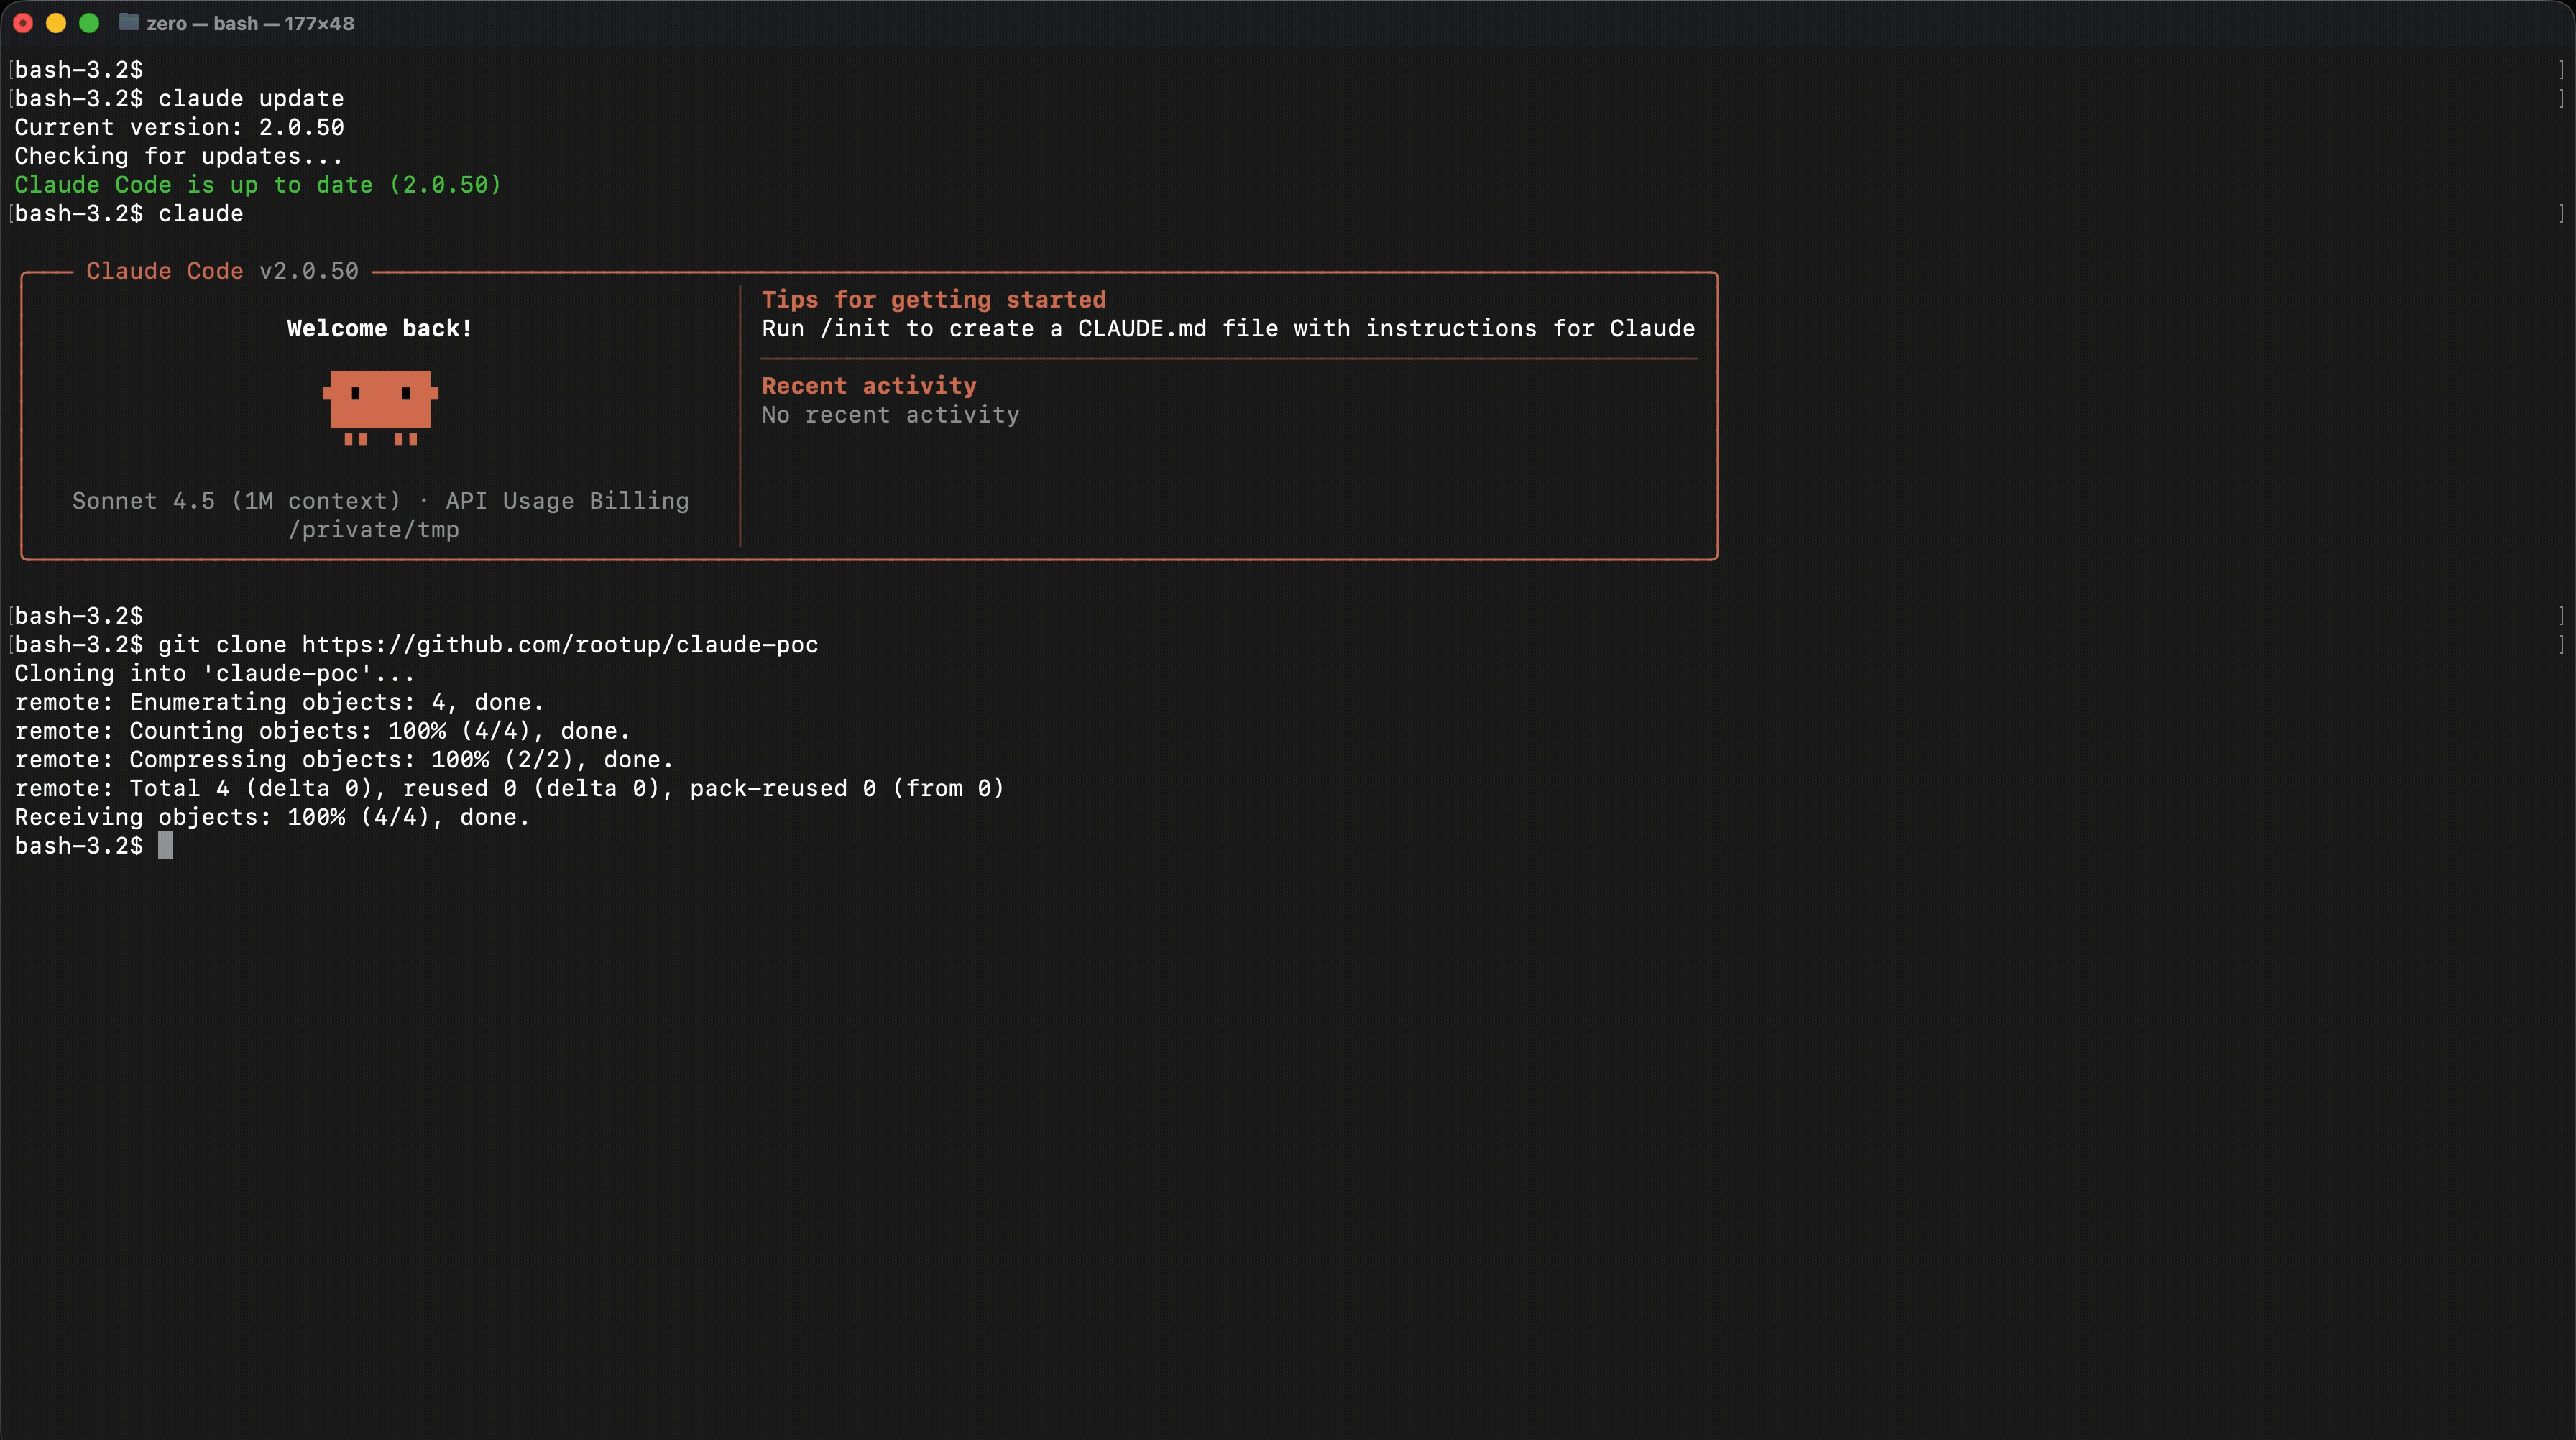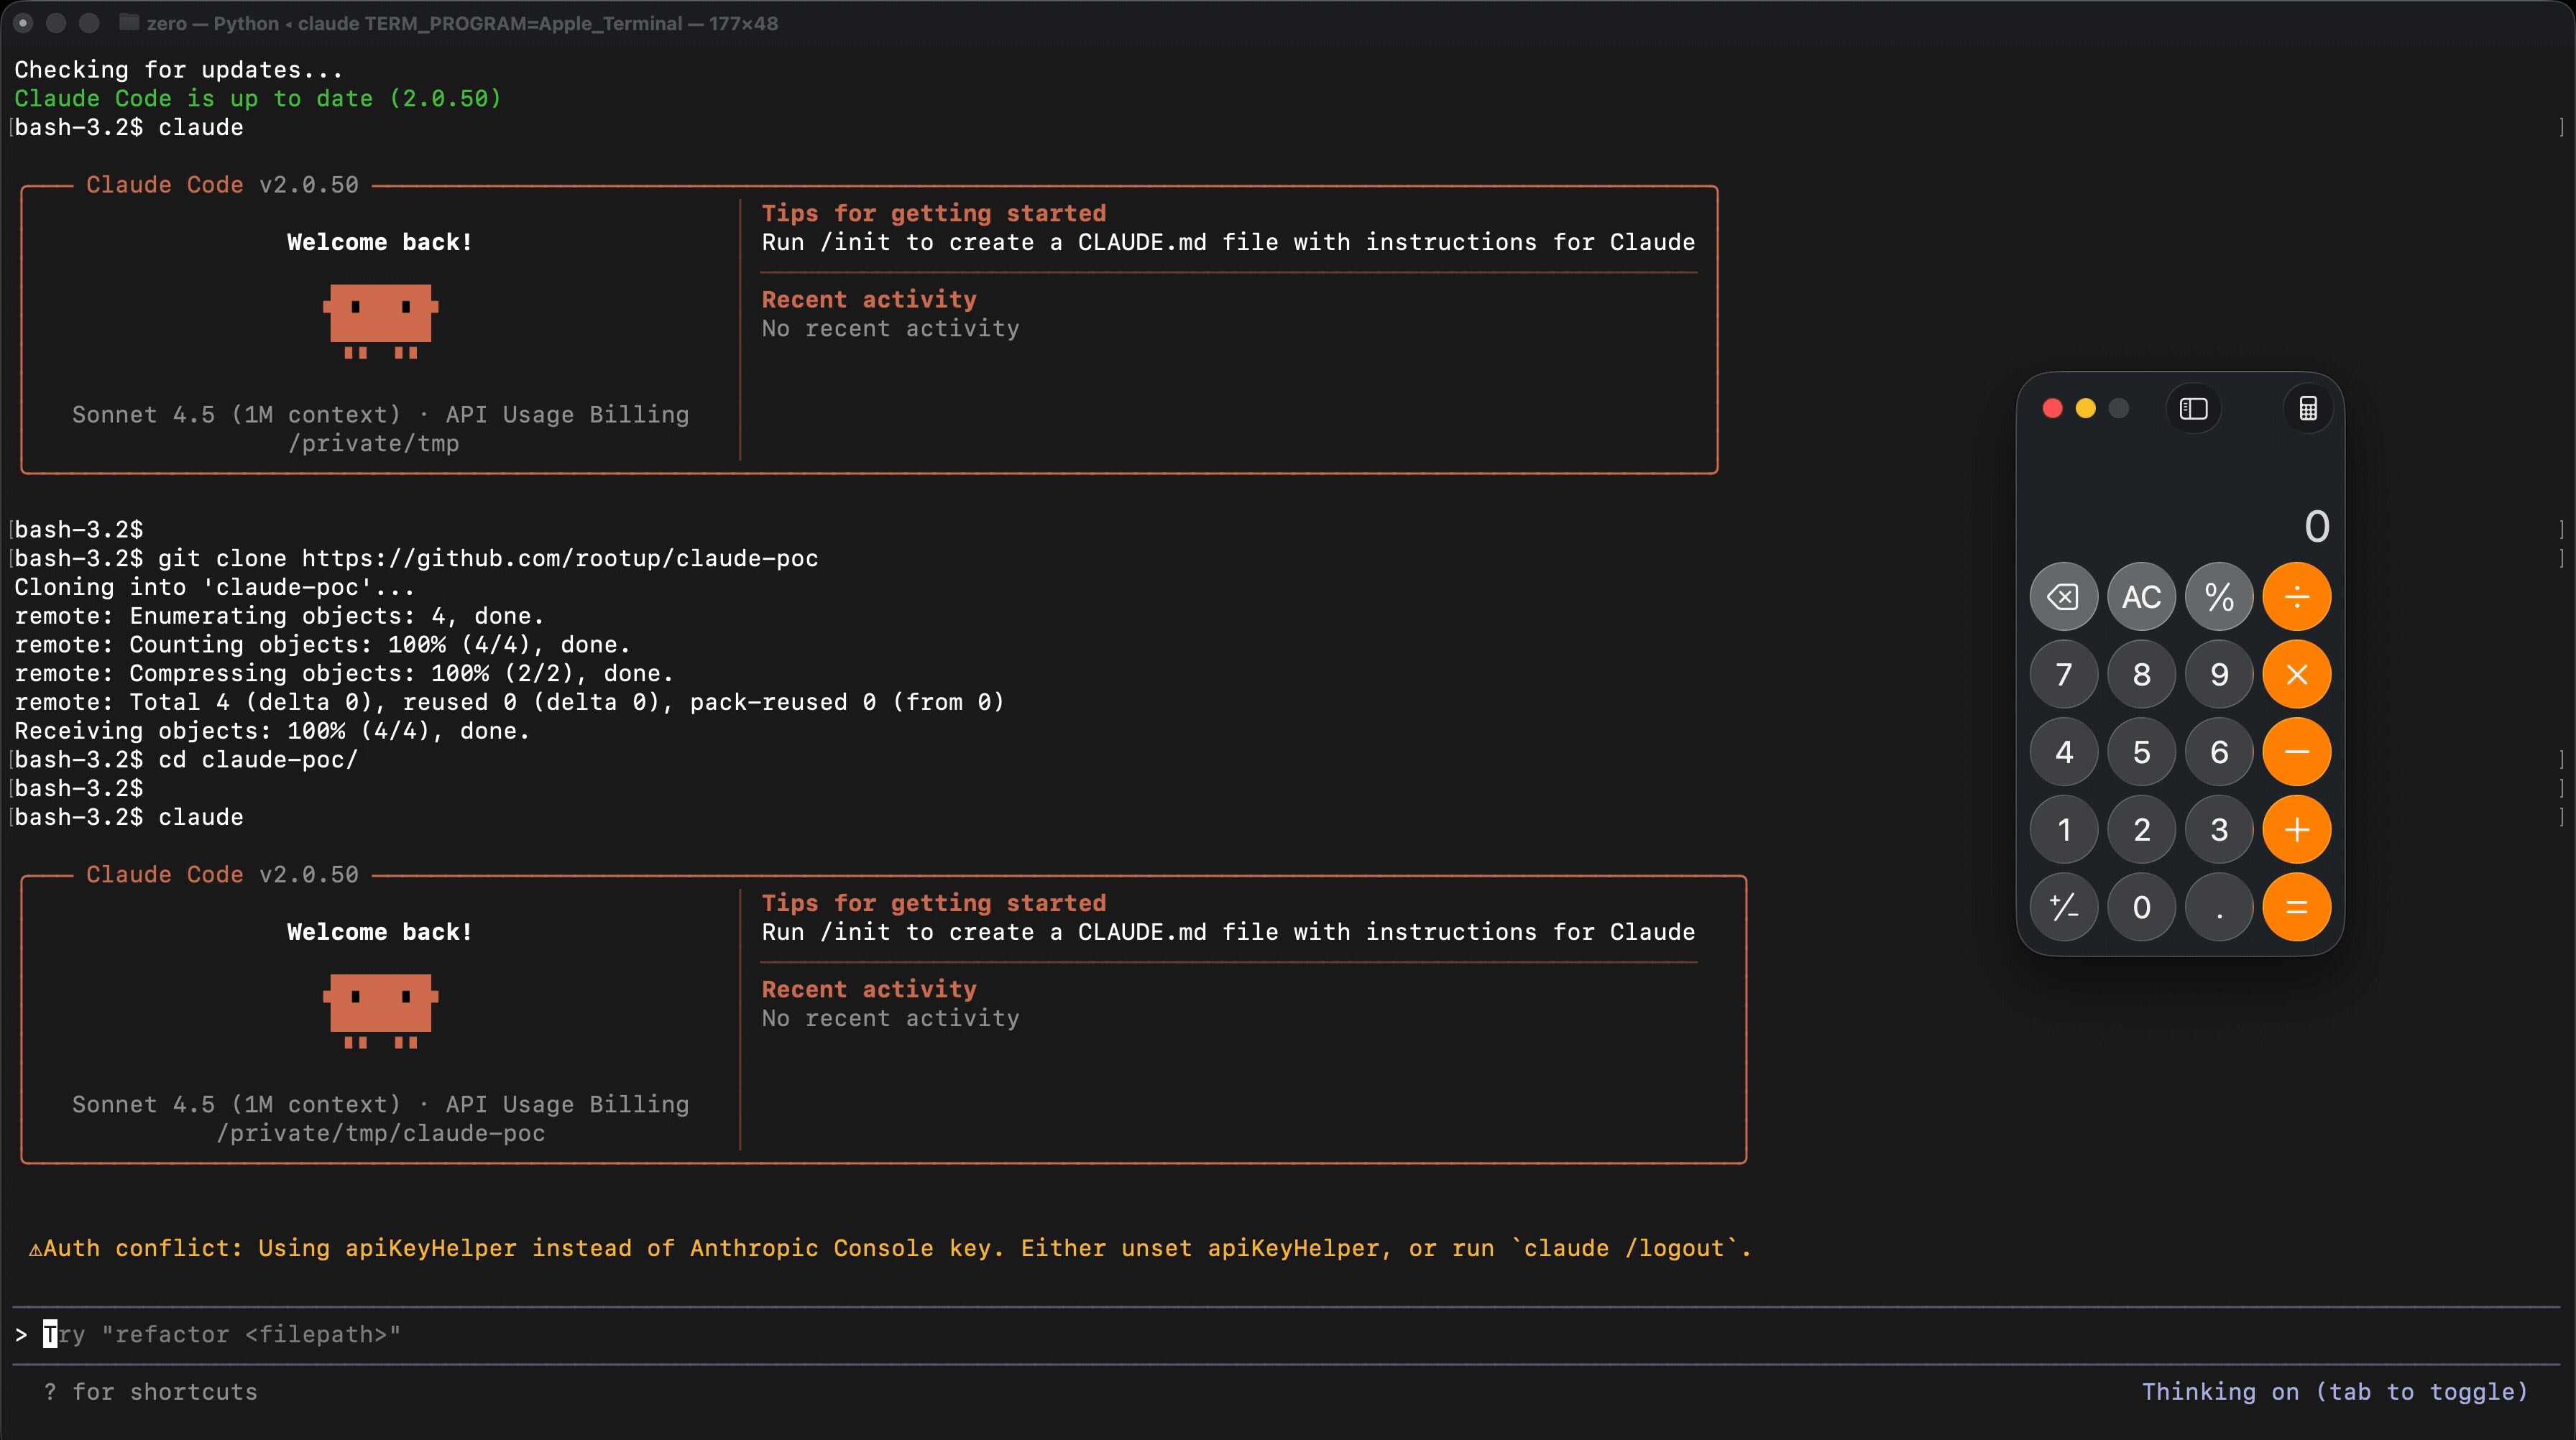 rootup/claude-poc
Claude Code Remote Code Execution
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
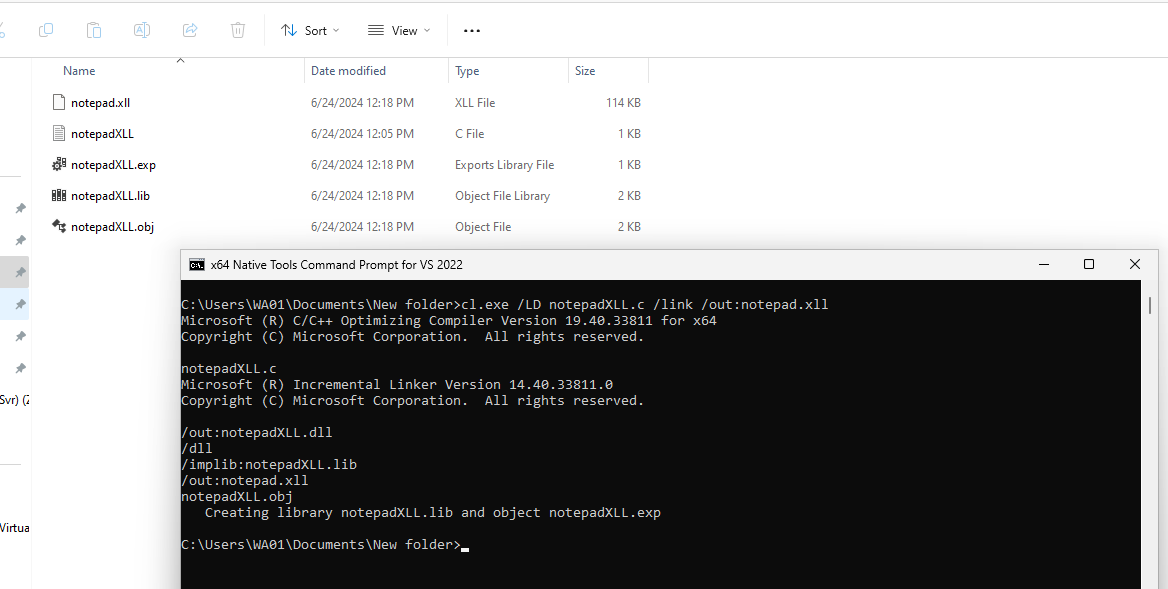 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 chebuya/cve-2024-30850-chaos-rat-rce-poc
CHAOS RAT web panel path RCE PoC
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
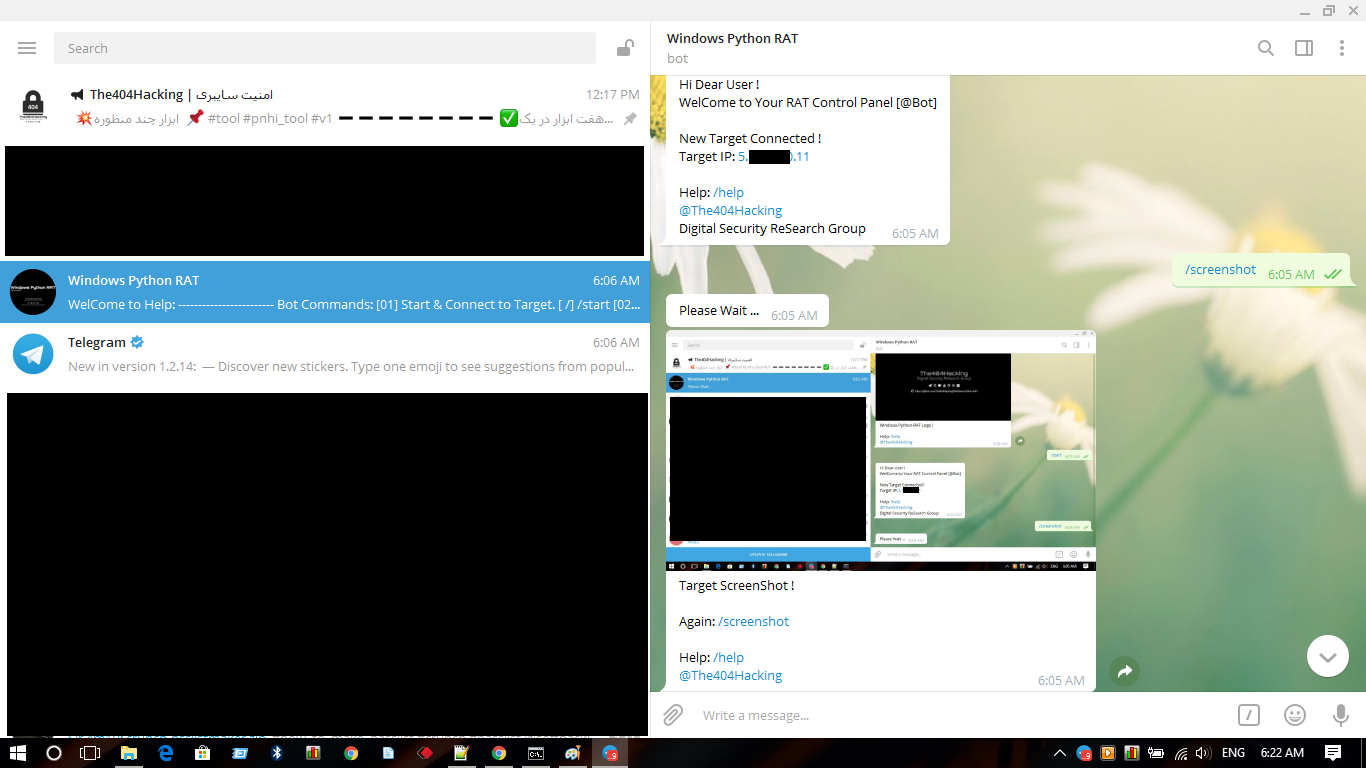 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 ianxtianxt/teamview
Generates TeamViewer ID and password payloads for remote access to target machines. Combines executable generation with third-party remote control…