metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Linux C2 beacon with native in-memory ELF BOF loader, AES-256-CFB encrypted polling, and a Python C2 server for fileless post-exploitation modules.

Single-file Python tool that fingerprints SonicWall SMA1000 Work Place appliances, probes and confirms the pre-auth SSRF (CVE-2026-83548) via…

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…

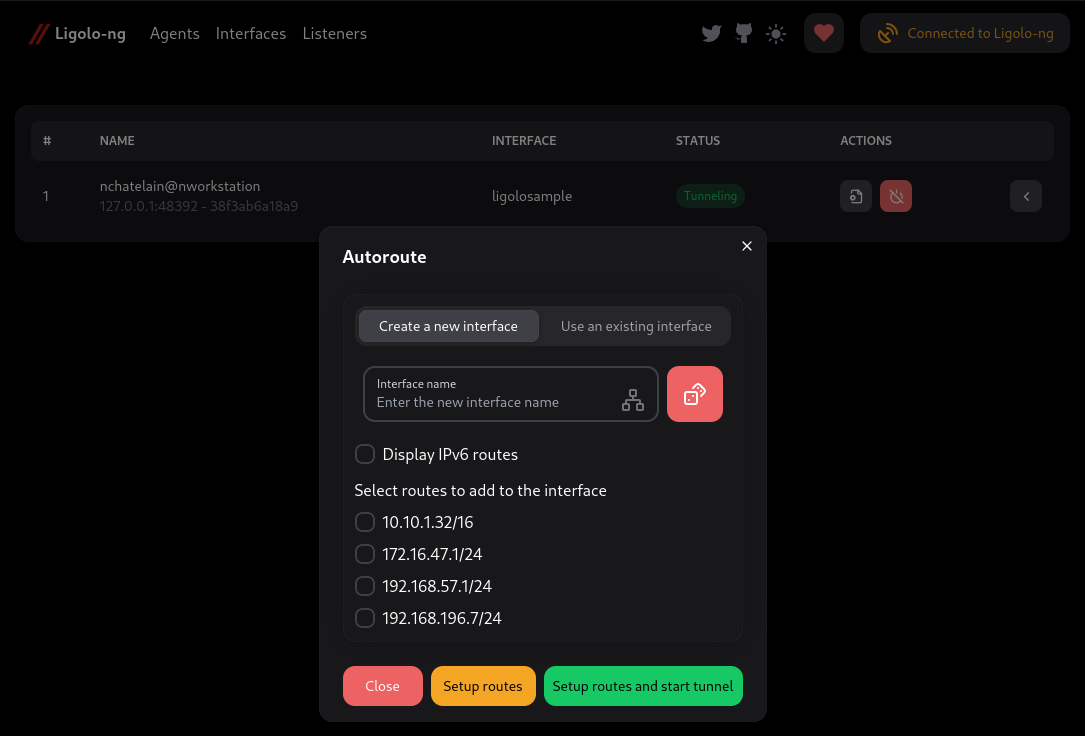
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.

AdaptixC2 is a highly modular advanced redteam toolkit

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

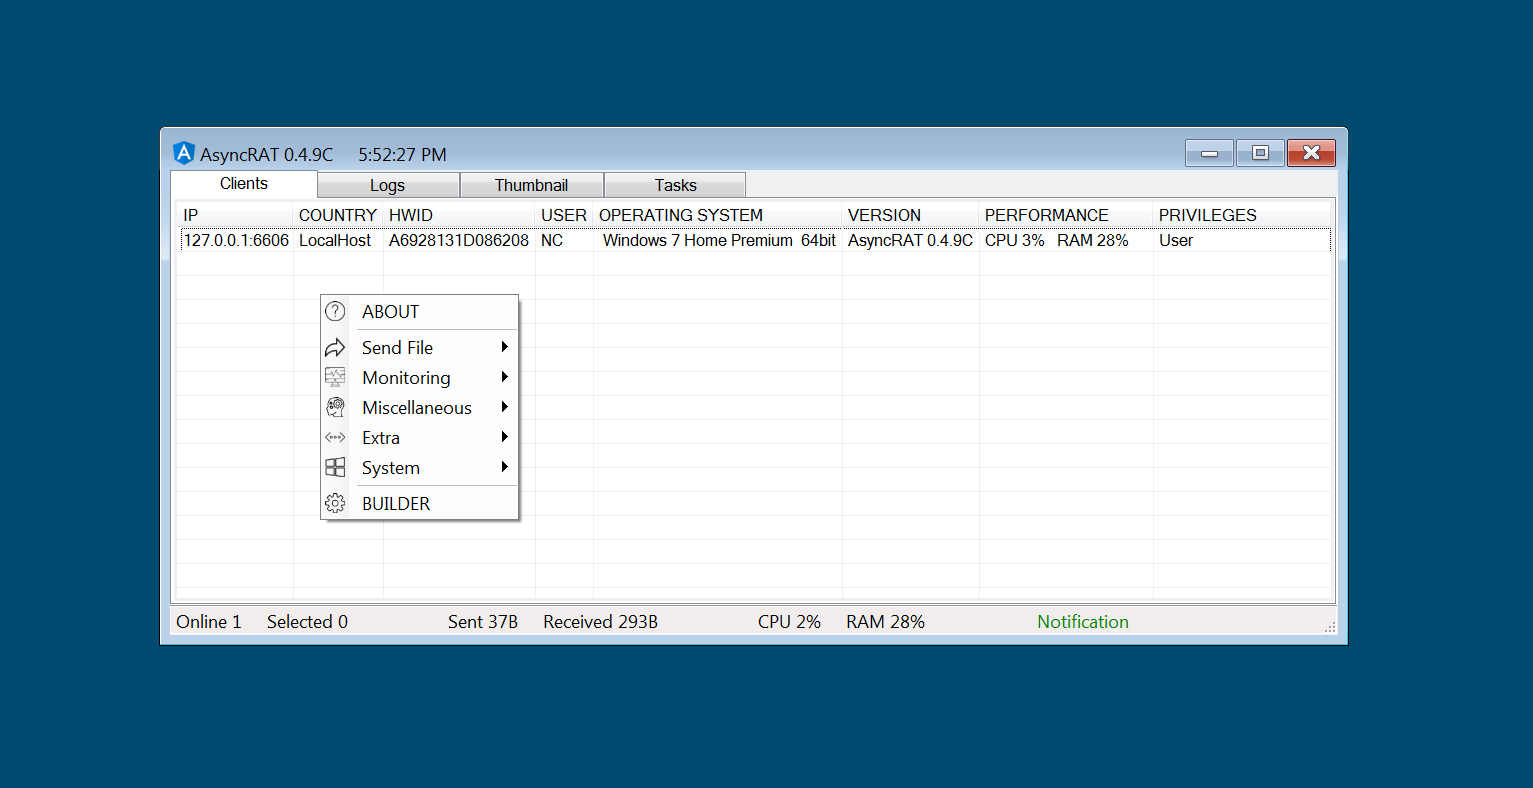
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…

ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…

CROSS PLATFORM REMOTE ACCESS TROJAN (RAT)

Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)

🔥 CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems.

A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side

Exploitation tool for CVE-2023-22527 targeting Confluence servers, enabling remote code execution with support for multiple targets, concurrency, and…

Open-Source Remote Administration Tool For Windows C# (RAT)

Exploit for CVE-2023-38646 in Metabase 0.46.6, enabling remote code execution via crafted requests and setup token retrieval.

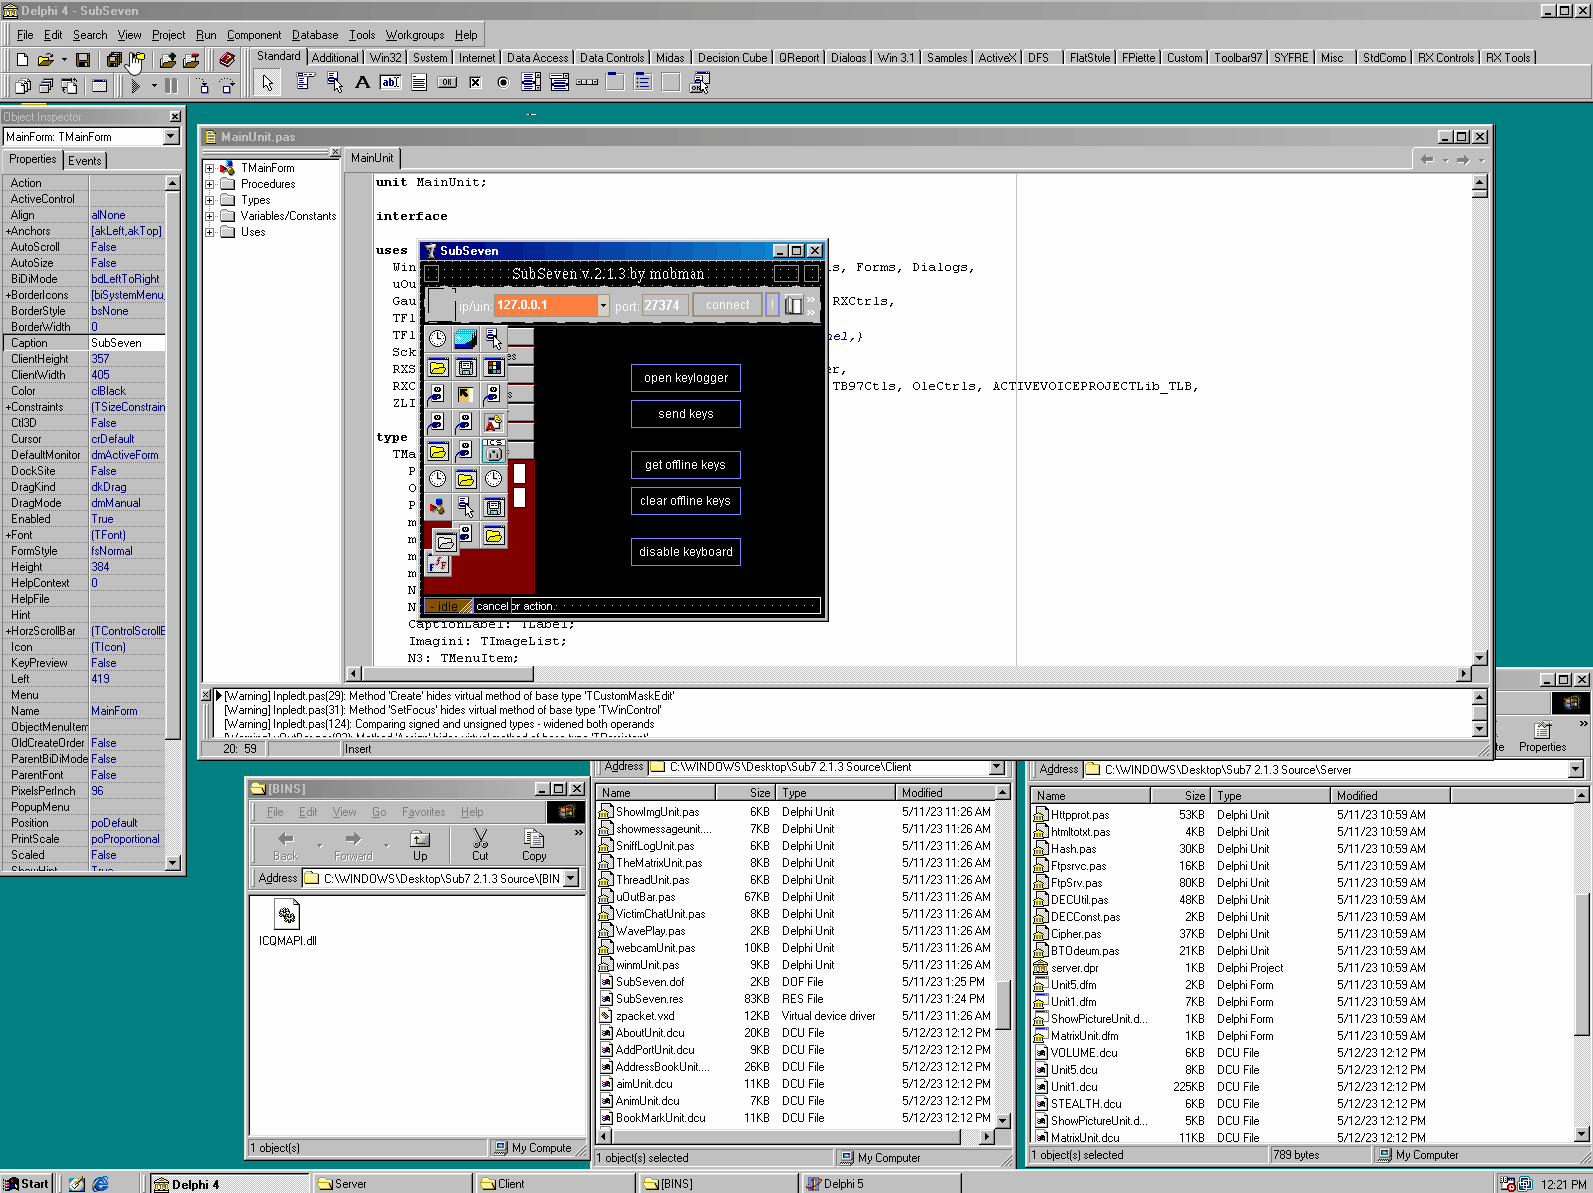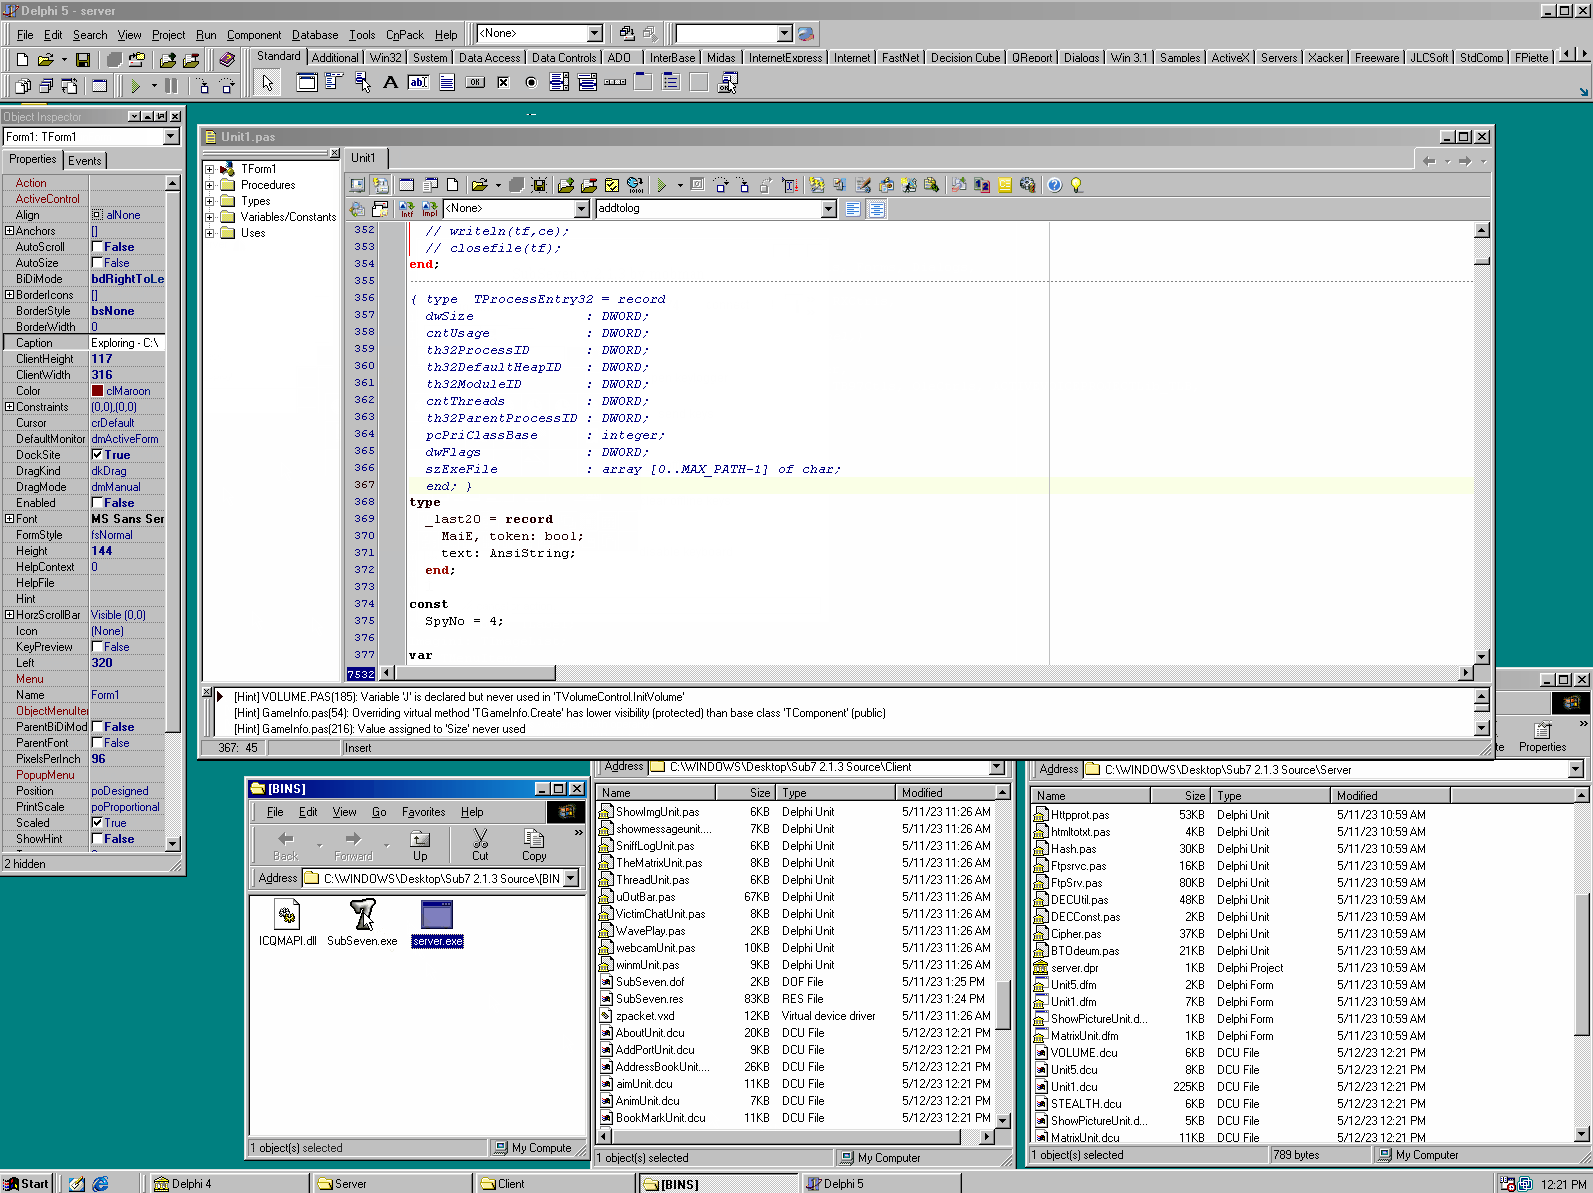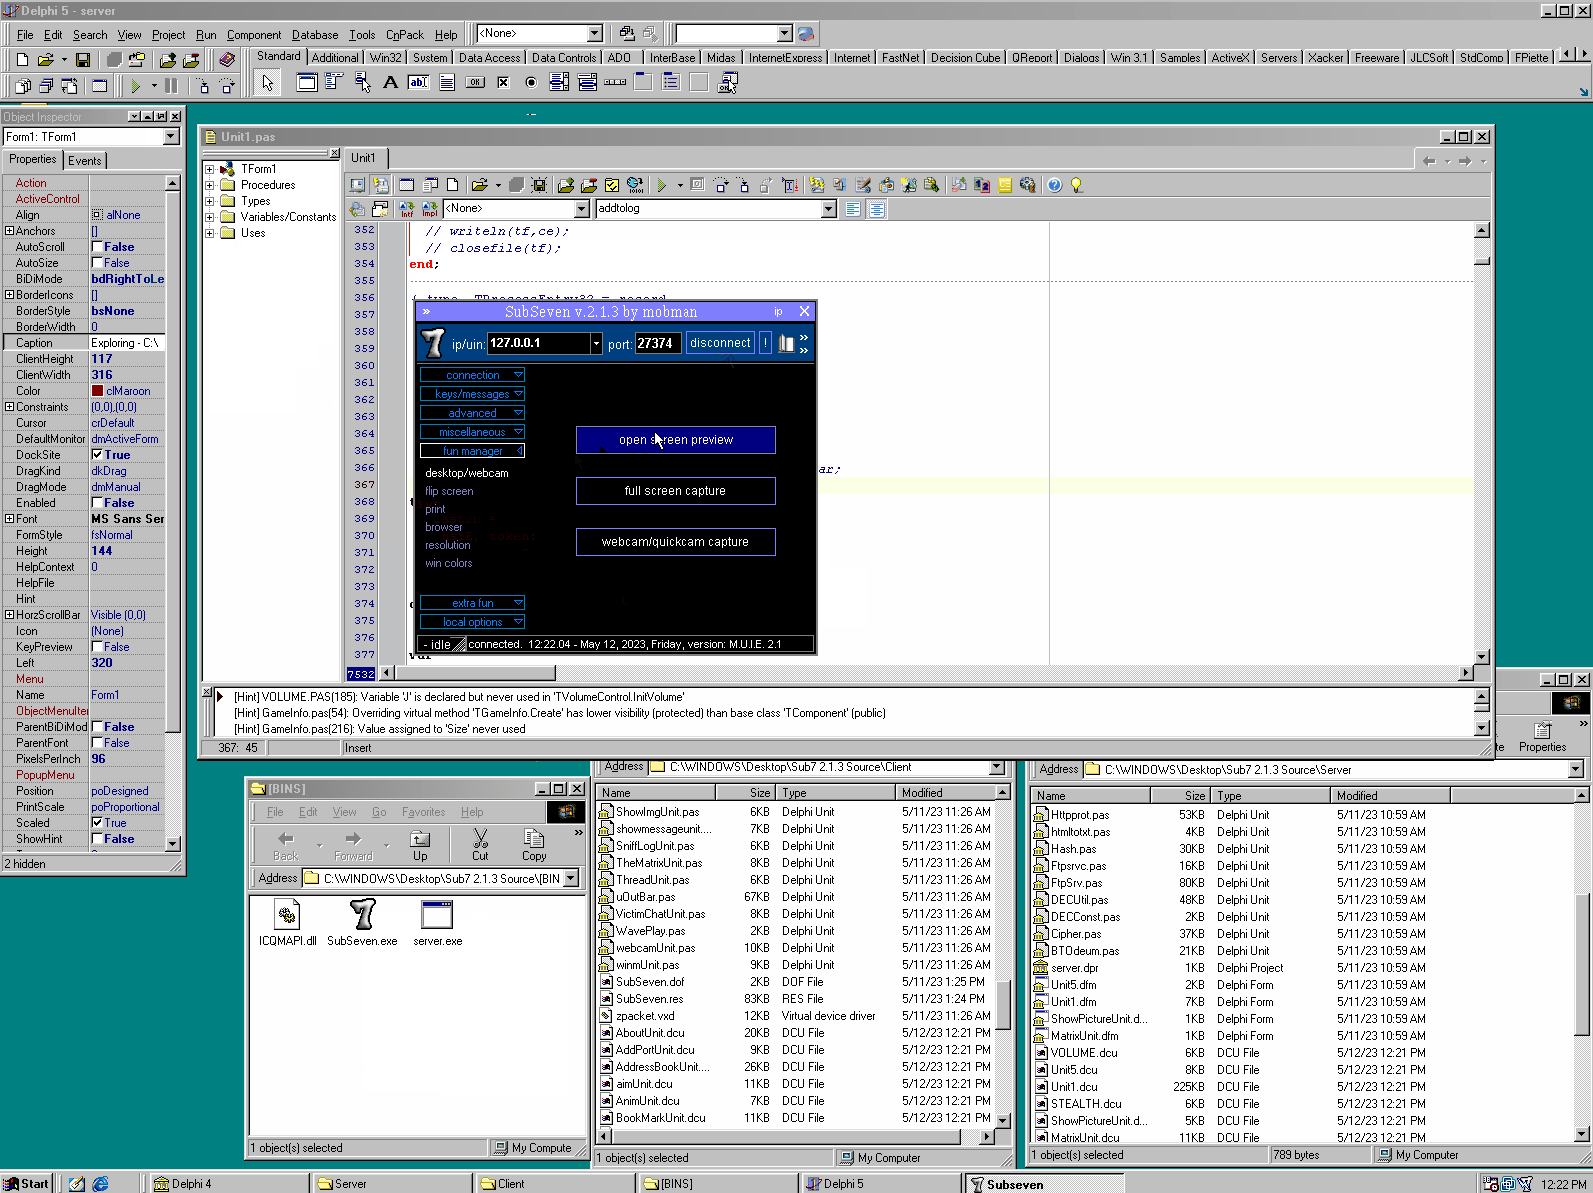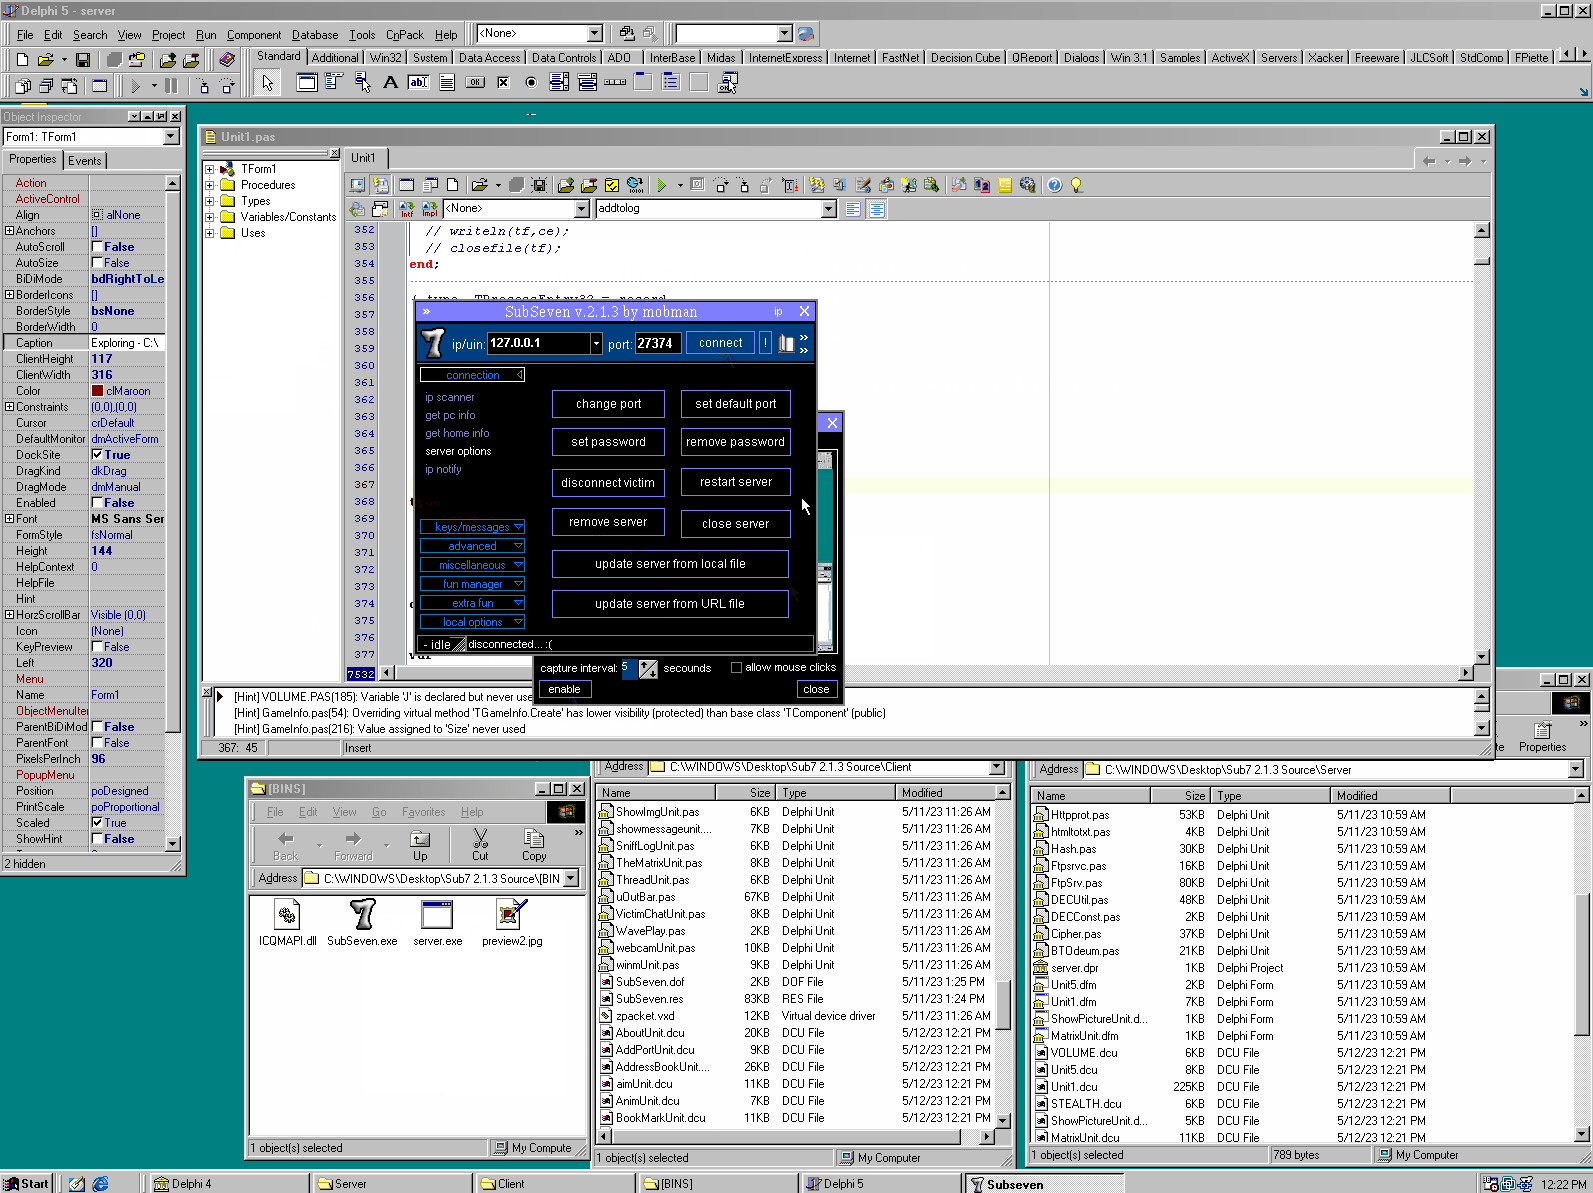
Source code for SubSeven 2.1.3